mythic_telegram_profile

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

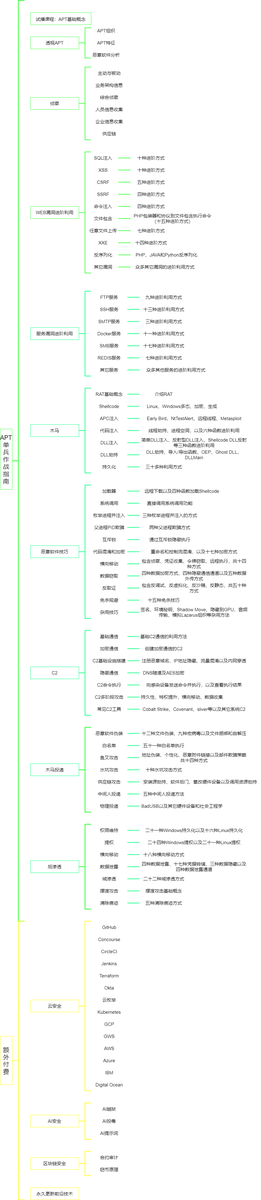
Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…

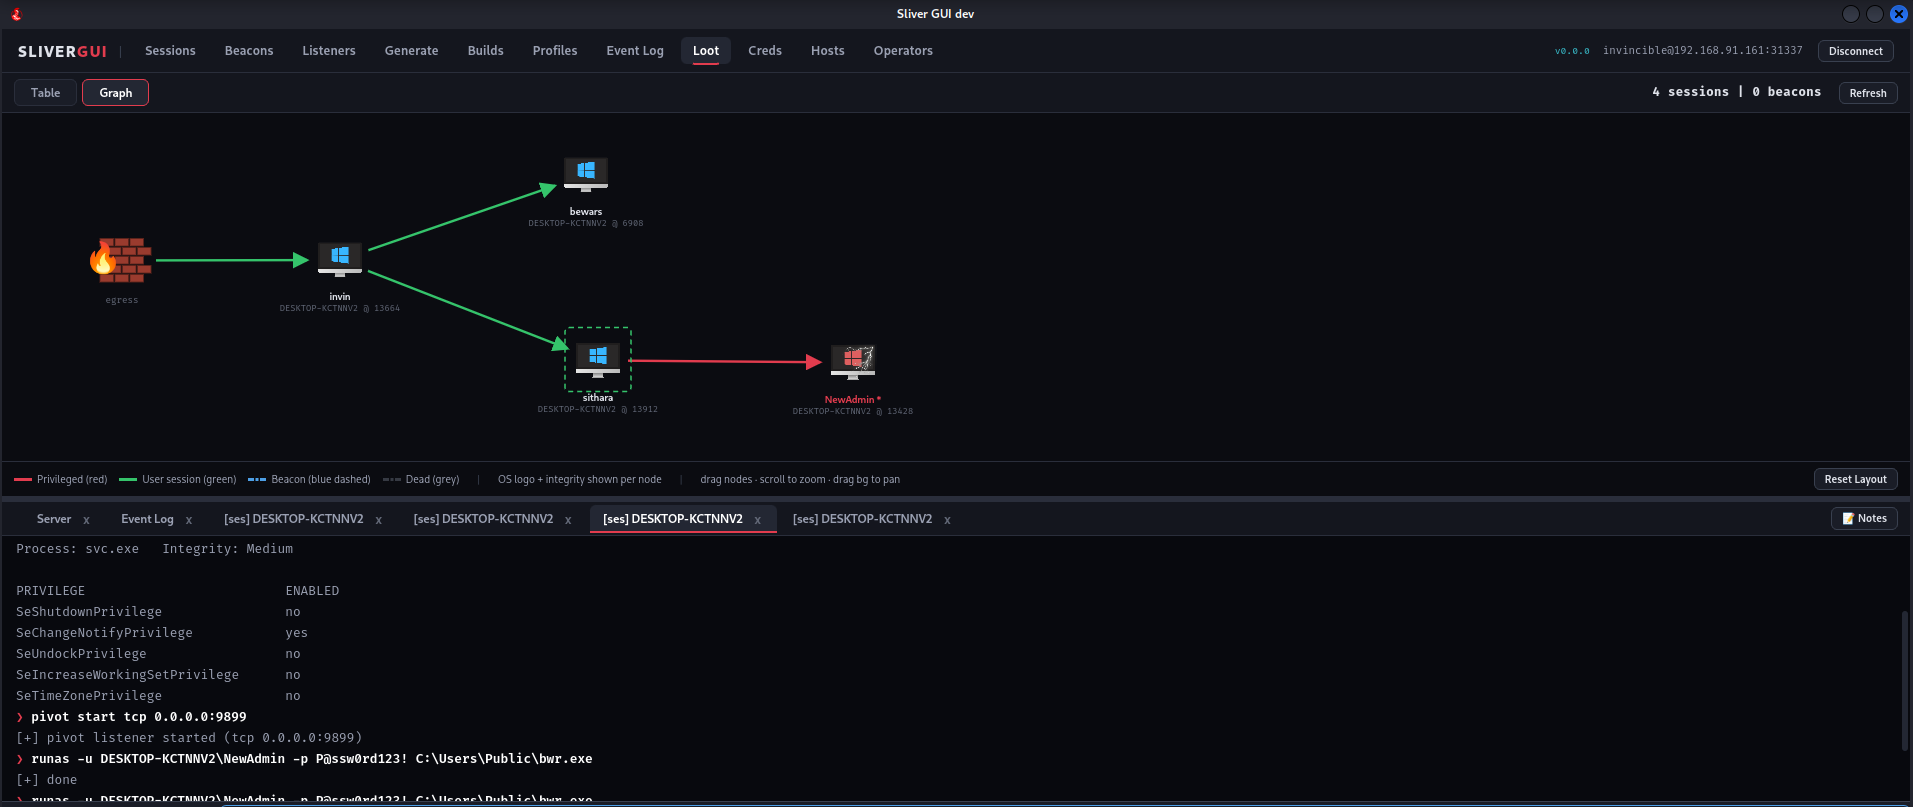
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…

Automated Mass Exploiter


poc for CVE-2025-24252 & CVE-2025-24132

Exploits locked/password protected computers over USB, drops persistent WebSocket-based backdoor, exposes internal router, and siphons cookies using…

** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…

Repo containing docker-compose files and setup scripts without having to clone the individual reternal components

Penetration testing framework with AI-driven decision engine

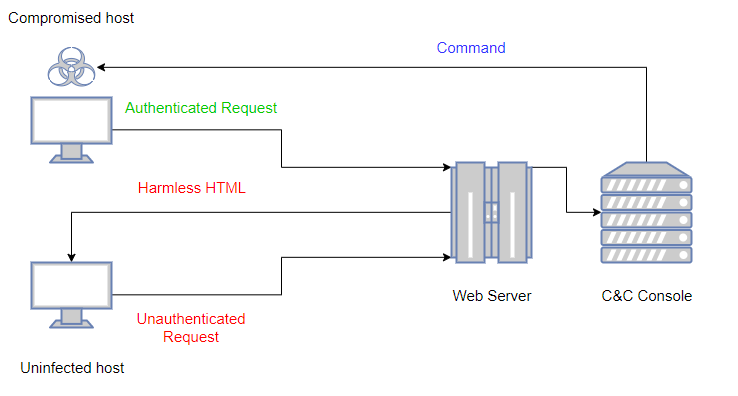
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service

On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.

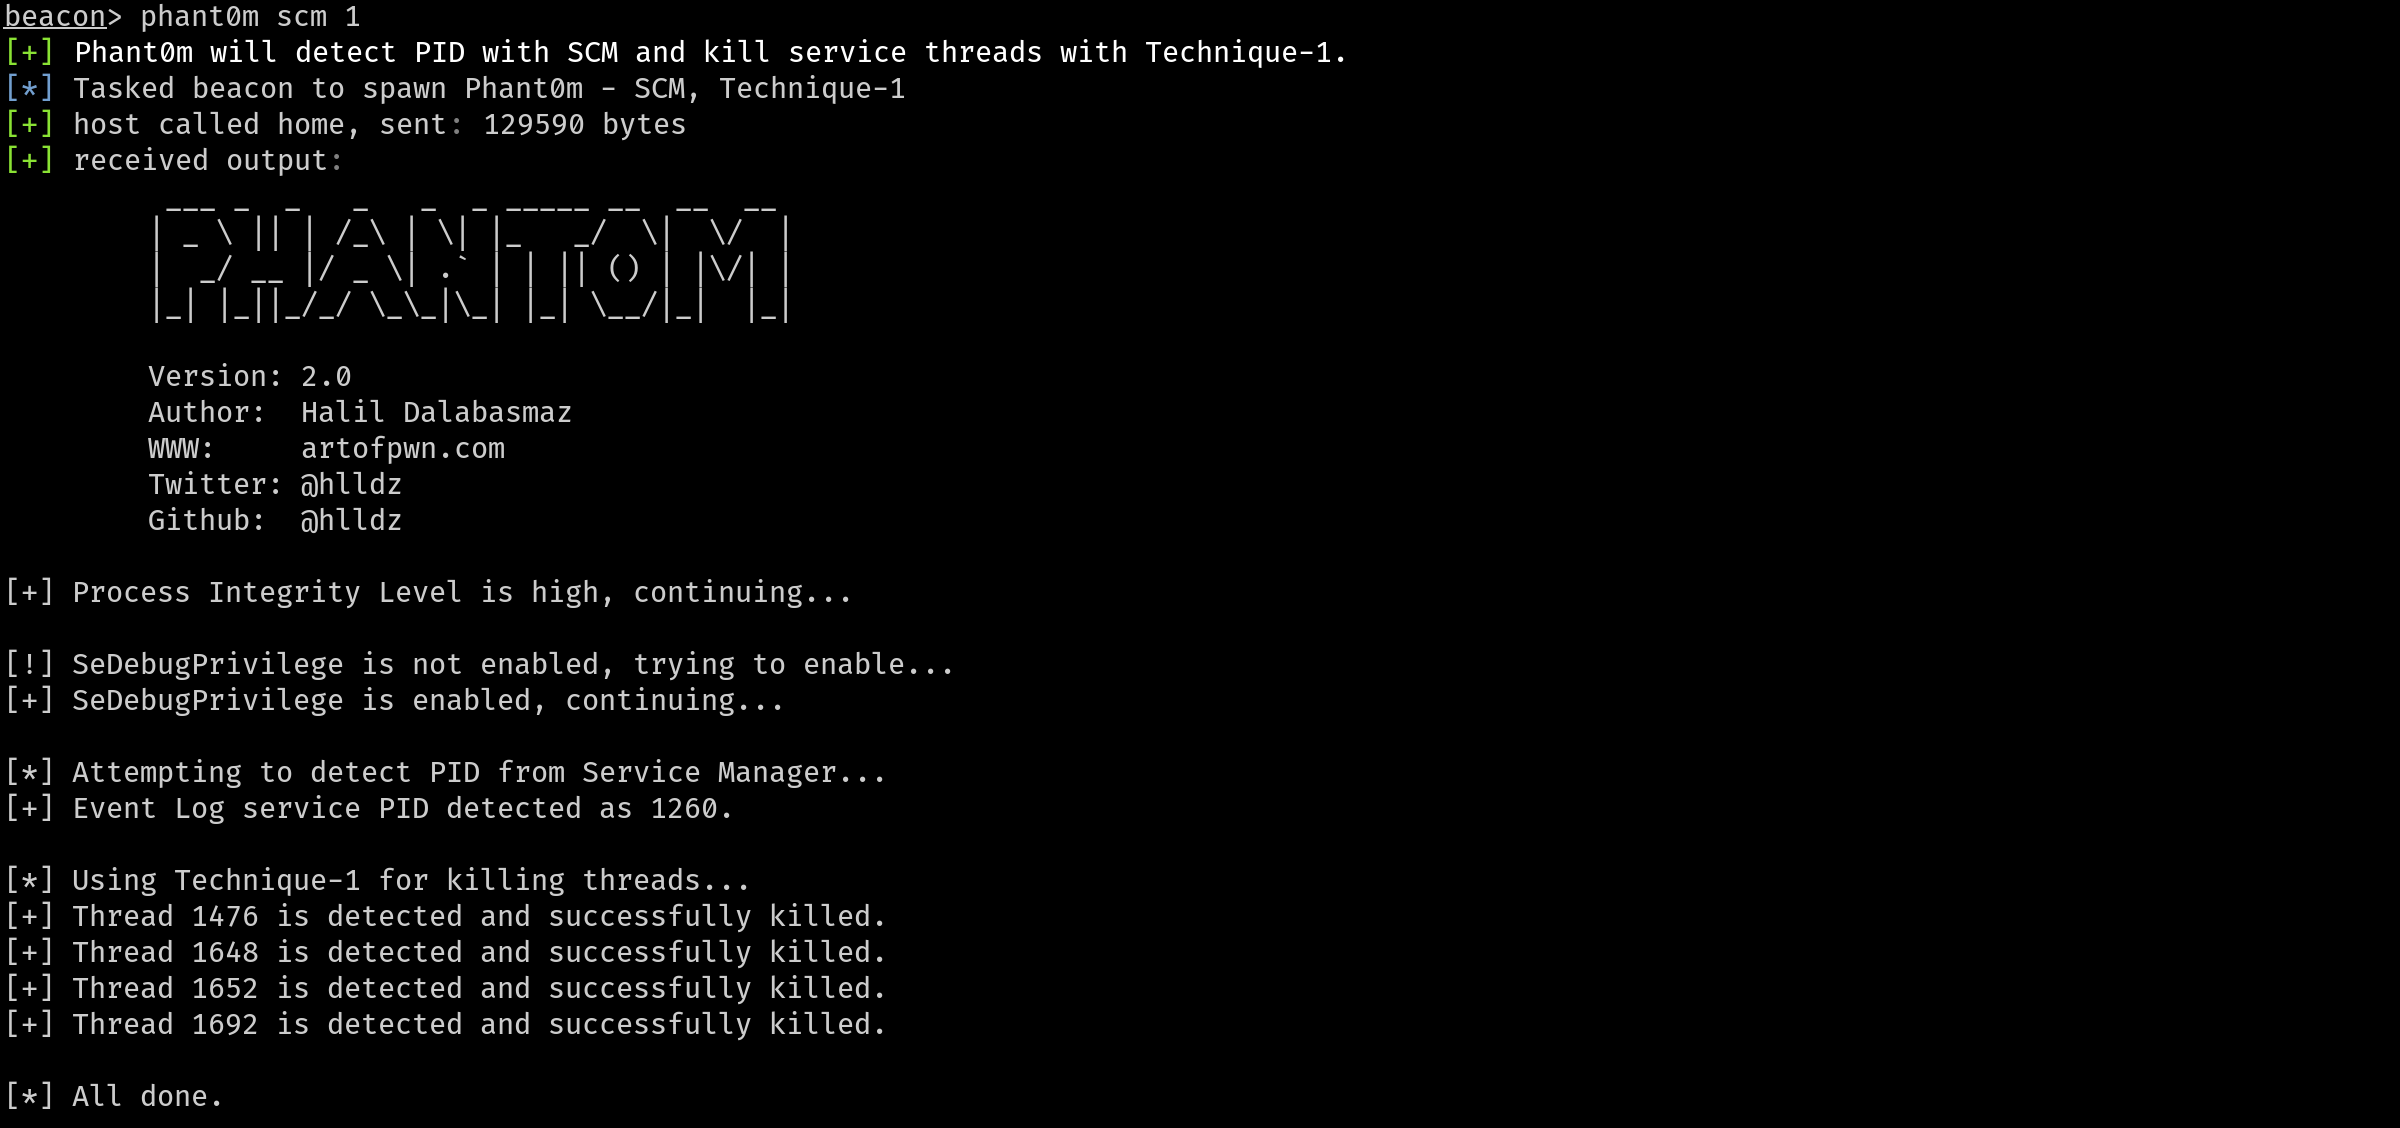
Windows Event Log Killer

Tor transport bridge for Sliver C2 - anonymous command and control

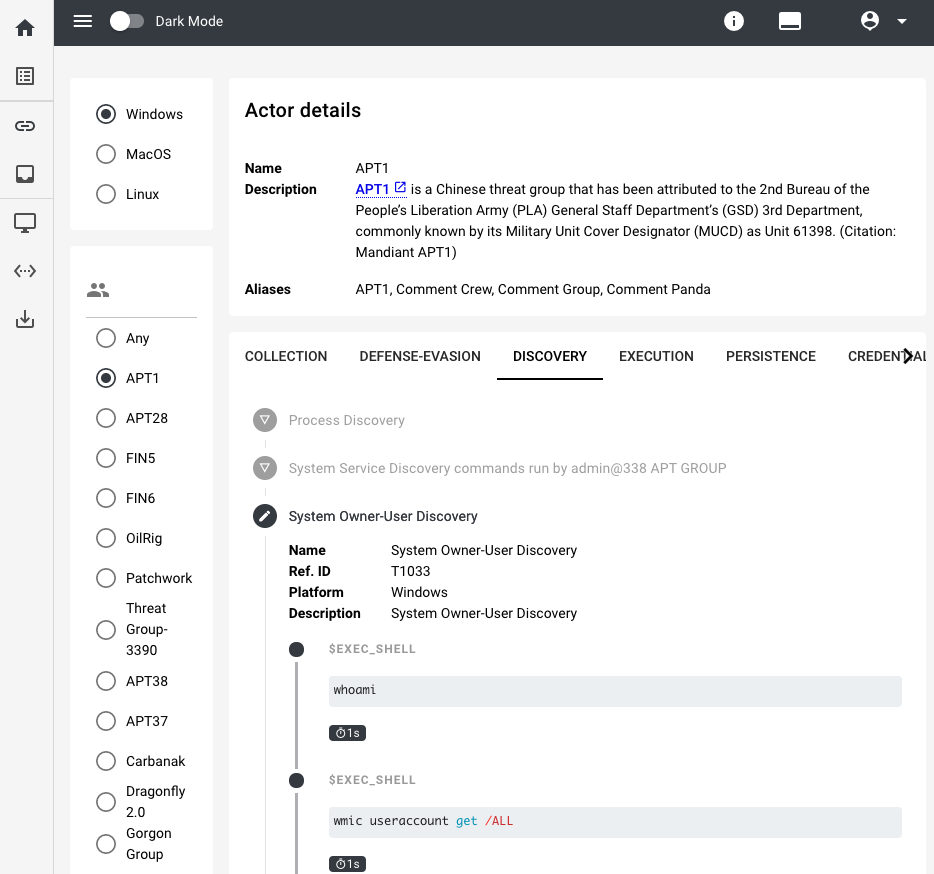
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…

Sliver HTTP(S) C2 PNG bomb DoS exploit — GHSA-663m-7x7m-g4fw (CVE-2026-77622)

Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.