
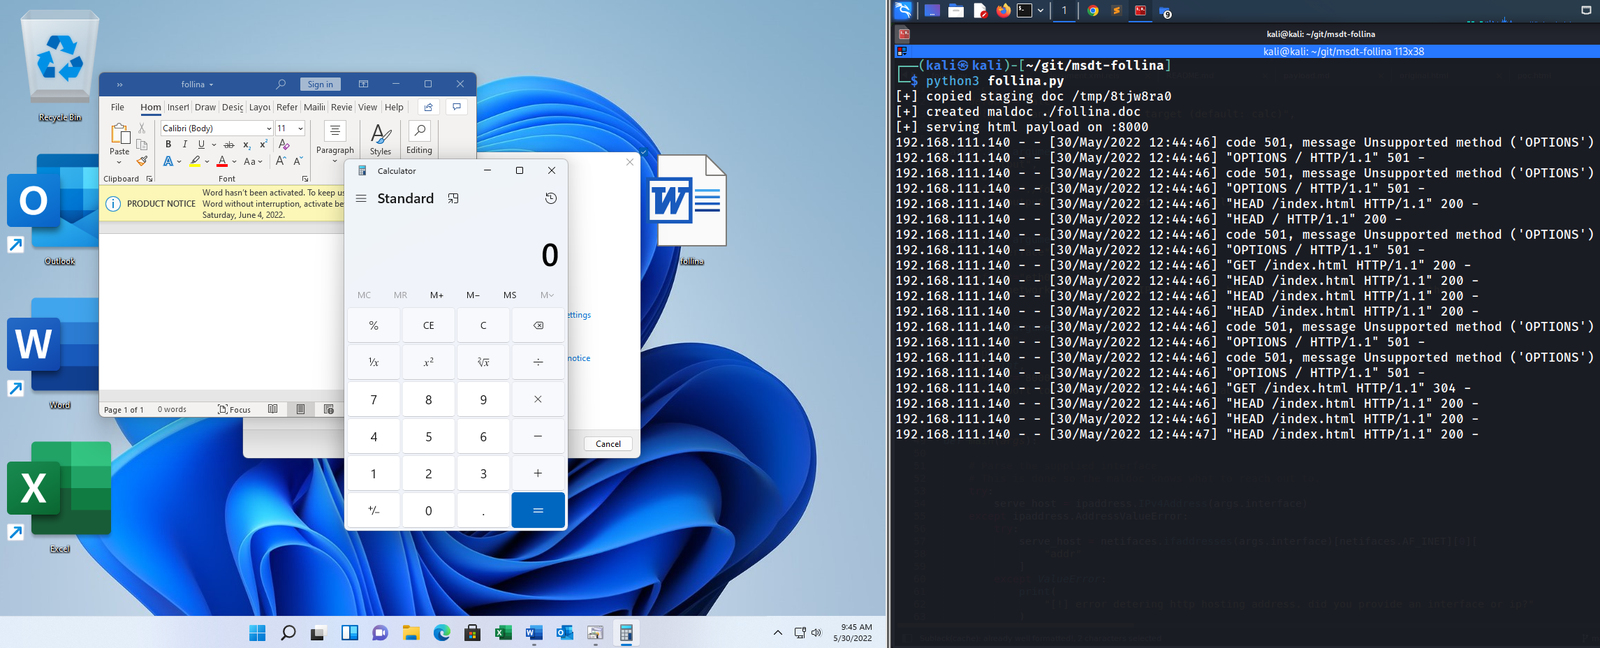
msdt-follina
 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
command-and-controlexploitationpayload-development+2
1.6k
johnhammond/msdt-follinaGenerates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 rohan-pt/cve-2025-26055
CVE Description
 payatu/cve-2017-5638
Apache Struts 2.0 RCE vulnerability - Allows an attacker to inject OS commands into a web application through the content-type header
 malwareman007/deathnote
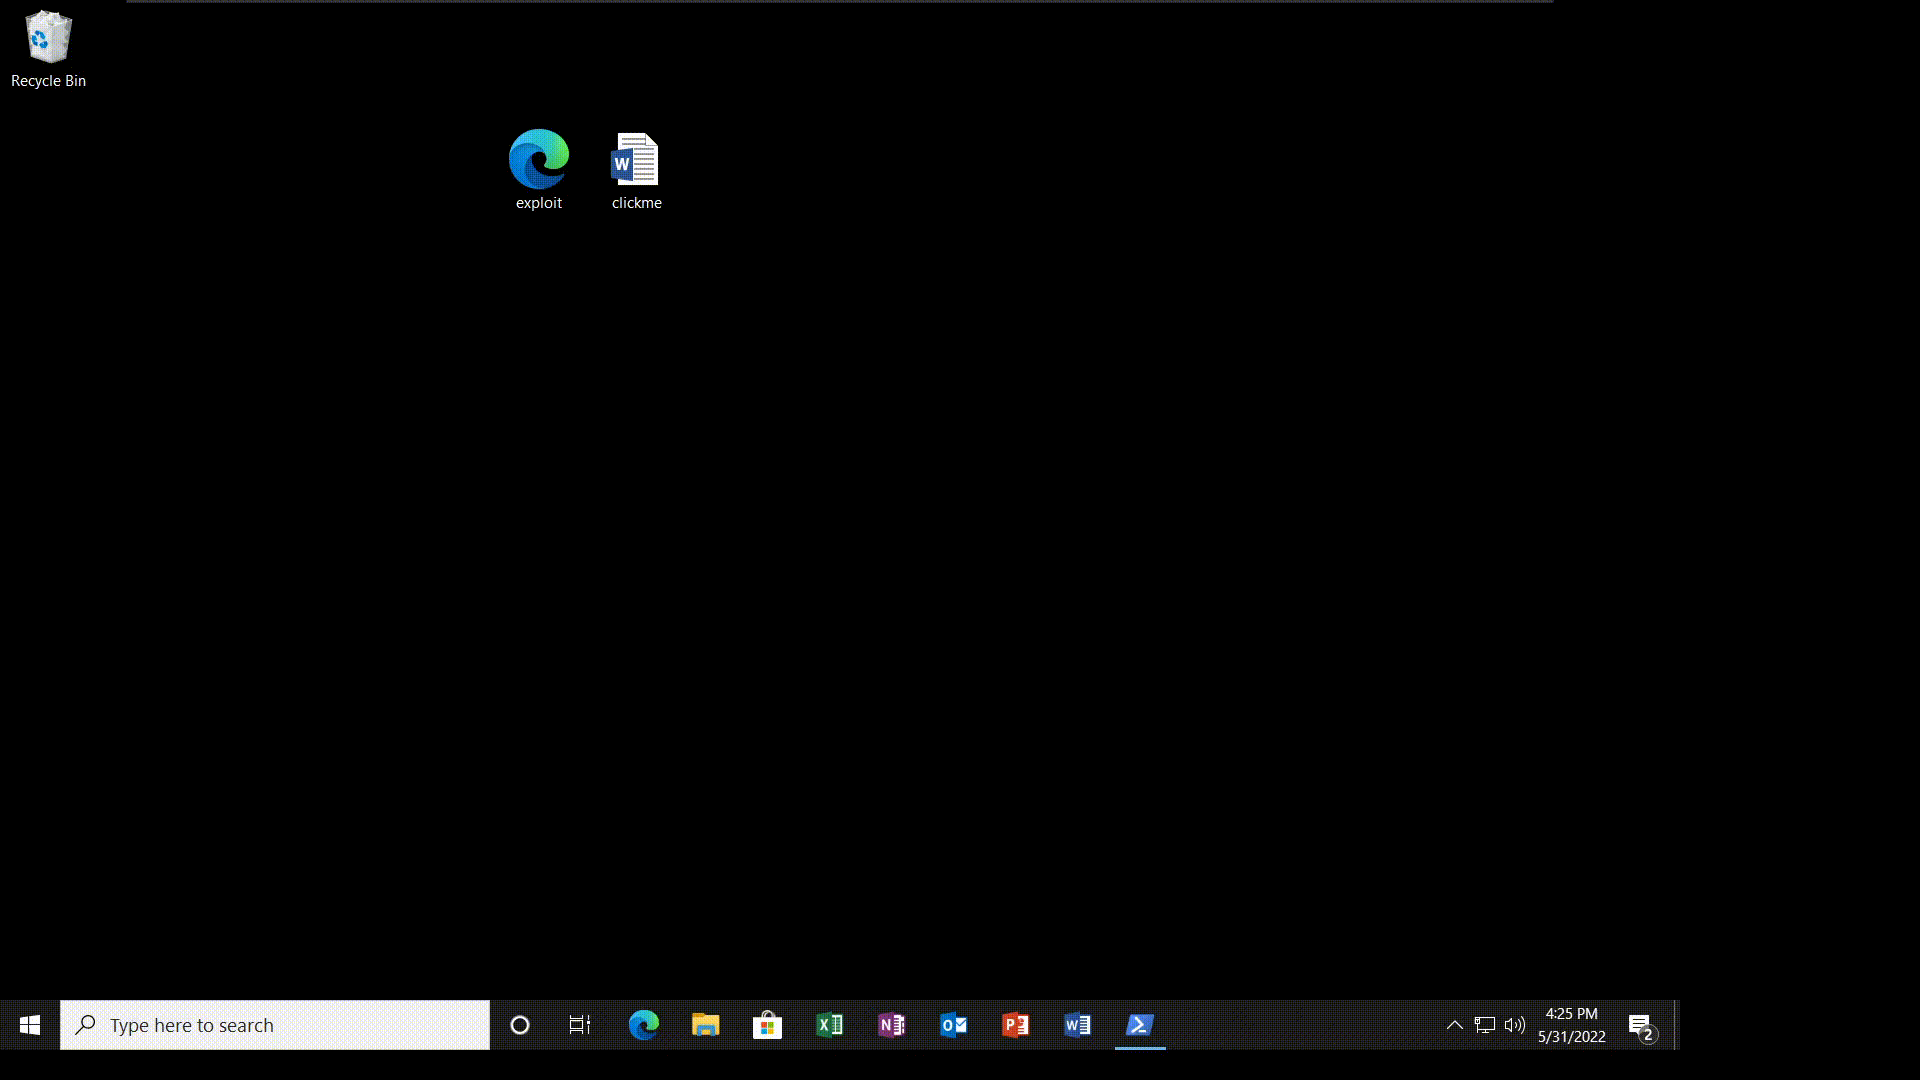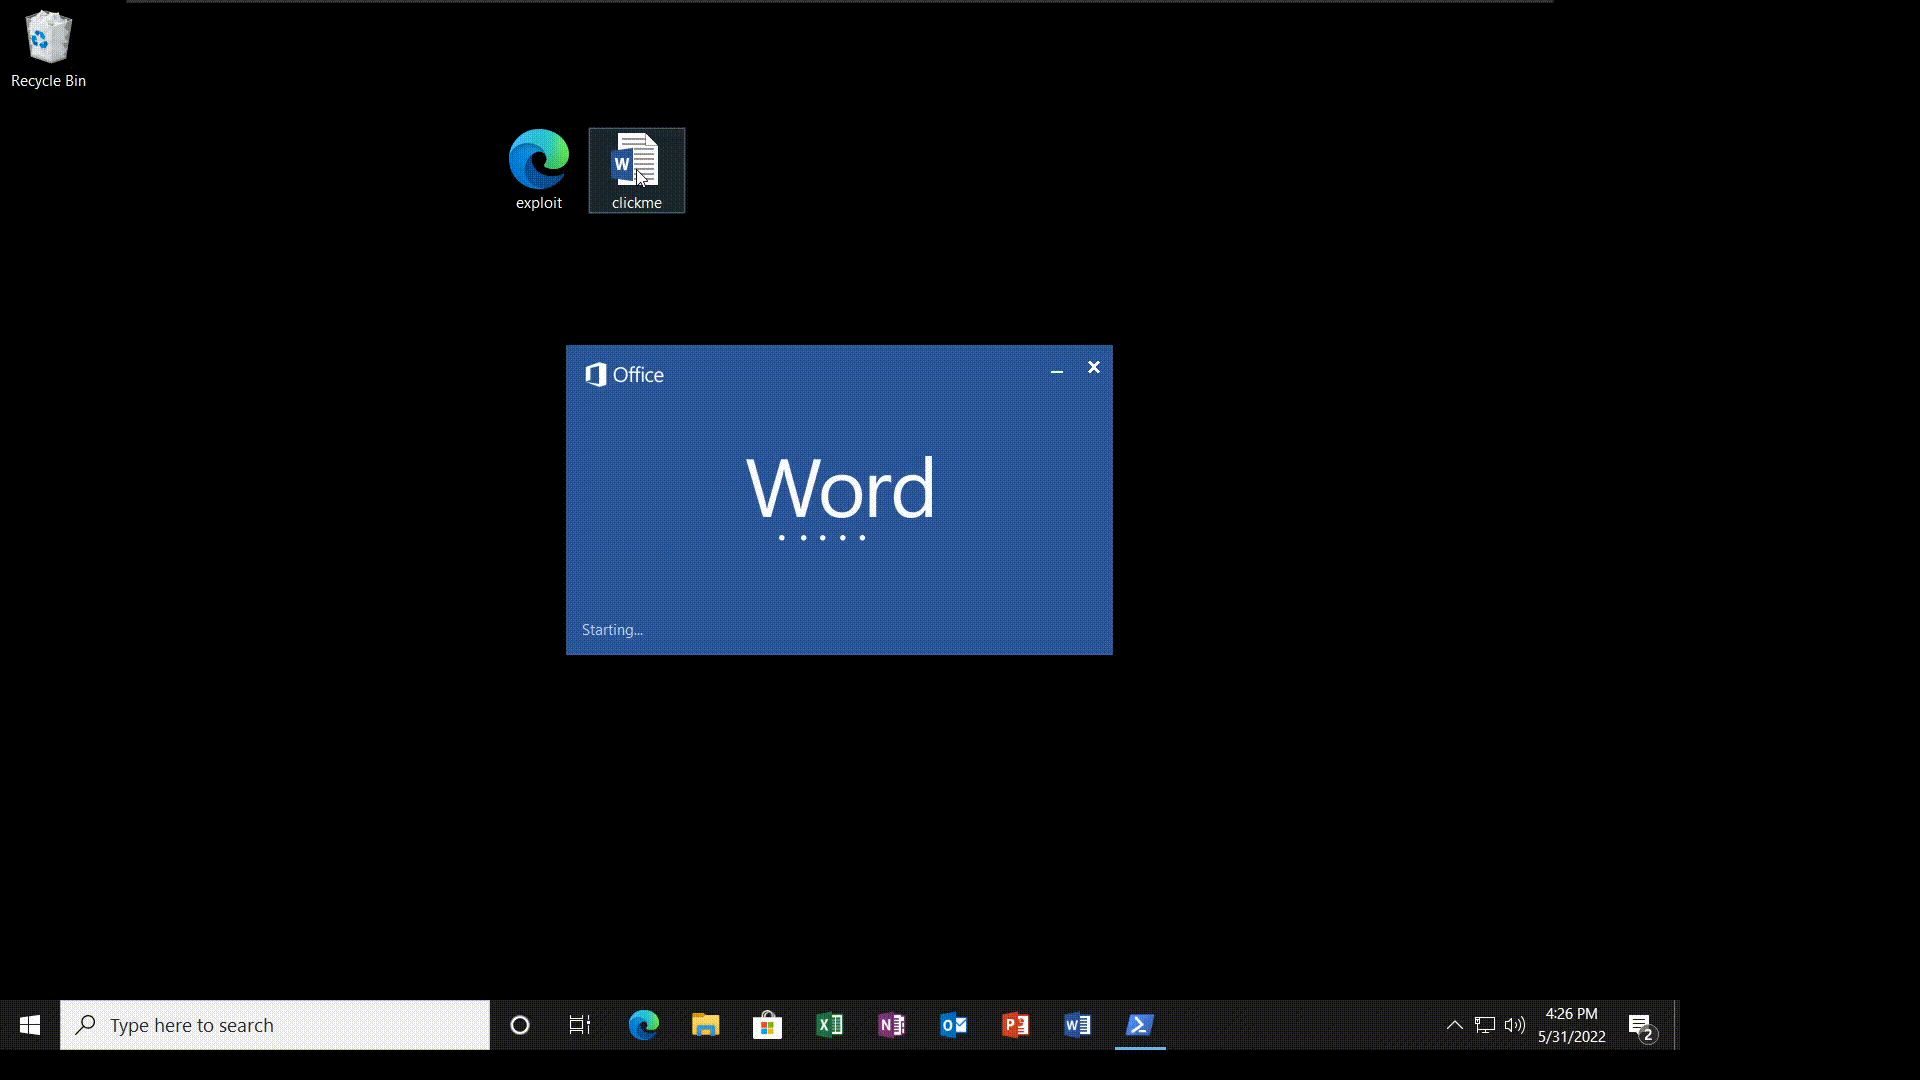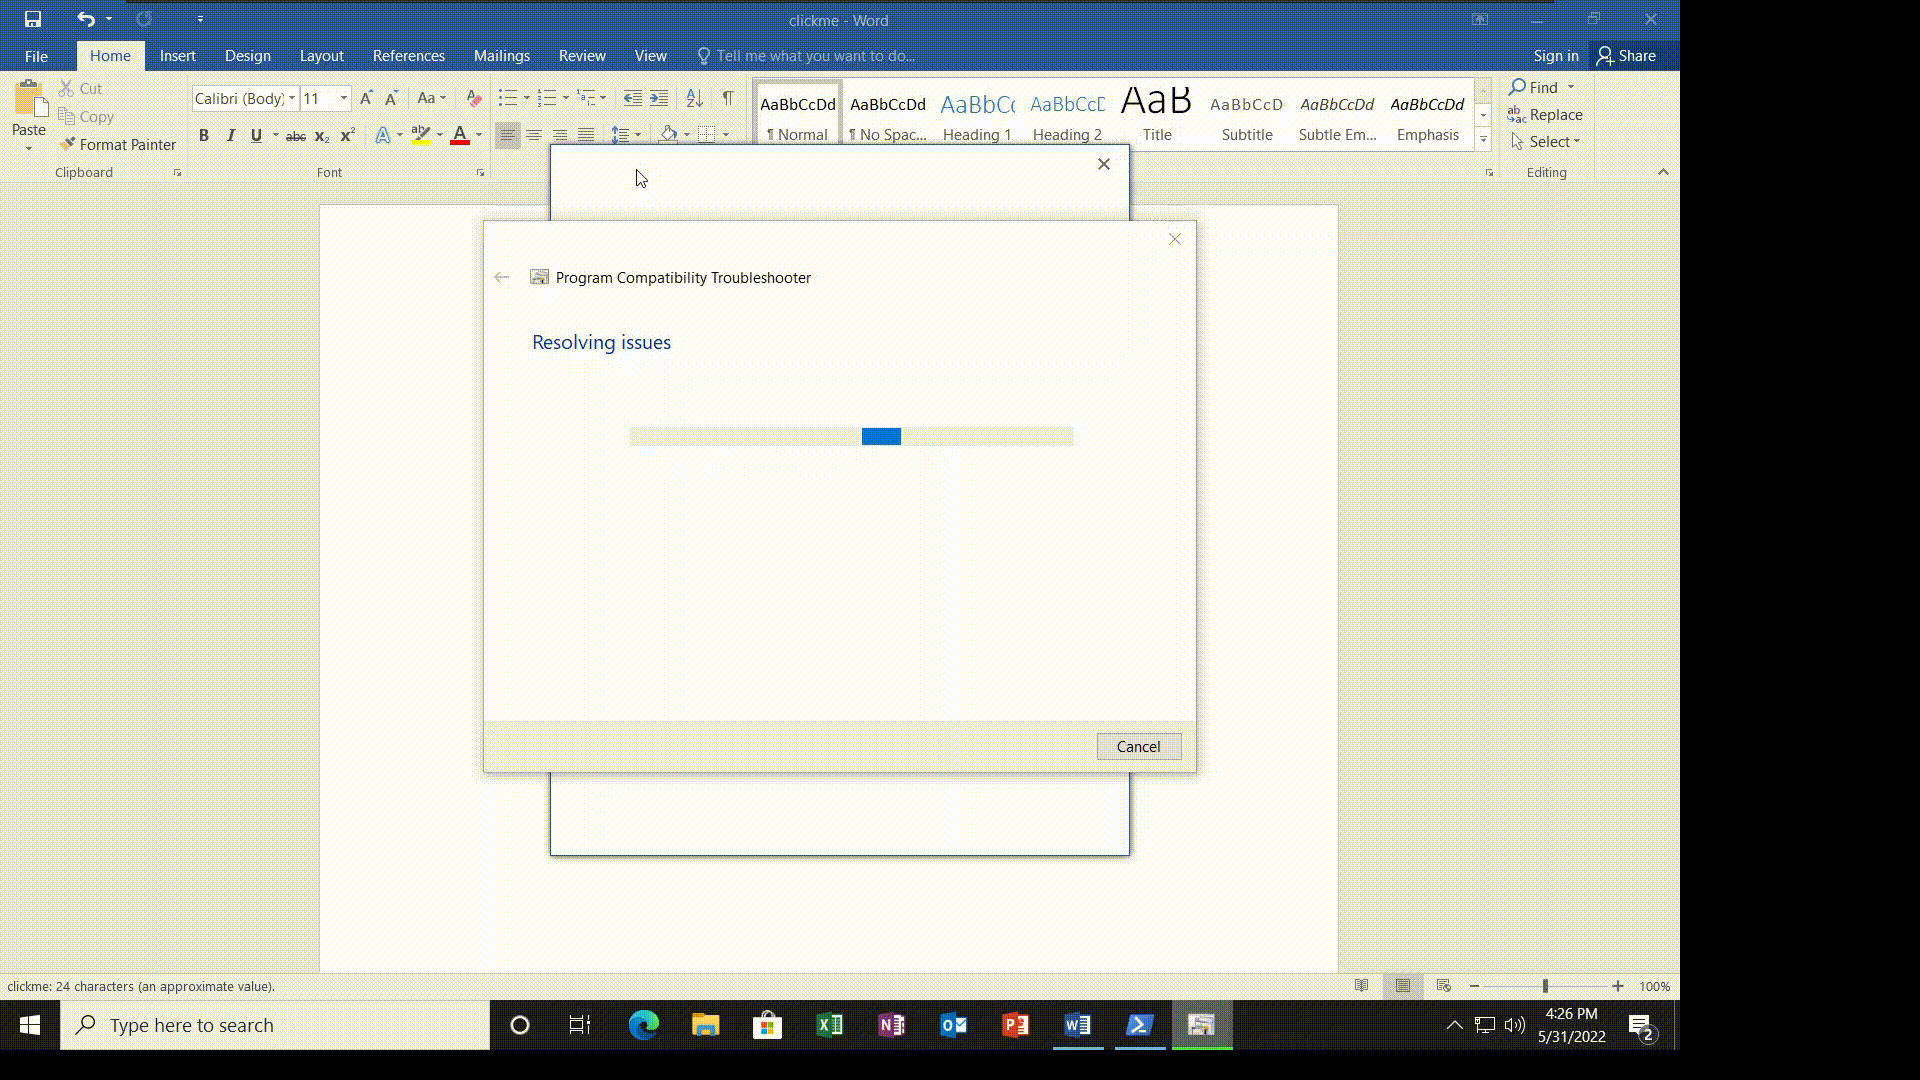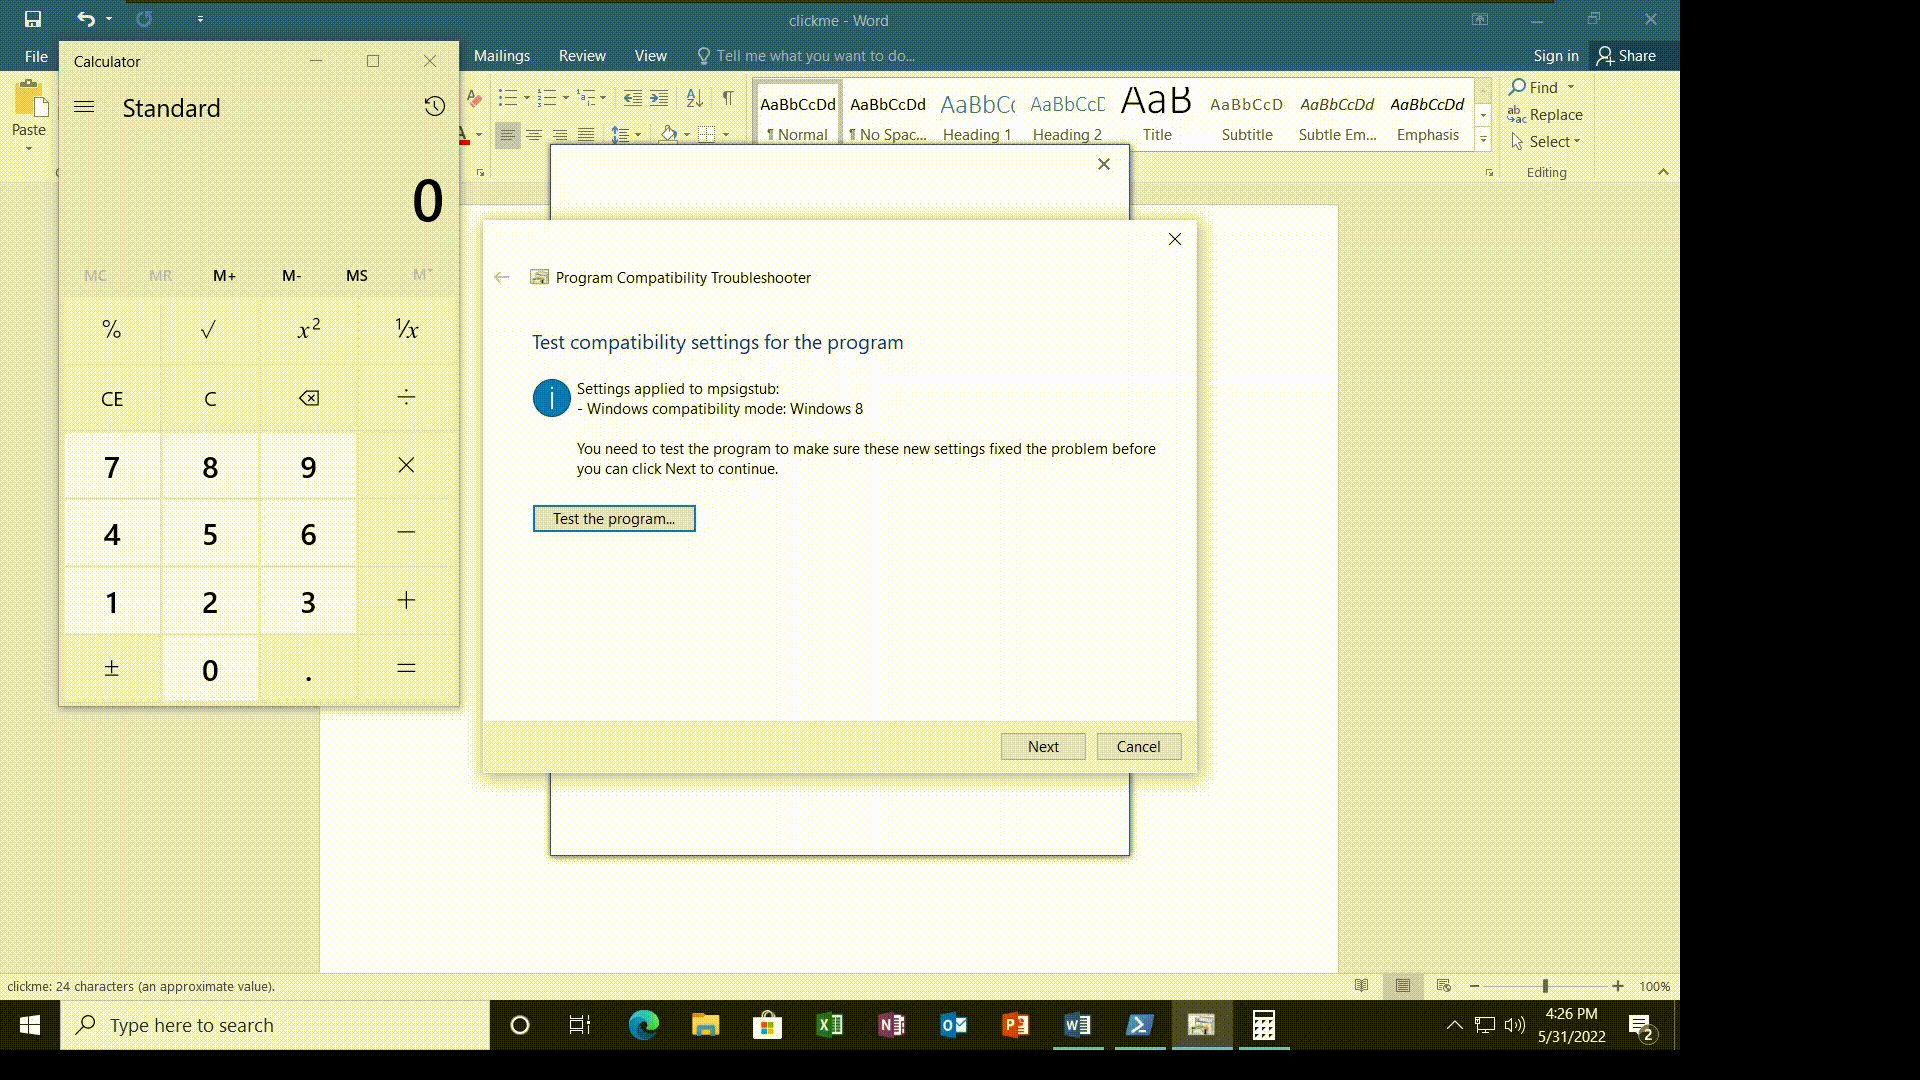
Proof of Concept of CVE-2022-30190
 tadash10/exploiting-cve-2021-44228-log4shell-in-a-banking-environment
Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.
 muhammad-ali007/follina_msdt_cve-2022-30190
Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…
 cotherm/cve-2025-25706
Detailed CVE-2025-25706 proof-of-concept demonstrating authenticated remote code execution via command injection in ProApps ping functionality,…
 syrins/cve-2025-55182-react2shell-rce
A modern, user-friendly GUI application for detecting and exploiting the CVE-2025-55182 vulnerability in React Server Components. Built with Python…
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…