
trojanizer
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
command-and-controlexploitationids-ips-evasion+6
2948 years ago
r00t-3xp10it/trojanizerTrojanize your payload - WinRAR (SFX) automatization - under Linux distros
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
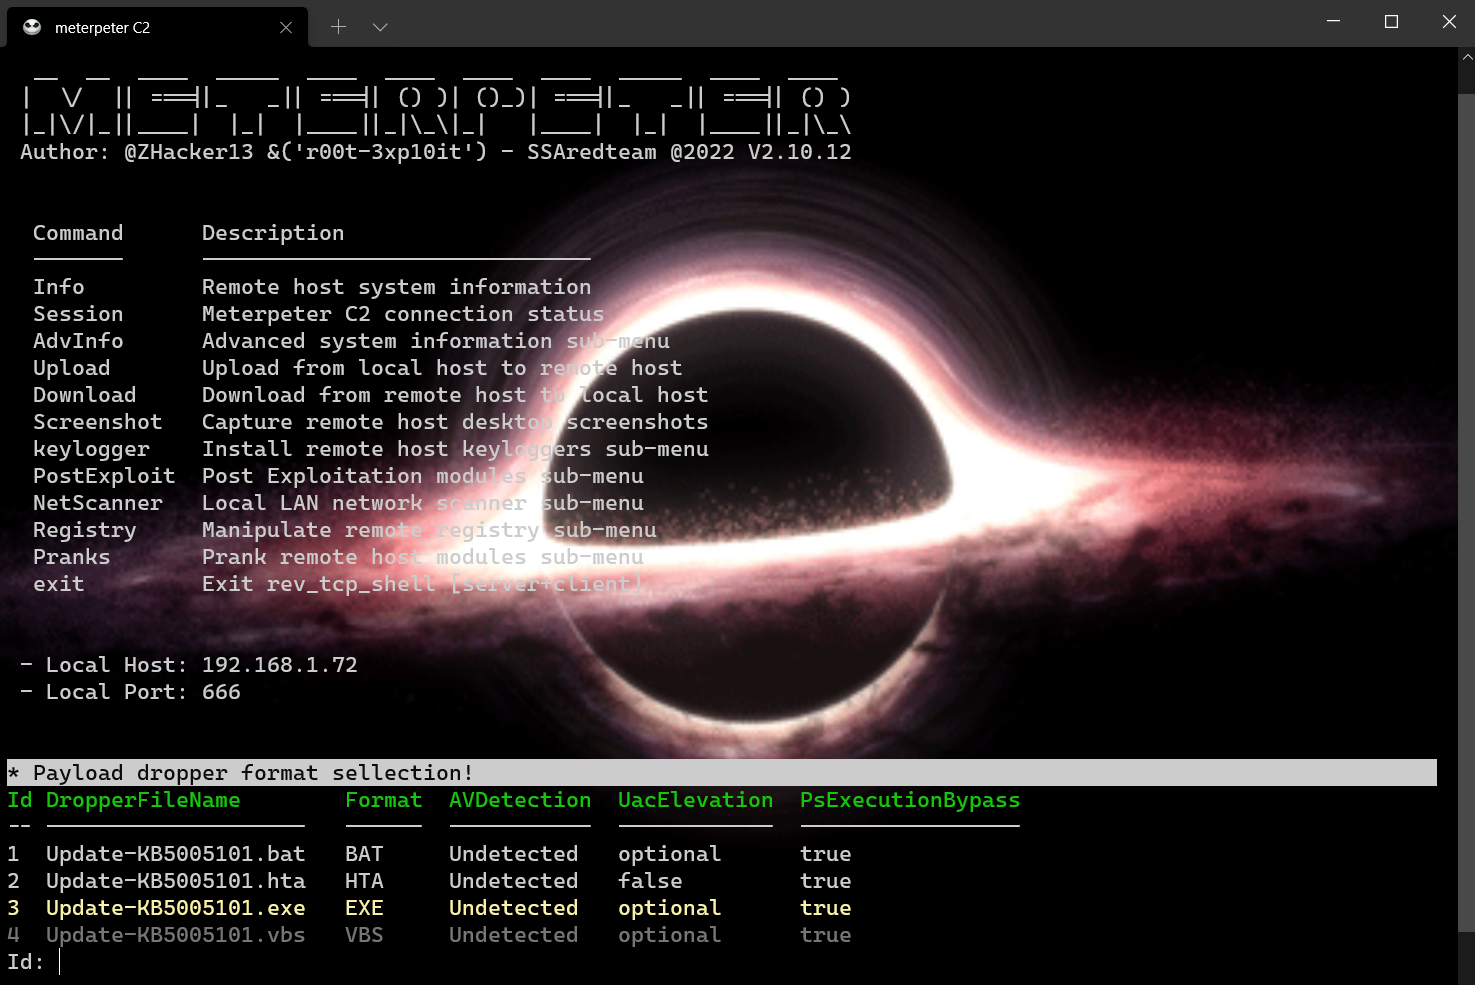 r00t-3xp10it/meterpeter
C2 Powershell Command & Control Framework with BuiltIn Commands
 r00t-3xp10it/meterpreter_paranoid_mode-ssl
Meterpreter Paranoid Mode - SSL/TLS connections
 febinrev/atril_cbt-inject-exploit
CVE-2023-44452, CVE-2023-51698: CBT File Parsing Argument Injection that affected Popular Linux Distros