
CaptainHook
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
binary-analysiscode-analysisdebuggers+2
9
synacktiv/captainhookTraces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 assassinukg/cve-2021-22204
Exploit script for CVE-2021-22204, an ExifTool RCE via malicious DjVu files, with manual exploitation steps and reverse shell payloads.
 anshumanbh/git-all-secrets
A tool to capture all the git secrets by leveraging multiple open source git searching tools
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 biitts/cve-2026-56121-feast-unauth-rce
CVE-2026-56121 — Feast <0.63.0 unauthenticated RCE via gRPC registry dill.loads of OnDemandFeatureView UDF (pre-auth). Lab + PoC, verified e2e.
 xiaoxiaoranxxx/cve-2025-56815
Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 nollium/cve-2024-9264
Exploit for Grafana arbitrary file-read and RCE (CVE-2024-9264)
 merbinr/cve-2024-44623
Details about the Blind RCE issue(SPX-GC) in SPX-GC
 haile01/perl_spreadsheet_excel_rce_poc
POC for RCE vulnerability in ParseExcel library, and ParseXLSX too, as a depending library
 maestro-ant/vvveb-cms-cve-2025-8518
This repository contains a Proof of Concept (PoC) demonstrating a critical vulnerability in givanz Vvveb 1.0.5. The vulnerability allows an…
 shoucheng3/nahsra__antisamy_cve-2016-10006_1-5-3
Fast, configurable HTML sanitization library for preventing XSS and malicious code injection from untrusted user input. Provides a policy-driven API…
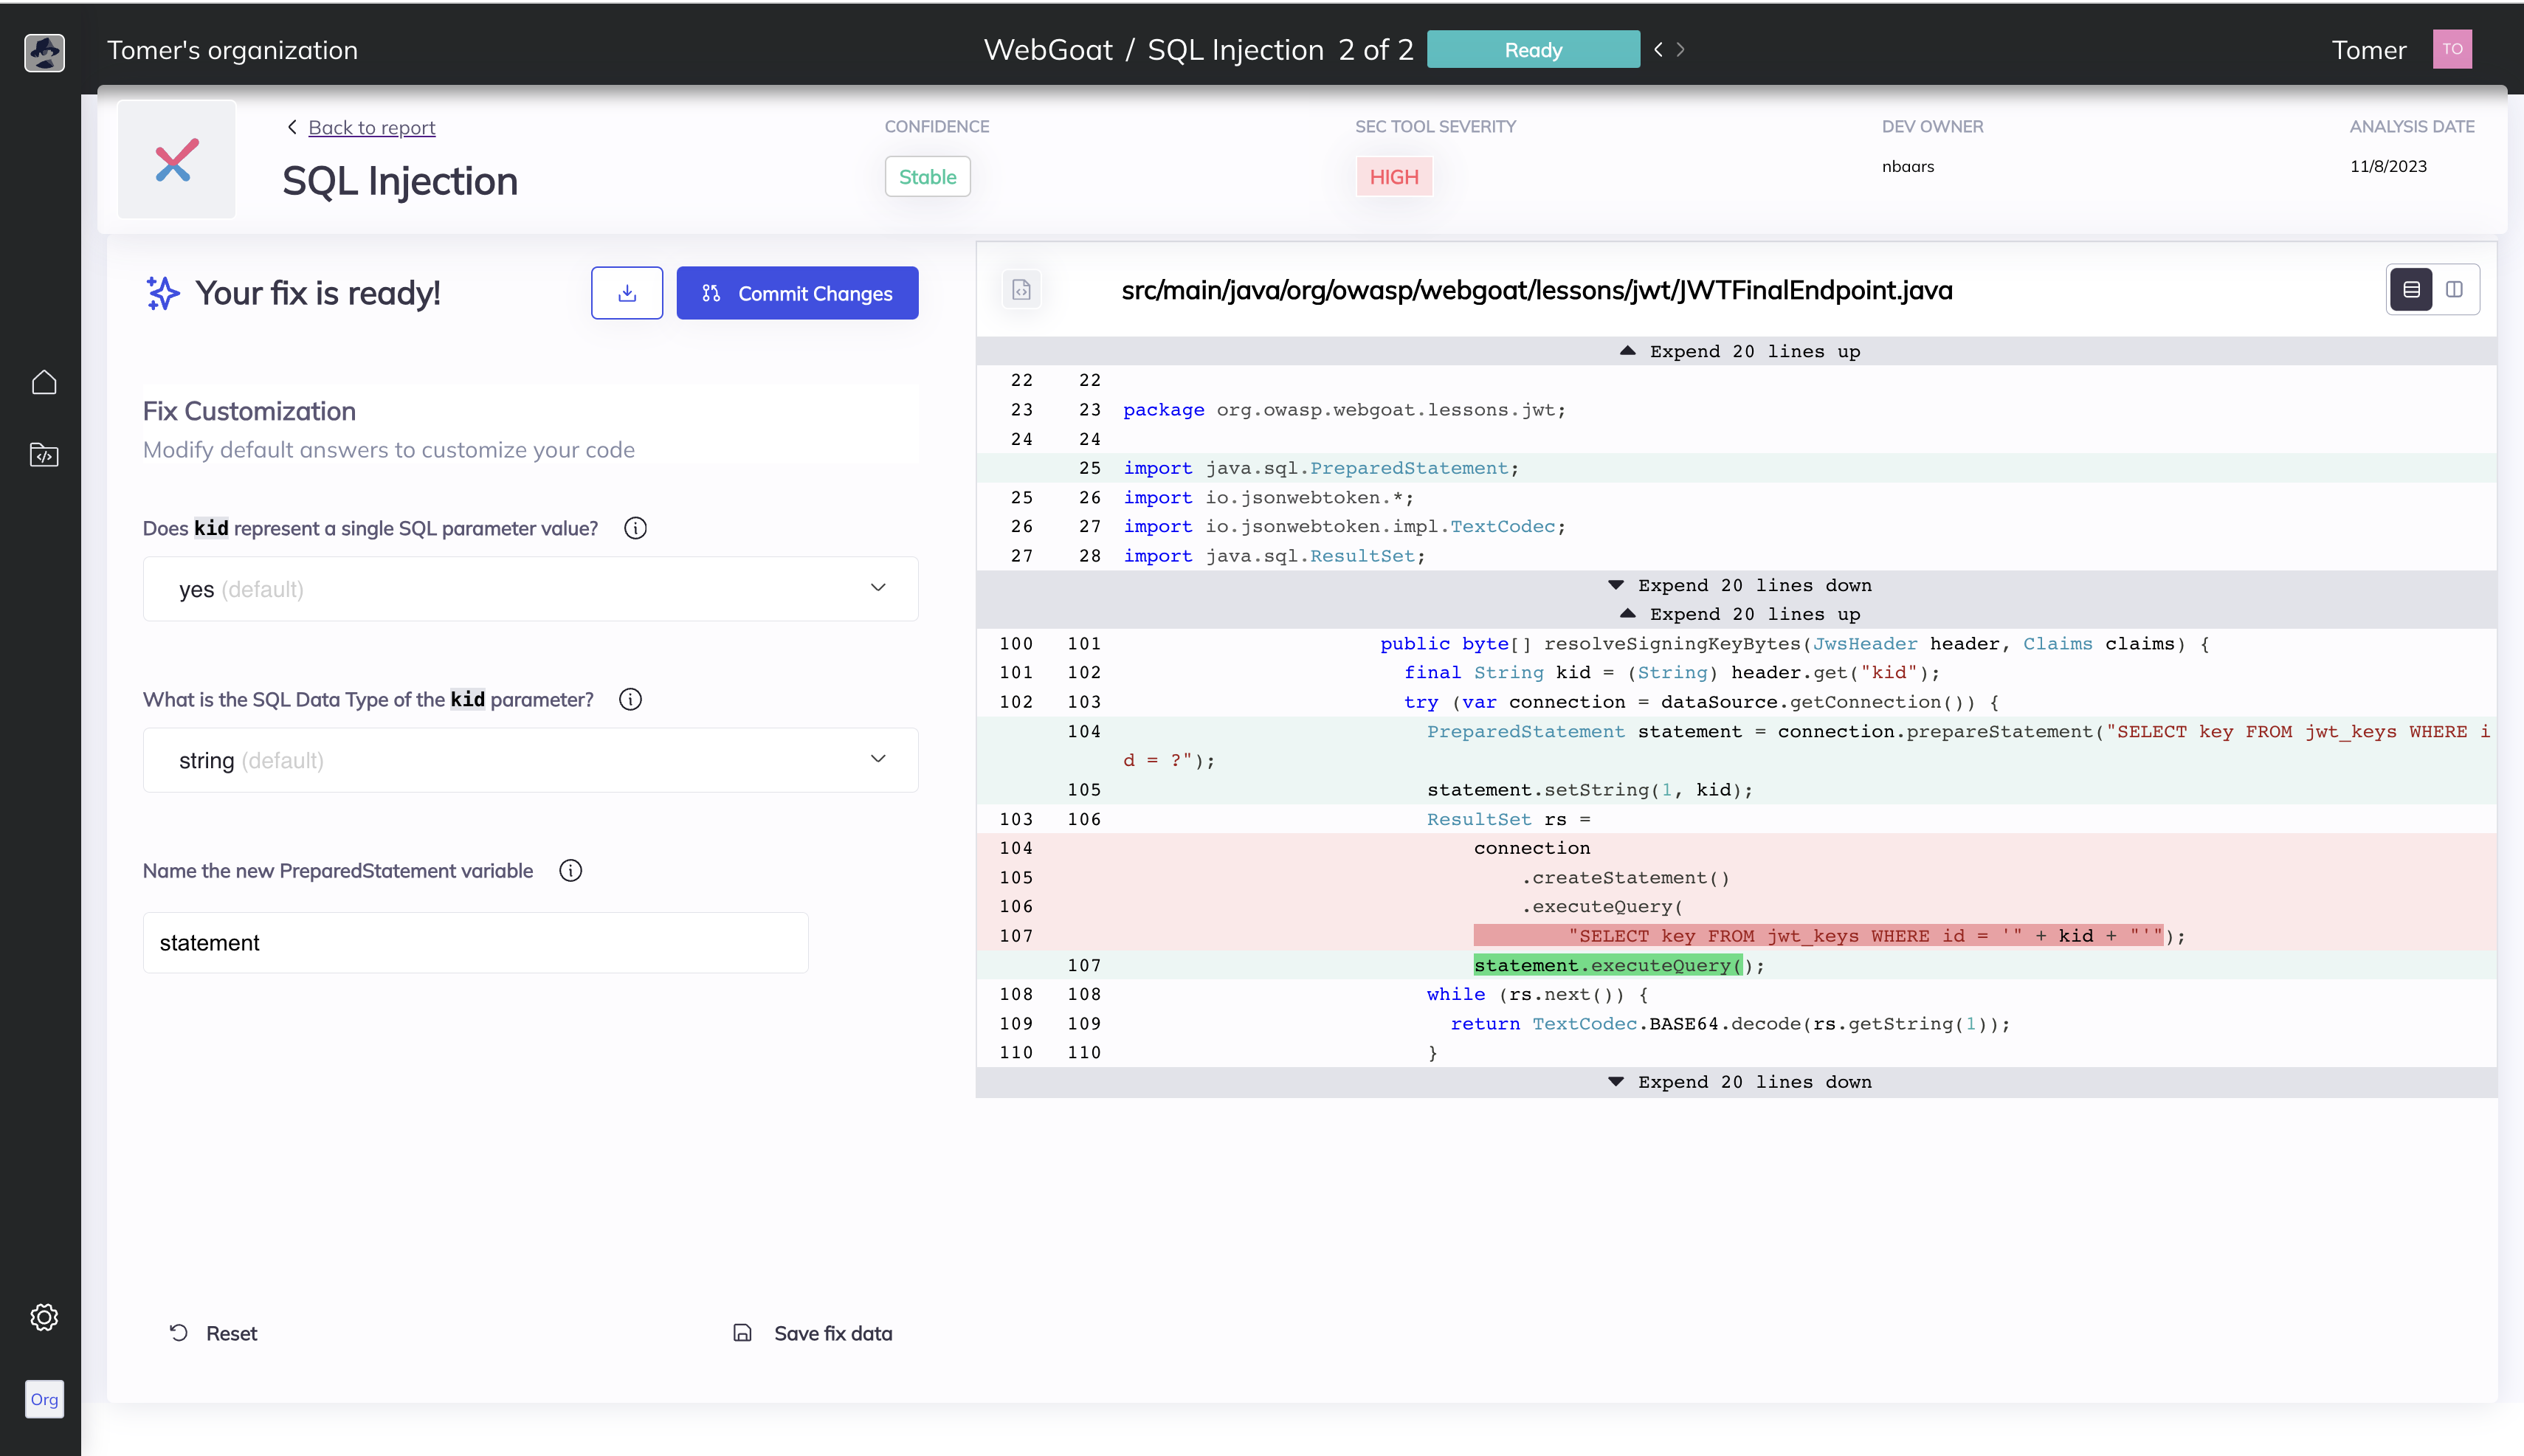 mobb-dev/bugsy
Automatic security vulnerability remediation for your code.
 osvaldotenorio/cve-2024-48325
Proof-of-concept for SQL injection in Portabilis i-Educar 2.8.0, demonstrating unauthenticated database access via the getDocuments endpoint with…
 nicpwns/cve-2026-62183
Apache Syncope: User self-service privilege escalation
 0xmrma/cve-2026-42089
A local package installation helper trusted caller-supplied package names too much. In yeoman-environment, missing generators could be installed…
 dannyendortest/gin-vulnerable
Demo consumer for gin v1.7.0 (CVE-2023-29401) — Context.FileAttachment with user input. endorctl scan target.