

brakeman
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
code-analysisdevsecopsstatic-analysis+2
7.3k2 days ago
presidentbeef/brakemanA static analysis security vulnerability scanner for Ruby on Rails applications
 0x-nope/cve-2019-12180
Advisory and proof of concept for CVE-2019-12180, demonstrating arbitrary Groovy code execution in SoapUI and ReadyAPI via malicious project files.
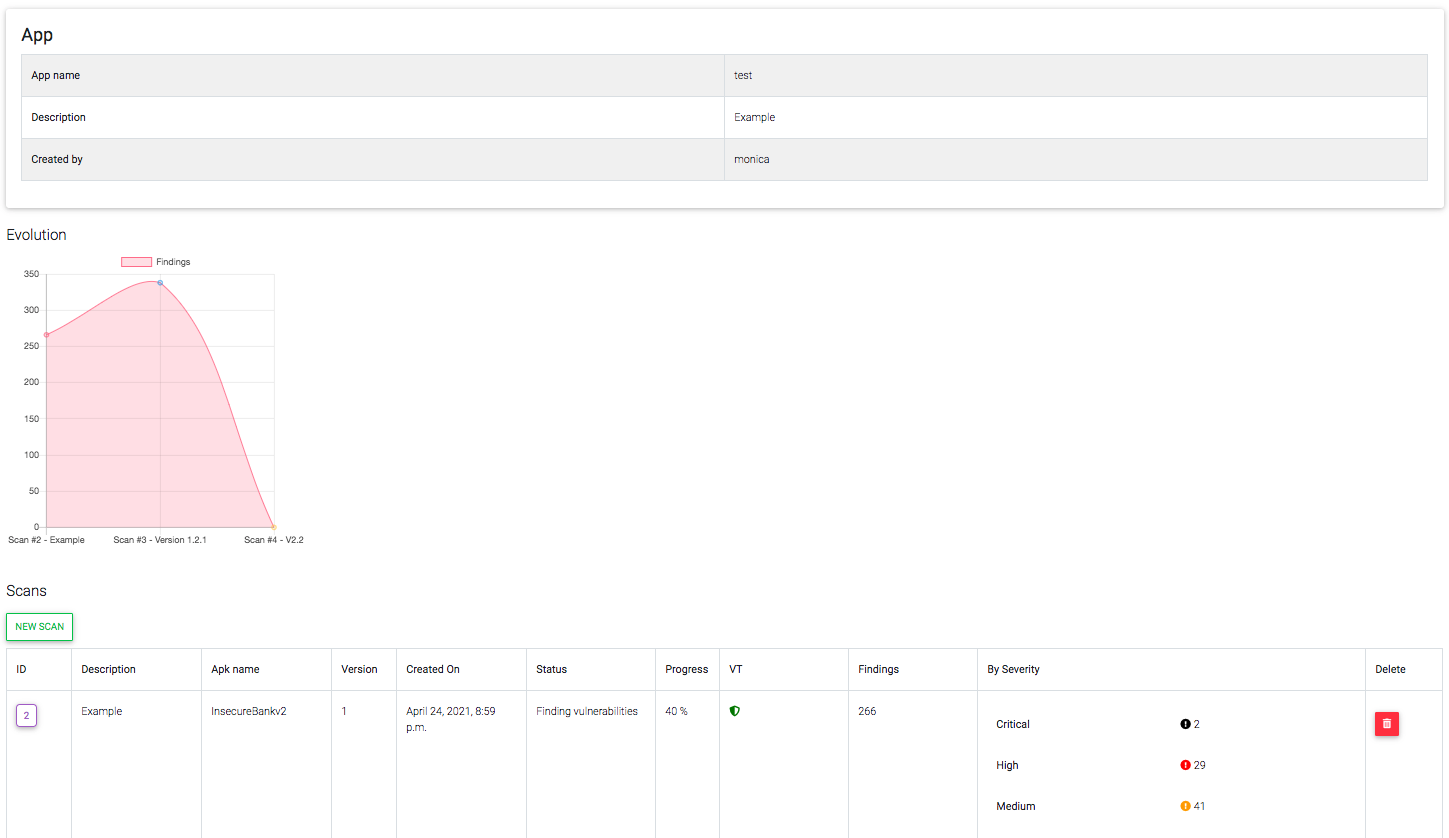 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
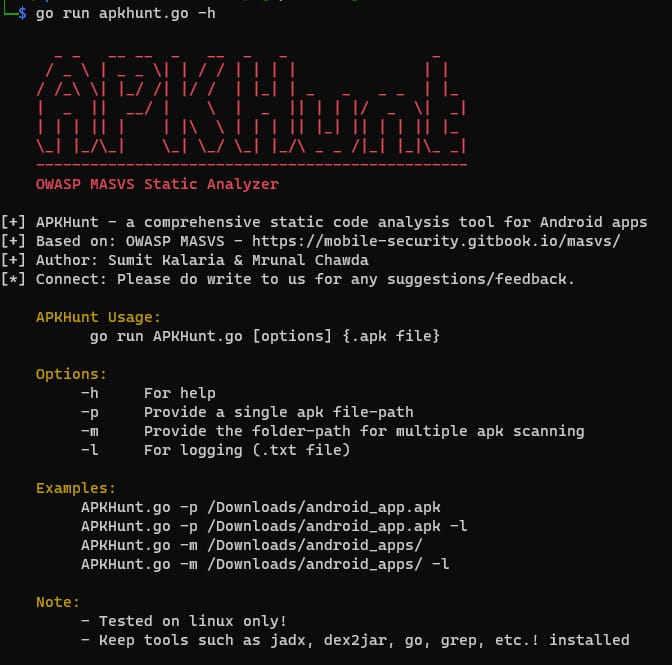 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 huhusmang/awesome-llms-for-vulnerability-detection
The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…
 giovannigatti/cve-bench
A benchmark for evaluating AI agents on fixing real-world security vulnerabilities.
 dexsemon/cve-2026-27495
Proof-of-concept exploit and lab environment for CVE-2026-27495
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 barroqueiro/cve-2023-37941
Exploit on the default cache of superset by using pickle
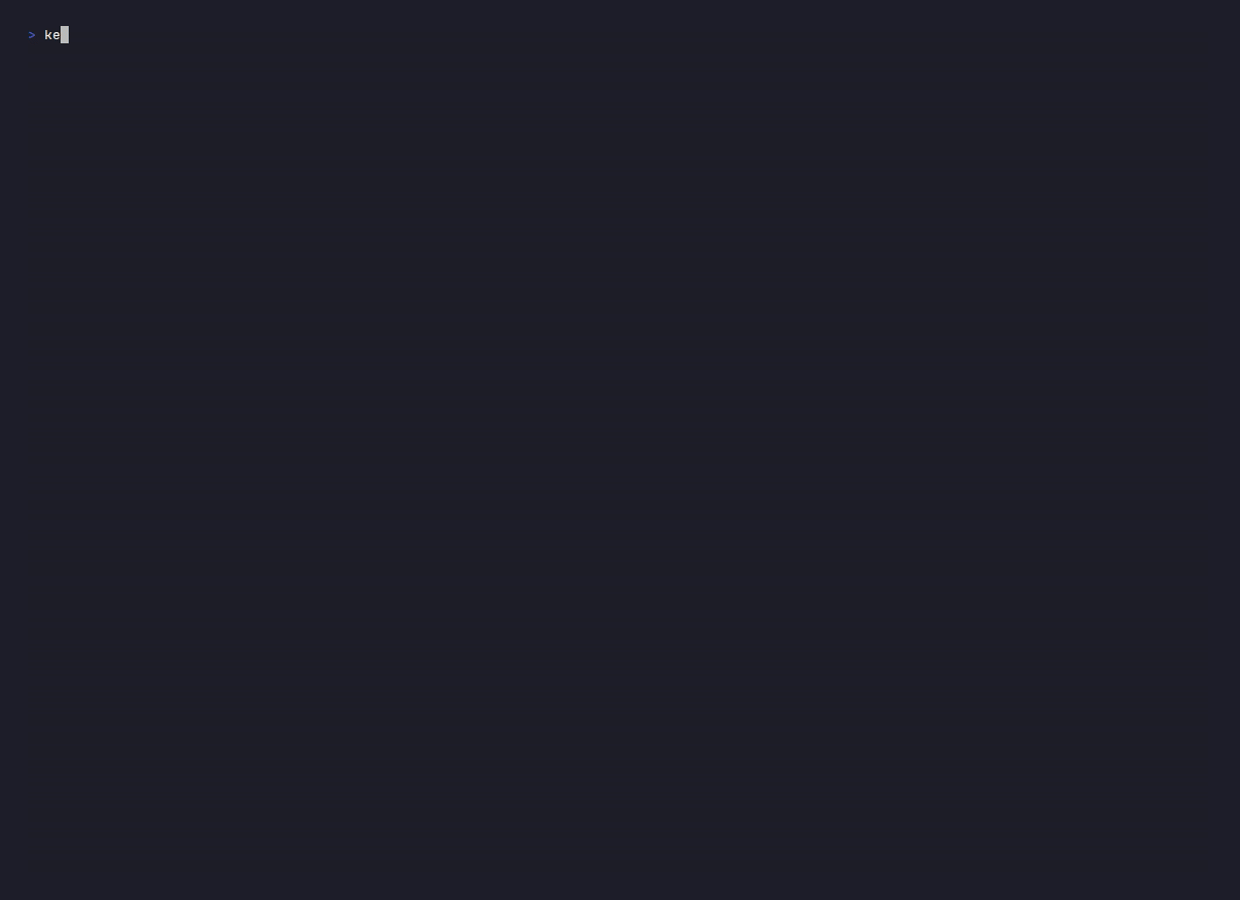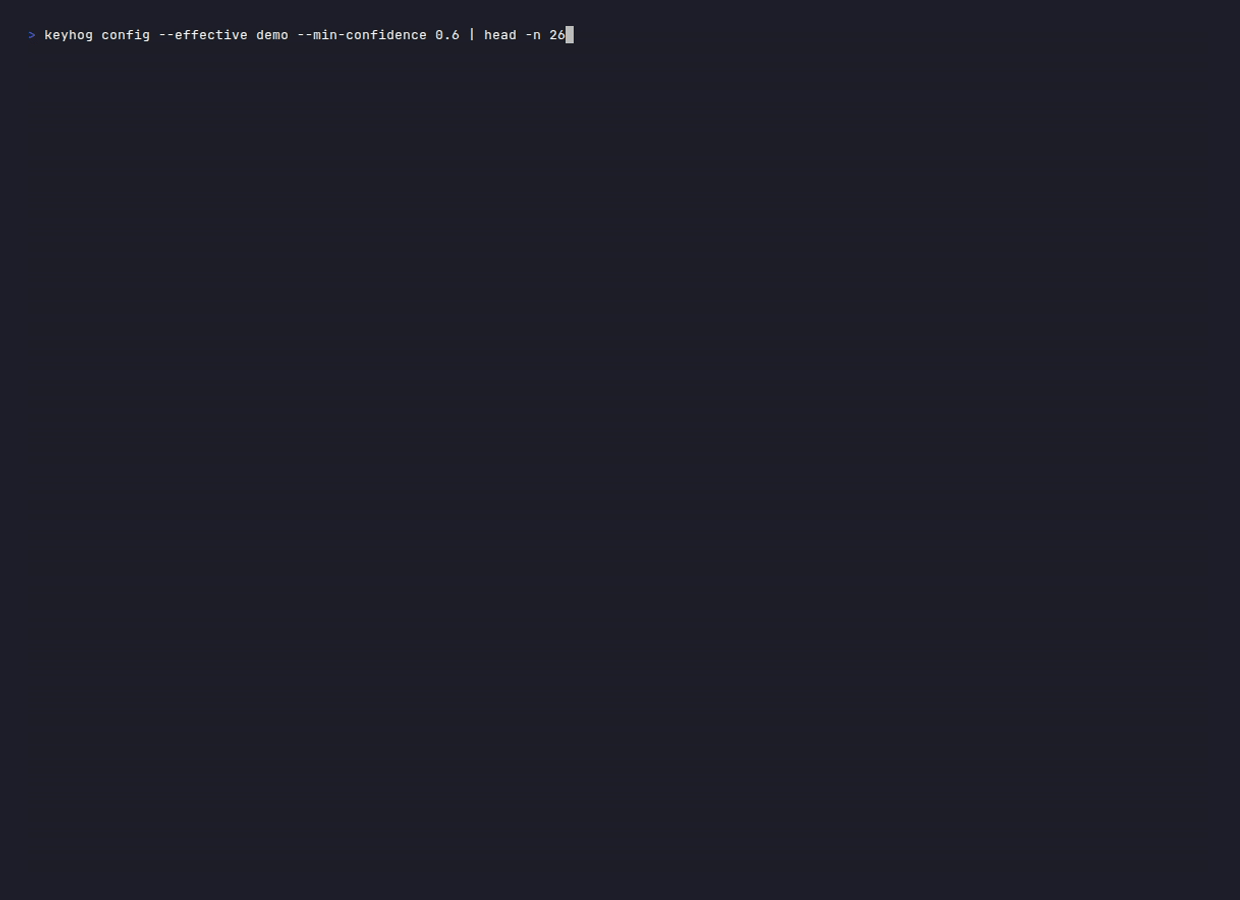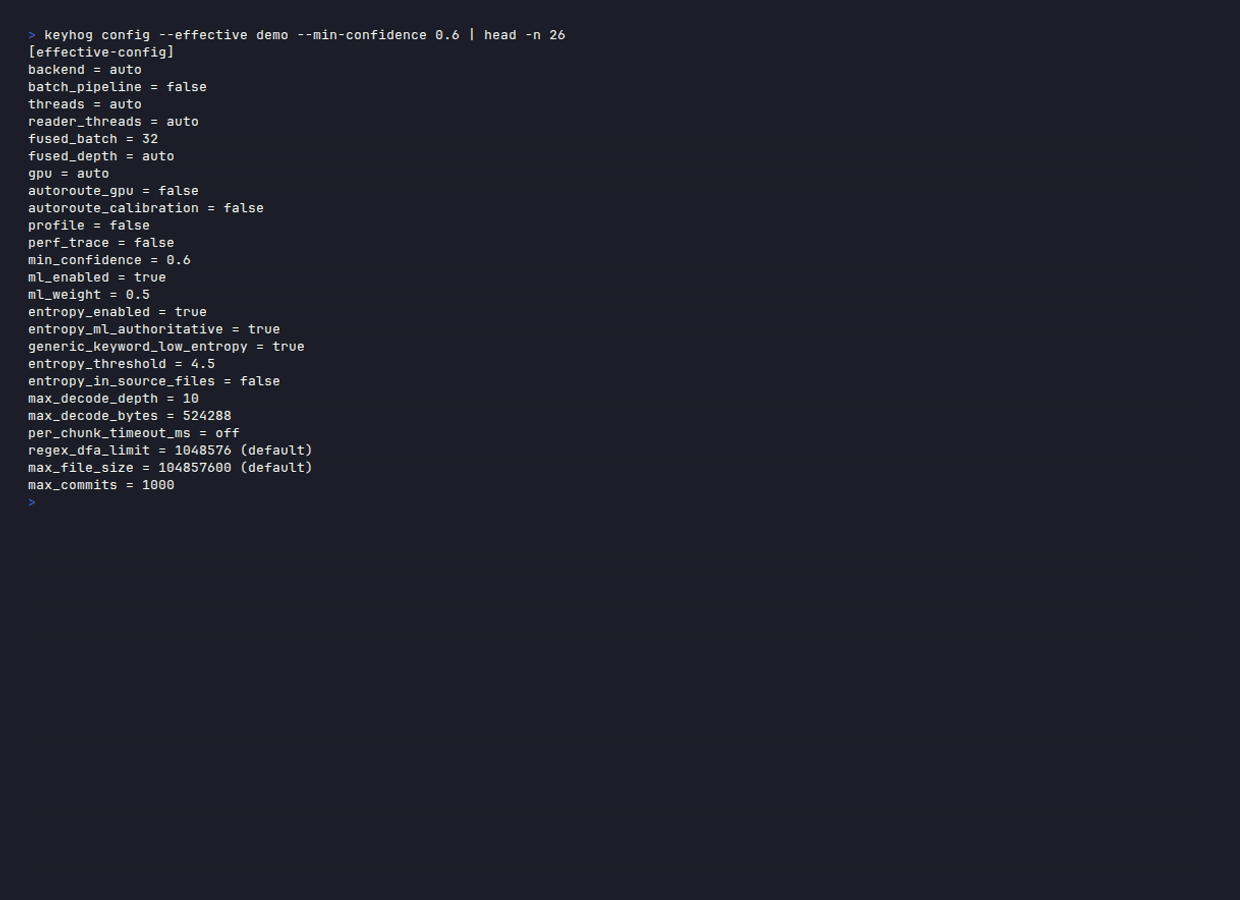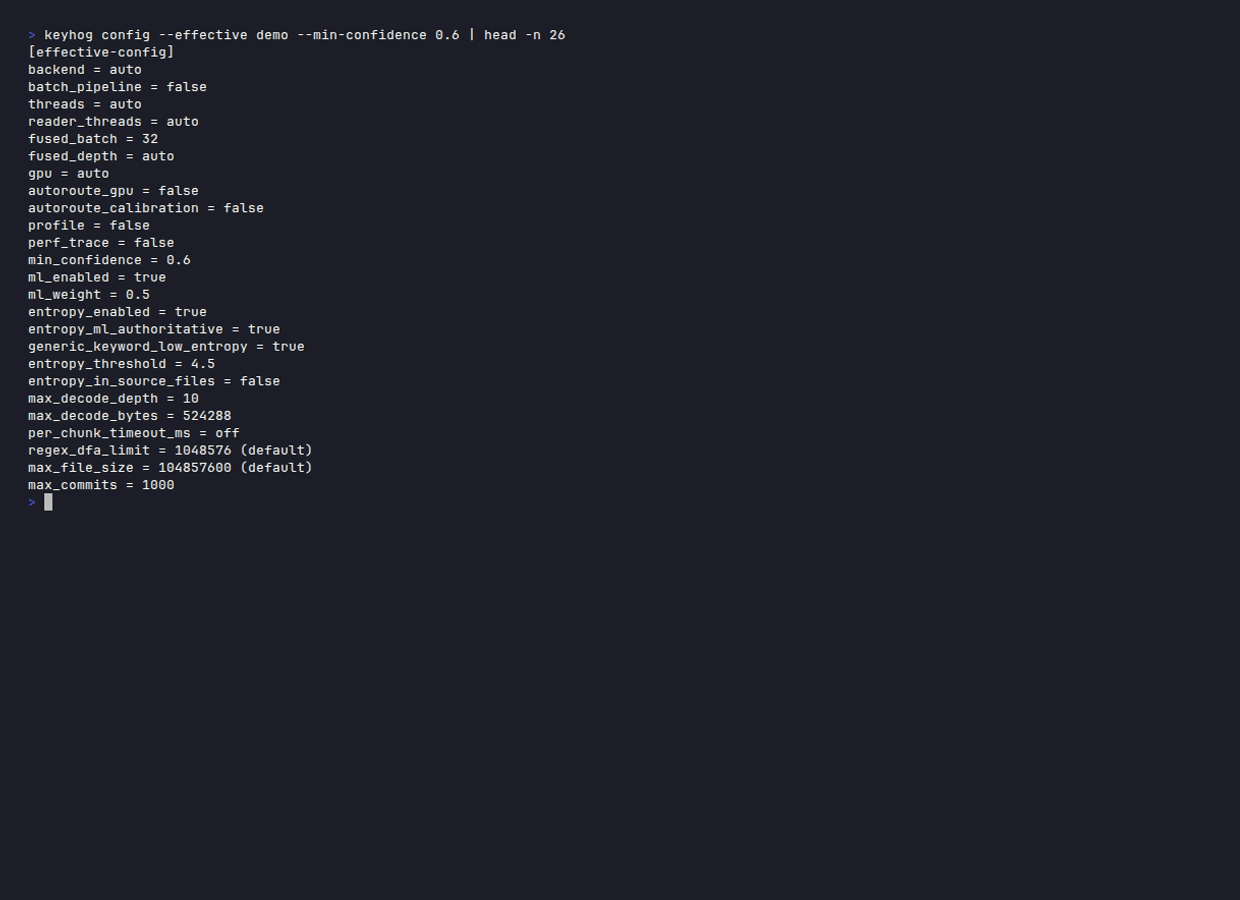 santhreal/keyhog
Open-source secret scanner in Rust
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
 falconkei/snakeyaml_cve_poc
SnakeYAML-CVE-2022-1471-POC
 yadhukrishnam/cve-2026-25053
Vulnerabilities in the Git node allowed authenticated users with permission to create or modify workflows to execute arbitrary system commands or…
 abdurahmon3236/-cve-2024-31211
Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.
 zinja-coder/jadx-ai-mcp
Plugin for JADX to integrate MCP server
 mhaskar/bughound
Static code analysis tool based on Elasticsearch