Jenkins_CVE-2019-1003000

PoC exploit for Jenkins Script Security Pipeline plugin remote code execution vulnerability (CVE-2019-1003000), implemented in Python for penetration…

PoC exploit for Jenkins Script Security Pipeline plugin remote code execution vulnerability (CVE-2019-1003000), implemented in Python for penetration…

Exploit module for Apache JSPWiki CVE-2019-0225, enabling remote code execution via crafted requests. Designed for penetration testing and…

Exploit for Apache Struts CVE-2017-9805, a remote code execution vulnerability in the REST plugin. Enables penetration testing and security…

UNIX-like reverse engineering framework and command-line toolset

Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…

Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…

An easy-to-learn/use static analysis framework for Java and Android

Static taint analysis platform for Android apps that detects vulnerabilities and compliance issues using customizable rule-based scanning and…

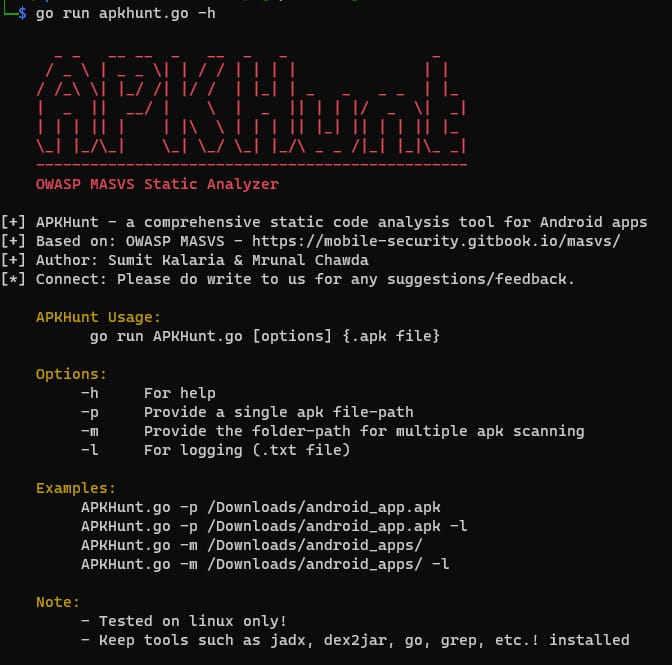
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…

A security focused static analysis tool for Android and Java applications.

mobsfscan is a static analysis tool that can find insecure code patterns in your Android and iOS source code. Supports Java, Kotlin, Swift, and…

MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…

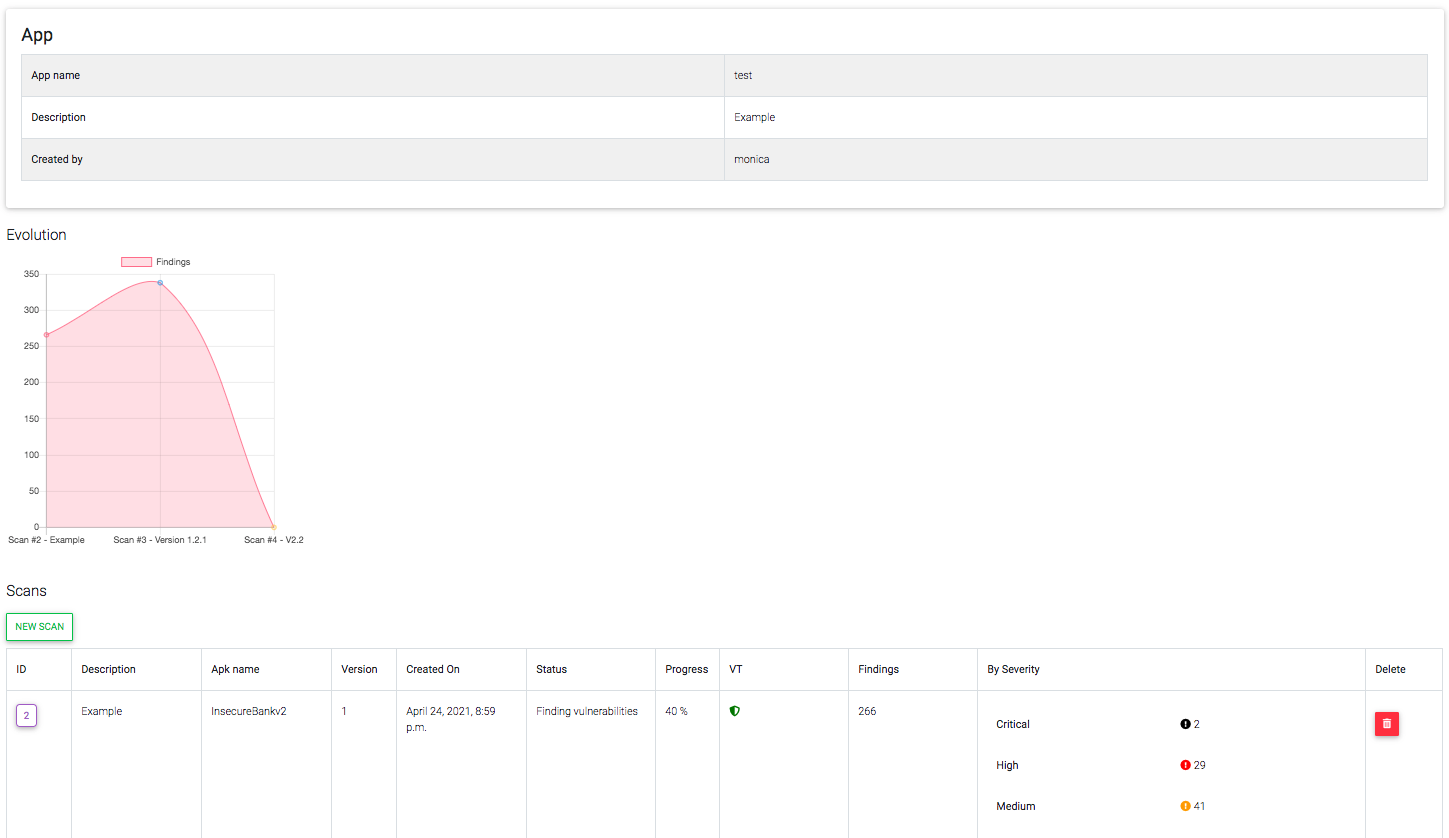
Django application that performs SAST and Malware Analysis for Android APKs

Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…

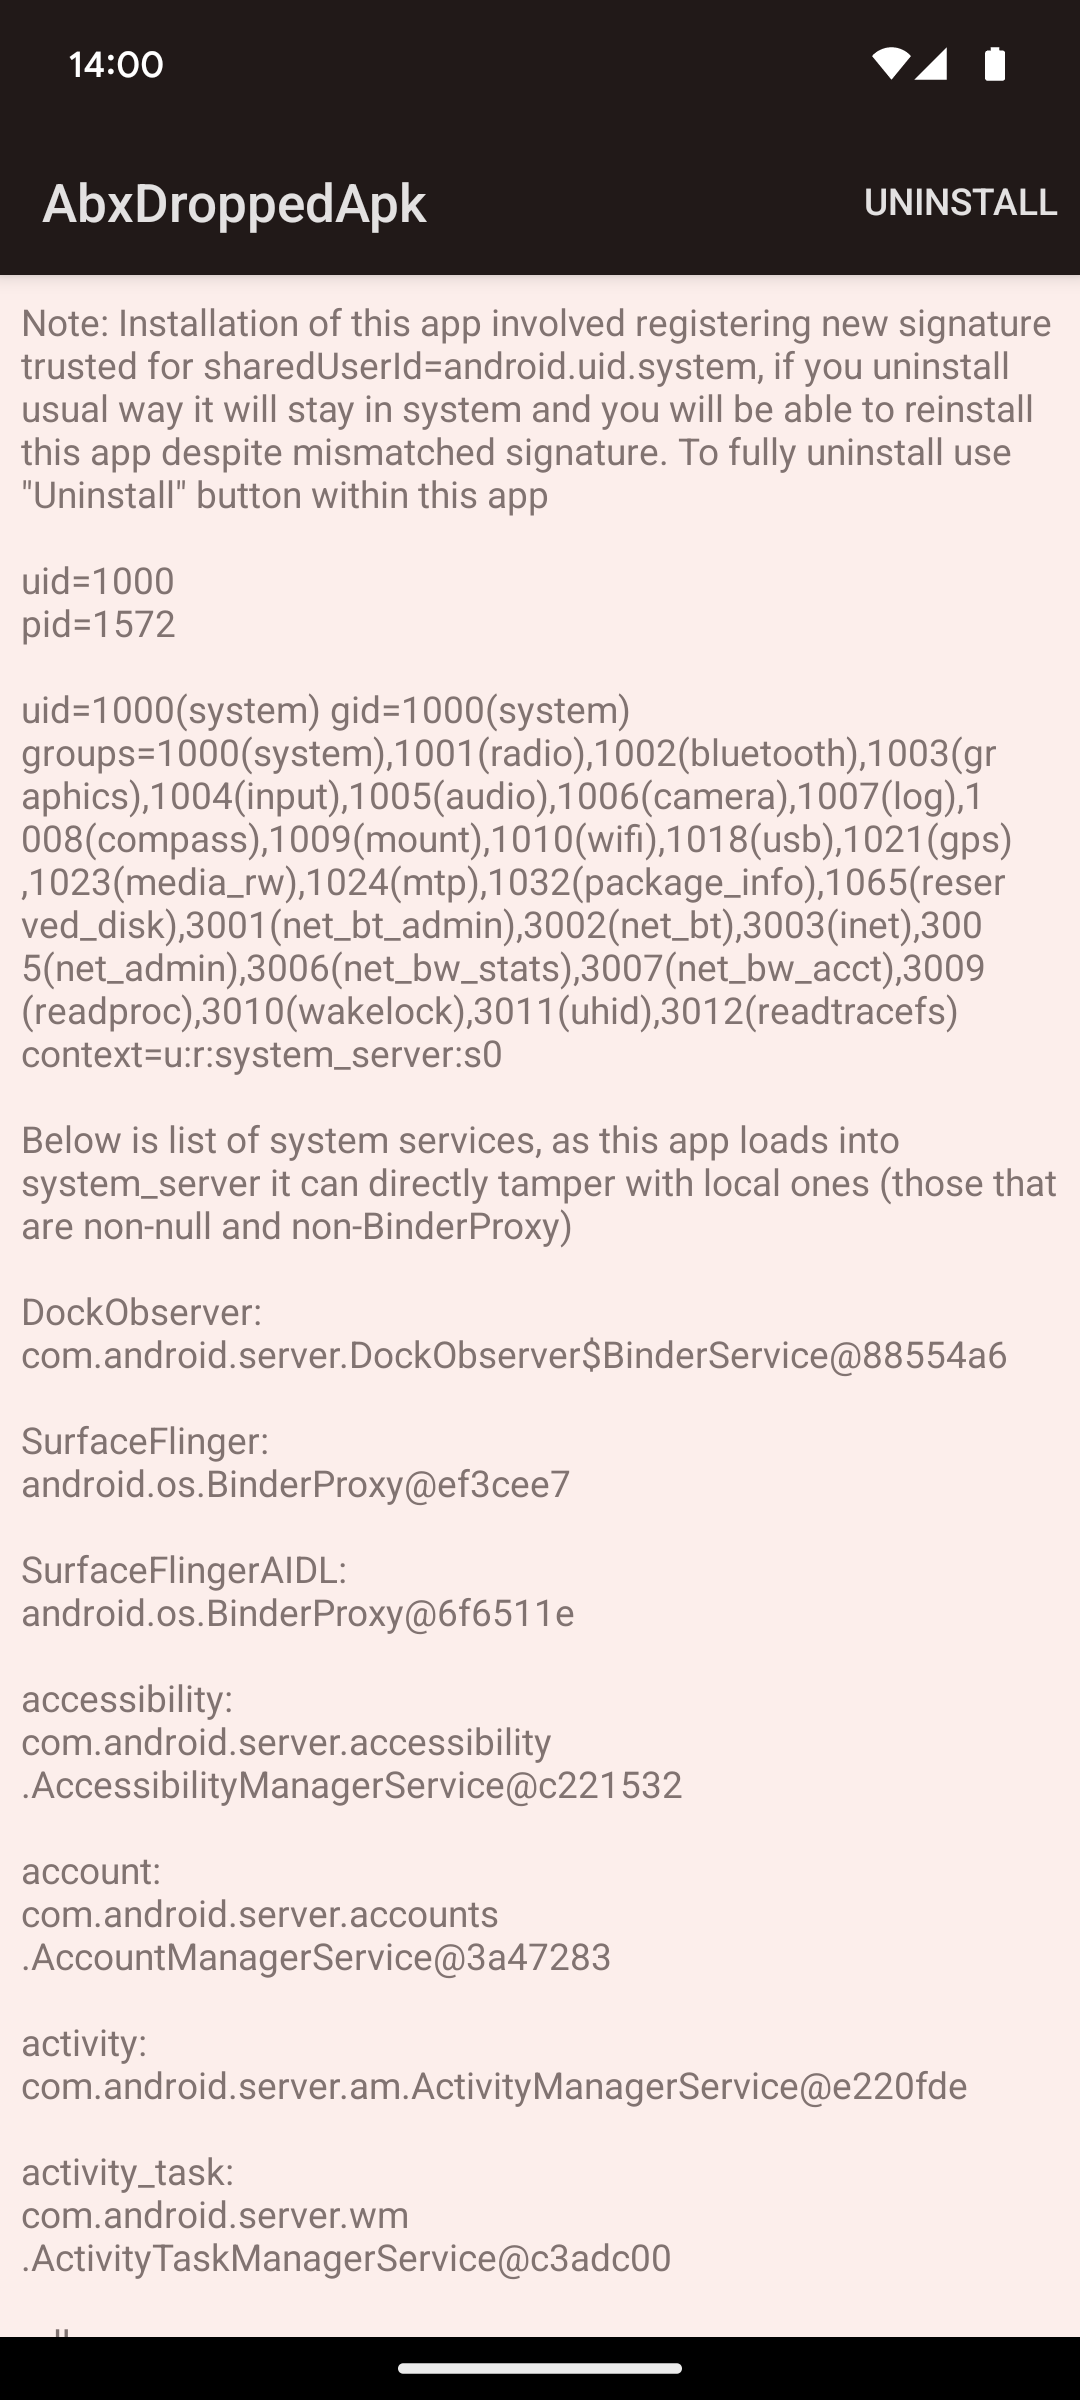
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…

A native APK and DEX decompiler written in Rust

Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…

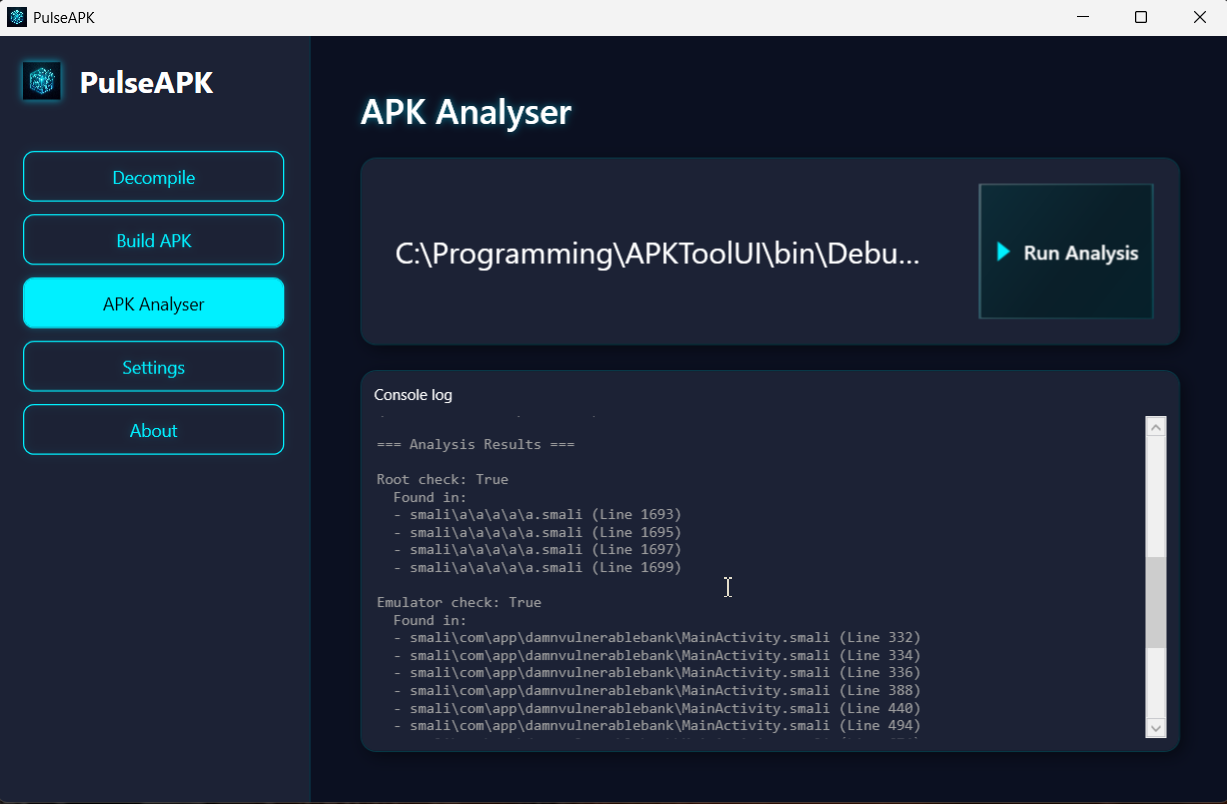
PulseAPK is a WPF frontend for apktool and uber-signer with drag-and-drop support, live decompilation output, smali analysis, and integrated APK…