
SecureAI-Scan
 akanthed/secureai-scan
SecureAI-Scan is a CLI tool that scans TypeScript and JavaScript codebases for security issues specific to AI-powered apps — prompt injection, MCP…
ai-securitycode-analysisdevsecops+5
22
akanthed/secureai-scanSecureAI-Scan is a CLI tool that scans TypeScript and JavaScript codebases for security issues specific to AI-powered apps — prompt injection, MCP…
 razi-interactive/claude-project-scanner
Read-only safety scanner for Claude Code projects. Catches CVE-2025-59536, statusLine injection, prompt injection, and more.
 ethiack/cve-2023-29007
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation via crafted repository…
 jricramc/aigate
AI Prompt Secret Scanner: local proxy and Claude Code hook that blocks secrets before they reach AI APIs
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 trickstersec/cve-2019-5420
Exploit for the Rails CVE-2019-5420
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
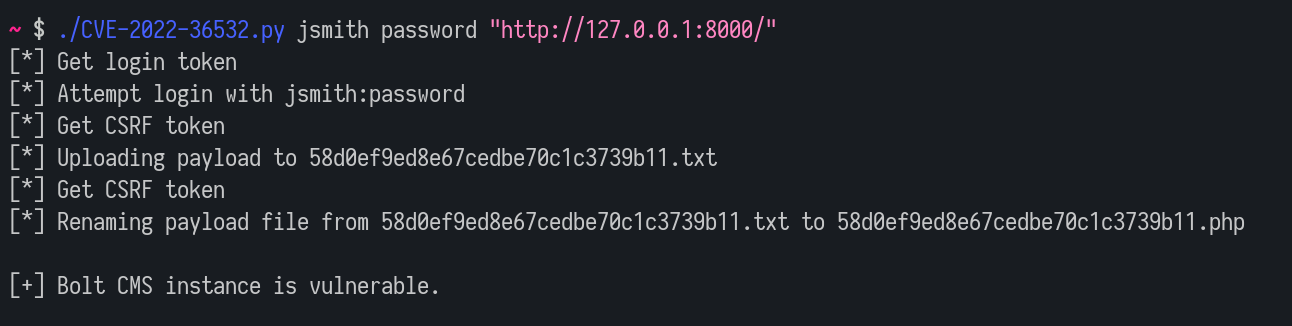 lutrasecurity/cve-2022-36532
Proof-of-concept exploit script for CVE-2022-36532 enabling authenticated remote code execution via file upload in Bolt CMS 5.1.12 and below.
 ludovicpatho/cve-2022-22965_spring4shell
A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 brianwrf/wordpress_4.9.8_rce_poc
A simple PoC for WordPress RCE (author priviledge), refer to CVE-2019-8942 and CVE-2019-8943.

 d0n601/cve-2025-9216
StoreEngine – Powerful WordPress eCommerce Plugin for Payments, Memberships, Affiliates, Sales & More <= 1.4.0 - Authenticated (Subscriber+)…
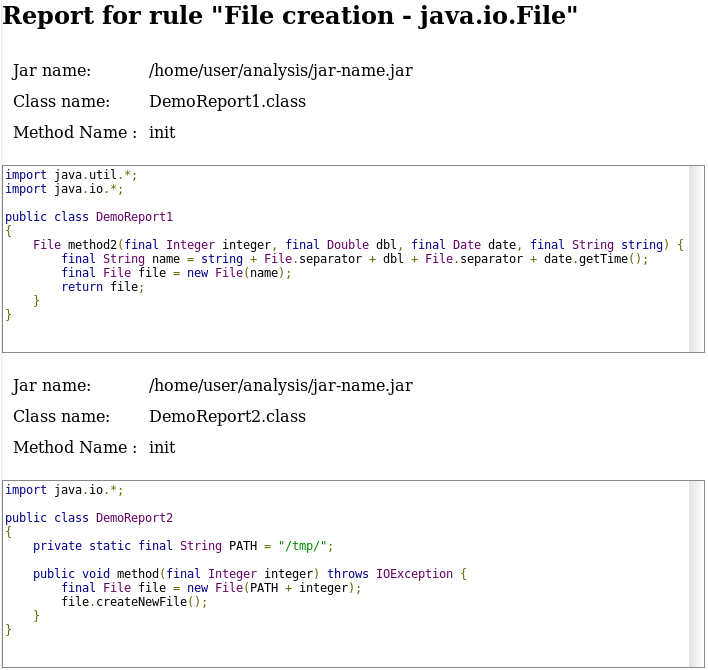 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules