

JAW
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
code-analysiscrawlerdatabase-security+5
soheilkhodayari/jawJAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 security-phoenix-demo/mongobleed-exploit-cve-2025-14847
Exploit lab, docker and code scanner for mongobleed Vulnerability CVE-2025-14847 plus Phoenix Security Sync tools
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
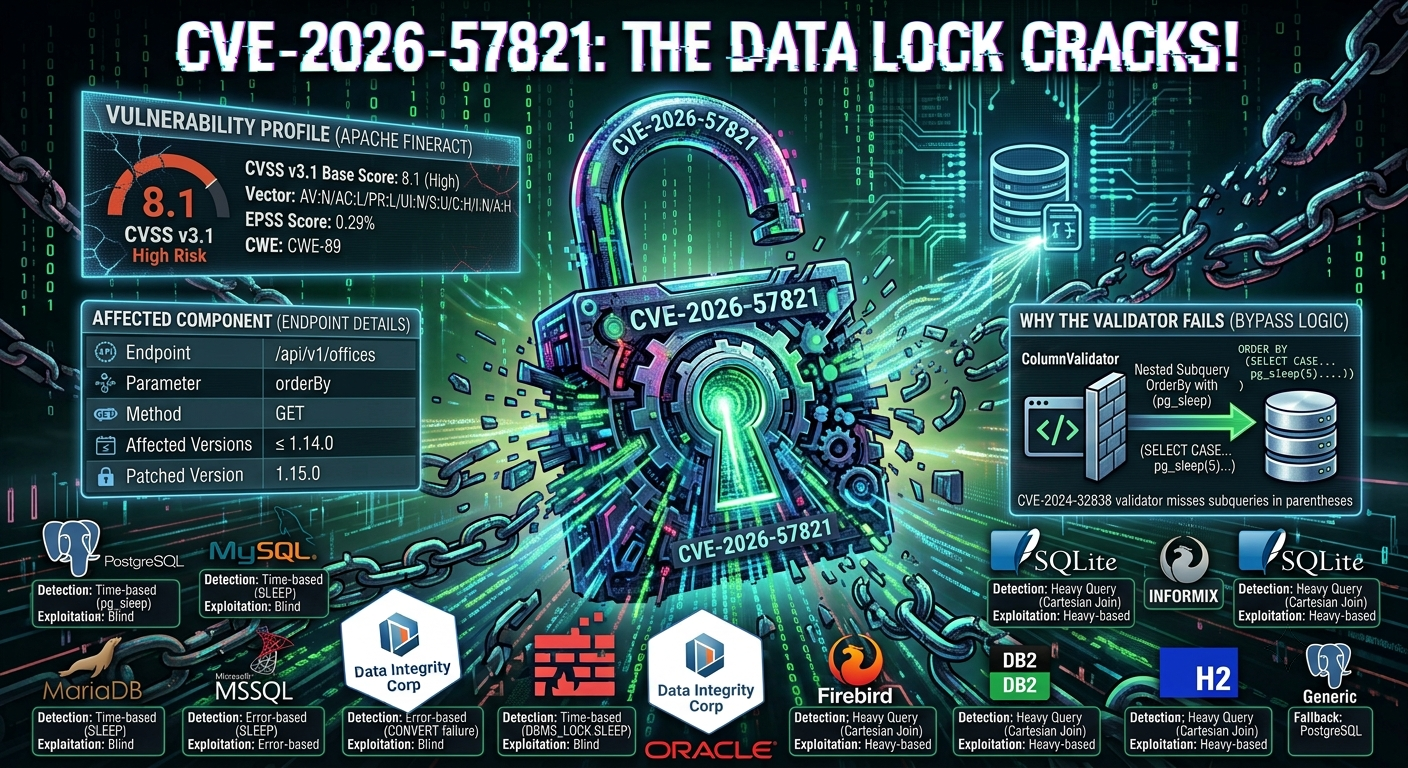 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 osvaldotenorio/cve-2024-48325
Proof-of-concept for SQL injection in Portabilis i-Educar 2.8.0, demonstrating unauthenticated database access via the getDocuments endpoint with…
 savagesanta11/reproduce-cve-2024-21513
Demonstrates CVE-2024-21513 in langchain-experimental, showing arbitrary code execution via VectorSQLDatabaseChain's eval() on retrieved values.…
 murataydemir/cve-2022-22980
[CVE-2022-22980] Spring Data MongoDB SpEL Expression Injection
 nulldreams/cve-2017-16082
NodeJS + Postgres (Remote Code Execution) 🛰
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
 oscerd/cve-2026-46591
Reproducer for CVE-2026-46591: Apache Camel camel-neo4j Cypher injection via property names in CamelNeo4jMatchProperties, enabling authorization…
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 seccoder-security-lab/jdbc-sqlxml-xxe
h2-jdbc(https://github.com/h2database/h2database/issues/3195) & mysql-jdbc(CVE-2021-2471) SQLXML XXE vulnerability reproduction.
 romain-deperne/cve-2026-33980
KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3
 drunkenshells/cve-2021-2471
PoC for CVE-2021-2471 - XXE in MySQL Connector/J
 romain-deperne/cve-2026-32247
Cypher injection in Graphiti via unsanitized node_labels — CVE-2026-32247 / CVSS 8.1
 zhaoqi99/cve-2022-34265
PoC for CVE-2022-34265