
sast-scan
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
cloud-securitycode-analysisconfiguration-auditing+6
883
shiftleftsecurity/sast-scanScan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 disruptops/cred_scanner
A simple file-based scanner to look for potential AWS access and secret keys in files
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
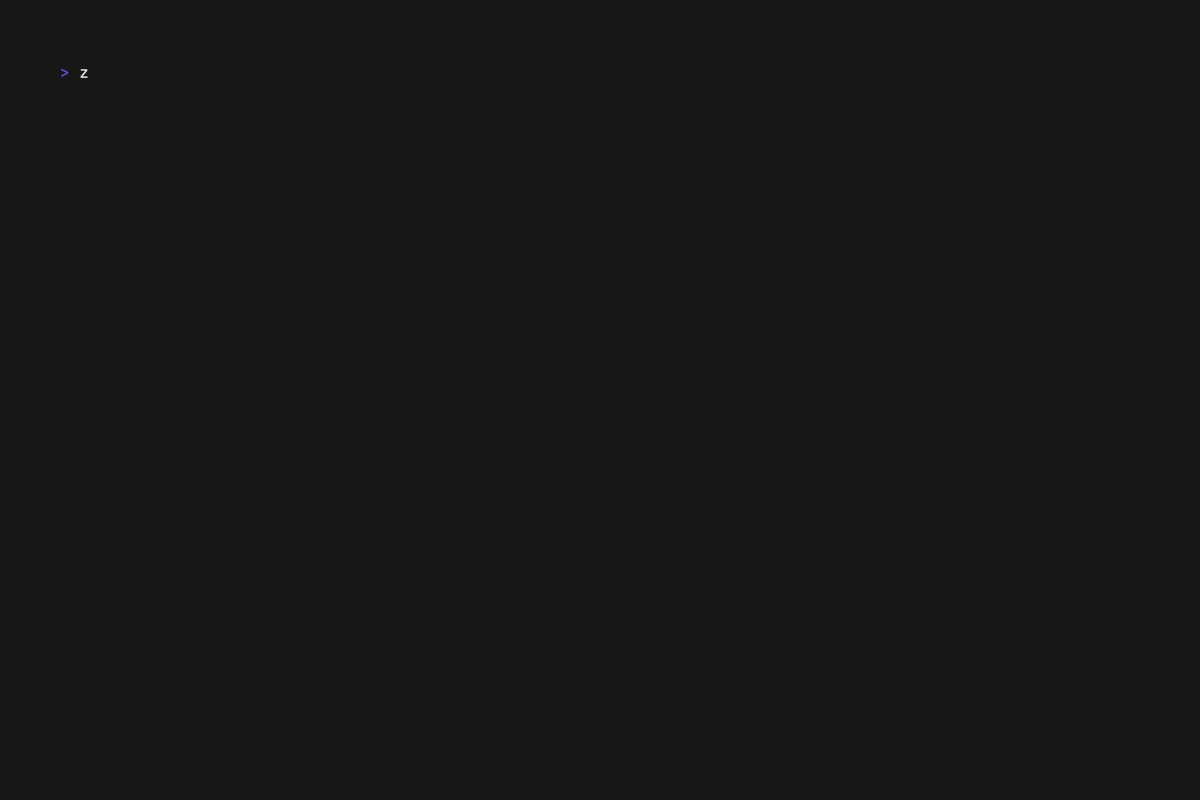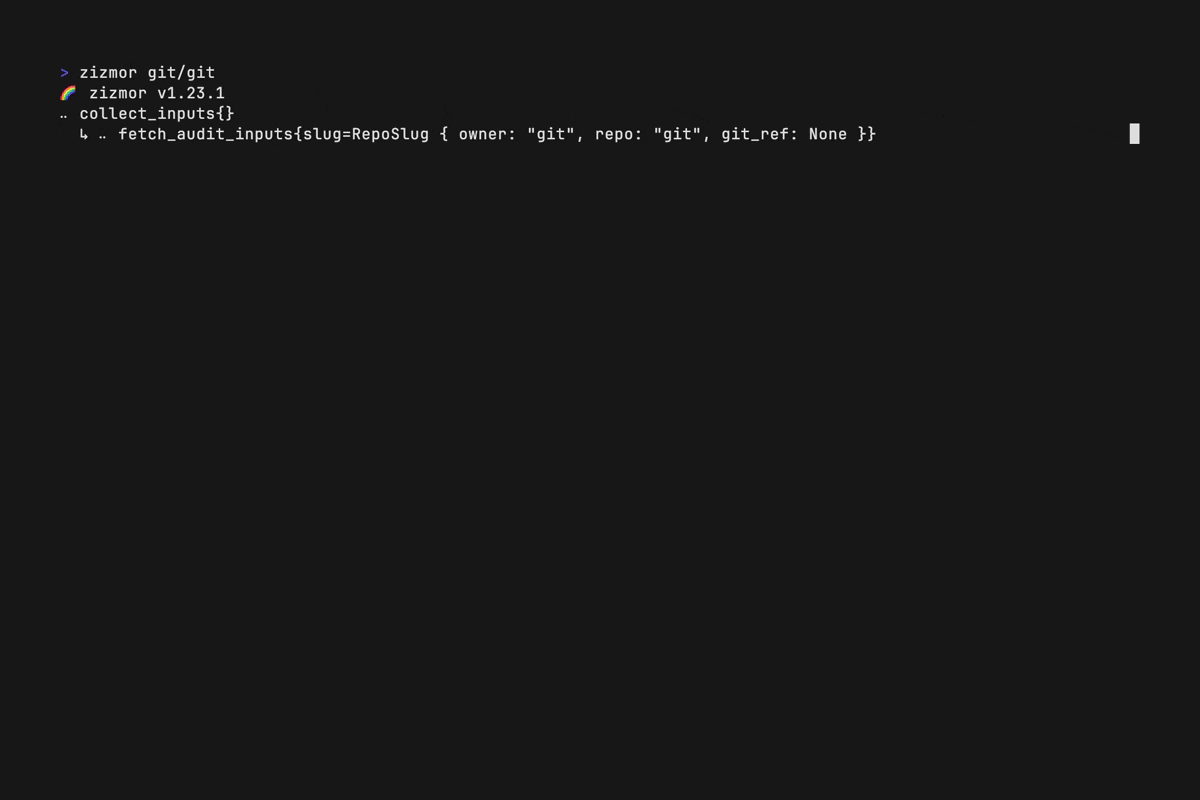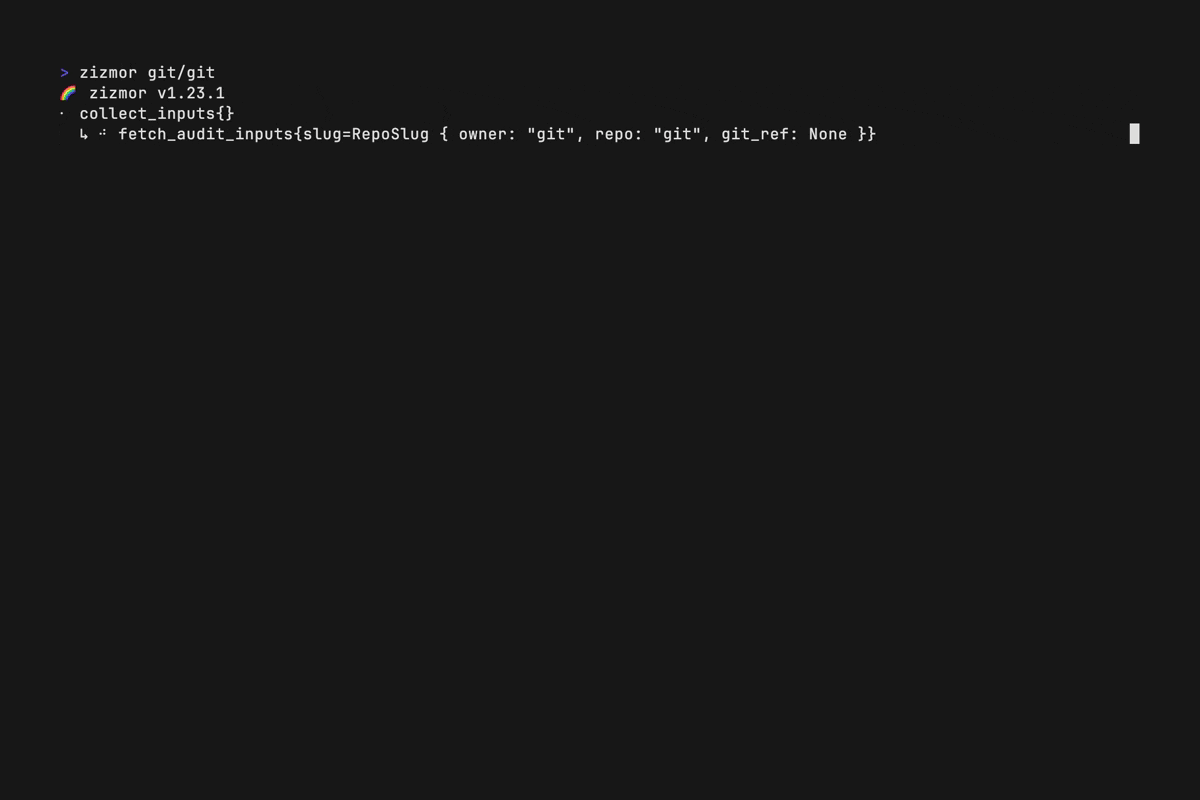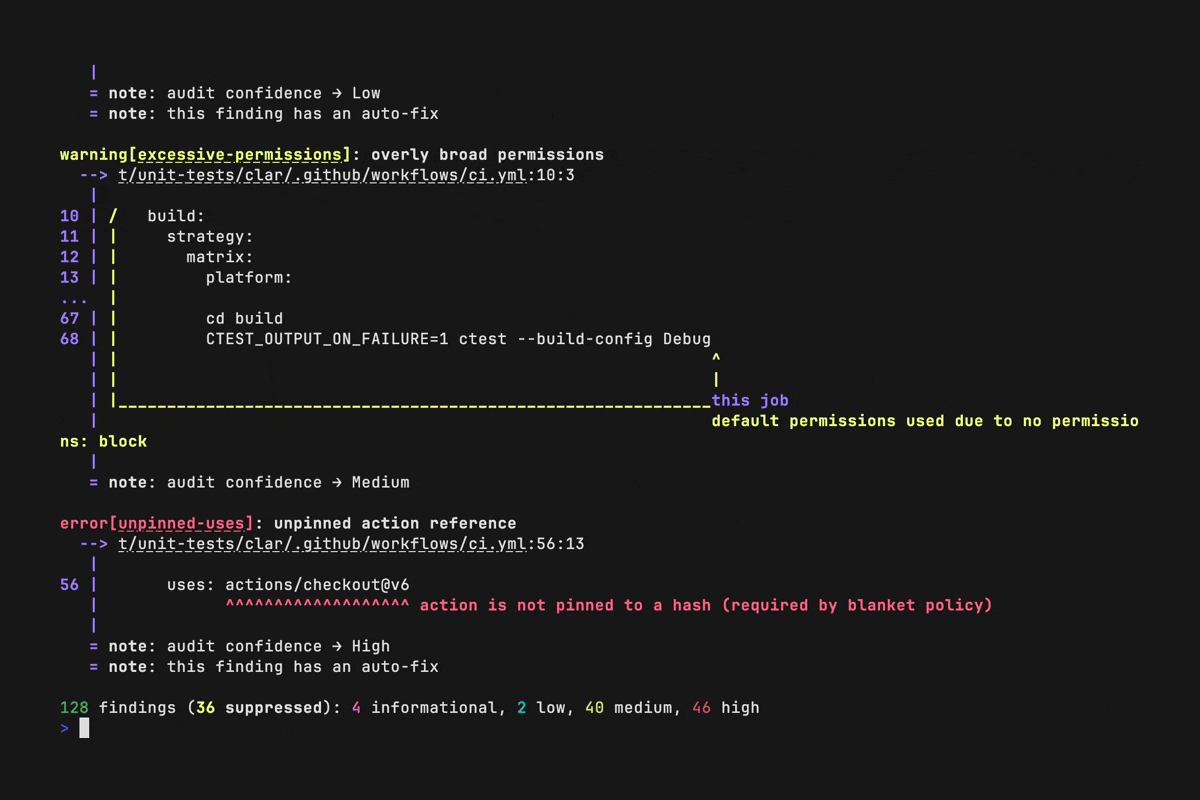 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 reposaur/reposaur
Open source compliance tool for development platforms.
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
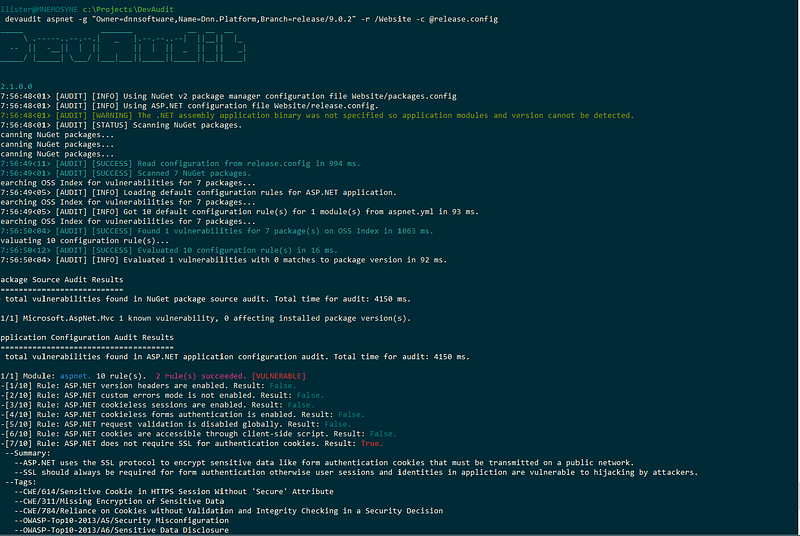 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 s1ko/cve-2026-52617
Advisory and proof-of-concept for OS command injection in an MCP ffmpeg helper, with root-cause analysis, detector guidance, and mitigations for an…
 hazcod/claudleak
Hunt for AI coding artifacts containing secrets.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.