jeremylong__DependencyCheck_CVE-2018-12036_3-1-2

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.

A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…

Apache RAT (Release Audit Tool) Gradle Plugin

Fix for ECDSA and EDDSA signature verification in Wycheproof project, addressing missing length checks that allowed zero-byte manipulation during…

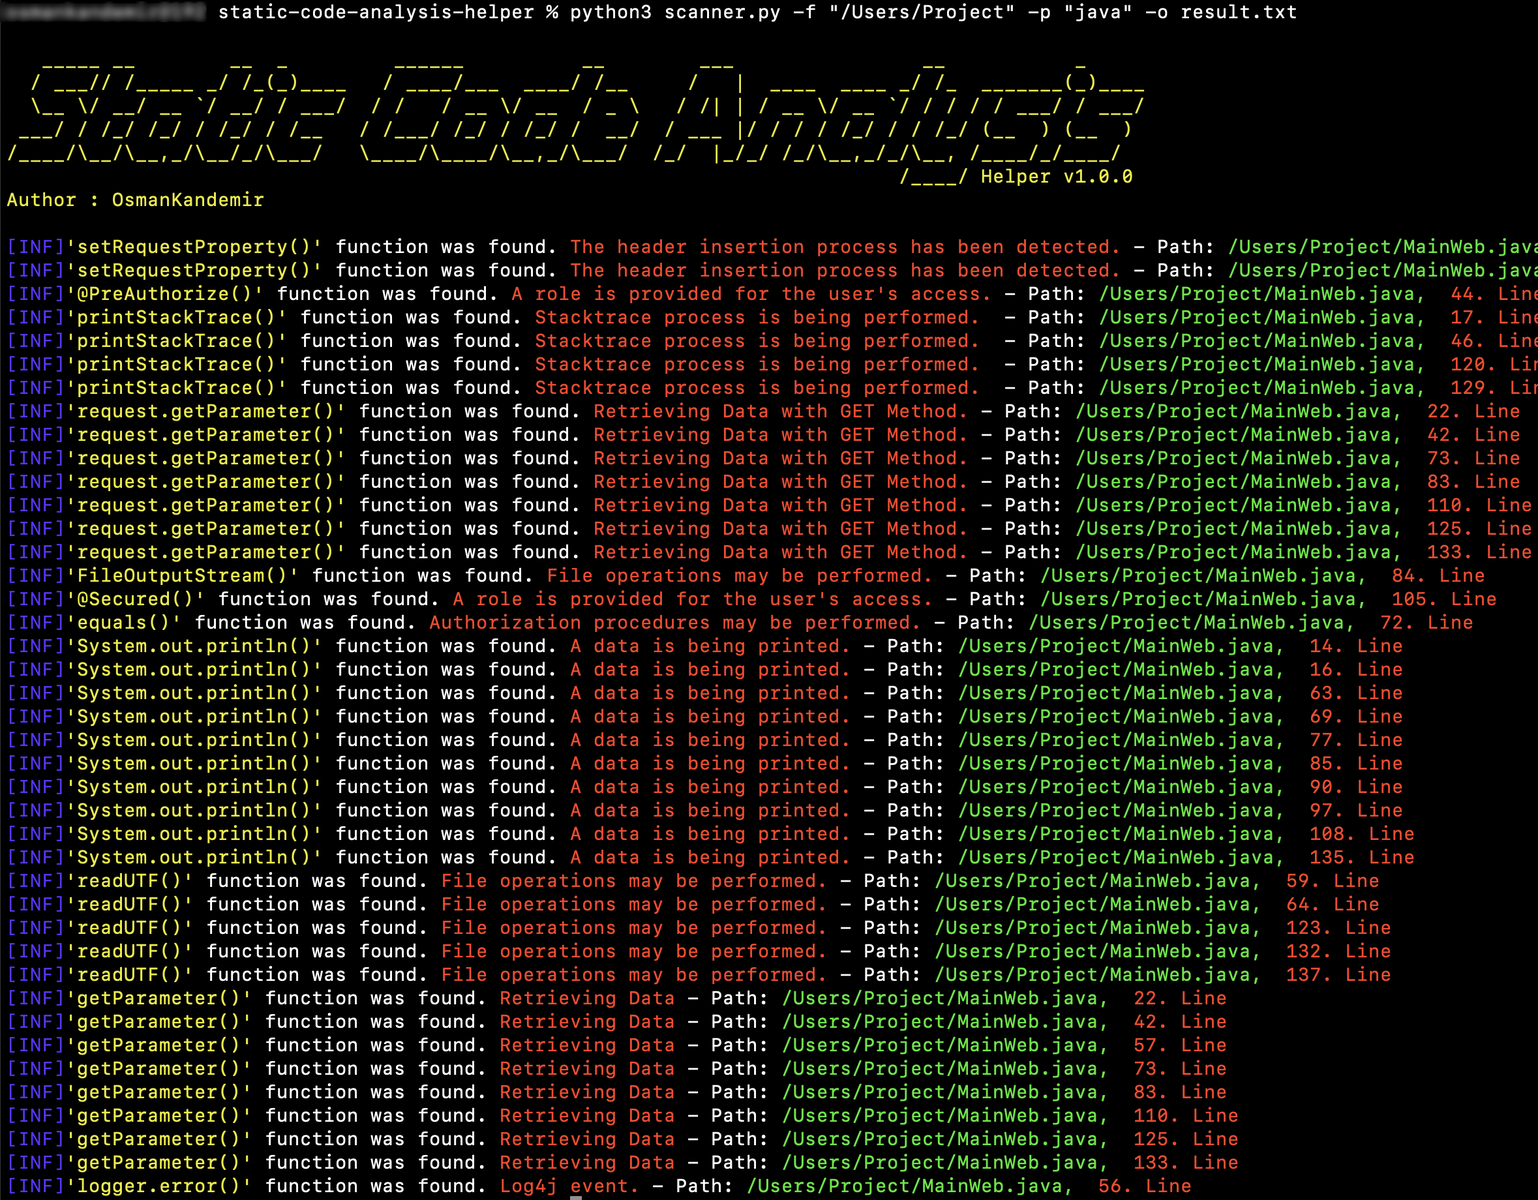
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…

Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…

Community Cryptography Specification Project

AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.

Utilize Tai-e to identify the Log4shell (a.k.a. CVE-2021-44228) Vulnerability

A project security/vulnerability/risk scanning tool


🐺 Vulfy – Fast Rust based package version scanner

Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…

A macOS app to scan Xcode project files for possible security issues.

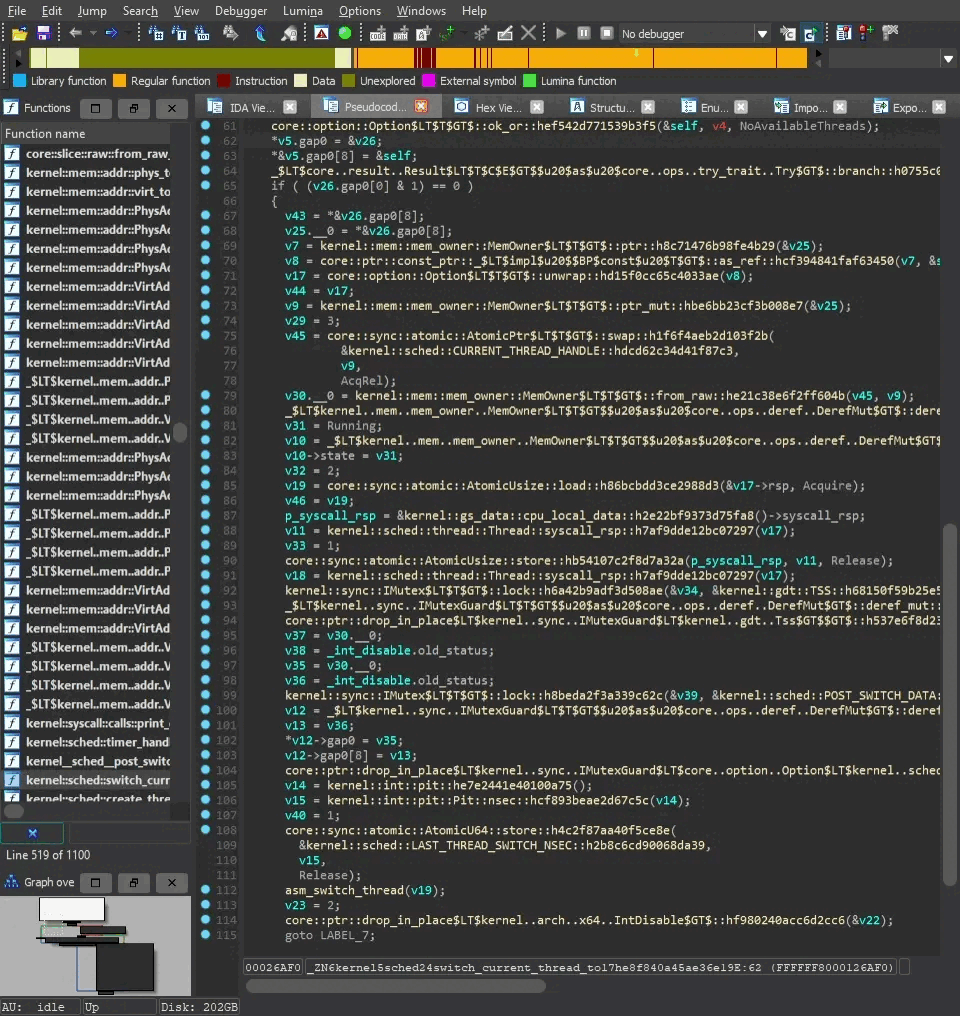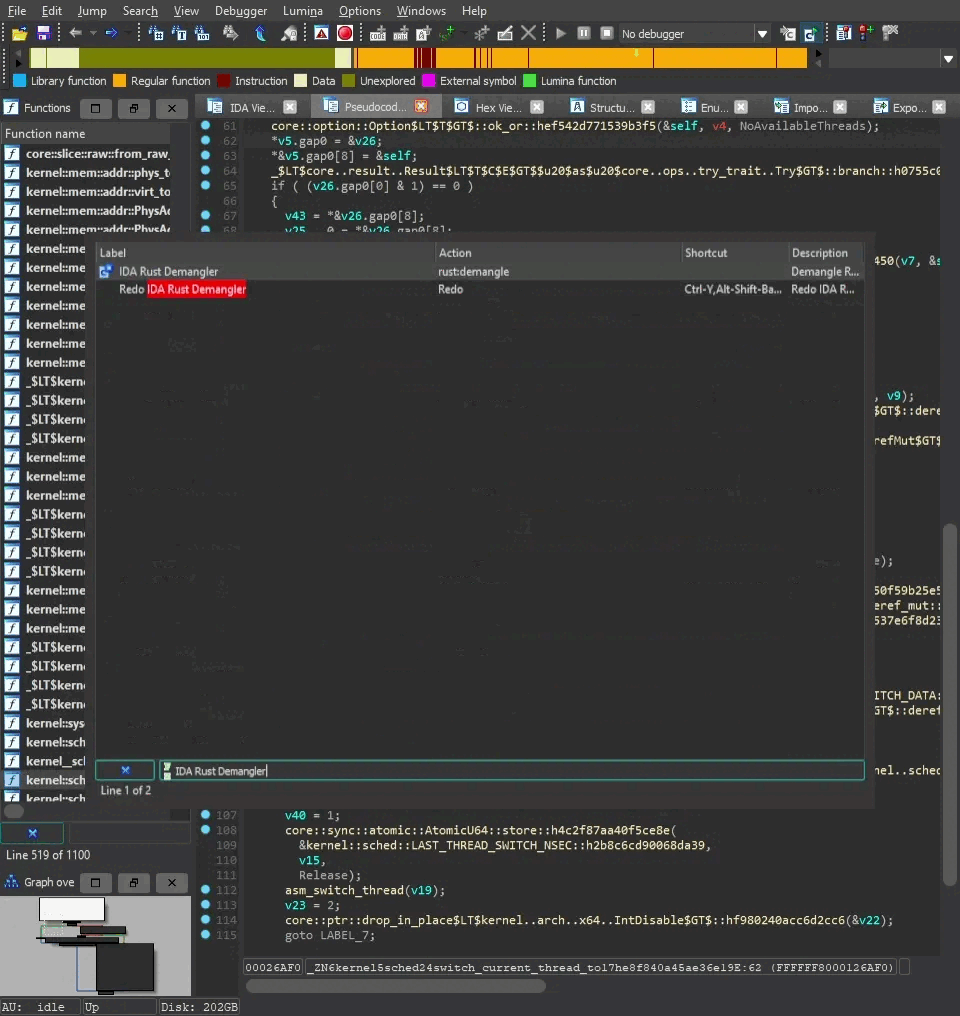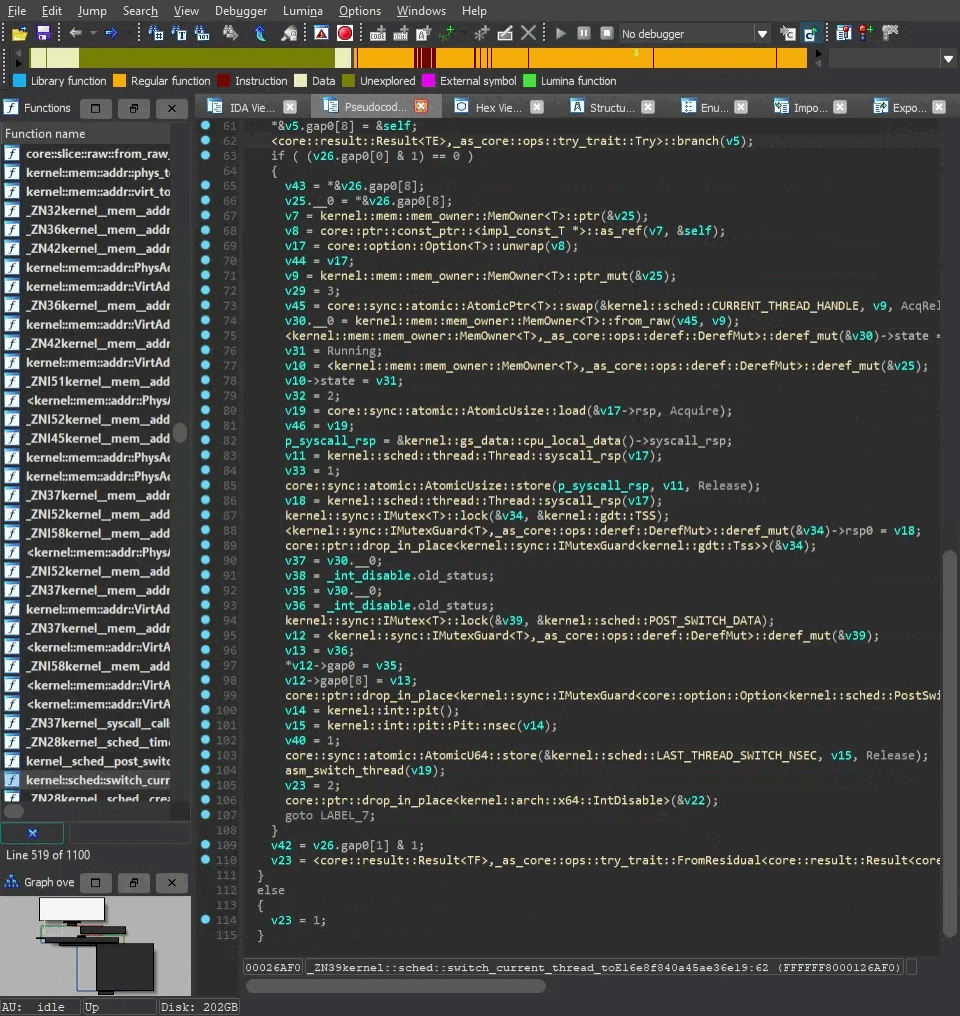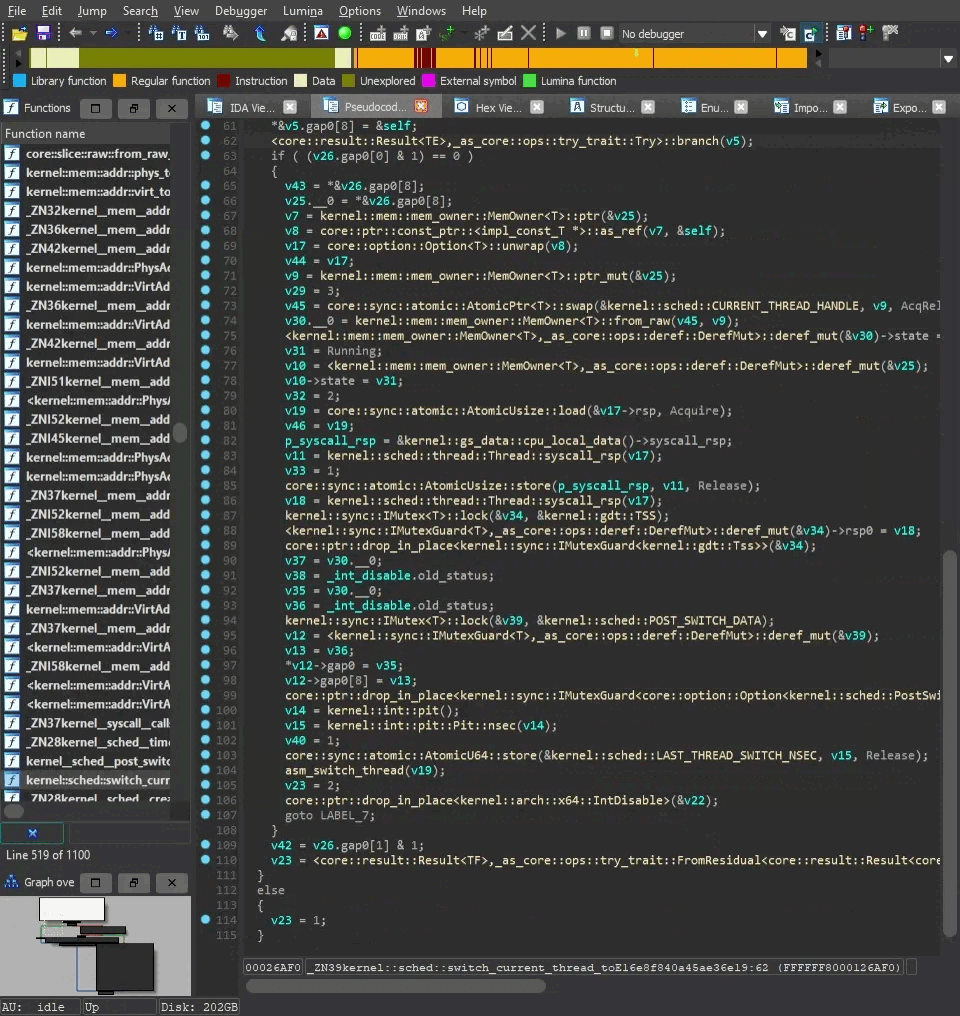
Rust Demangler & Normalizer plugin for IDA

Neto | A tool to analyse browser extensions

Ghidra Extension to integrate BinDiff for function matching