
cwe-tool
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
code-analysiscurated-resourceseducation+3
owasp/cwe-toolA command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 geeksikhsecurity/ai-tool-poisoning-guard
Free security-baseline rule for Claude Code, Codex, and Cursor: treats MCP tool descriptions as untrusted input (OWASP MCP Top 10 MCP03,…
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
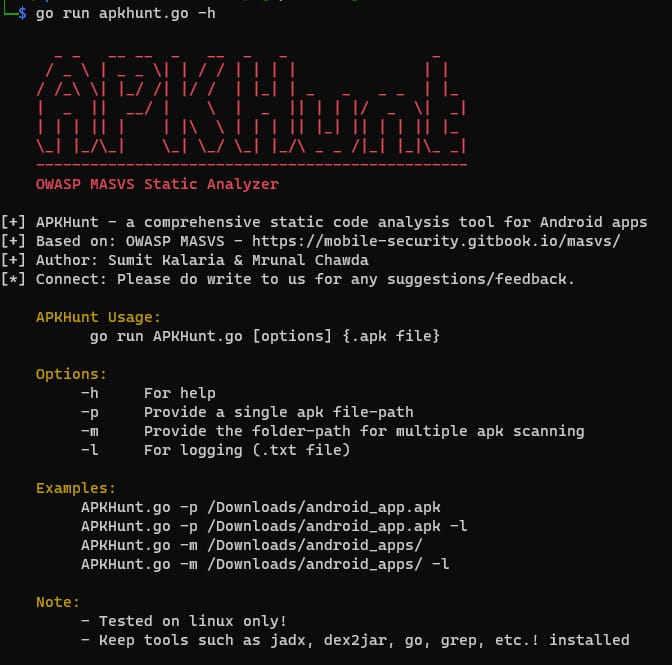 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
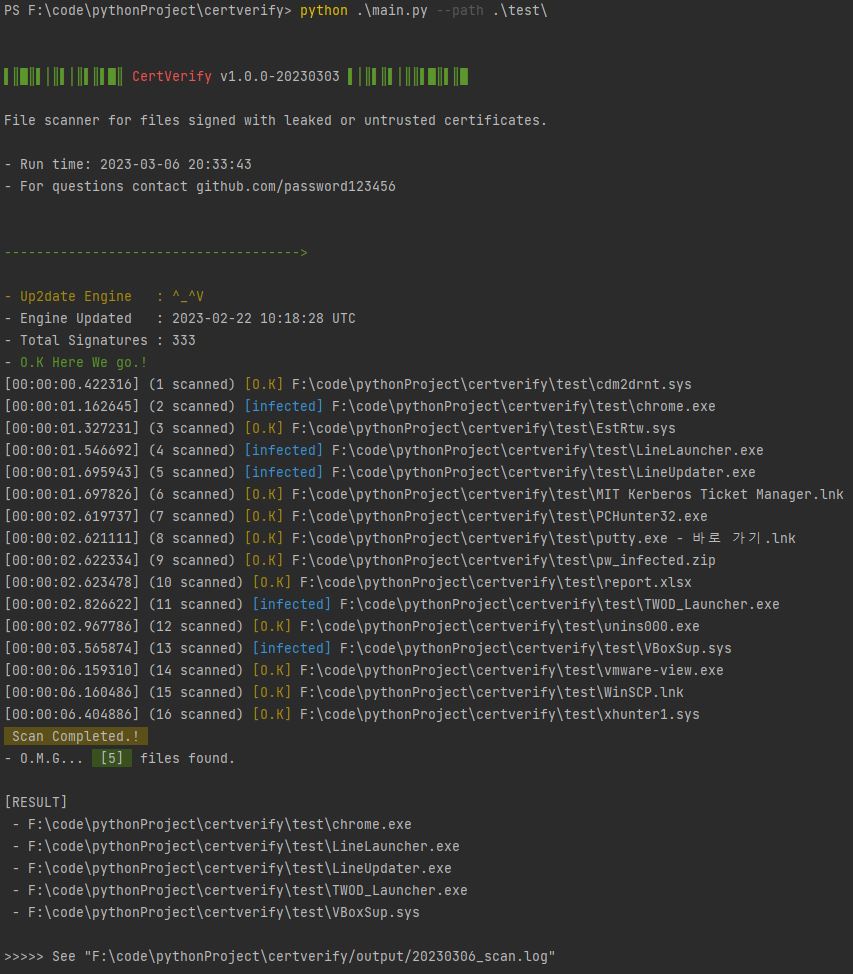 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
 security-code-scan/security-code-scan
Vulnerability Patterns Detector for C# and VB.NET
 owasp/riskassessmentframework
The Secure Coding Framework
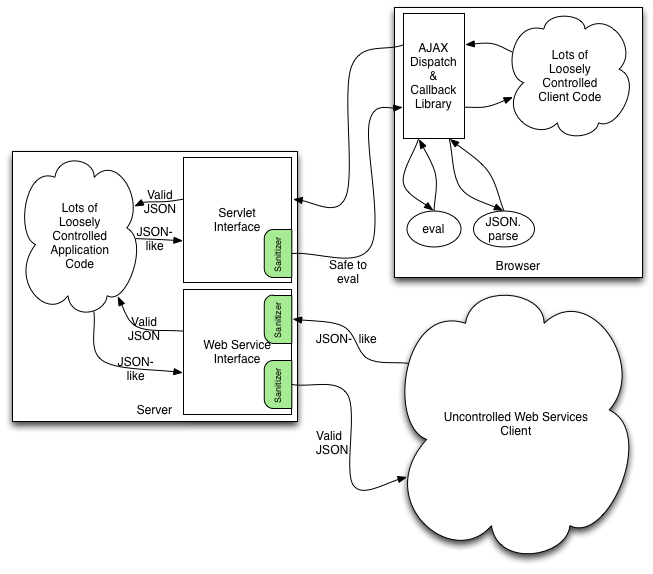 owasp/json-sanitizer
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.
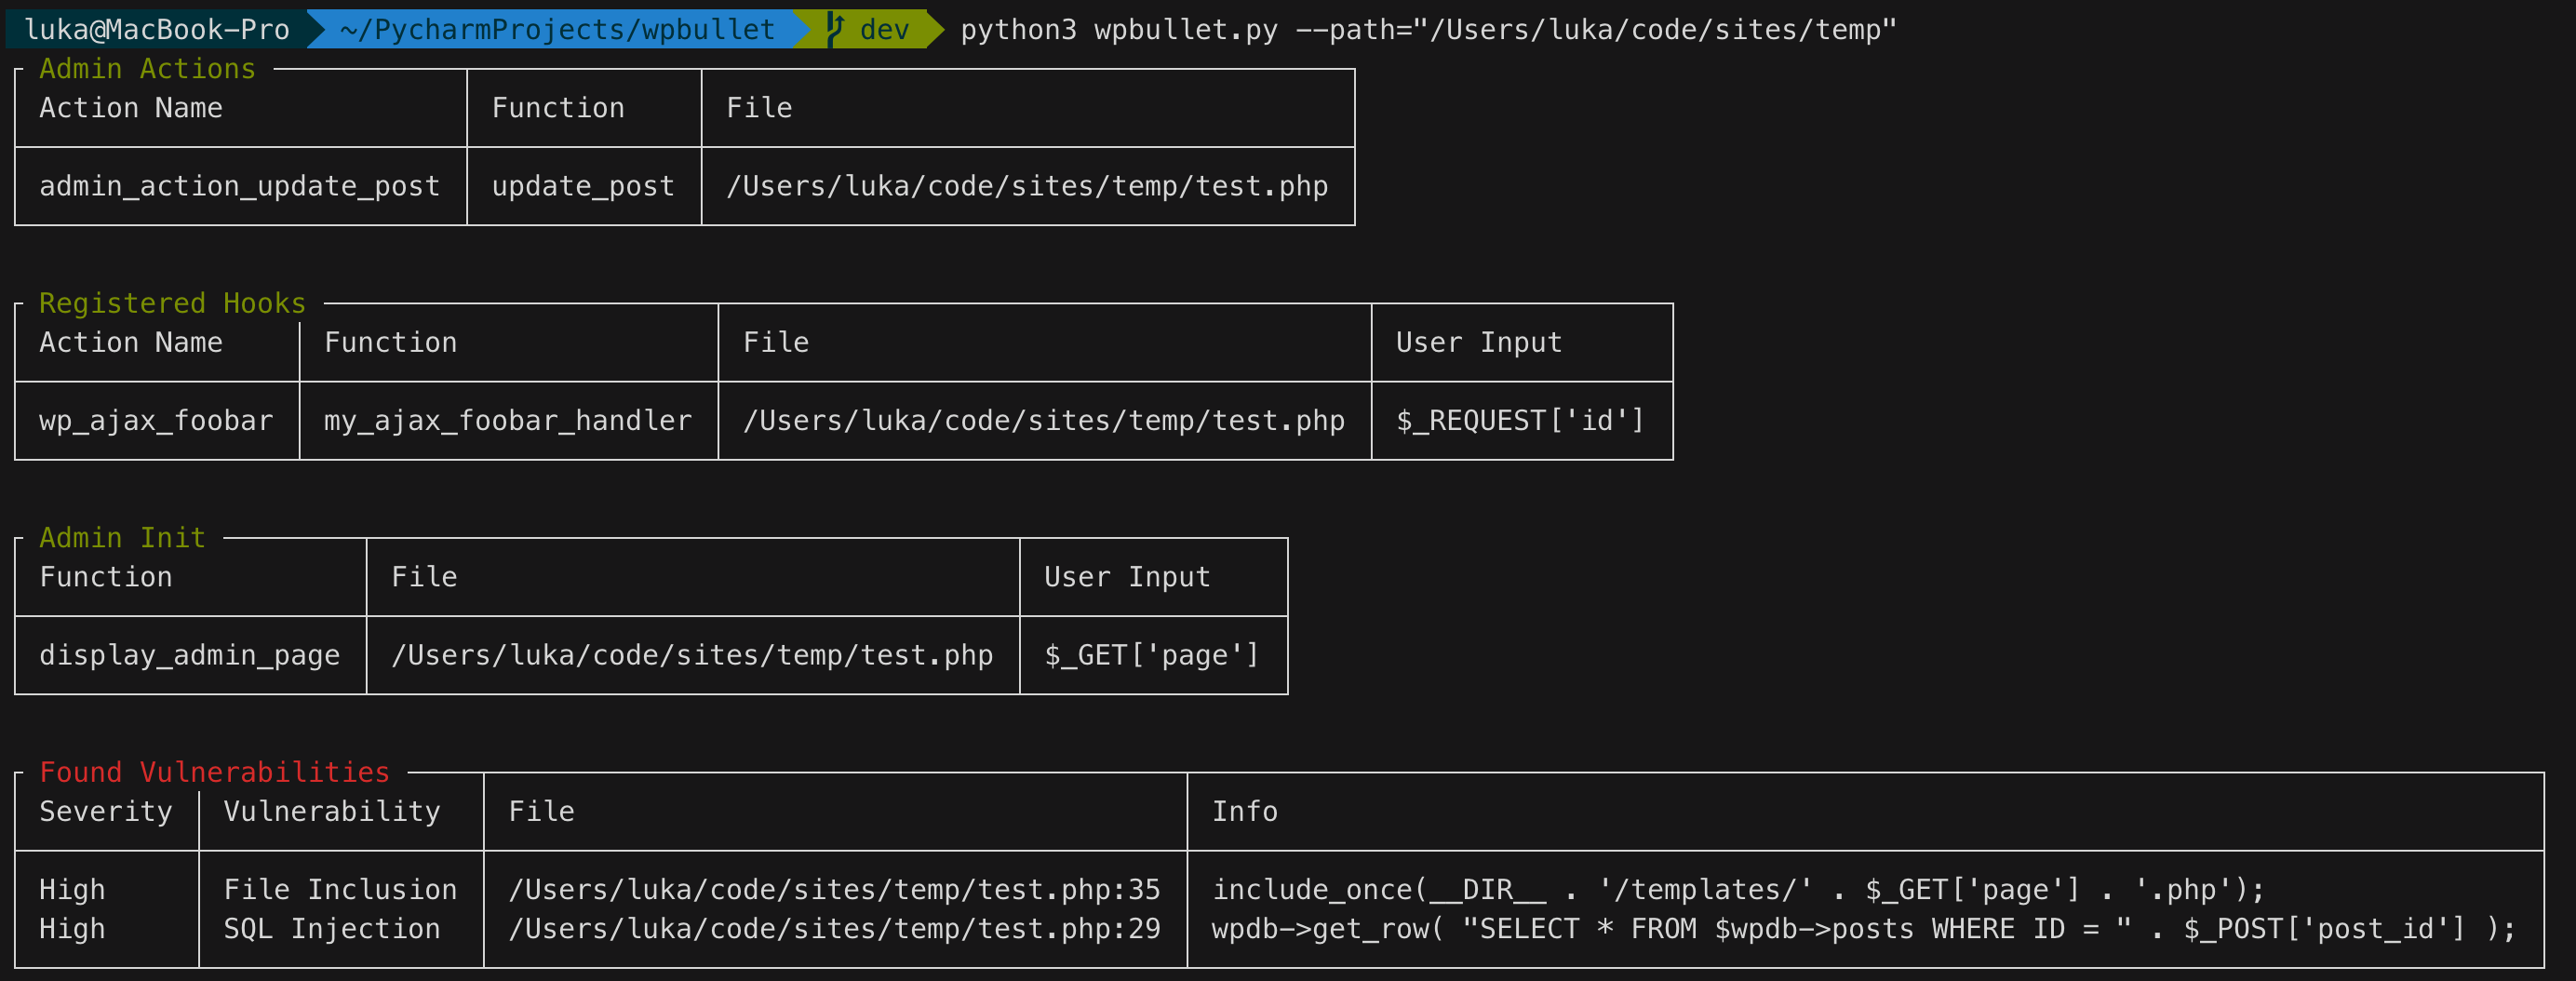 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.