
Archived
gradle-static-analysis-plugin
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
android-securitycode-analysisdevsecops+3
novoda/gradle-static-analysis-pluginEasy setup of static analysis tools for Android and Java projects.
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 nyameeeain/cve-2022-28171-poc
Python exploit for CVE-2022-28171 targeting Hikvision Hybrid SAN devices, automating blind SQL injection and command injection to achieve remote code…
 nccgroup/goatcasino
This is an intentionally vulnerable smart contract truffle deployment aimed at allowing those interested in smart contract security to exploit a wide…
 nccgroup/matt.net
Matt.Net is a simple GUI wrapper around Microsoft's CAT.NET Code Auditing Tool
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 avito-tech/deepsecrets
Static analysis tool that scans source code for hardcoded secrets, API keys, and credentials using semantic understanding of code context.
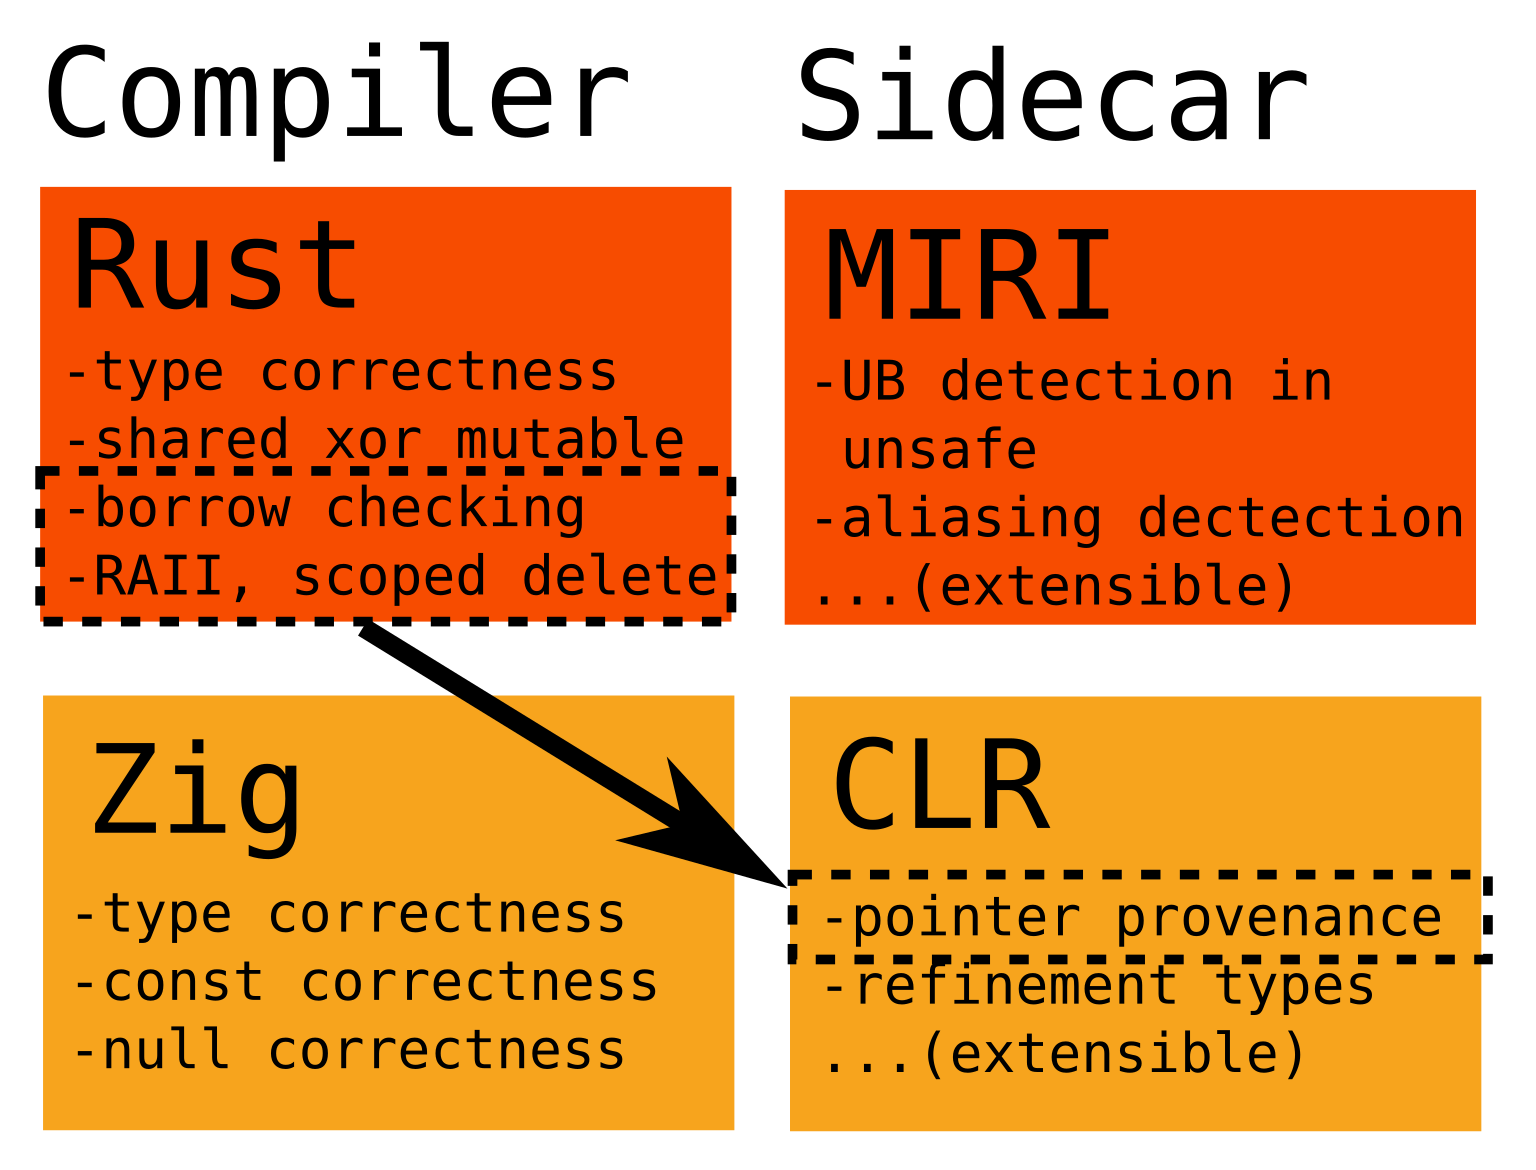 ityonemo/clr
Checker for Lifetimes and other Refinement types
 nccgroup/rustproofing-linux
Educational examples porting Linux kernel vulnerabilities to Rust, featuring intentionally vulnerable code and exploits for learning kernel security…
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 shoucheng3/codehaus-plexus__plexus-utils_cve-2022-4244_3-0-23
Java utility library with patched CVE-2022-4244 vulnerability, providing common helper classes for I/O, reflection, and CLI argument parsing in…
 shoucheng3/codehaus-plexus__plexus-archiver_cve-2018-1002200_3-5
Java library for creating and extracting archives (ZIP, TAR, JAR) with support for various compression formats. Note: version 3.5 contains a fix for…
 dor-tumarkin/cve-2019-17564-fastjson-gadget
Basic code for creating the Alibaba FastJson + Spring gadget chain, as used to exploit Apache Dubbo in CVE-2019-17564 - more information available at…
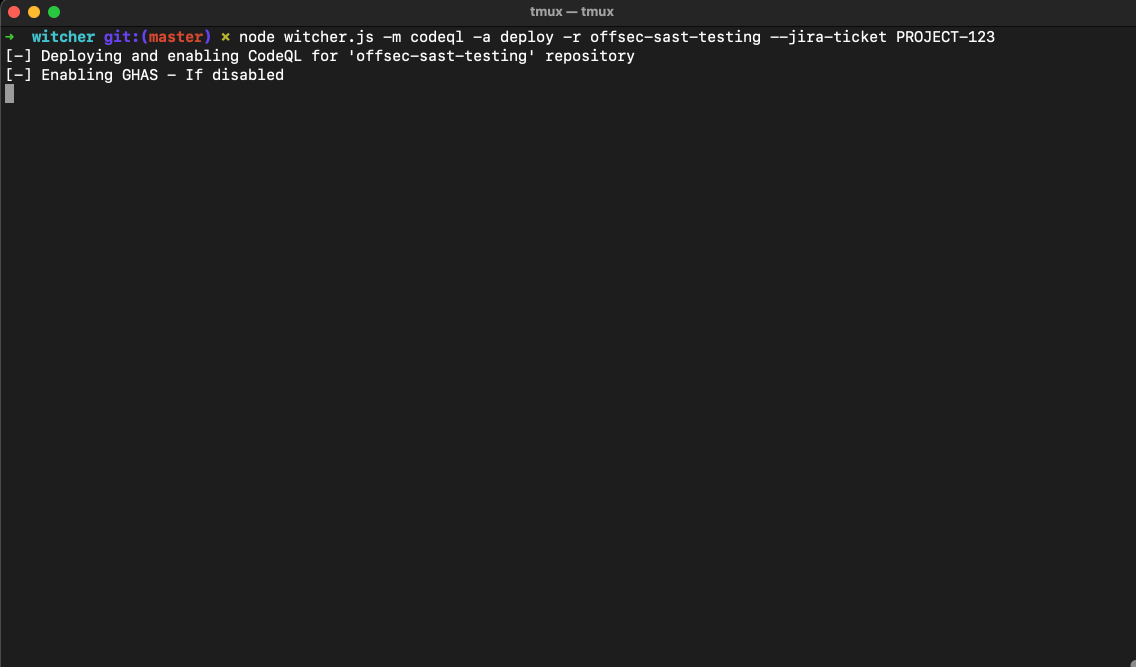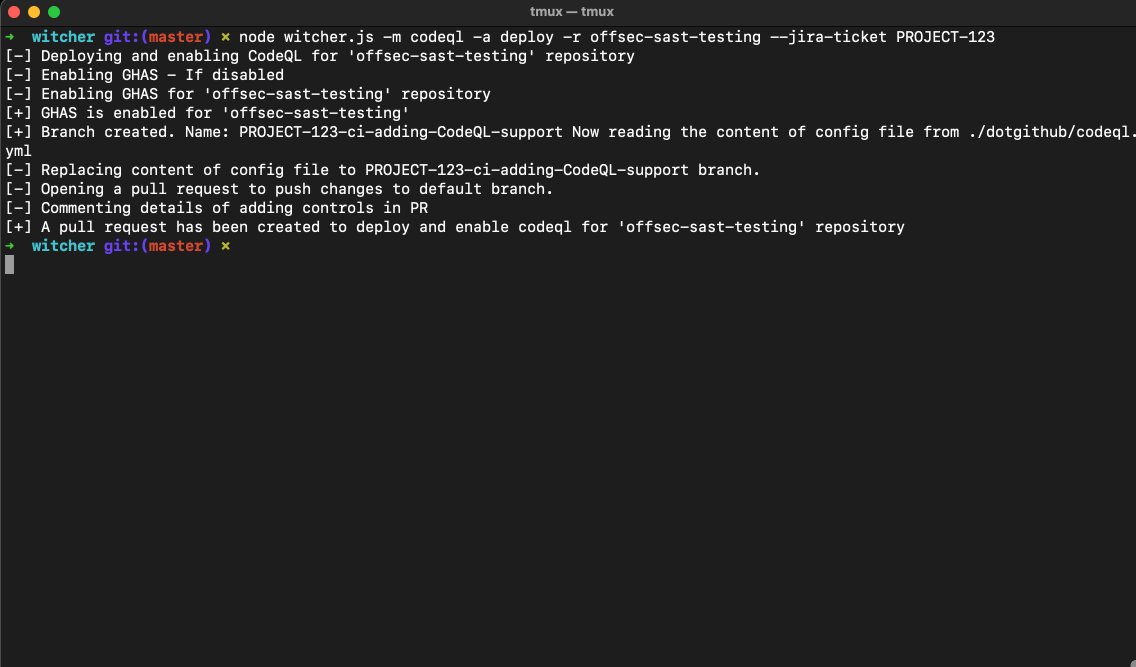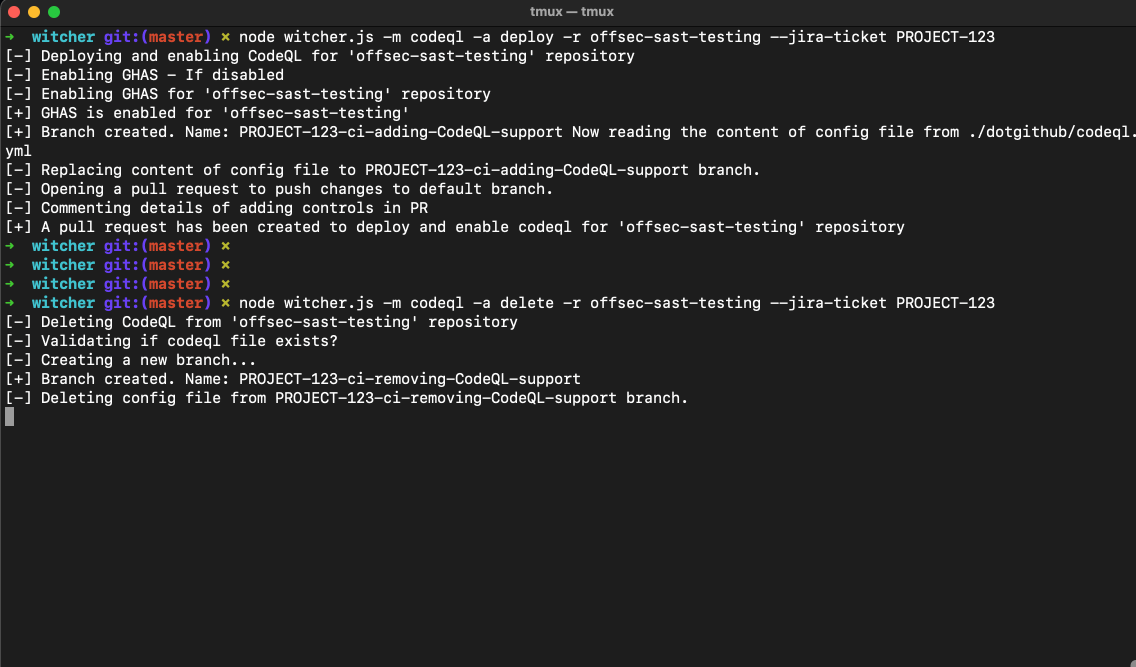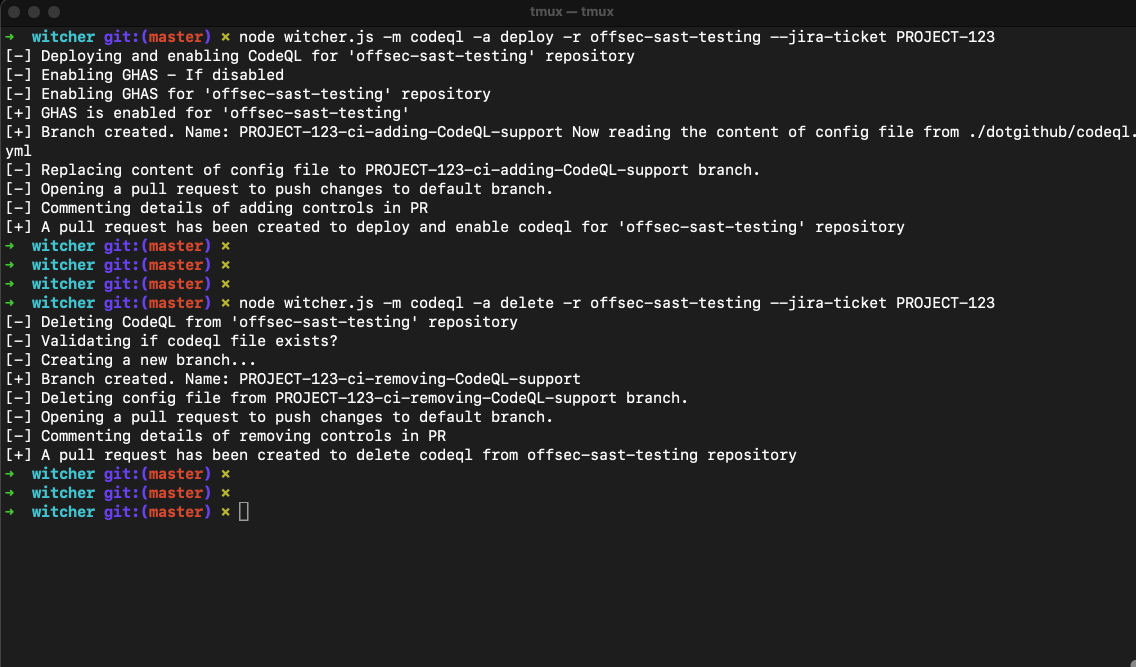 mf-labs/witcher
Managing GitHub Advanced Security (GHAS) Controls at Scale
 hyperps/cve-2026-0848
nltk.tokenize.StanfordSegmenter dynamically loads external Java .jar files without verification or sandboxing. If an attacker can supply or replace…
 joelbts/cve-2020-0601_poc
Demonstration of CVE-2020-0601 aka curveball. Based on the PoC's available at https://github.com/kudelskisecurity/chainoffools and…
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 anthropics/defending-code-reference-harness
Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize