

AtomShields
 elevenpaths/atomshields
Security testing framework for repositories and source code
code-analysisdevsecopsmisconfiguration+3
elevenpaths/atomshieldsSecurity testing framework for repositories and source code
 owasp/riskassessmentframework
The Secure Coding Framework
 uthrasri/frame_cve-2023-40133_136_137
Exploit for CVE-2023-40133, a vulnerability in Android's Framework component, enabling code execution analysis and security testing.
 epicosy/vul4j-23
Curated Java web framework vulnerability (CVE-2016-5394) for Apache Sling, designed for security testing, exploitation practice, and vulnerability…
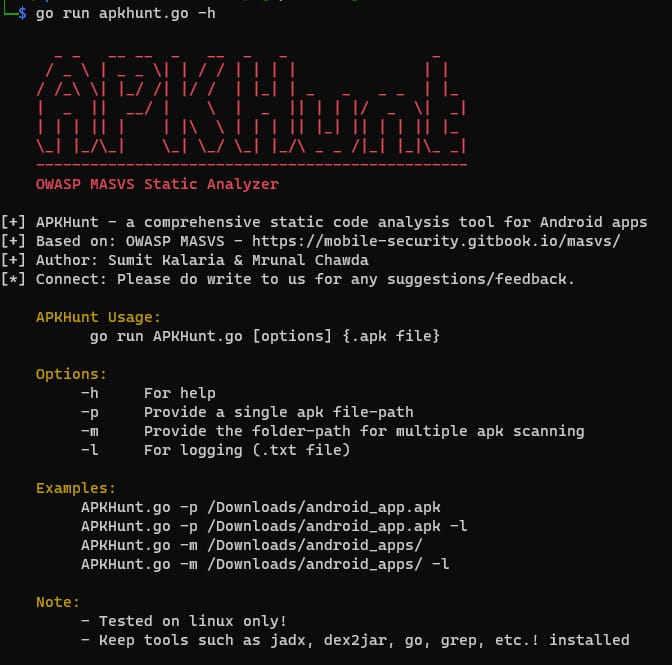 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 rvermeulen/apache-struts-cve-2017-9805
Exploit for Apache Struts CVE-2017-9805, a remote code execution vulnerability in the REST plugin. Enables penetration testing and security…
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 ak-cybe/cve-2025-68664-langgrinch-poc
A testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only
 shoucheng3/testng-team__testng_cve-2022-4065_7-5
Java testing framework for unit, integration, and end-to-end tests with annotations, data-driven testing, and parallel execution support.
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 drackyjr/cve-2025-3248-exploit
A comprehensive Python exploitation framework for testing and demonstrating CVE-2025-3248, a critical unauthenticated remote code execution…
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 shoucheng3/asf__cxf_cve-2019-17573_3-2-11
Web services framework for building and developing SOAP, RESTful, and CORBA services with support for WS-Security, WS-Trust, and JAX-WS/JAX-RS APIs.
 trinadh465/platform_frameworks_base_cve-2023-21281
Android platform framework patch for CVE-2023-21281, addressing a security vulnerability in the Android framework.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 kadamnayan/poc-cve-2024-38820
Proof-of-concept exploit for CVE-2024-38820, demonstrating locale-dependent case conversion bypass of Spring Framework DataBinder disallowedFields…
 trinadh465/frameworks_base_aosp10_r33_cve-2023-21284
Android framework patch for CVE-2023-21284, addressing a security vulnerability in AOSP 10.
 funcid/cve-2024-38828
PoC and fix for CVE-2024-38828: Spring Framework DoS via Content-Length manipulation in ByteArrayHttpMessageConverter. Includes load testing,…