
CVE-2023-6246
 elpe-pinillo/cve-2023-6246
C-based proof-of-concept exploit for CVE-2023-6246, targeting a privilege escalation vulnerability in the Linux kernel's syscalls. Tested on Fedora…
binary-exploitationcode-analysisexploitation+2
8
elpe-pinillo/cve-2023-6246C-based proof-of-concept exploit for CVE-2023-6246, targeting a privilege escalation vulnerability in the Linux kernel's syscalls. Tested on Fedora…
 m8seven/cve-2026-11837-ansible-posix-authorized-key
CVE-2026-11837: local privilege escalation in the ansible.posix authorized_key module via symlink-following chown. Technical writeup; sibling of…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
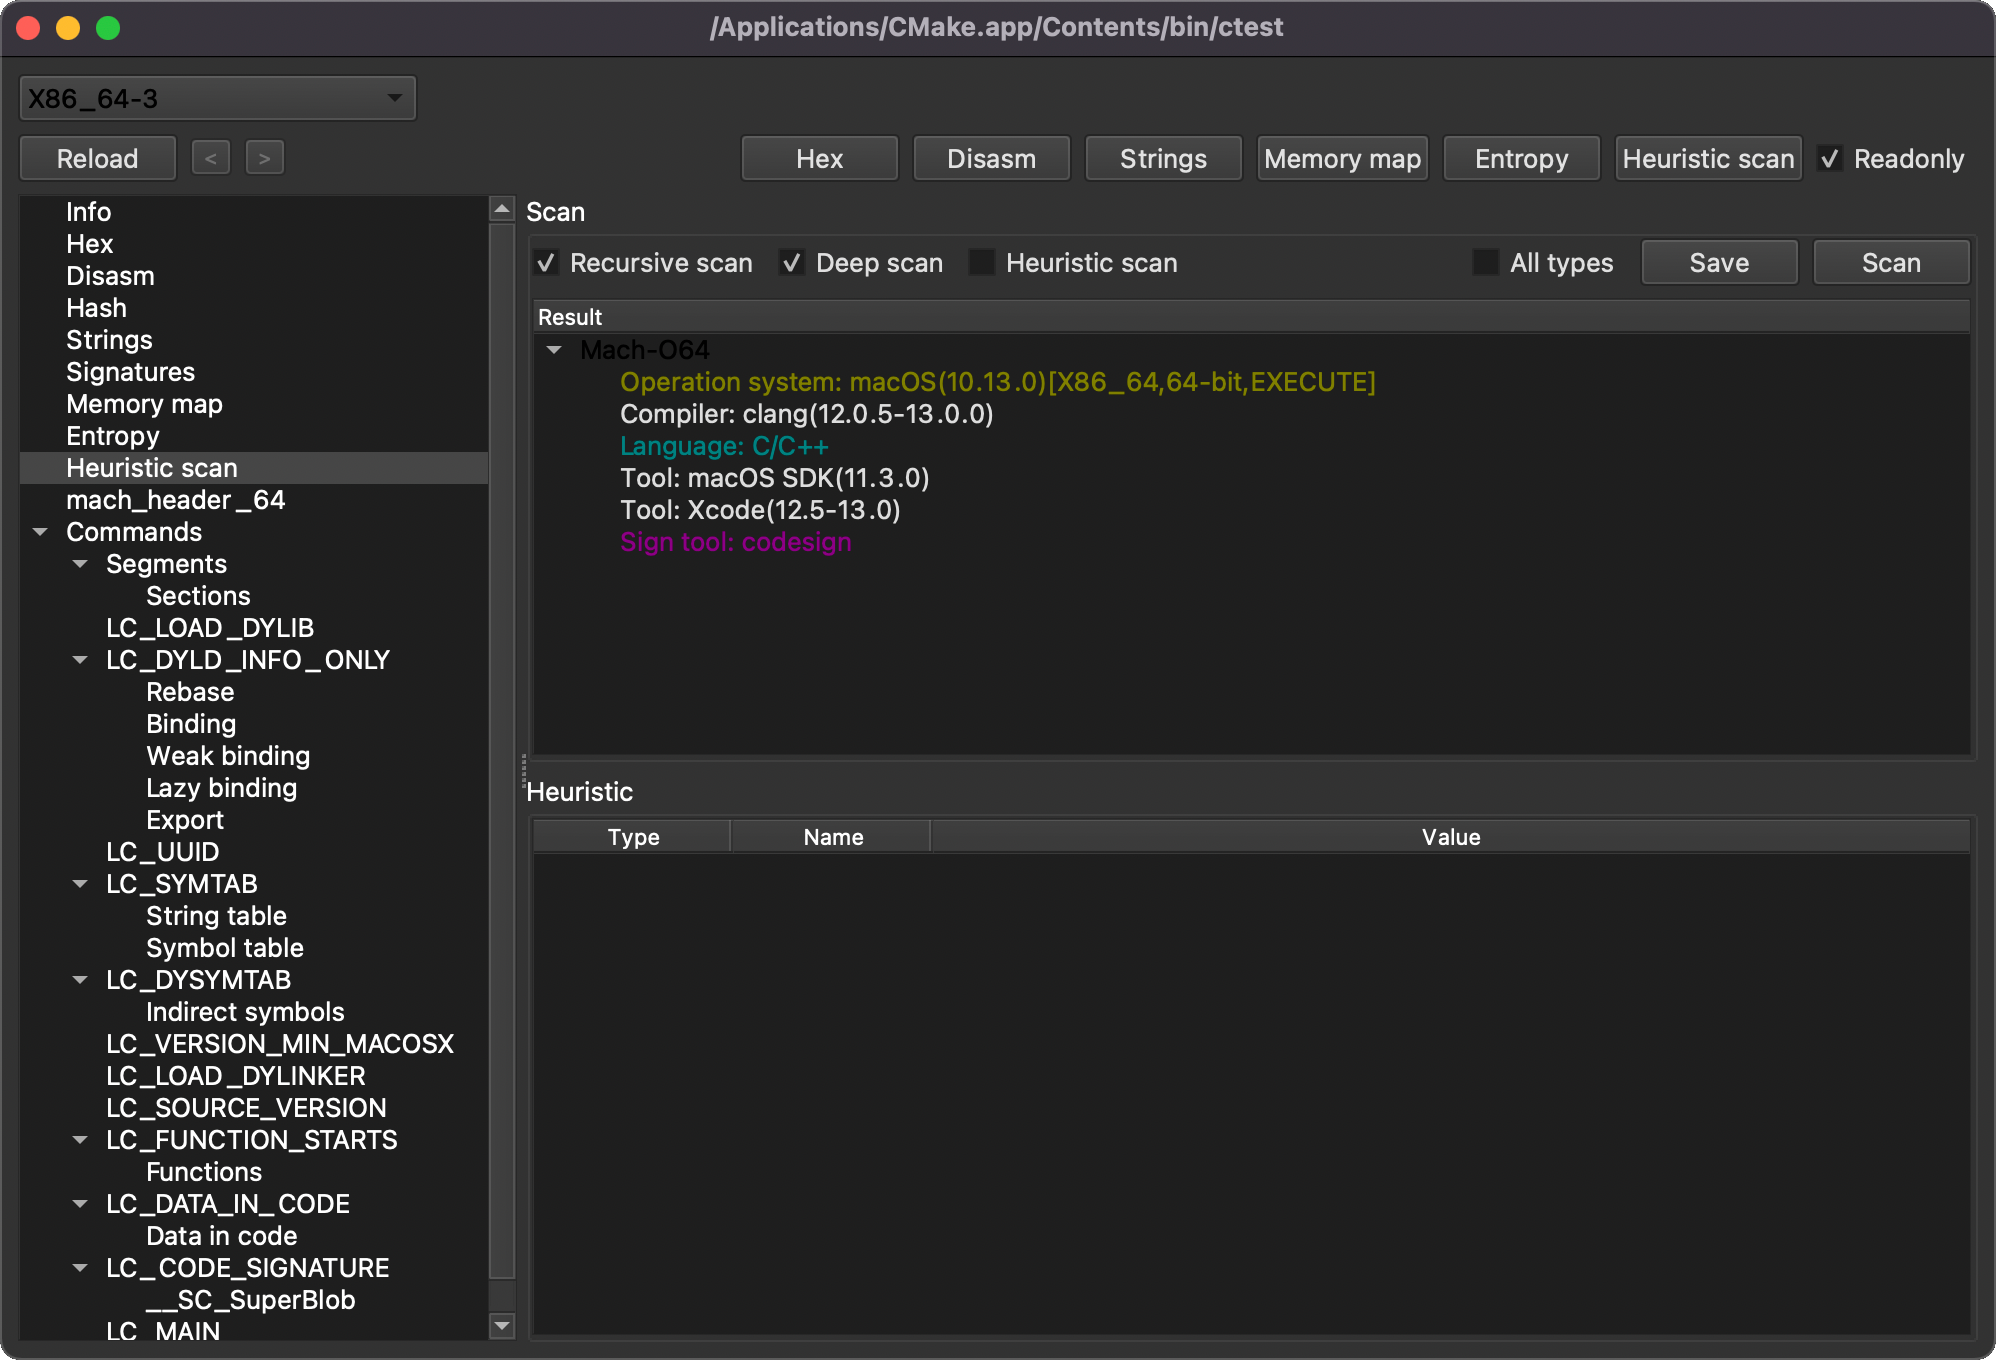 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 nccgroup/rustproofing-linux
Educational examples porting Linux kernel vulnerabilities to Rust, featuring intentionally vulnerable code and exploits for learning kernel security…
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 bluedragonsecurity/linux-kernel-dirty-pipe-exploitation-logic-bug-
Exploiting CVE-2022-0847 - written by : Antonius (w1sdom)
 cahyod/react2shell
Alat ini mendeteksi potensi kerentanan React2Shell (CVE-2025-55182) dalam proyek React dengan memeriksa: - File `package.json` dan file lock untuk…
 gogooma125732/cve-2016-5195
Non-weaponized CVE-2016-5195 (Dirty COW) analysis and validation harness with root-cause research, upstream patch review, and safe lab-only PoC for…
 andhrimnirr/mintinstall-object-injection
CVE-2019-17080
 dpomnean/log4j_scanner_wrapper
log4j vulnerability wrapper scanner for CVE-2021-44228
 eqstlab/cve-2024-8353
GiveWP PHP Object Injection exploit
 polaris64/web_exploit_detector
The Web Exploit Detector is a Node.js application used to detect possible infections, malicious code and suspicious files in web hosting environments
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.