

contrast
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
cloud-infrastructure-securitycloud-securitycode-analysis+6
20
contrastsecurity/contrastSAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 radicle-dev/heartwood
Peer-to-peer code collaboration and publishing stack with a secure, decentralized protocol, CLI tool, and network daemon for sovereign code forges.
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 uzju/gin-vue-admin-poc-cve-2022-21660
CVE-2022-21660
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
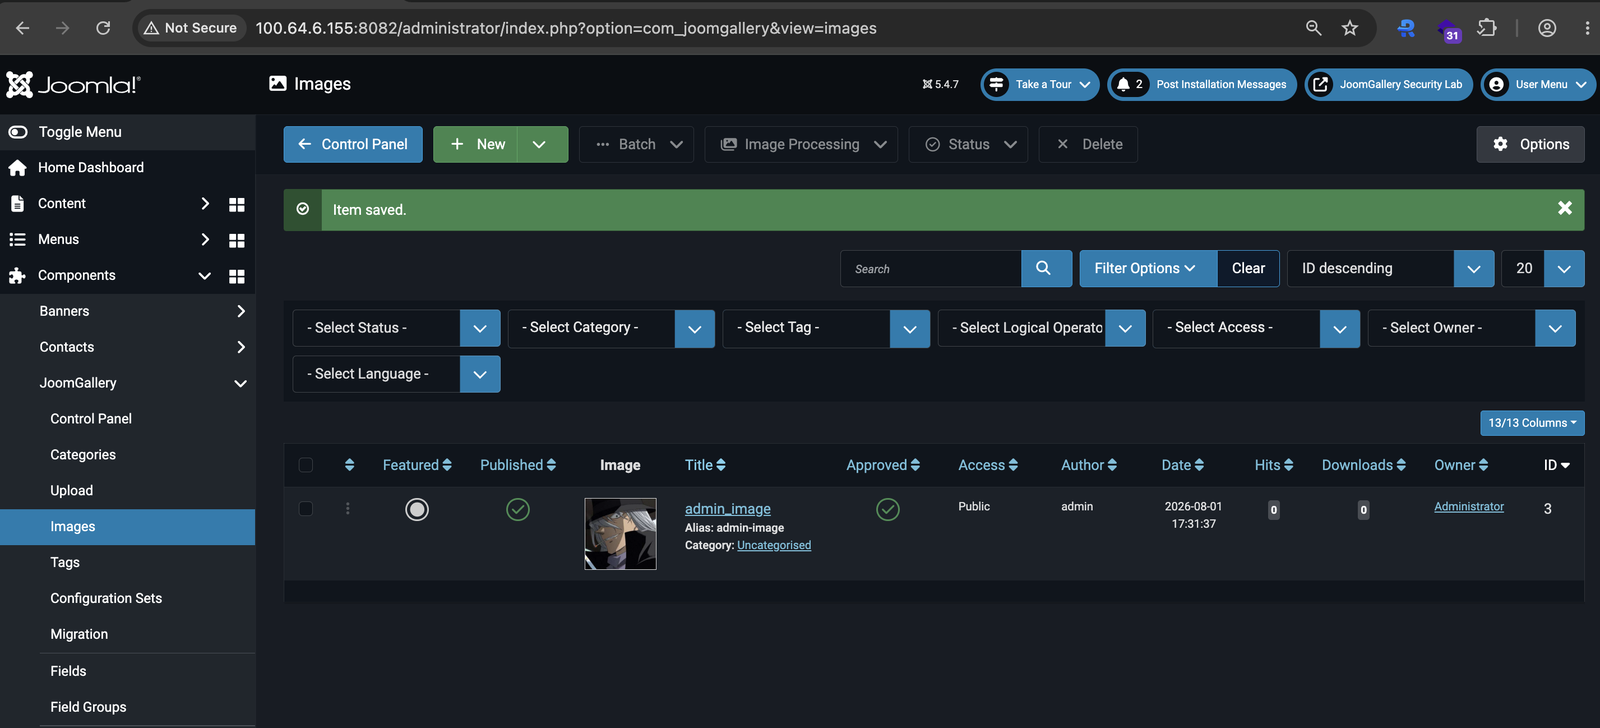 toanln-cov/cve-2026-66917
IDOR + Stored XSS via Broken Object-Level Authorization in JoomGallery
 theopaid/cve-2026-66751-insufficient-access-controls-allow-for-unauthorized-room-deletion-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized Room Deletion (Let's Chat)
 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 bekwiner/cve-2026-47777
Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 sudo-wp/sudowp-clickfunnels-zurich
A security-patched fork of the legacy ClickFunnels Classic WordPress plugin. Fixes critical Stored XSS vulnerabilities (CVE-2022-4782) while…
 darrocarocatest-sys/pv2-victim
authz research - CVE-2026-3306 fix coverage
 sudo-wp/sudowp-crowdsignal-forms
A security-hardened fork of Crowdsignal Forms. Patches CVE-2025-69015 (Broken Access Control), modernizes for PHP 8.2+, and enforces strict…