
auth-header-trust-rules
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
authentication-authorizationcode-analysiseducation+3
bk-security/auth-header-trust-rulesSemgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 radicle-dev/heartwood
Peer-to-peer code collaboration and publishing stack with a secure, decentralized protocol, CLI tool, and network daemon for sovereign code forges.
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 farenhytee/database-sentinel
Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…
 uzju/gin-vue-admin-poc-cve-2022-21660
CVE-2022-21660
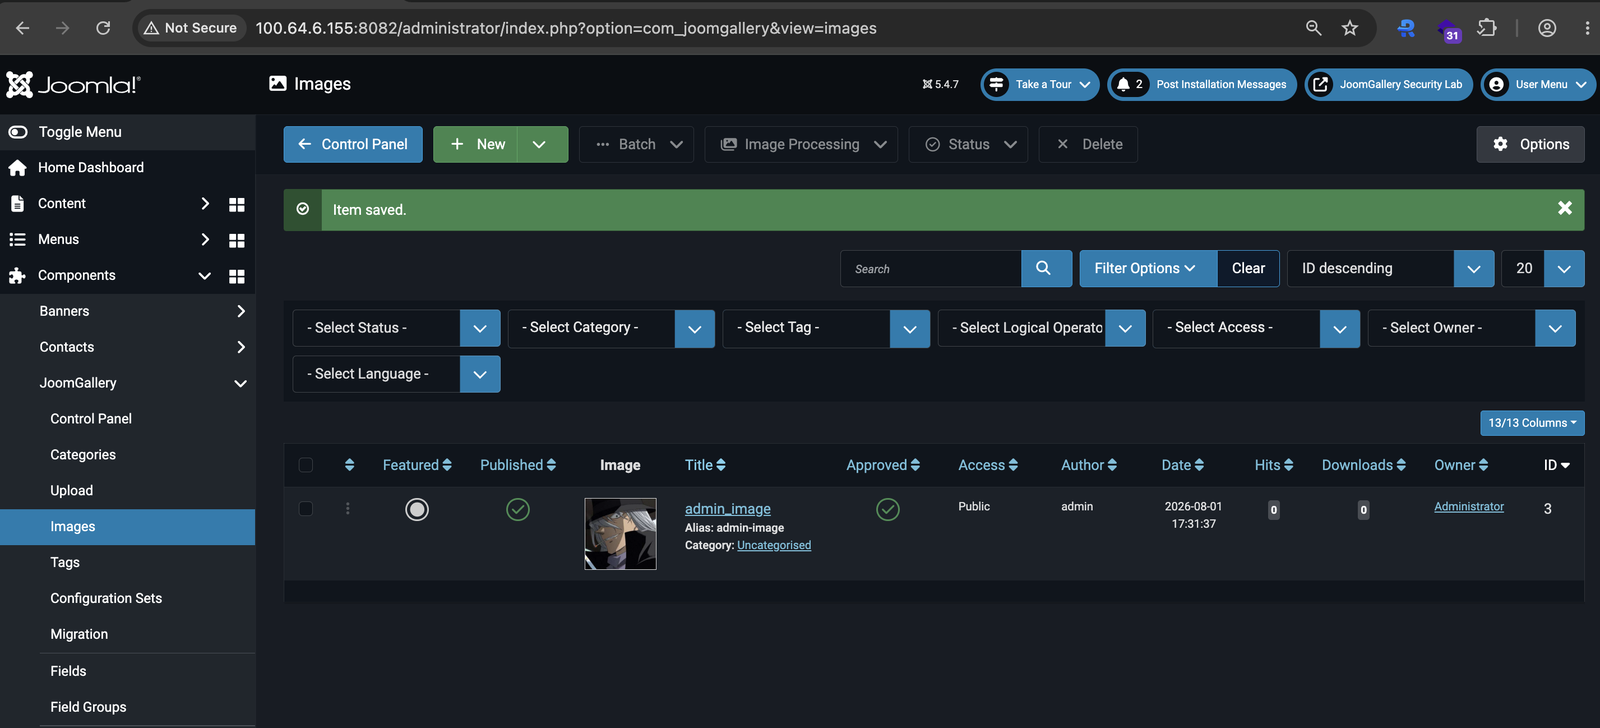 toanln-cov/cve-2026-66917
IDOR + Stored XSS via Broken Object-Level Authorization in JoomGallery

 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
 theopaid/cve-2026-66751-insufficient-access-controls-allow-for-unauthorized-room-deletion-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized Room Deletion (Let's Chat)
 bekwiner/cve-2026-47777
Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…
 sudo-wp/sudowp-clickfunnels-zurich
A security-patched fork of the legacy ClickFunnels Classic WordPress plugin. Fixes critical Stored XSS vulnerabilities (CVE-2022-4782) while…
 darrocarocatest-sys/pv2-victim
authz research - CVE-2026-3306 fix coverage
 sudo-wp/sudowp-crowdsignal-forms
A security-hardened fork of Crowdsignal Forms. Patches CVE-2025-69015 (Broken Access Control), modernizes for PHP 8.2+, and enforces strict…
 pazhanivel07/openssl_1_0_1g_cve-2015-1788
General-purpose cryptography library implementing SSL/TLS protocols, symmetric/ asymmetric ciphers, message digests, and X.509 certificate handling…