
CVE-2023-38890
 tagoletta/cve-2023-38890
Exploit for CVE-2023-38890, an unauthenticated SQL injection to remote code execution in Online Shopping Portal 3.1, with a proof-of-concept and…
code-analysisexploitationpenetration-testing+2
tagoletta/cve-2023-38890Exploit for CVE-2023-38890, an unauthenticated SQL injection to remote code execution in Online Shopping Portal 3.1, with a proof-of-concept and…
 aaryan-11-x/cve-2024-57487-and-cve-2024-57488
Proof-of-concept and detailed writeups for CVE-2024-57487 (authenticated RCE via file upload) and CVE-2024-57488 (stored XSS) in Online Car Rental…
 k1nakoo/cve-2024-10410
Proof-of-concept exploit for CVE-2024-10410: unrestricted file upload in Online Hotel Reservation System. Demonstrates bypass of image validation via…
 buraksevben/cve-2024-24138
Proof-of-concept exploit for SQL injection vulnerability in Online Timesheet App, demonstrating the attack and providing technical details for…
 hax3xploit/cve-2021-41644
Remote Code Exection (RCE) vulnerability exists in Sourcecodester Online Food Ordering System 2.0 via a maliciously crafted PHP file that bypasses…
 bytereaper77/cve-2025-8971
Sql injection in itsourcecode Online Tour and Travel Management System 1.0.
 windecks/cve-2023-46404
PoC and Writeup for CVE-2023-46404.
 shoucheng3/dspace__dspace_cve-2022-31194_5-10
Security patch for DSpace repository software addressing CVE-2022-31194, a vulnerability in the Java-based digital asset management platform.
 shoucheng3/dspace__dspace_cve-2022-31195_5-10
Patched version of DSpace repository addressing CVE-2022-31195, providing a secure digital asset management platform with enhanced vulnerability…
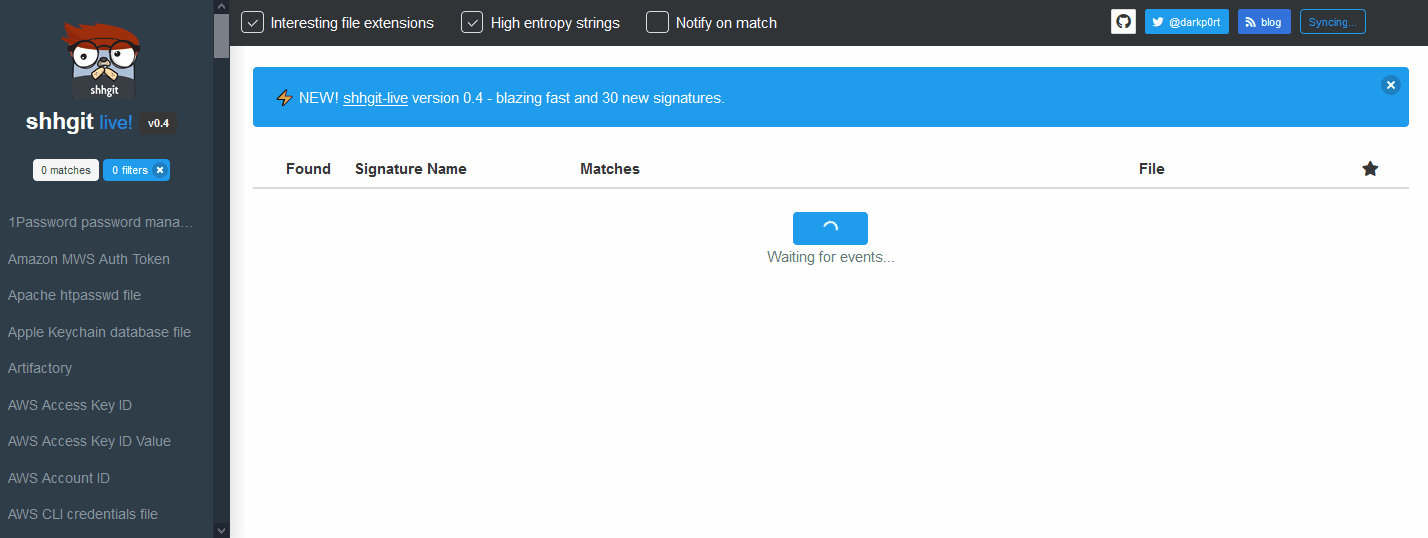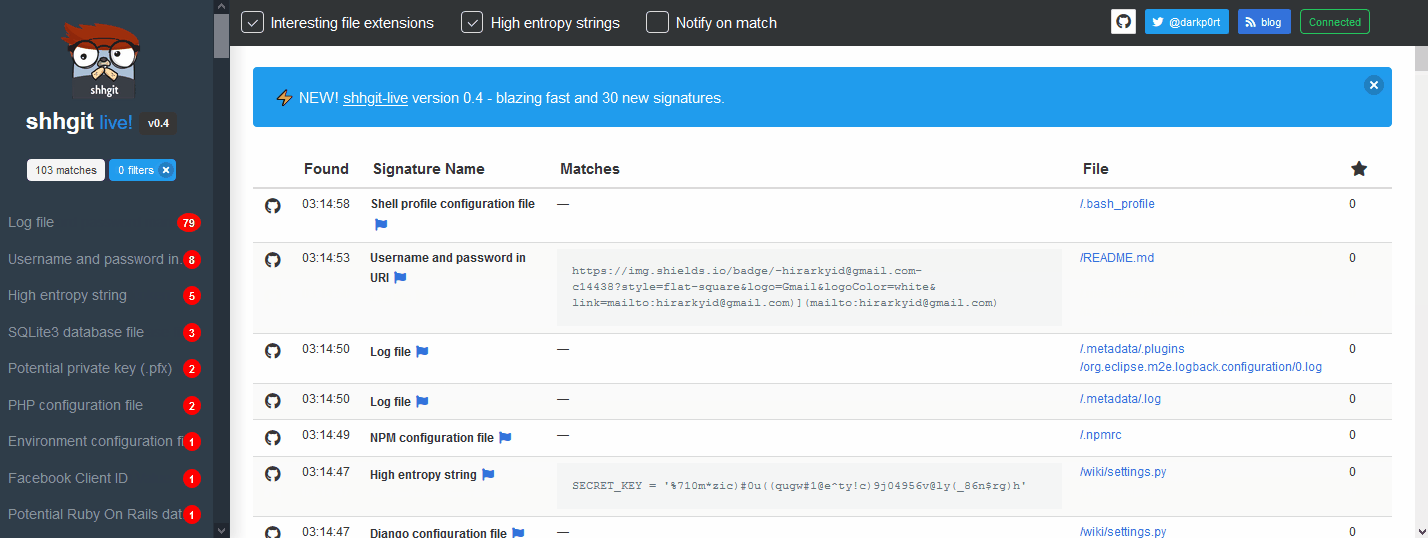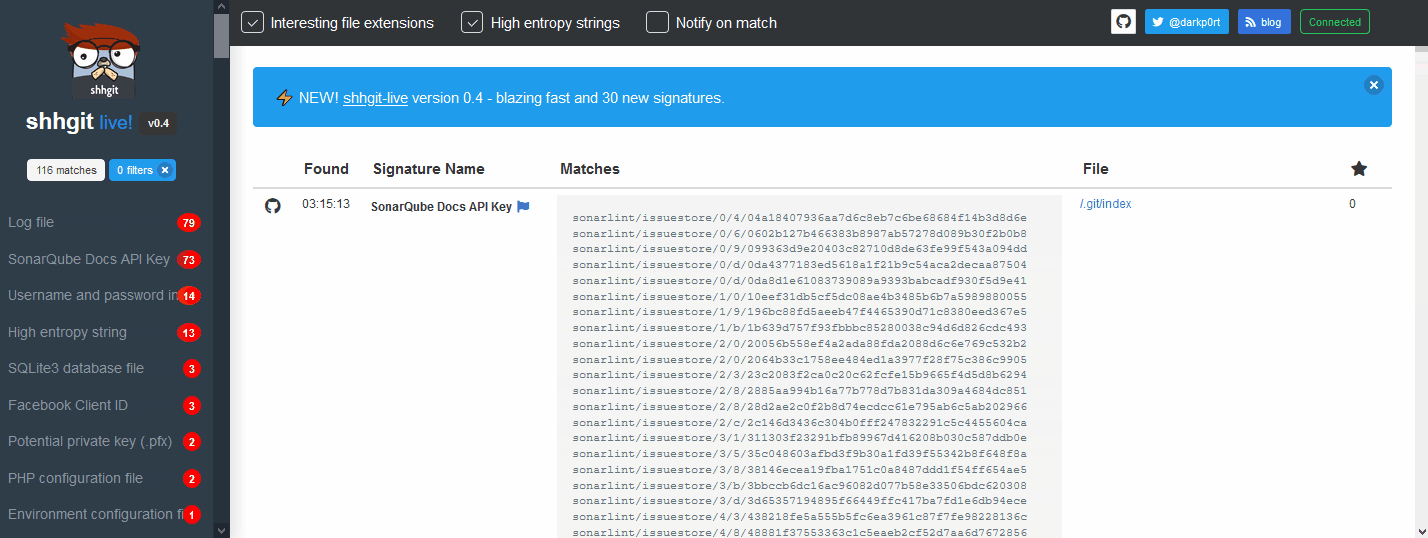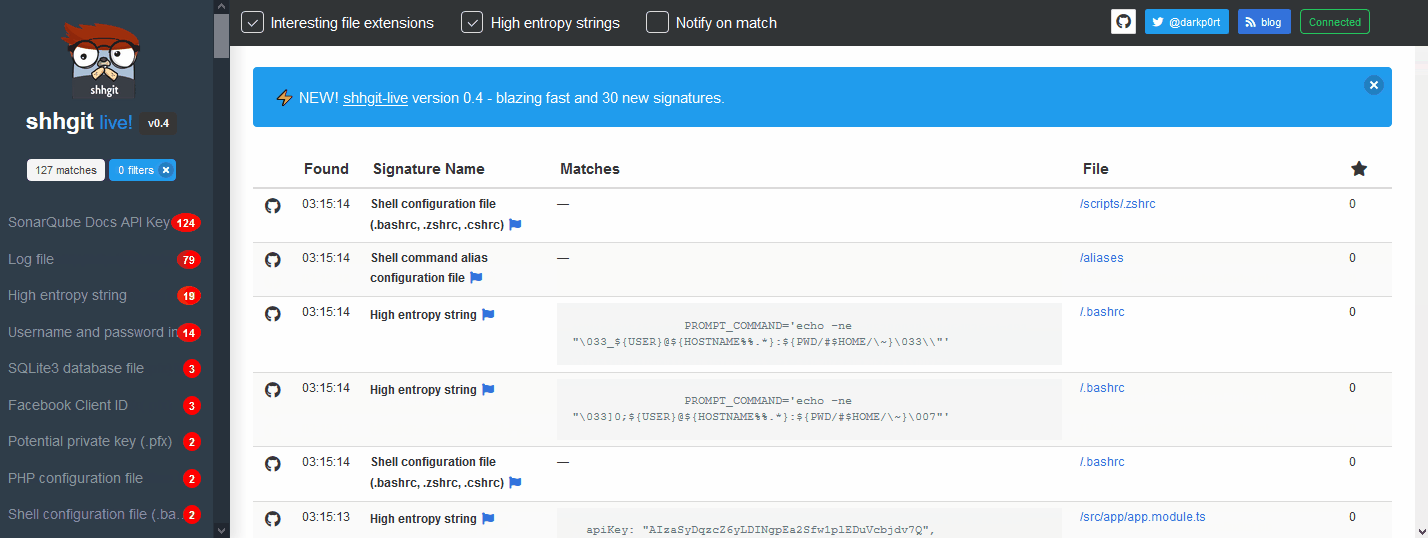 eth0izzle/shhgit
Ah shhgit! Find secrets in your code. Secrets detection for your GitHub, GitLab and Bitbucket repositories.
 cve-search/git-vuln-finder
Finding potential software vulnerabilities from git commit messages
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…