
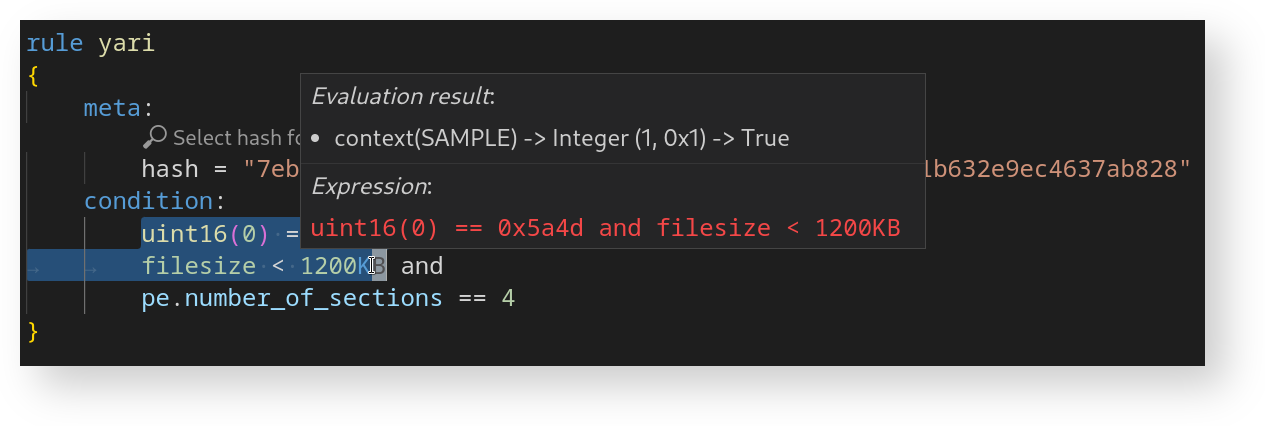
yari
 avast/yari
YARI is an interactive debugger for YARA Language.
binary-analysiscode-analysisdebuggers+2
avast/yariYARI is an interactive debugger for YARA Language.
 freeqaz/react2shell
RCE exploit toolkit for CVE-2025-55182 and CVE-2025-66478 in React Server Components. Includes multiple exploit variants, detection scripts, a…
 lat-06/cve-2026-34197
Proof-of-concept exploit for CVE-2026-34197, demonstrating authenticated remote code execution in Apache ActiveMQ via Jolokia JMX-HTTP bridge and…
 bhanunamikaze/cve-2026-2587-exploit-poc
CVE-2026-2587 PoC validator for Eclipse GlassFish EL Injection RCE in the admin console gadget.jsf handler. Safe authenticated vulnerability scanner…
 vladjrfhfg/react-site-cve-2025-55182
Intentionally vulnerable Next.js corporate landing page demonstrating CVE-2025-55182, a JSON injection leading to RCE/SSRF via unsafe deserialization…
 nikic/php-fuzzer
Edge-coverage-guided fuzzer for PHP libraries that detects bugs via crashes, timeouts, and warnings. Supports corpus management, crash minimization,…
 spoofzu/jvmxray
Externalize Java application access to protected resources as log messages.
 biitts/cve-2026-53753-crawl4ai-rce
CVE-2026-53753 — Crawl4AI <0.8.7 unauthenticated RCE (AST sandbox escape via gi_frame.f_back). Lab + PoC, verified e2e.
 rxerium/cve-2025-4427-cve-2025-4428
Detection for CVE-2025-4427 and CVE-2025-4428
 shoucheng3/x-stream__xstream_cve-2020-26217_1-4-14-java77
Java library for XML serialization and deserialization, with a focus on the CVE-2020-26217 deserialization vulnerability exploit.
 patriksimek/vm2
Isolated JavaScript sandbox for Node.js that runs untrusted code with restricted access to built-in modules and host resources via Proxy-based…
 trailofbits/test-fuzz
Rust macros and Cargo subcommand to automate fuzzing with afl.rs, including corpus generation and harness implementation, integrated with Rust's…
 rubo77/log4j_checker_beta
a fast check, if your server could be vulnerable to CVE-2021-44228
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
 rog3rsm1th/frelatage
Coverage-based fuzzer for python applications
 jas502n/cve-2019-12384
Jackson Rce For CVE-2019-12384
 aliclub0x00/cve-2025-55182-poc-nextjs
Working proof of concept for NextJS RCE to establish a reverse shell. [React2Shell]
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava