
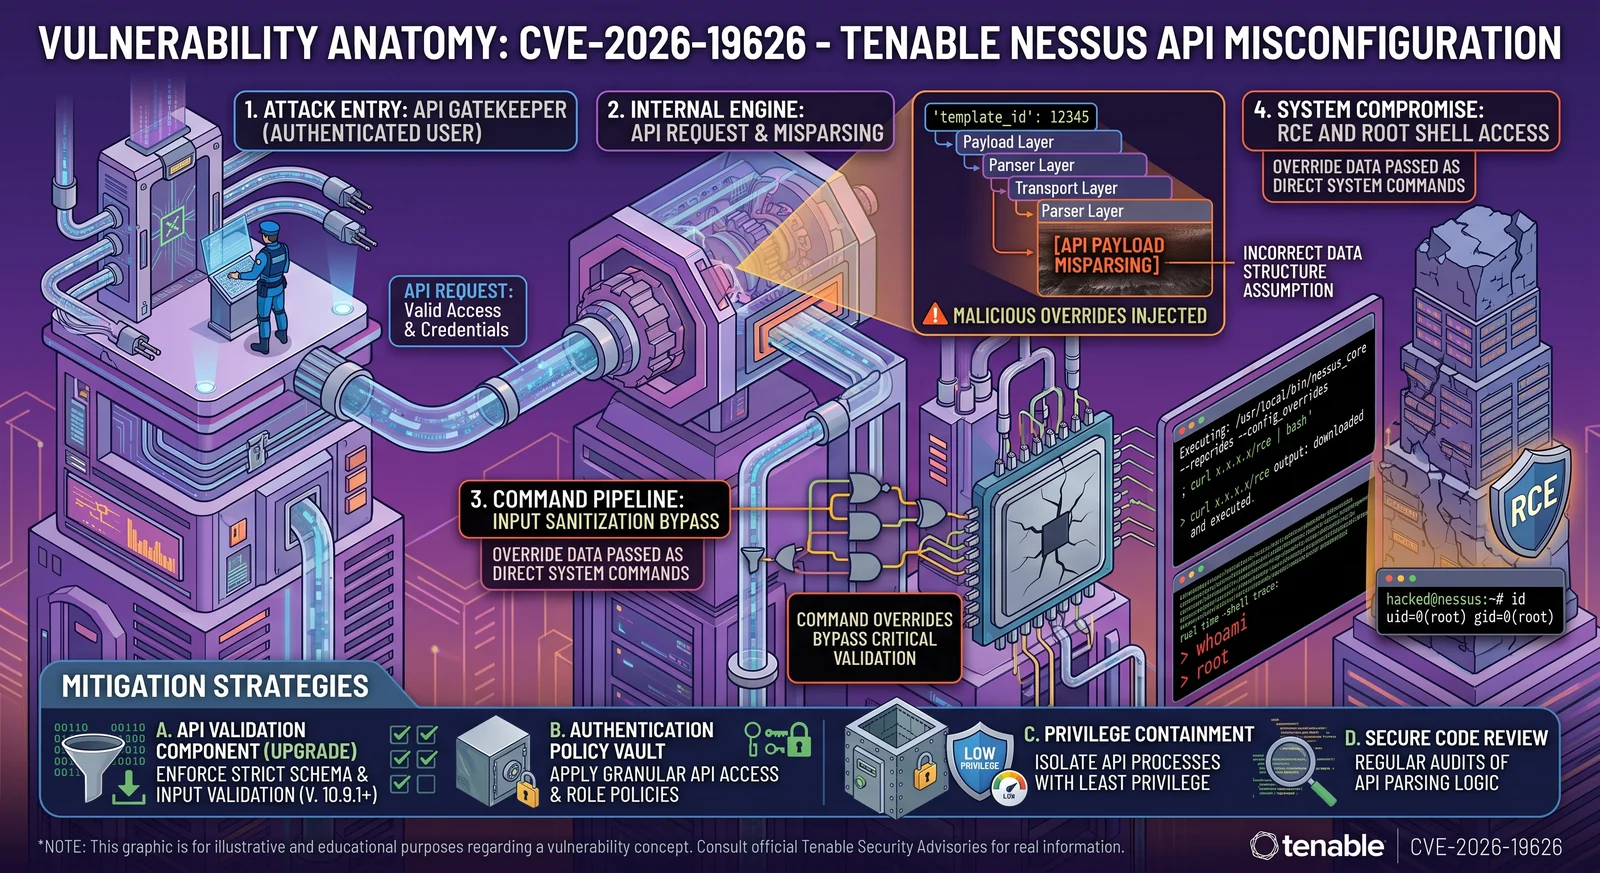
POC-CVE-2026-19626
 h00die/poc-cve-2026-19626
Proof-of-concept exploit for CVE-2026-19626, an authenticated remote code execution in SecurityCenter report generation, demonstrating a non-admin…
code-analysisexploitationpenetration-testing+3
h00die/poc-cve-2026-19626Proof-of-concept exploit for CVE-2026-19626, an authenticated remote code execution in SecurityCenter report generation, demonstrating a non-admin…
 lirantal/safer-eval-cve-cve-2019-10760
Publicly disclosed Proof-of-Concept (POC) exploit for the [email protected] version
 jivasecurity/dolibarr-rce-cve-2026-22666
dol_eval_standard() whitelist bypass eval() RCE, affecting Dolibarr 23.0.0 and below by jiva (jivasecurity.com)
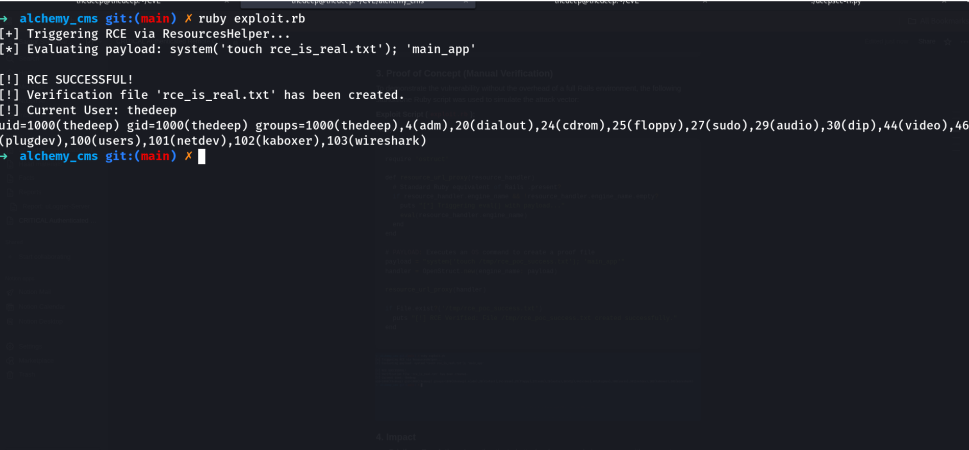 thedeepopc/cve-2026-23885
Proof-of-concept exploit for CVE-2026-23885, an authenticated RCE in AlchemyCMS via eval() injection, with technical analysis and remediation…
 savagesanta11/reproduce-cve-2024-21513
Demonstrates CVE-2024-21513 in langchain-experimental, showing arbitrary code execution via VectorSQLDatabaseChain's eval() on retrieved values.…
 haile01/perl_spreadsheet_excel_rce_poc
POC for RCE vulnerability in ParseExcel library, and ParseXLSX too, as a depending library
 htrxuan/hdwebmobile-formula-pricing
WooCommerce plugin: safe formula-based product pricing, closing CVE-2026-4001's eval()-based RCE
 ludy-dev/phpunit_eval-stdin_rce
(CVE-2017-9841) PHPUnit_eval-stdin_php Remote Code Execution
 joakimbulow/cve-2026-48962
CVE-2026-48962 - IO::Compress - Code Execution
