
Argus
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
code-analysisdevsecopseducation+4
552 years ago
purs3lab/argusStaged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
 niokagi/react-cve-2025-55182
Test & Analyze the CVE-2025-55182 vulnerability within Next.js Server Actions
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 colton1skees/dna
LLVM based static binary analysis framework
 shoucheng3/spring-projects__spring-framework_cve-2022-22965_5-2-19-release
Exploit for CVE-2022-22965 (Spring4Shell) targeting Spring Framework versions vulnerable to remote code execution via classLoader manipulation.
 a0xnirudh/kurukshetra
Kurukshetra - A framework for teaching secure coding by means of interactive problem solving.
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
 kadamnayan/poc-cve-2024-38820
Proof-of-concept exploit for CVE-2024-38820, demonstrating locale-dependent case conversion bypass of Spring Framework DataBinder disallowedFields…
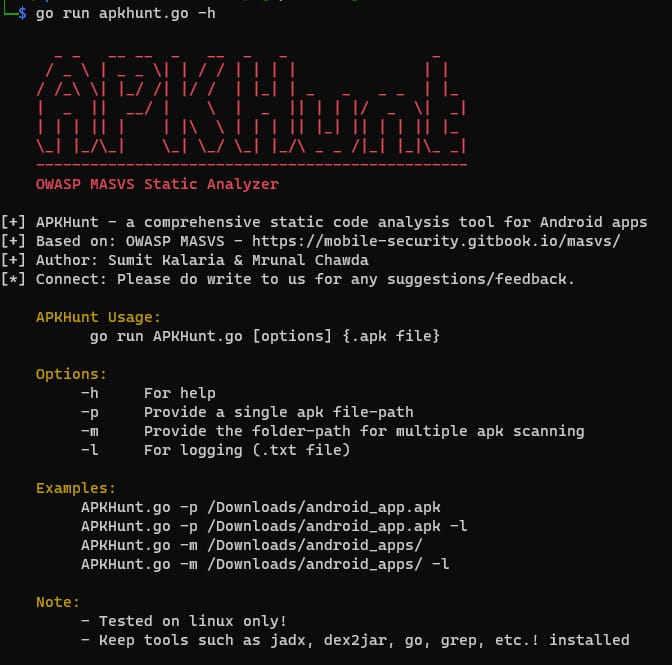 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 vinsontang1/vultriage
The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection
 gpt-laboratory/trustworthyrag
An Evaluation Agent for Detecting Misinformation and Knowledge Poisoning in Retrieval-Augmented Generation Systems.
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering