

ApplicationInspector
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
code-analysisdevsecopsstatic-analysis+3
4.4k
microsoft/applicationinspectorA source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 colton1skees/dna
LLVM based static binary analysis framework
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
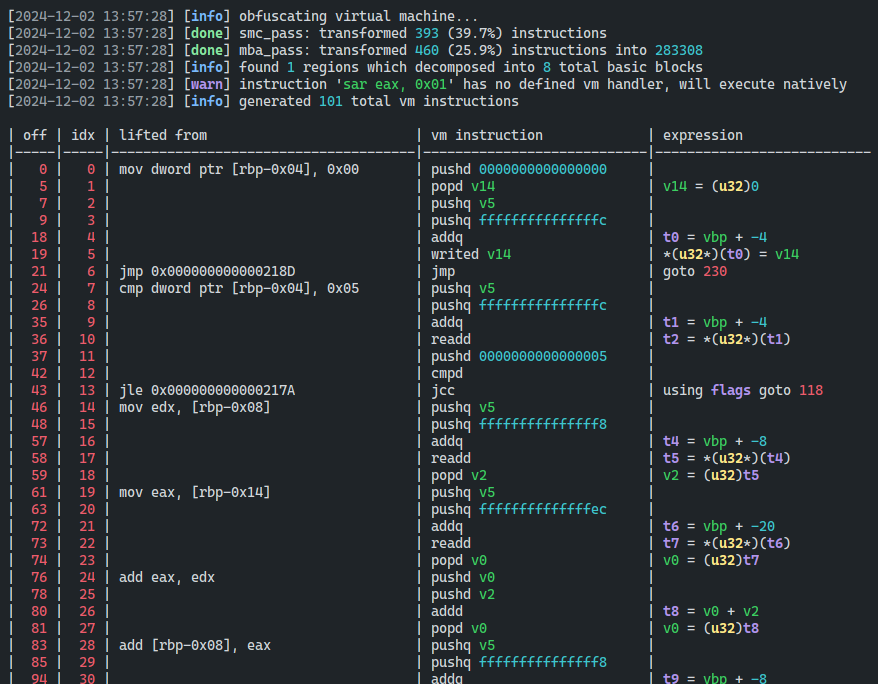 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 parikhakshat/autoharness
A tool that automatically creates fuzzing harnesses based on a library
 samsung/utopia
UT based automated fuzz driver generation
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.
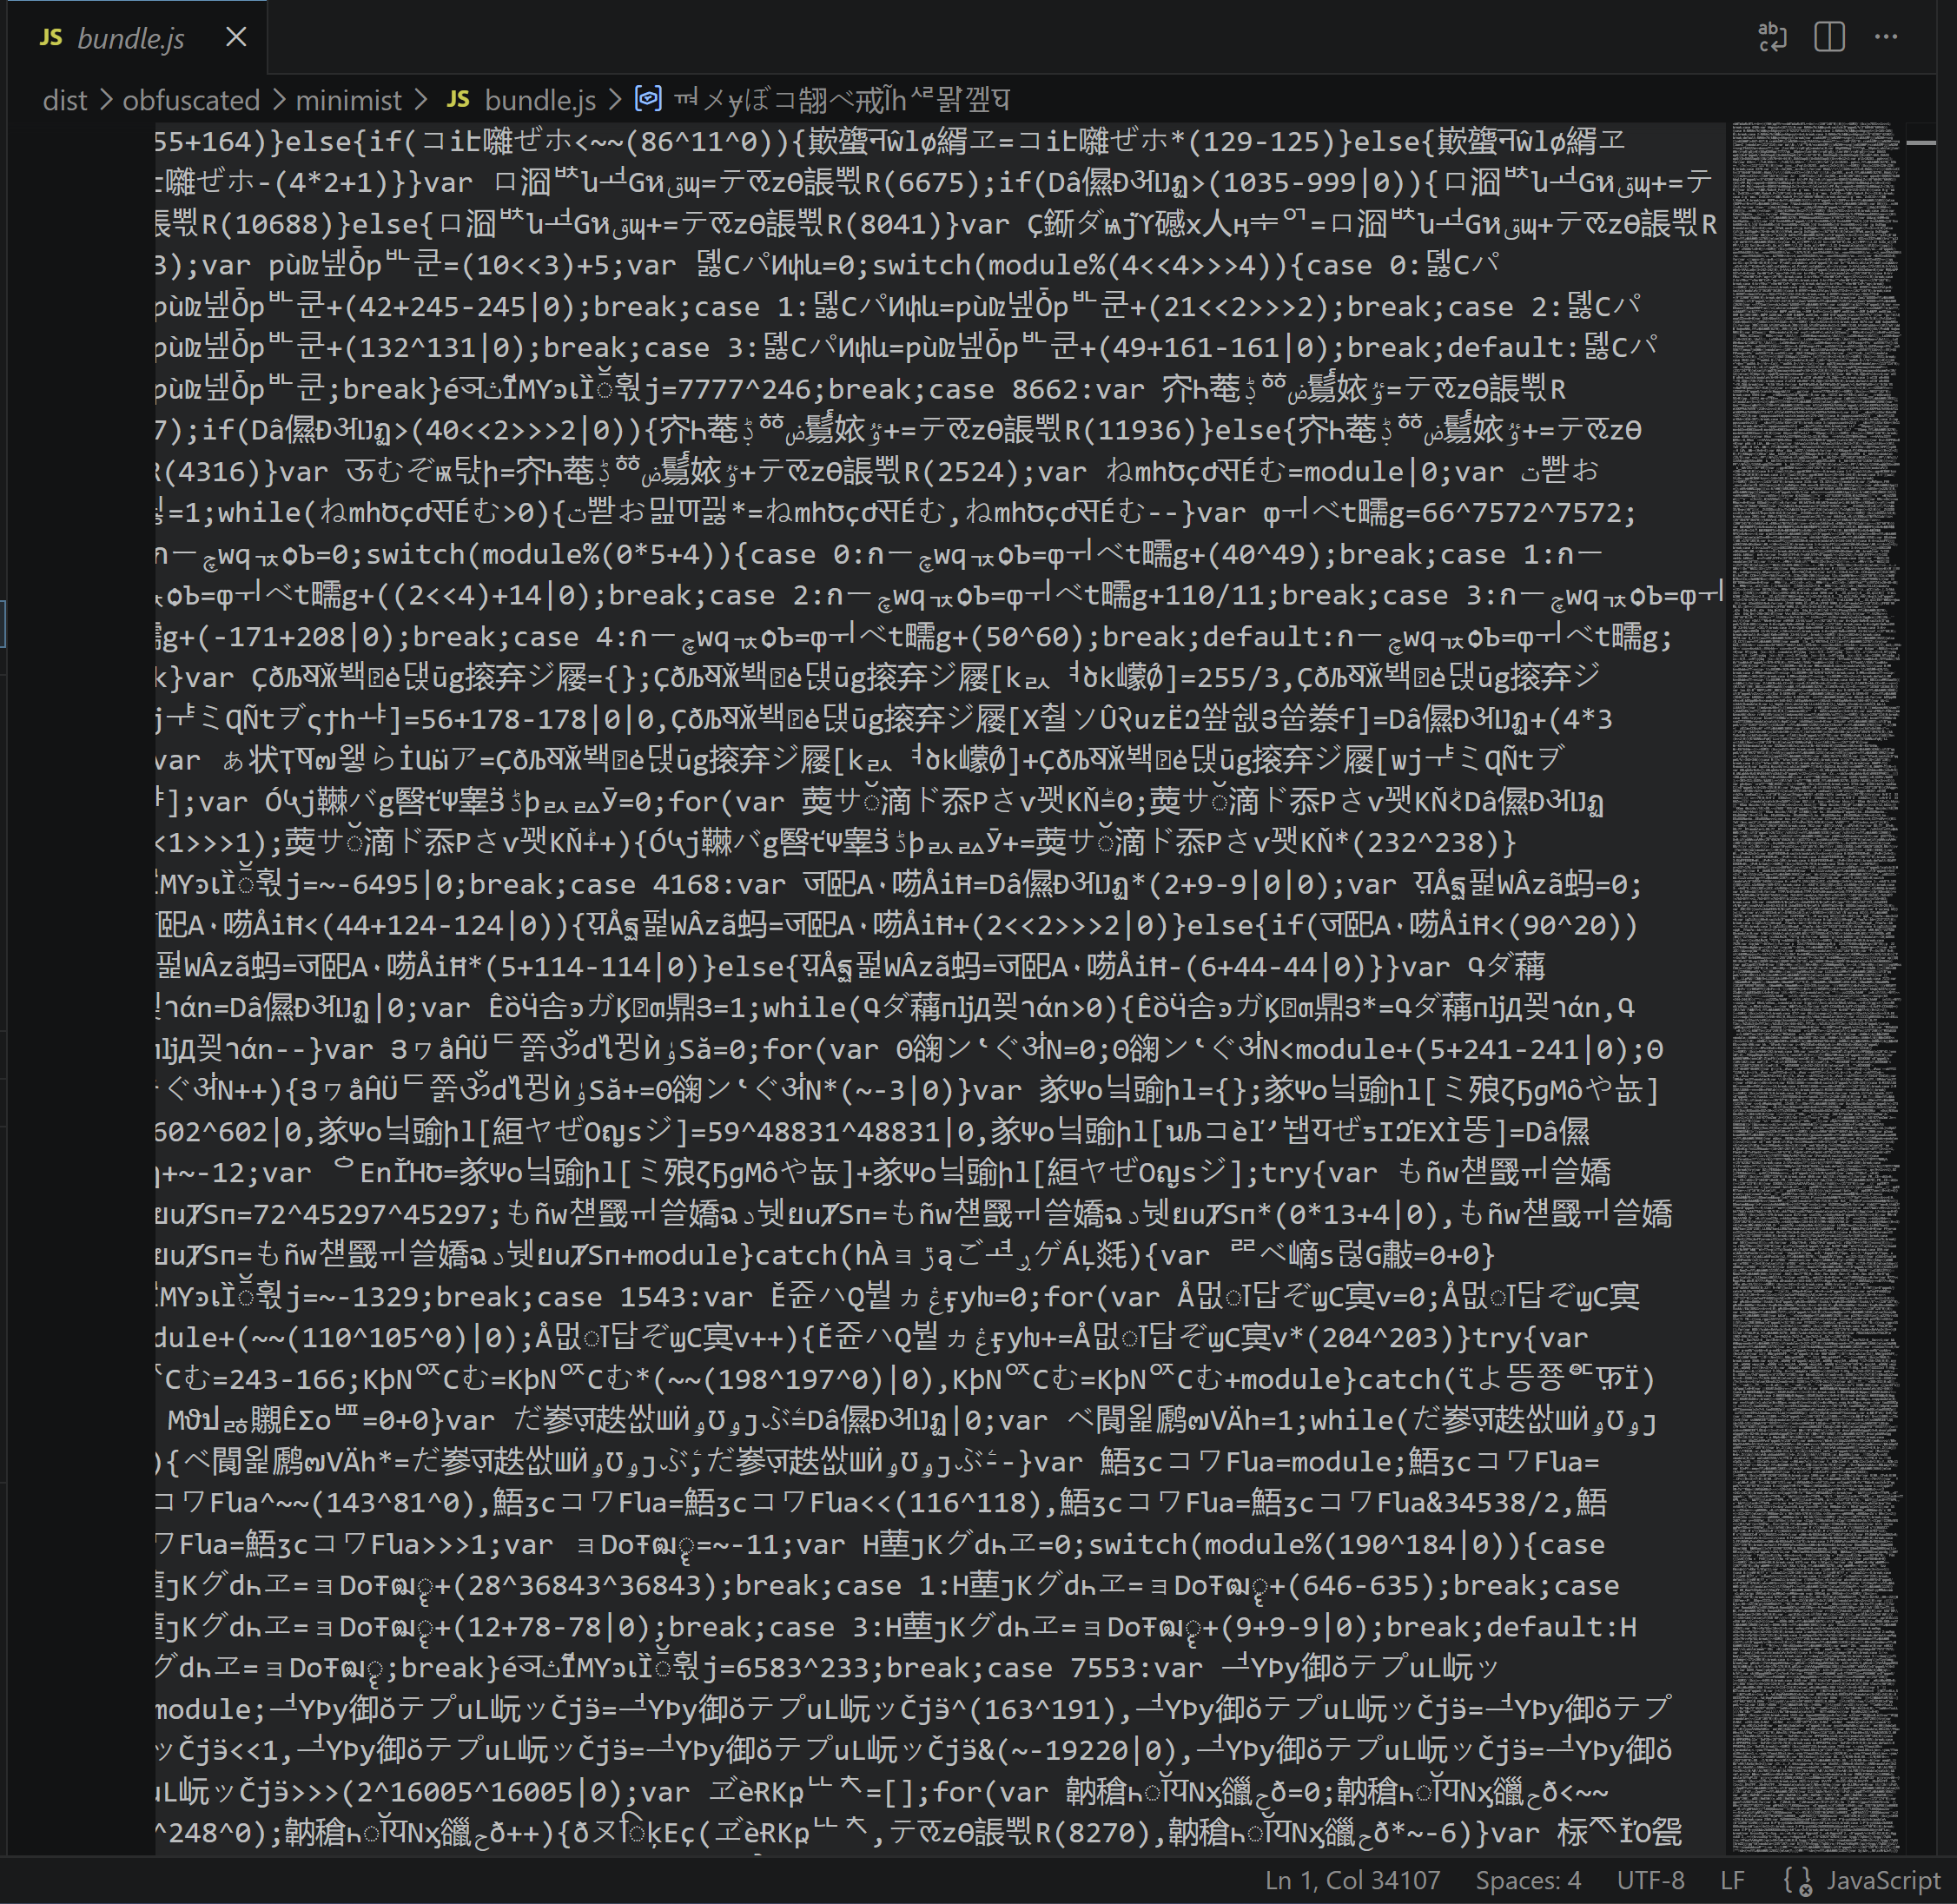 nstarke/egodeath
A JavaScript Obfuscator based on Cryptographic Indistinguishability Obfuscation techniques
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 rgielen/struts1filter
A request parameter filter solution for Struts 1 CVE-2014-0114 based on the work of Alvaro Munoz and the HP Fortify team
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner
 dedellix/mut-bc-ss-01
Mutation testing on X.509 Certificate Validation IN OpenSSL v.1.1.1h, based on CVE-2021-3450.
 joelbts/cve-2020-0601_poc
Demonstration of CVE-2020-0601 aka curveball. Based on the PoC's available at https://github.com/kudelskisecurity/chainoffools and…
 scabench/fastjson-tp1fn1
a scenario based on CVE-2022-25845 yielding a TP for metadata based SCA but a FN if the callgraph is used