
lfi
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
binary-analysiscode-analysisdynamic-analysis-sandboxing+4
118
lfi-project/lfiTop-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
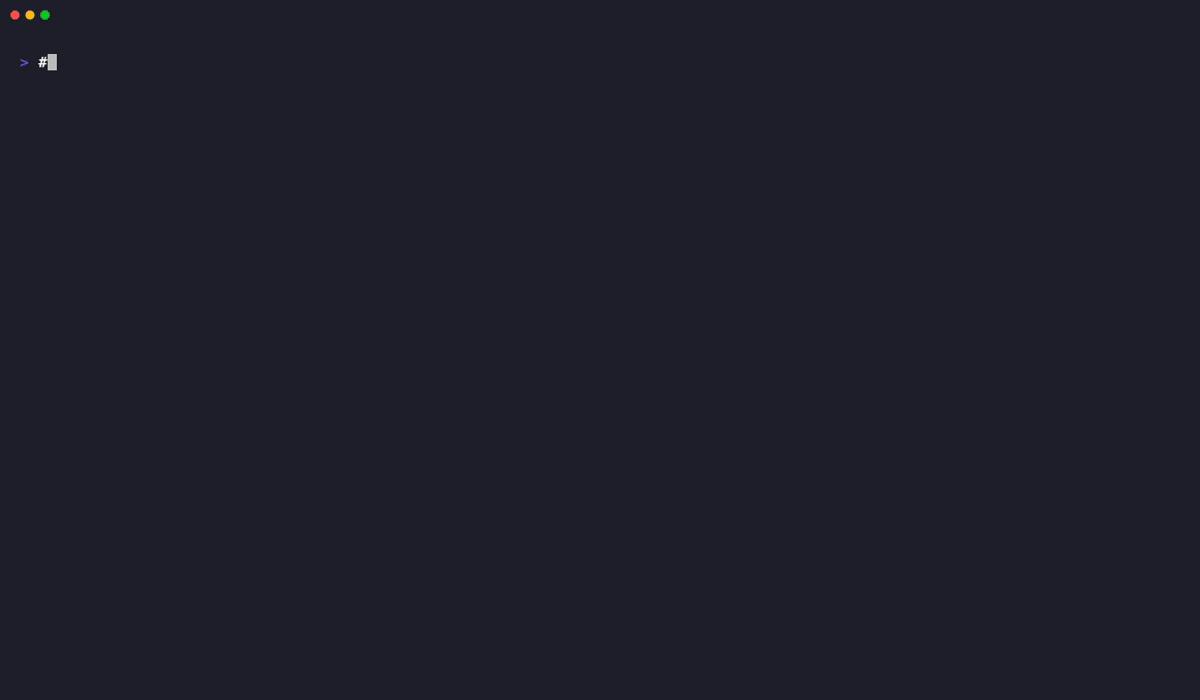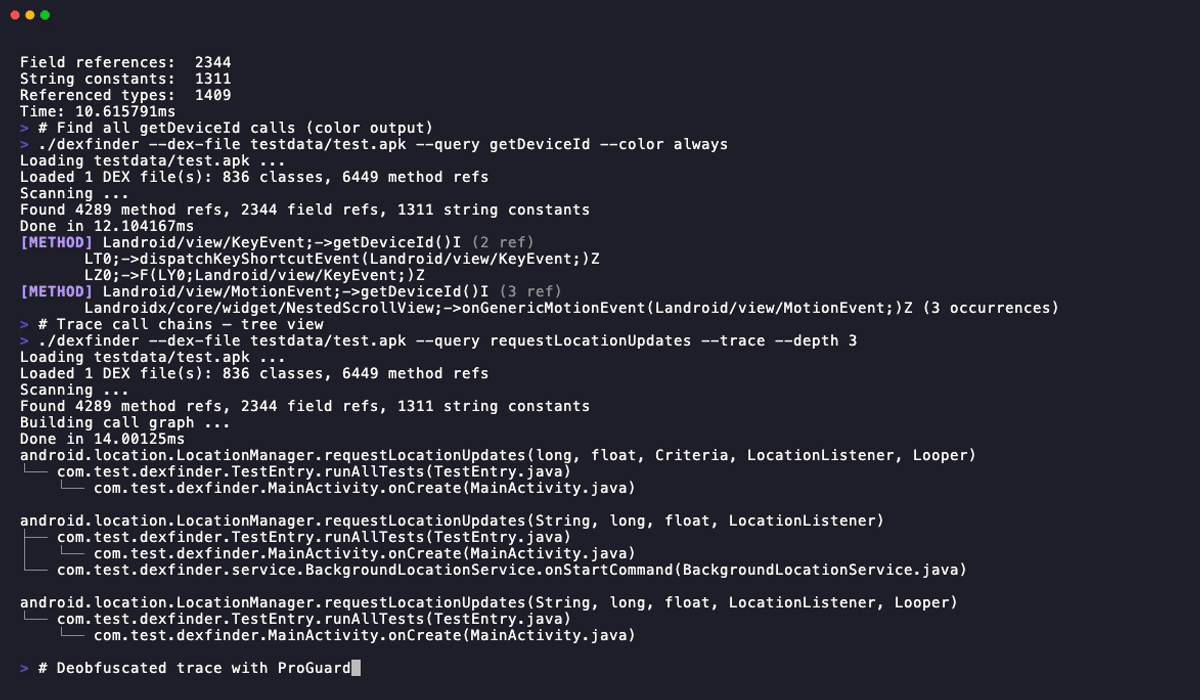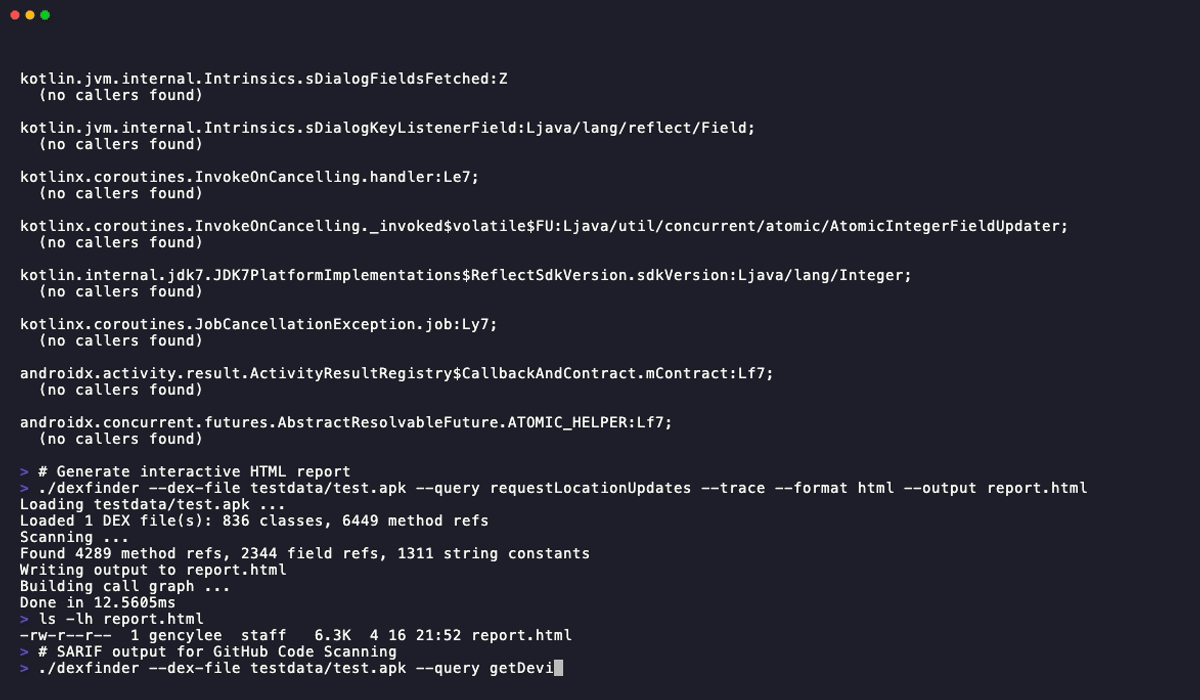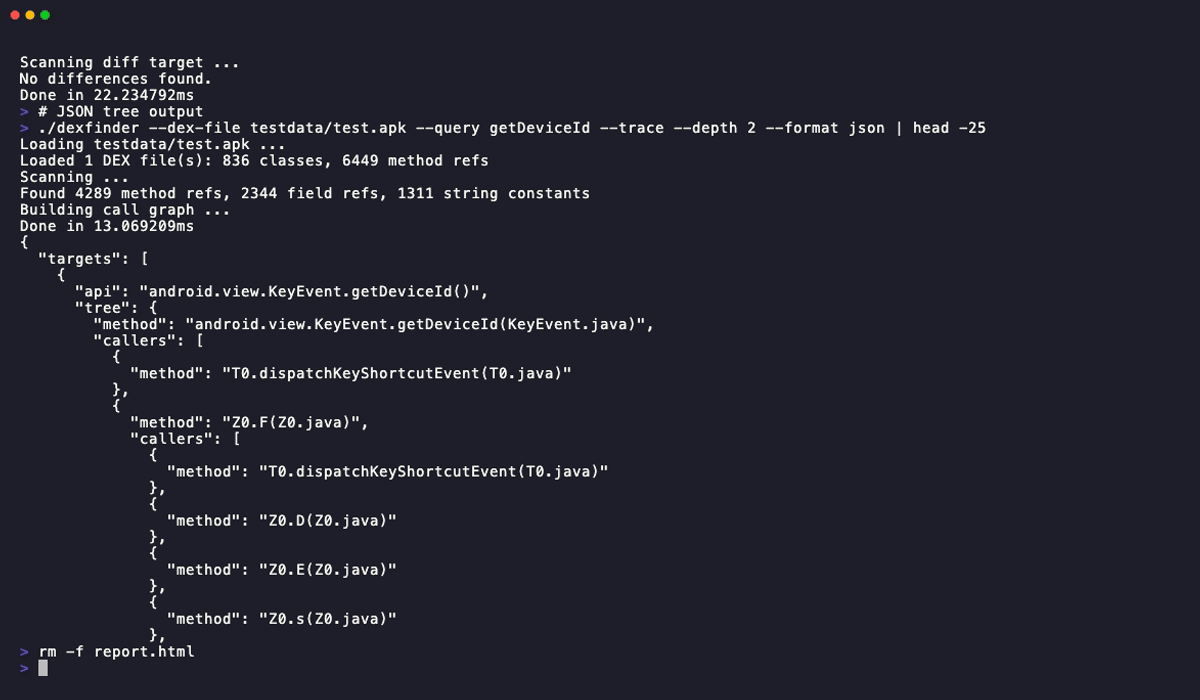 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 seifreed/yaraast
A powerful Python library and CLI tool for parsing, analyzing, and manipulating YARA rules through Abstract Syntax Tree (AST) representation
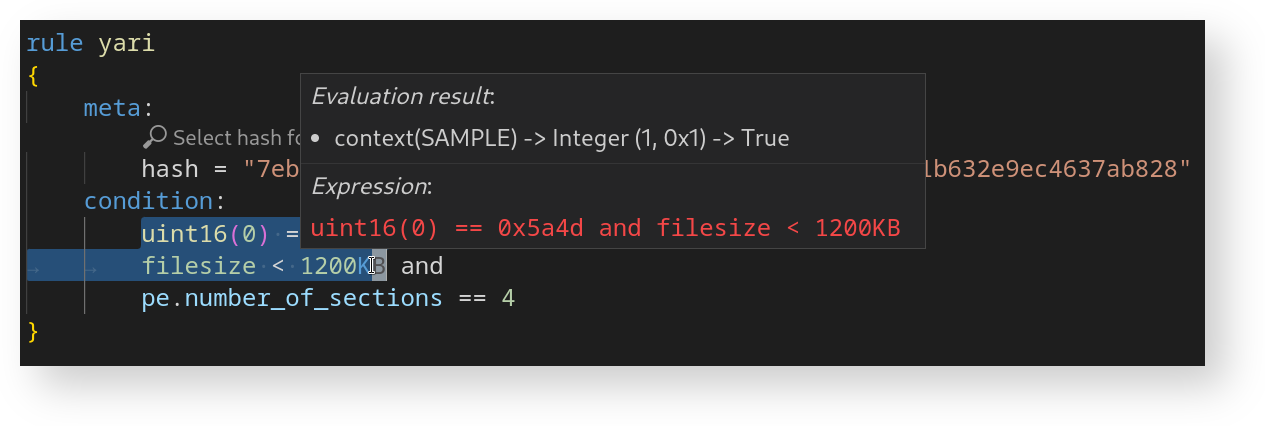 avast/yari
YARI is an interactive debugger for YARA Language.
 m417z/x64dbg-xfg-marker
An x64dbg plugin which marks XFG call signatures as data

 ahaggard2013/binaryninja-ollama
Plugin for Binary Ninja that integrates local Ollama models to rename functions and variables in decompiled HLIL code, preserving privacy by keeping…
 silverplate3/my-cves
CVE's I found. technical writeups, expolitation examples and fuzzing sessions walkthroughs
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.
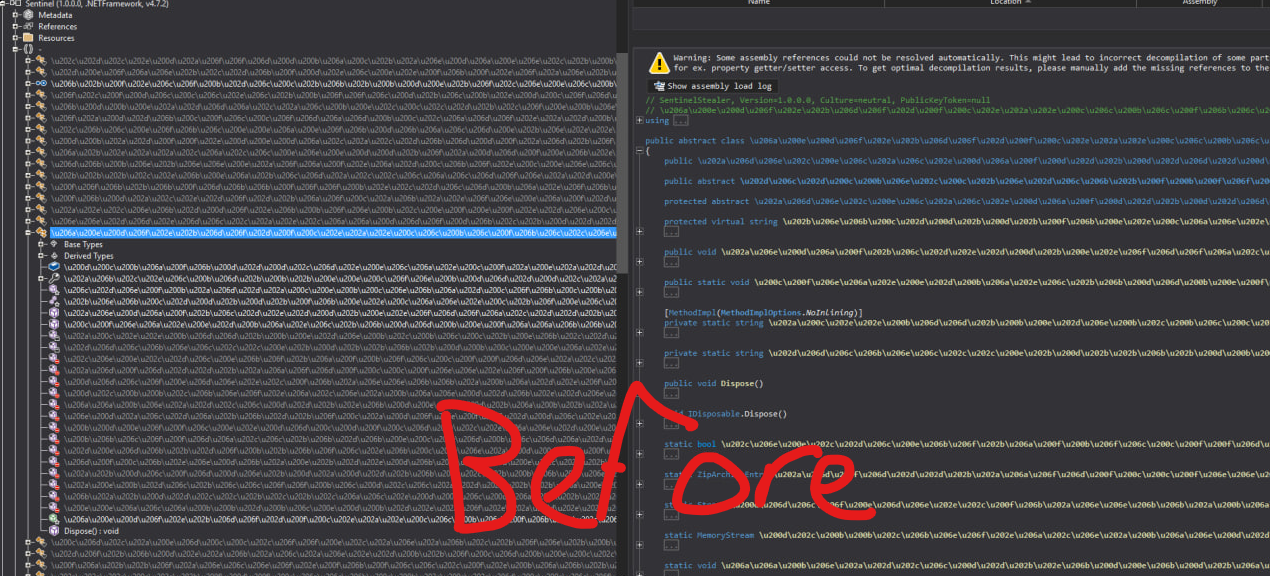 zypherion-technologies/unconfuserex
A ConfuserEx2 deobfuscator with support for anti tamper, compressor, constants, control flow, and resource recovery.
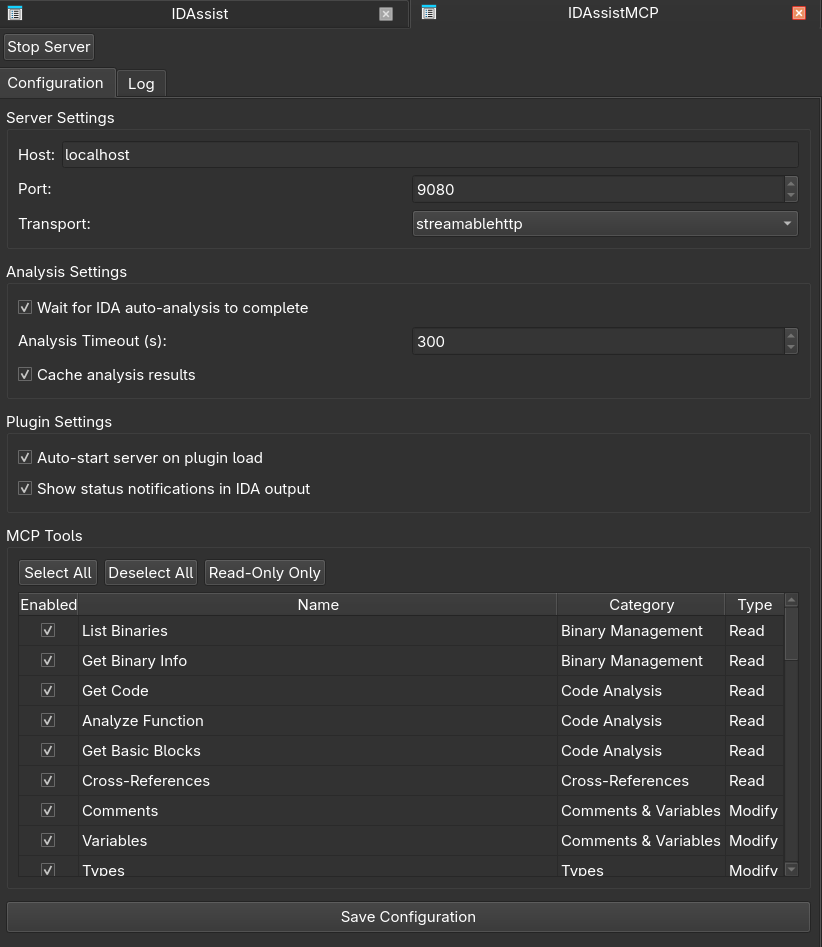 symgraph/idassistmcp
Standalone MCP server plugin for IDA Pro.
 ga1ois/blackhat-europe-2022
Select Bugs From Binary Where Pattern Like CVE-1337-Days
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 saint0x/fzy
a systems programming language prioritizing verifiable correctness, determinism, and performance
 zerowang030221/quantum-algorithm-for-elliptic-curve-discrete-logarithms-with-space-efficient-point-addition
Qiskit-based resource estimation framework for space-efficient quantum modular inversion and affine point-addition circuits used in elliptic-curve…
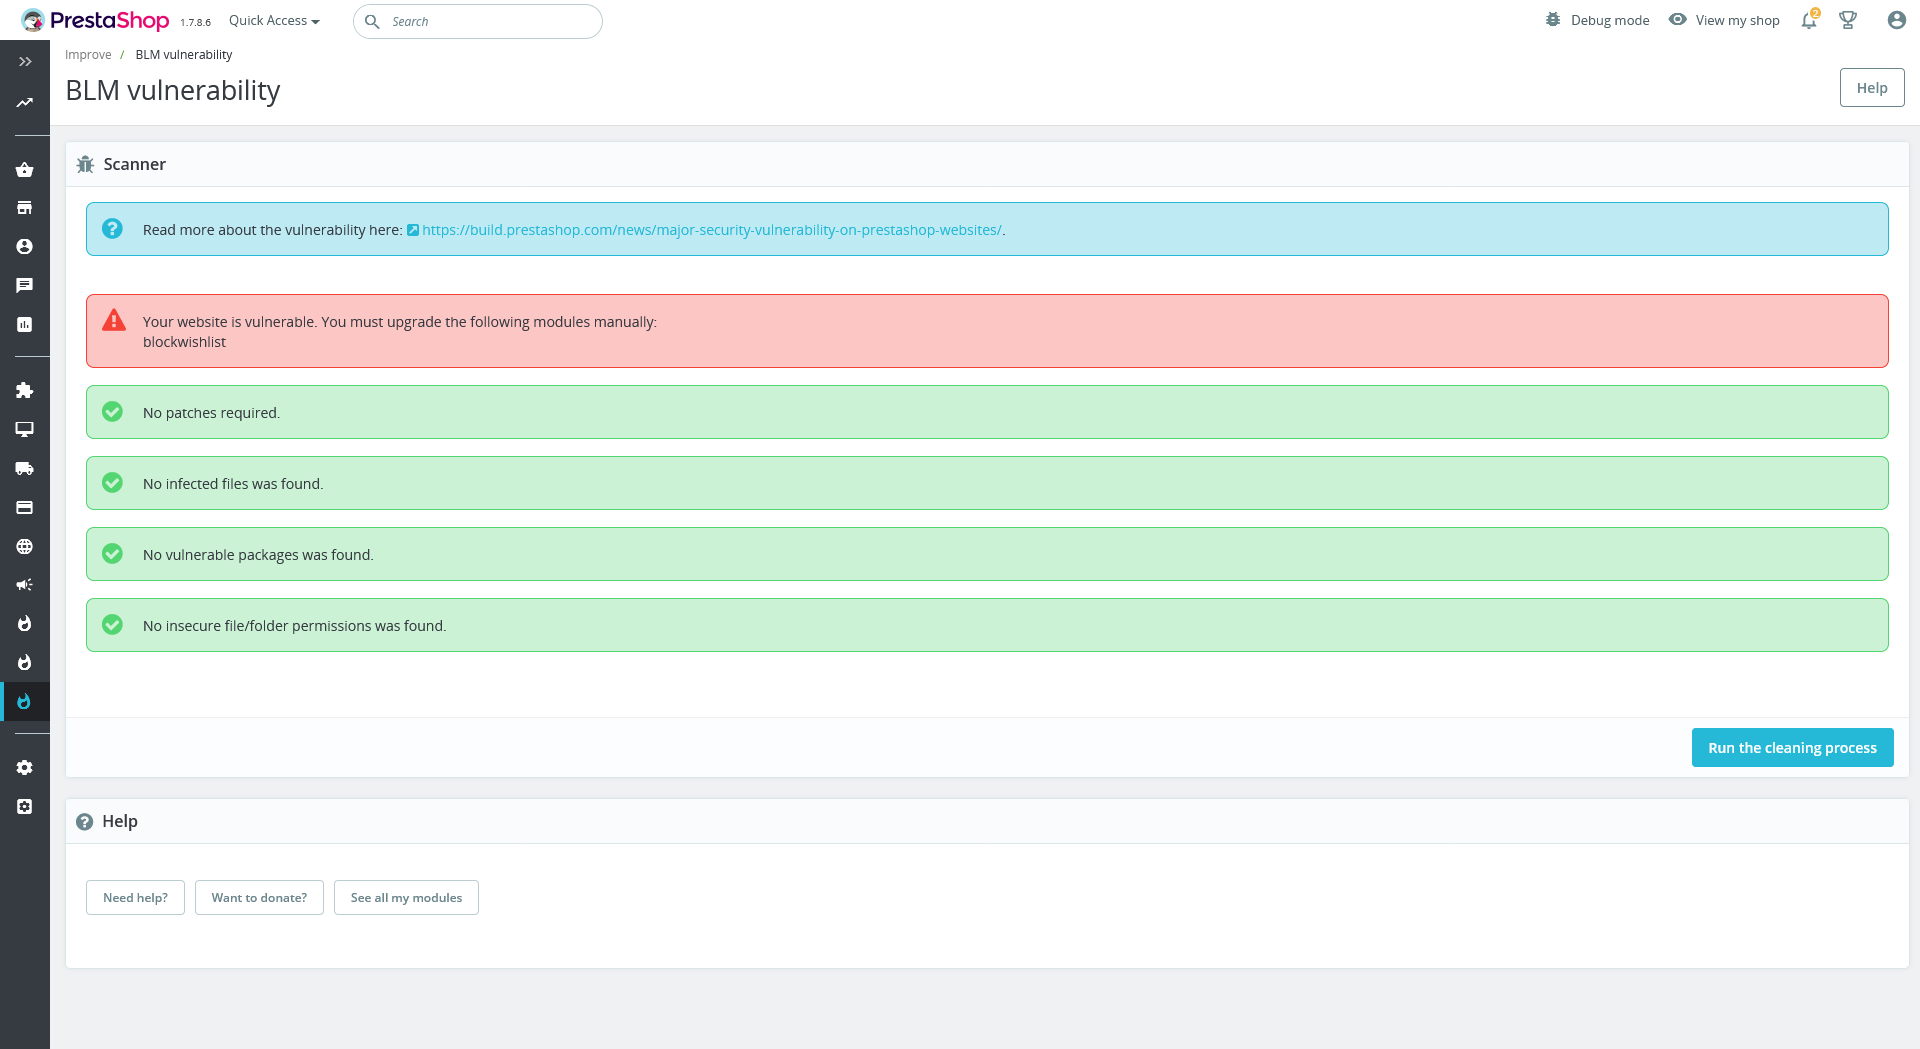 mathiasreker/blmvuln
Major Security Vulnerability on PrestaShop Websites - CVE-2022-31101