

CVE-2020-36184
 al1ex/cve-2020-36184
CVE-2020-36184 && Jackson-databind RCE
code-analysiseducationexploitation+3
al1ex/cve-2020-36184CVE-2020-36184 && Jackson-databind RCE
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
 whenx/cve-2026-0776
Security research and proof-of-concept for CVE-2026-0776 affecting Discord Desktop Client.
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
 nccgroup/lightweight_static_analysis
Create useful, lightweight static analyses using open source tools + a tiny bit of your code
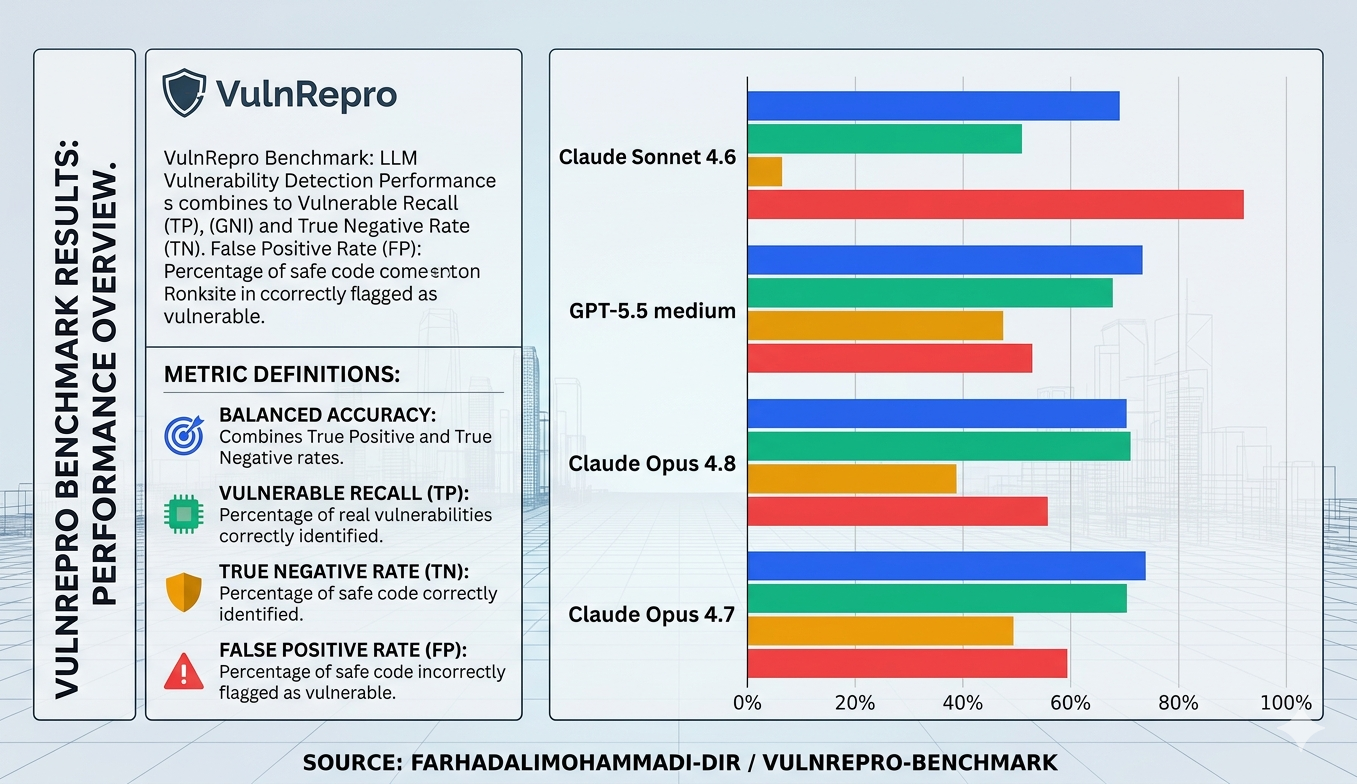 farhadalimohammadi-dir/vulnrepro-benchmark
Benchmark measuring AI models' ability to detect vulnerabilities in source code via real bug bounty cases with balanced recall and false-positive…
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
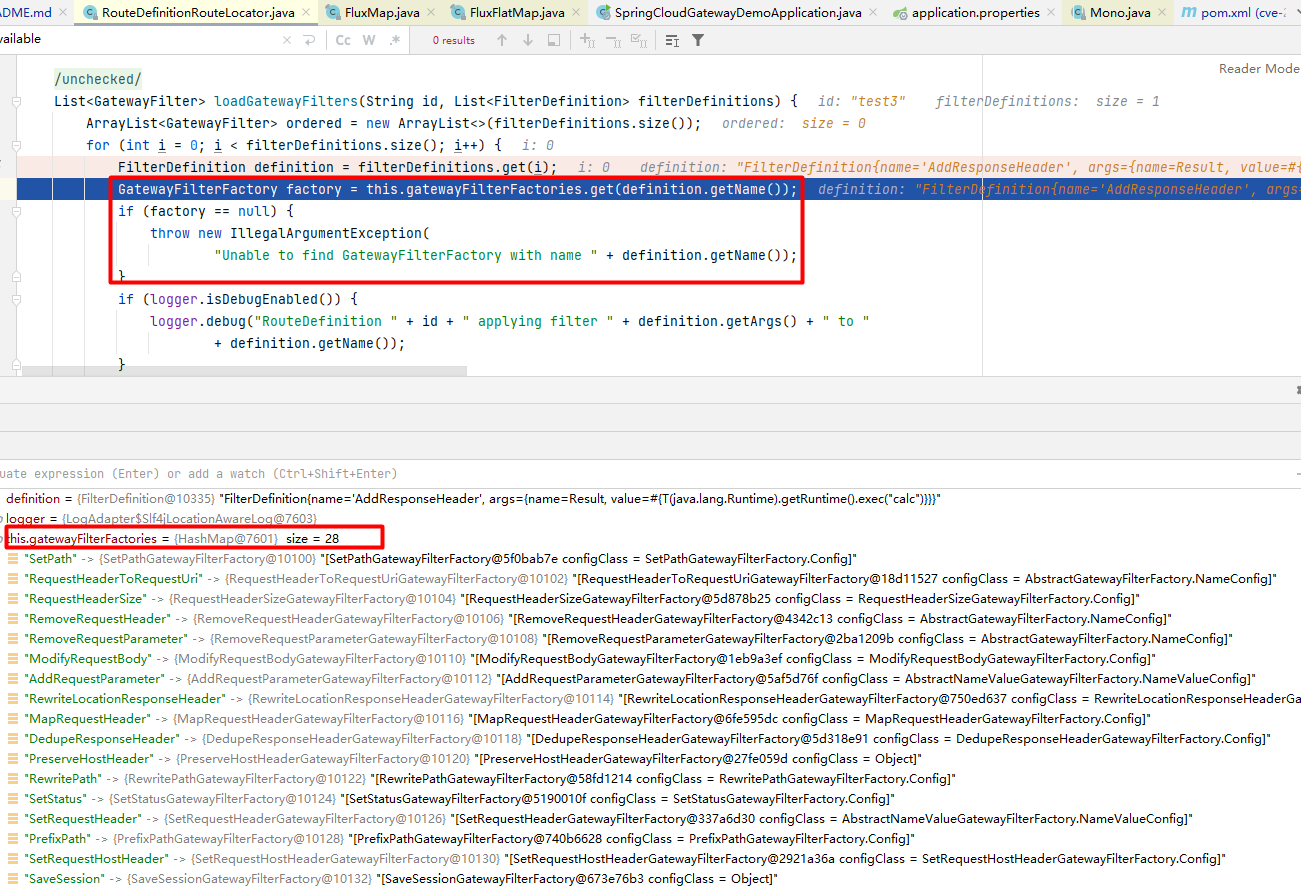 enokiy/cve-2022-22947-spring-cloud-gateway
Detailed analysis and exploit for CVE-2022-22947, a remote code execution vulnerability in Spring Cloud Gateway via SpEL injection in the Actuator…
 adityabhatt3010/react2shell-cve-2025-55182
React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…
 chybeta/cve-2018-11235-demo
Demonstrates exploitation of CVE-2018-11235, a Git submodule RCE vulnerability, with build script and analysis for educational purposes.
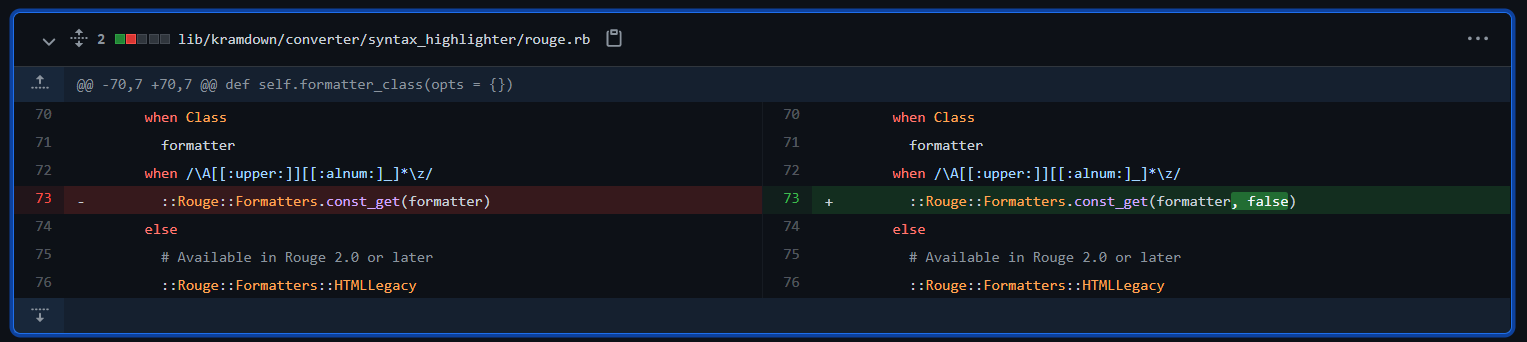
 vinsontang1/vultriage
The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection
 rvermeulen/codeql-workshop-cve-2021-21380
A CodeQL workshop covering CVE-2021-21380
 hakaioffsec/cve-2026-12191
PoC for CVE-2026-12191
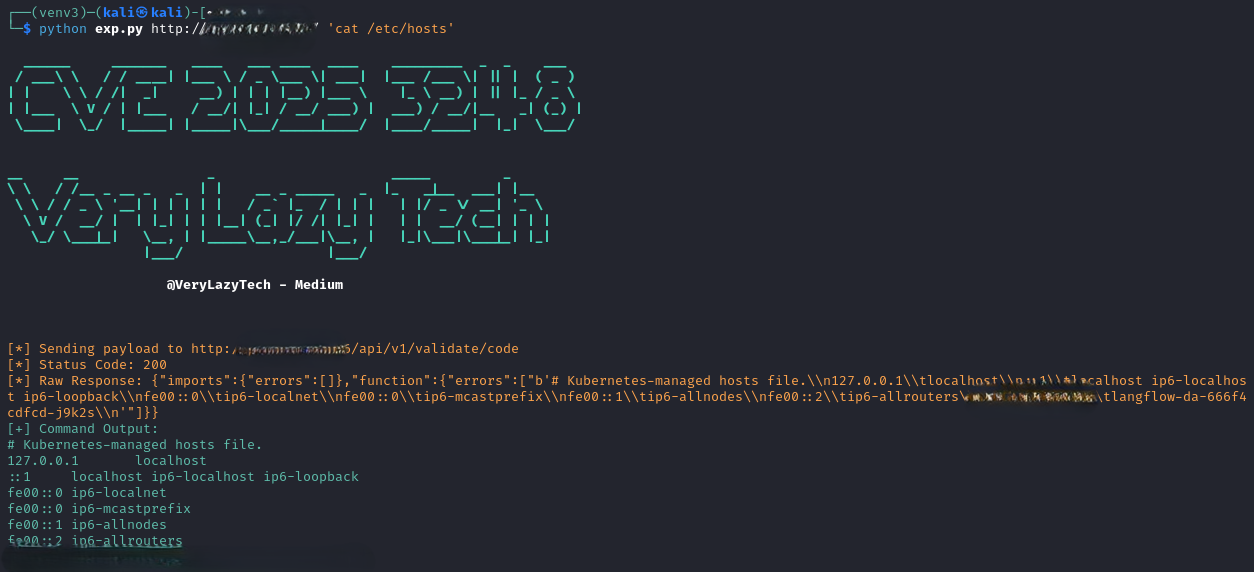 verylazytech/cve-2025-3248
Proof-of-concept exploit for CVE-2025-3248, a remote code injection vulnerability in Langflow prior to 1.3.0. Sends crafted HTTP requests to execute…
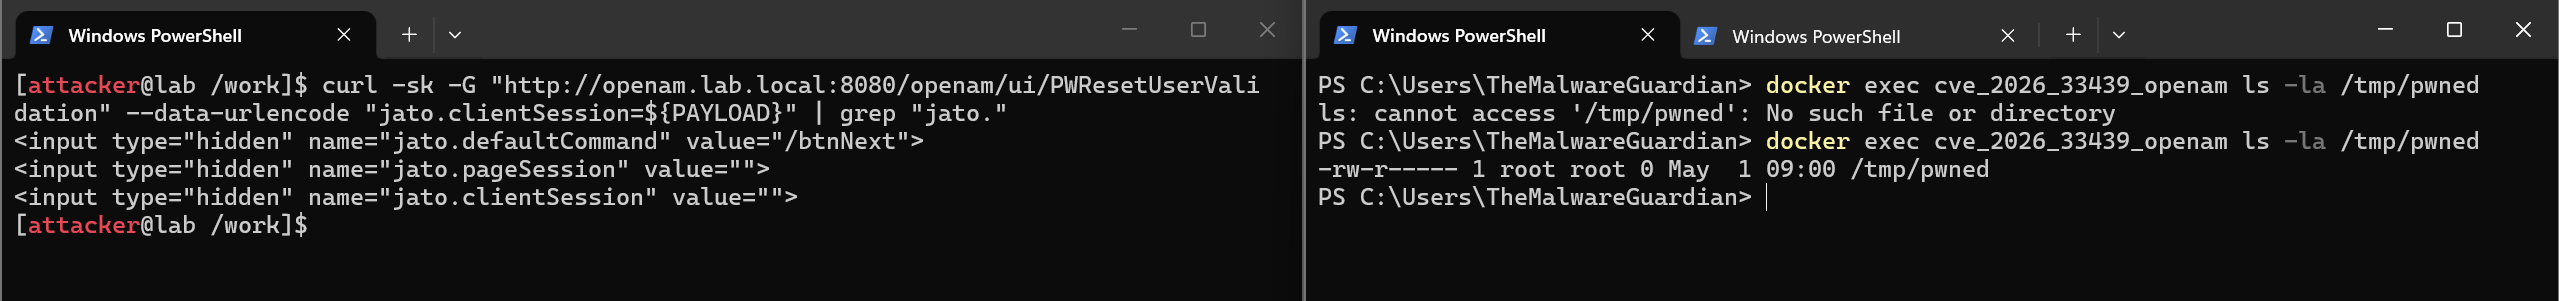 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
 al1ex/cve-2020-36188
CVE-2020-36188 &&Jackson-databind RCE