

CVE-2024-24725-PoC
 melkorw/cve-2024-24725-poc
Proof-of-concept exploit for CVE-2024-24725, demonstrating a web application vulnerability with PHP-based exploitation code for security testing and…
code-analysisexploitationpenetration-testing+2
1
melkorw/cve-2024-24725-pocProof-of-concept exploit for CVE-2024-24725, demonstrating a web application vulnerability with PHP-based exploitation code for security testing and…
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 dollarboysushil/dolibarr-17.0.0-exploit-cve-2023-30253
In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…
 zack0x01/vuln-app-cve-2025-55182
Intentionally vulnerable Next.js application demonstrating CVE-2025-55182 RCE via unsafe deserialization in React Server Components. Includes exploit…
 andrenasx/cve-2015-10034
Demonstrates CVE-2015-10034 in a vulnerable Java application, including SARIF analysis results from J-TAS Action for educational security testing.
 d3sca/cve-2024-52302
PoC exploit for CVE-2024-52302: unrestricted file upload in common-user-management Spring Boot app leading to remote code execution via…
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
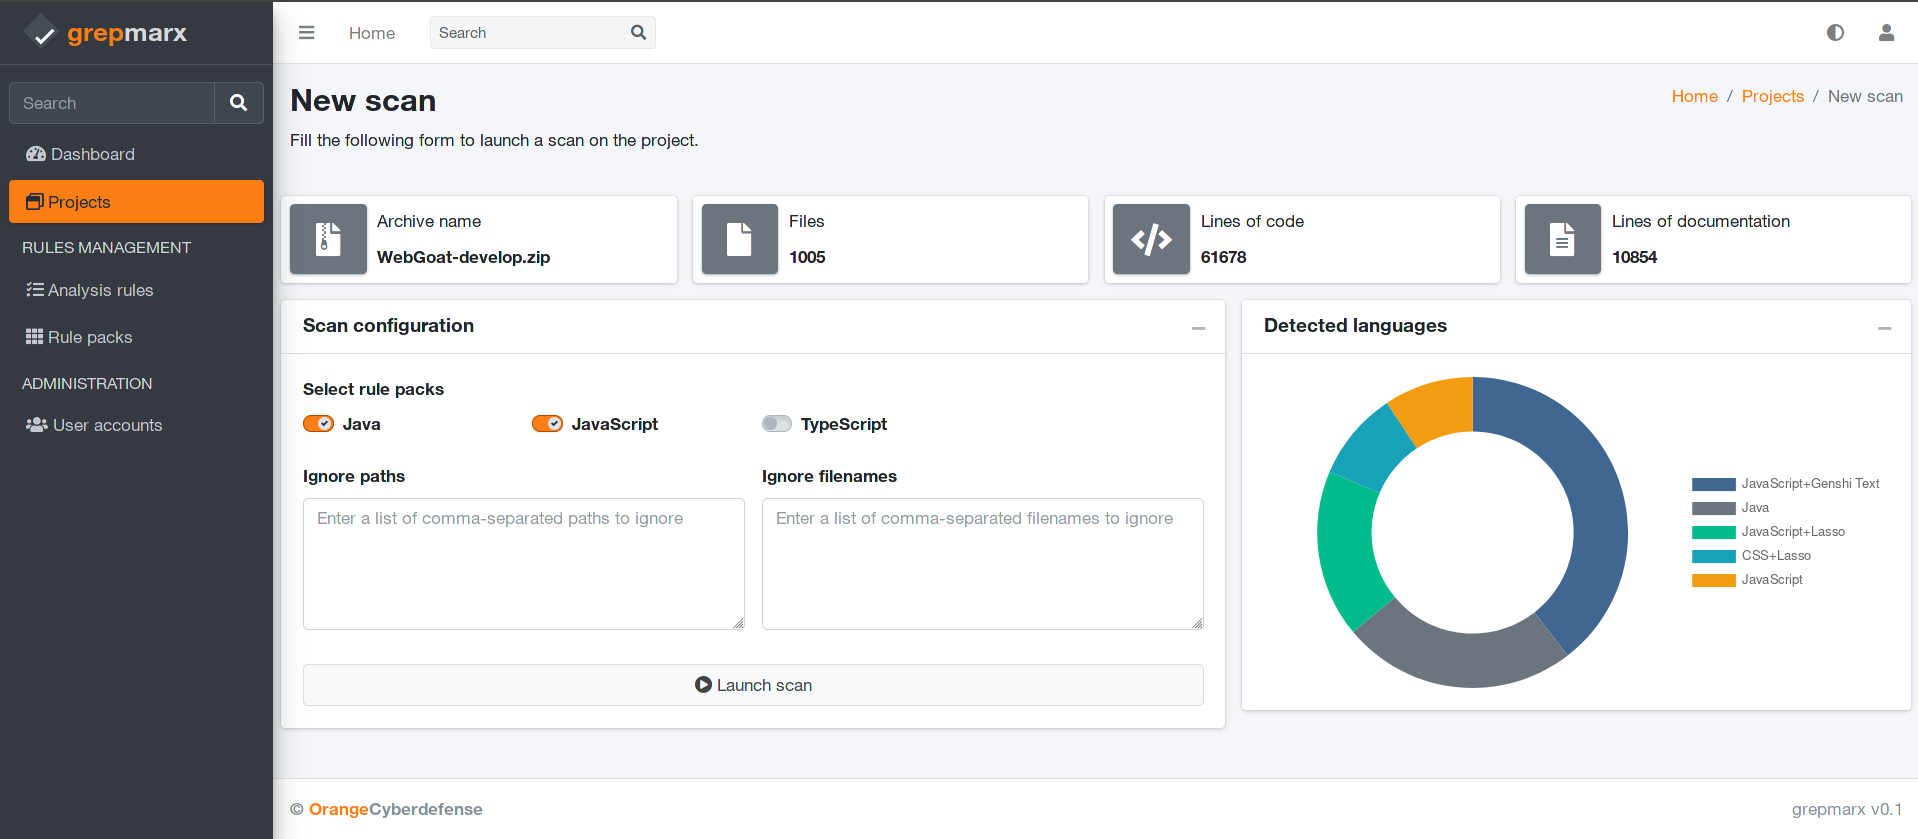 orange-cyberdefense/grepmarx
A source code static analysis platform for AppSec enthusiasts.
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 theopaid/cve-2026-66746-http-response-splitting-via-unvalidated-response-header-values-rouille-
Security Advisory: HTTP Response Splitting via Unvalidated Response Header Values (rouille)
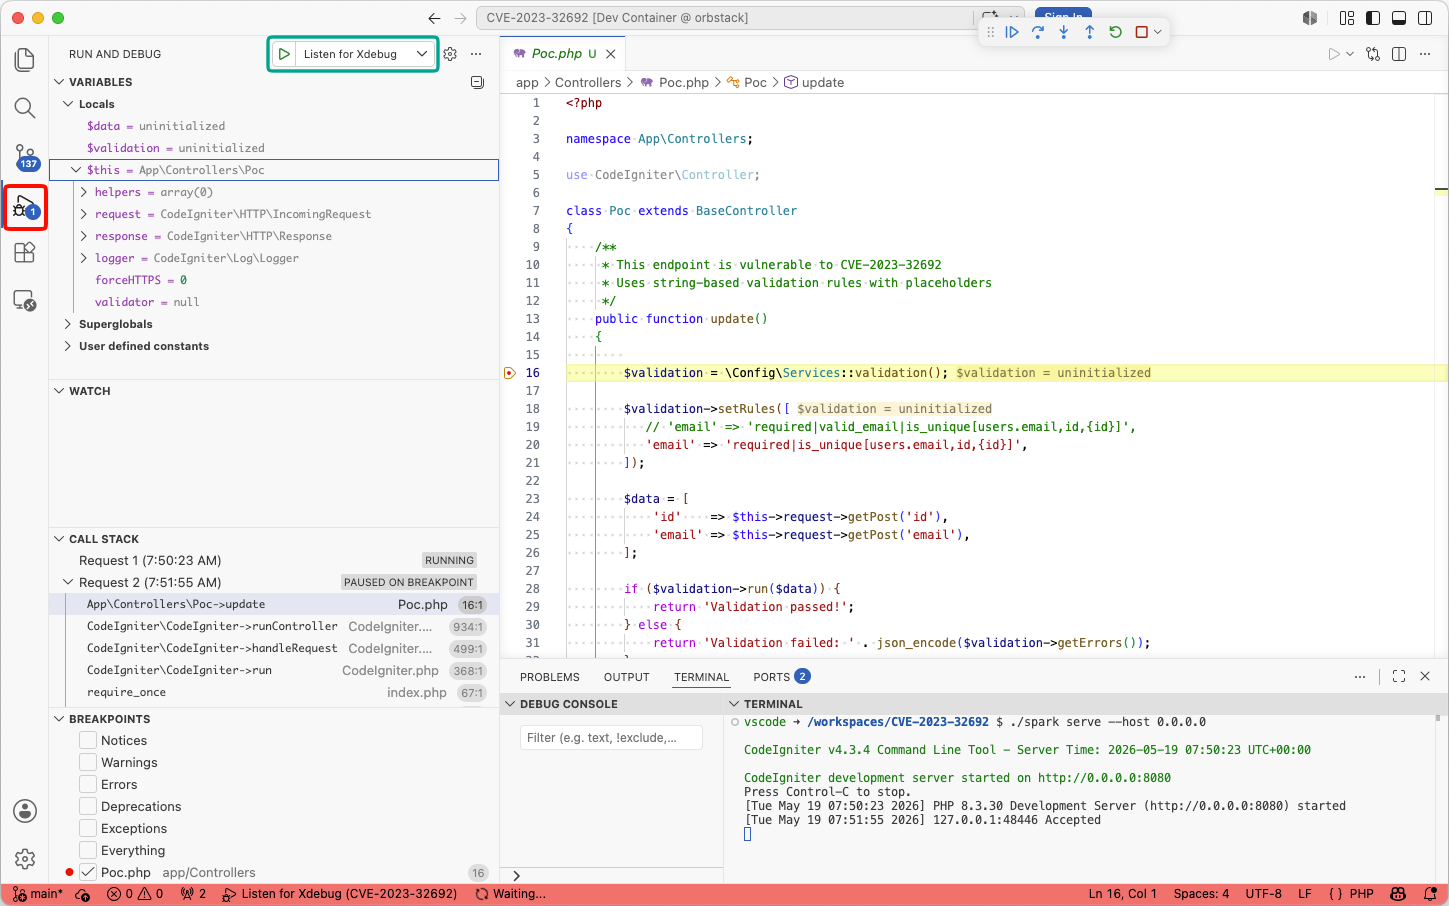 mogwailabs/cve-2023-32692-codeigniter4
Example application, vulnerable to CVE-2023-32692 (Validation Rule Injection in the PHP Framework CodeIgniter)
 sakib570/cve-2018-1263-demo
Educational exploit demo for CVE-2018-1263 (phpMyAdmin RCE/LFI). Includes vulnerable environment setup via Docker and step-by-step attack walkthrough…
 scabench/jsonorg-fn1
simple application with a CVE-2022-45688 vulnerability
 yosasasutsut/cve-2025-56803
OS Command Injection Vulnerability via Plugin Execution in Figma Desktop Application