
ReactOOPS-WriteUp
 thestingr/reactoops-writeup
Hack The Box Writeup for Retired Challenge ReactOOPS - Complete solution and educational guide to CVE-2025-55182/CVE-2025-66478 (React2Shell RCE).…
code-analysisctfeducation+8
6
thestingr/reactoops-writeupHack The Box Writeup for Retired Challenge ReactOOPS - Complete solution and educational guide to CVE-2025-55182/CVE-2025-66478 (React2Shell RCE).…
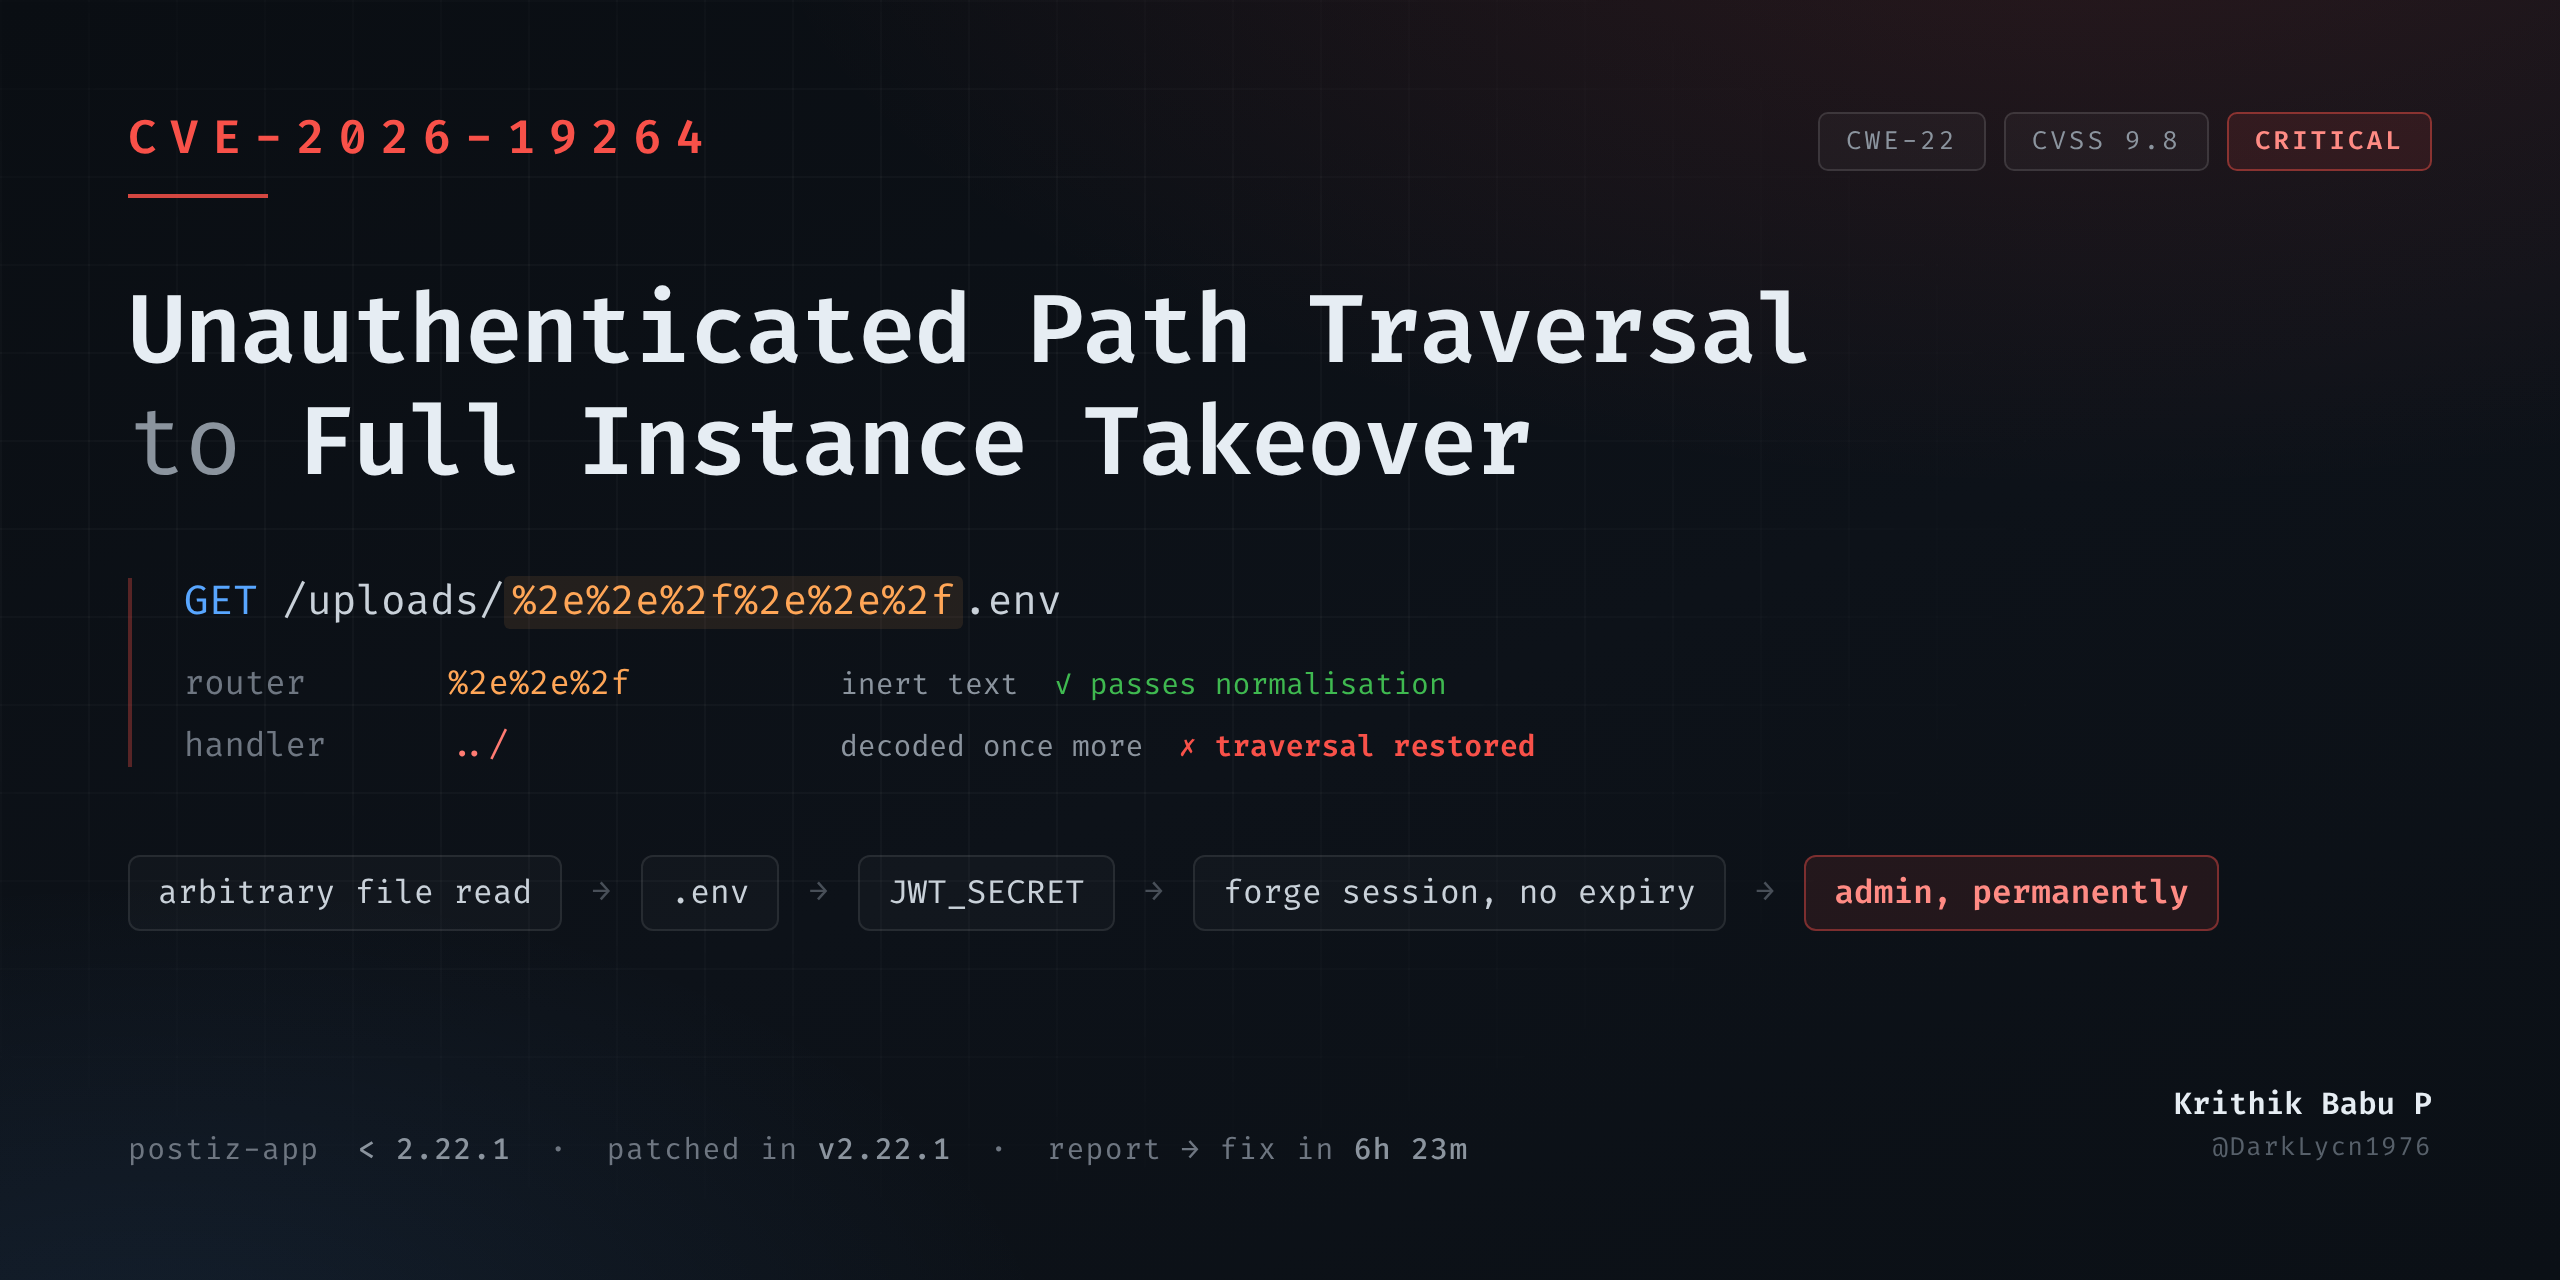 darklycn1976/cve-2026-19264
CVE-2026-19264 - Critical unauthenticated path traversal to full instance takeover in Postiz (< 2.22.1). Technical writeup: decode-order bypass,…
 0x00phantom-hat/cve-2026-5029-exploit
Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…
 oscerd/cve-2026-49098
PoC reproducer for CVE-2026-49098 (Apache Camel camel-kafka): the non-Camel-prefixed kafka.OVERRIDE_TOPIC header escapes the upstream HTTP header…
 romain-deperne/cve-2026-48017
Remote Code Execution in DbGate via functionName injection in the loadReader endpoint — CVSS 8.8
 nixon-h/cve-2025-68147-ospos-stored-xss
PoC repository for CVE-2025-68147: Stored Cross-Site Scripting (XSS) in OpenSourcePOS. Vulnerability allows privilege escalation via malicious…
 oscerd/cve-2026-55994
PoC reproducer for CVE-2026-55994 (Apache Camel camel-iggy): the consumer copies an Iggy message's user-headers onto the Exchange unfiltered, so an…
 0xmrma/cve-2026-14361
Consul Template's writeToFile helper opened an operator-supplied destination directly and followed linked path components, allowing rendered output…
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 r0ngy40/cve-2025-30208-series
Analysis of the Reproduction of CVE-2025-30208 Series Vulnerabilities
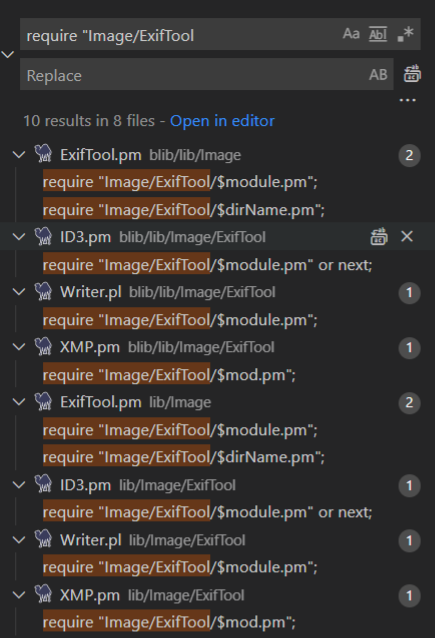 trganda/cve-2021-22204
In-depth technical analysis of CVE-2021-22204 (ExifTool RCE) with PoC reproduction, payload construction, and Perl code review of the vulnerable DjVu…
 kunalkhandelwal-dev/cve-2021-41773-source-code-analysis
A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 datawiza-inc/spring-rec-demo
The demo code showing the recent Spring4Shell RCE (CVE-2022-22965)
 rat5ak/cve-2025-55182-react2shell-rce-poc
This repository documents research into deserialization behavior within Next.js React Server Components (RSC) using the Flight protocol. It focuses…
 itsc1sco/freepbx-sqli-exploit-privilege-escalation
This walkthrough documents the complete compromise of the HTB machine Connected.
 oscerd/cve-2026-49042
PoC reproducer for CVE-2026-49042 (Apache Camel camel-langchain4j-tools): a prompt-injected LLM's tool-call arguments become unfiltered Exchange…
 dhammon/pfblockerng-cve-2022-40624
Proof-of-concept exploit for unauthenticated remote code execution in pfBlockerNg via unsanitized input in the DNSBL TLD query function, with SAST…