
mininode
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
code-analysiseducationpapers-research+3
21
wspr-ncsu/mininodeStatic analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
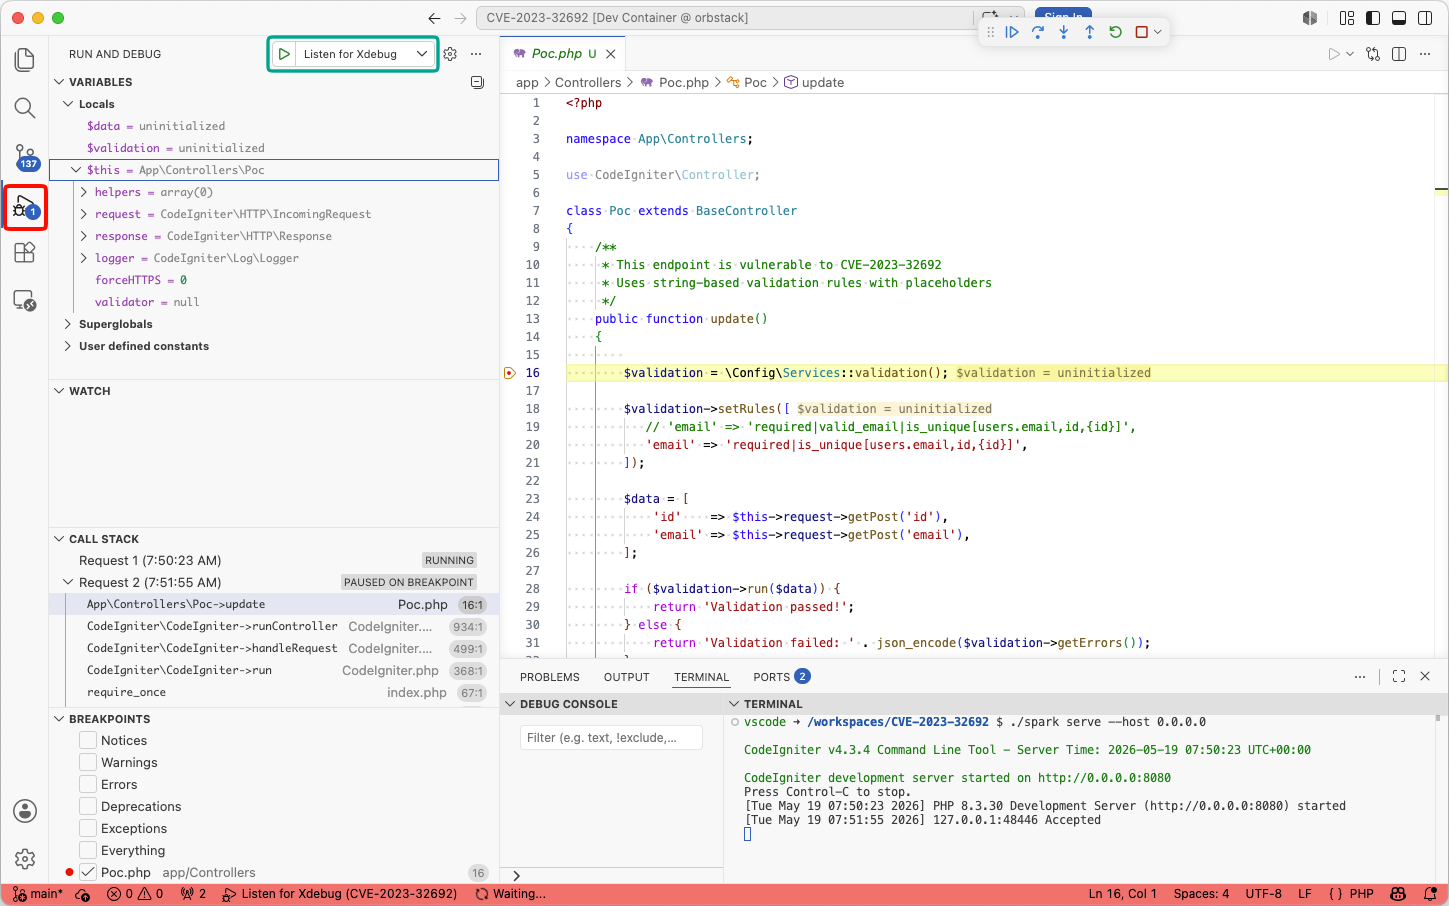 mogwailabs/cve-2023-32692-codeigniter4
Example application, vulnerable to CVE-2023-32692 (Validation Rule Injection in the PHP Framework CodeIgniter)
 yosasasutsut/cve-2025-56803
OS Command Injection Vulnerability via Plugin Execution in Figma Desktop Application
 kov404/cve-2025-56515
Cross-Site Scripting (XSS) Vulnerability in Fiora Chat Application
 theratpack/grails-javamelody-sample-app
Grails sample application using the Javamelody 1.44 plugin to illustrate the CVE-2013-4378 vulnerability.
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 a1ohadance/cve-2026-38360
Advisory: CVE-2026-38360 path traversal (CWE-22) in dash-uploader (Python/PyPI)
 phusion/rails-cve-2012-5664-test
Demo app showing how the Rails CVE-2013-5664 vulnerability works.
 themehackers/cve-2026-34038
CVE-2026-34038: Authenticated Remote Command Injection in Coolify
 g4nkd/cve-2023-30253-poc
I couldn’t find a PoC for CVE-2023-30253, so I developed an effective one
 shoucheng3/jenkinsci__git-client-plugin_cve-2019-10392_2-8-4
Jenkins plugin providing Git APIs for automated repository operations including fetch, checkout, merge, and tag, with support for credential-based…
 lycshub/cve-2020-5245
Proof-of-concept exploit for CVE-2020-5245, demonstrating expression language injection in Dropwizard REST endpoints via crafted HTTP parameters.
 trickstersec/cve-2019-5420
Exploit for the Rails CVE-2019-5420
 snicoll-scratches/spring-boot-cve-2022-22965
Showcase of overridding the Spring Framework version in older Spring Boot versions
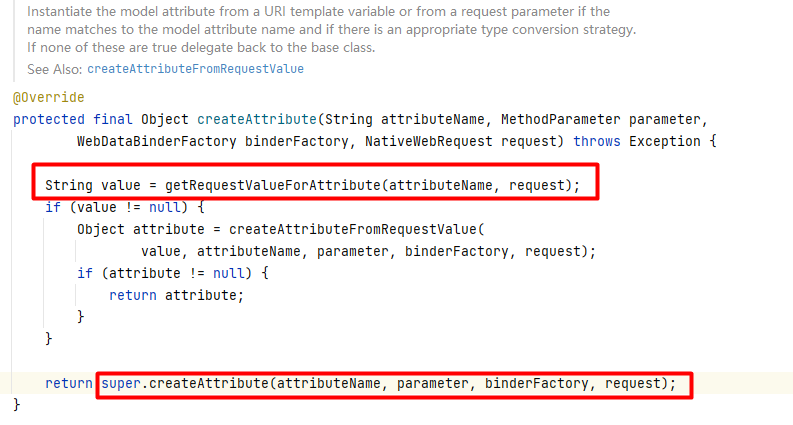 enokiy/spring-rce-cve-2022-22965
Educational analysis and proof-of-concept exploit for CVE-2022-22965, a Spring MVC/WebFlux remote code execution vulnerability via data binding on…
