

spring-amqp-deserialization
 x1r0z/spring-amqp-deserialization
PoC of Spring AMQP Deserialization Vulnerability (CVE-2023-34050)
code-analysisexploitationpenetration-testing+2
13
x1r0z/spring-amqp-deserializationPoC of Spring AMQP Deserialization Vulnerability (CVE-2023-34050)
 mpgn/cve-2018-19276
CVE-2018-19276 - OpenMRS Insecure Object Deserialization RCE
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 p0in7s/cve-2024-38475
Proof-of-concept exploit for CVE-2024-38475 targeting Apache HTTP Server mod_rewrite improper escaping, enabling URL-to-filesystem mapping for code…
 sickwell/cve-2025-55182
CVE-2025-55182 - React Server Components RCE Exploit & Scanner Supports external servers and CLI interface
 jweny/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980, a remote code execution vulnerability in Spring Data MongoDB via SpEL injection in the username…
 theori-io/reactguard
ReactGuard provides framework- and vulnerability-detection tooling for CVE-2025-55182 (React2Shell)
 sudistark/vscode-rce-electrovolt
Trying to reproduce CVE-2021-43908
 hunntr/cve-2023-46818
An issue was discovered in ISPConfig before 3.2.11p1. PHP code injection can be achieved in the language file editor by an admin if…
 elpe-pinillo/cve-2023-6246
C-based proof-of-concept exploit for CVE-2023-6246, targeting a privilege escalation vulnerability in the Linux kernel's syscalls. Tested on Fedora…
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
 dollarboysushil/dolibarr-17.0.0-exploit-cve-2023-30253
In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…
 csenox/cve-2021-21425
GravCMS Unauthenticated Arbitrary YAML Write/Update leads to Code Execution (CVE-2021-21425)

 babyteam1024/cve-2021-2394
Exploit code for CVE-2021-2394, a Java vulnerability, providing proof-of-concept for security testing and research.
 fuzzlove/fudforum-xss-rce
FUDForum 3.0.9 - XSS / Remote Code Execution (CVE-2019-18873, CVE-2019-18839)
 vulnmachines/spring-cve-2022-22947
Spring cloud gateway code injection : CVE-2022-22947
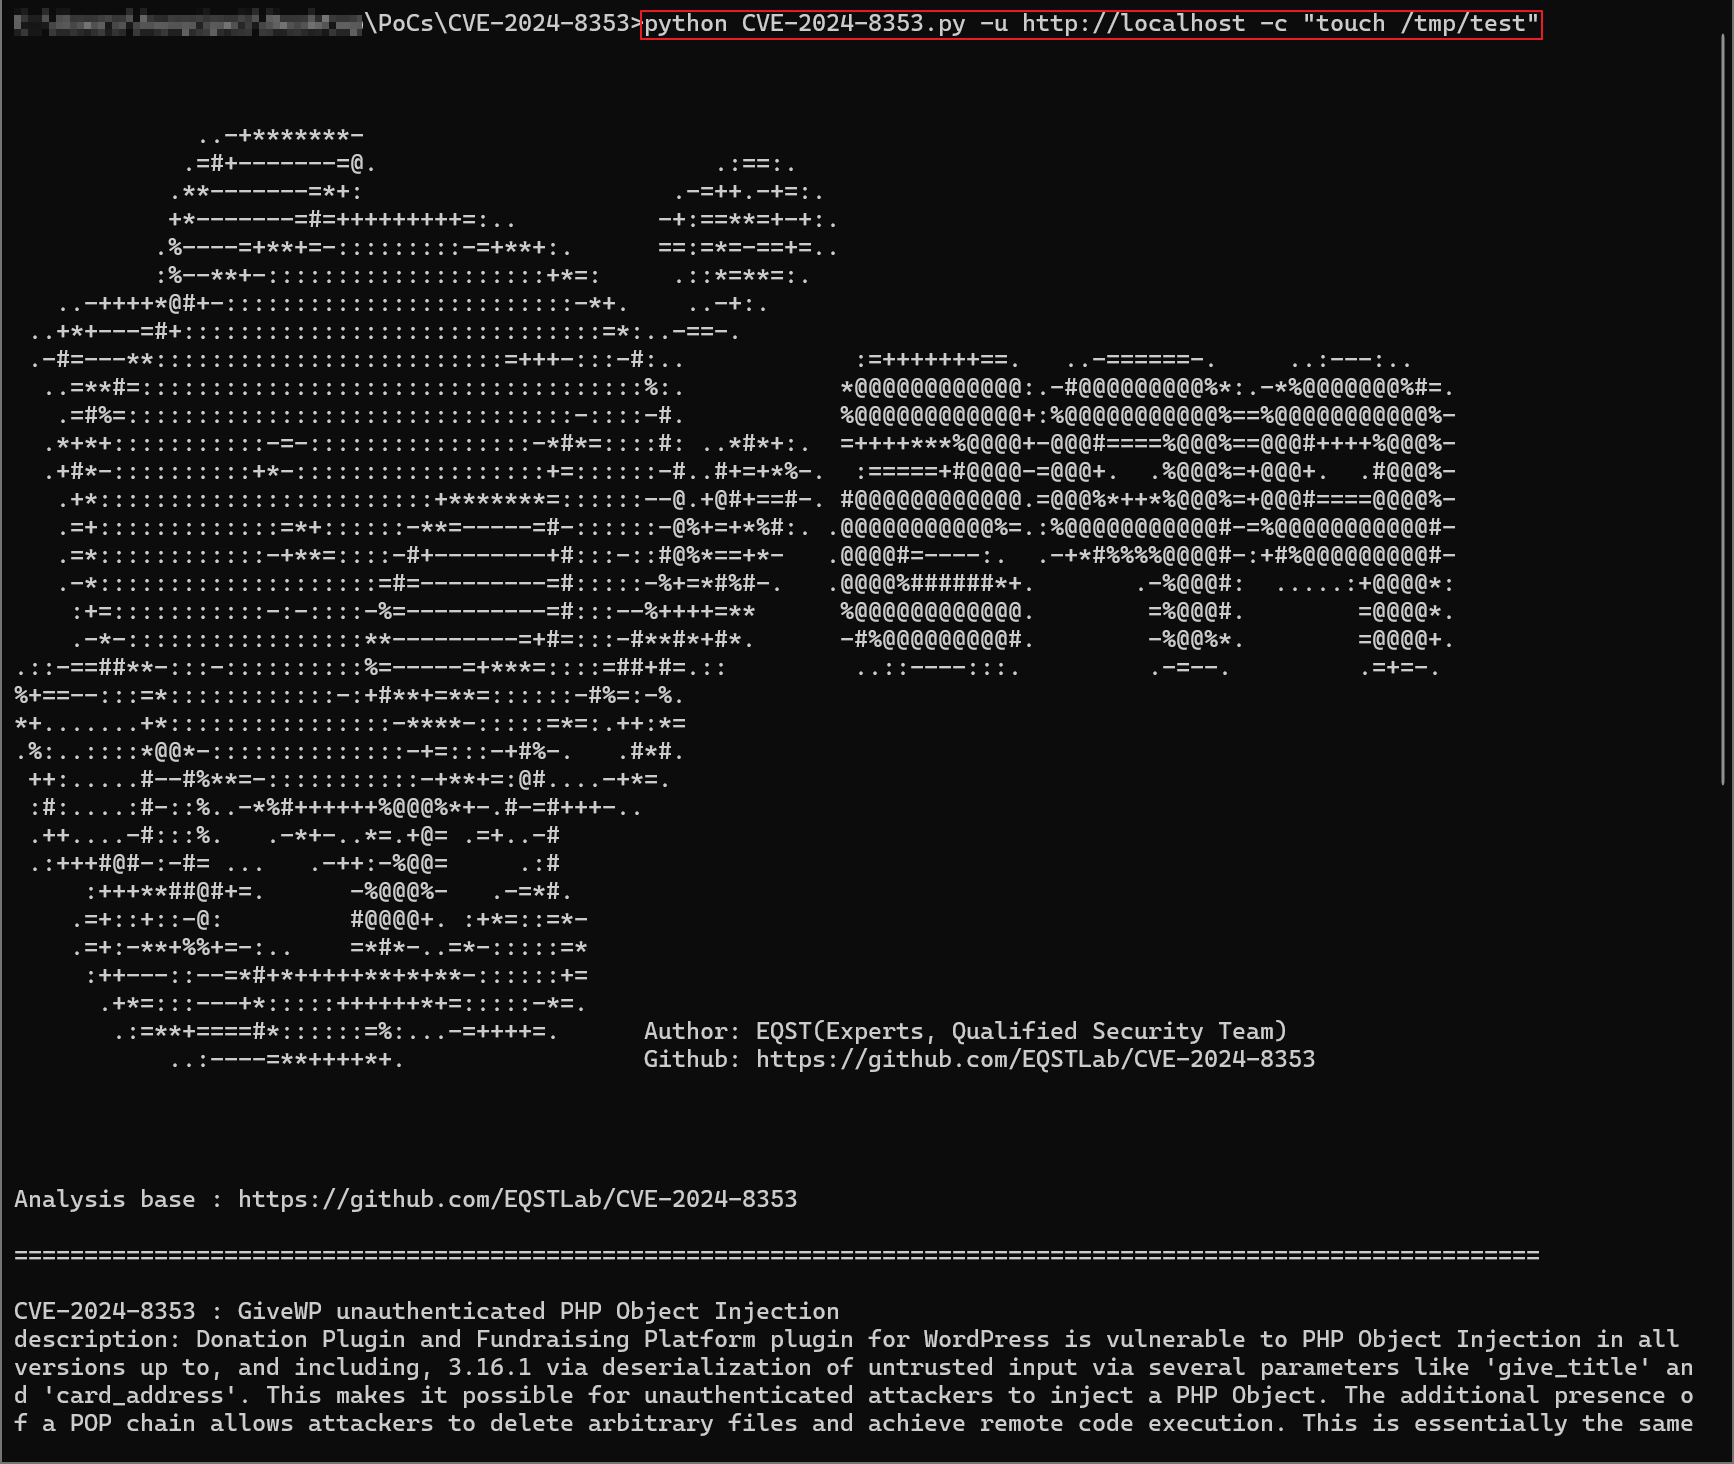 eqstlab/cve-2024-8353
GiveWP PHP Object Injection exploit