
CVE-2026-48017
 romain-deperne/cve-2026-48017
Remote Code Execution in DbGate via functionName injection in the loadReader endpoint — CVSS 8.8
code-analysiseducationexploitation+4
romain-deperne/cve-2026-48017Remote Code Execution in DbGate via functionName injection in the loadReader endpoint — CVSS 8.8
 squeeze440/openlore-poc
PoC — path traversal via unsanitized LLM-derived domain field in OpenLore (GHSA-5j8x-q7q6-58j5, CVE-2026-87001, CVSS 4.7).
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 jricramc/aigate
AI Prompt Secret Scanner: local proxy and Claude Code hook that blocks secrets before they reach AI APIs
 gh-ost00/cve-2024-0195-spiderflow
CVE-2024-0195 Improper Control of Generation of Code ('Code Injection')
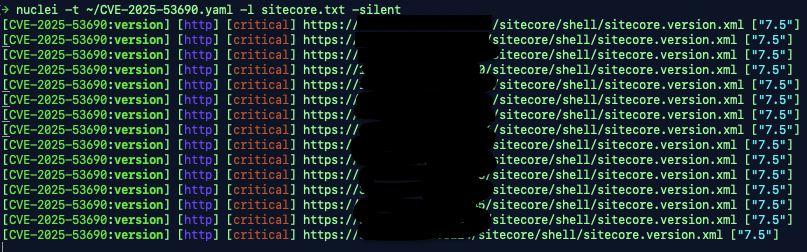 rxerium/cve-2025-53690
Detection for CVE-2025-53690
 viszsec/cve-2024-23897
Jenkins POC of Arbitrary file read vulnerability through the CLI can lead to RCE
 akiraaisha/shellshocker-python
This is a Python Application that helps you detect if your machine that run bash is vulnerable by CVE-2014-6271
 zoly-zoly/cve-2025-3248
Educational analysis and proof-of-concept exploit for CVE-2025-3248, a critical unauthenticated code injection vulnerability in Langflow, including…
 d0rb/cve-2023-49606
Critical use-after-free vulnerability discovered in Tinyproxy
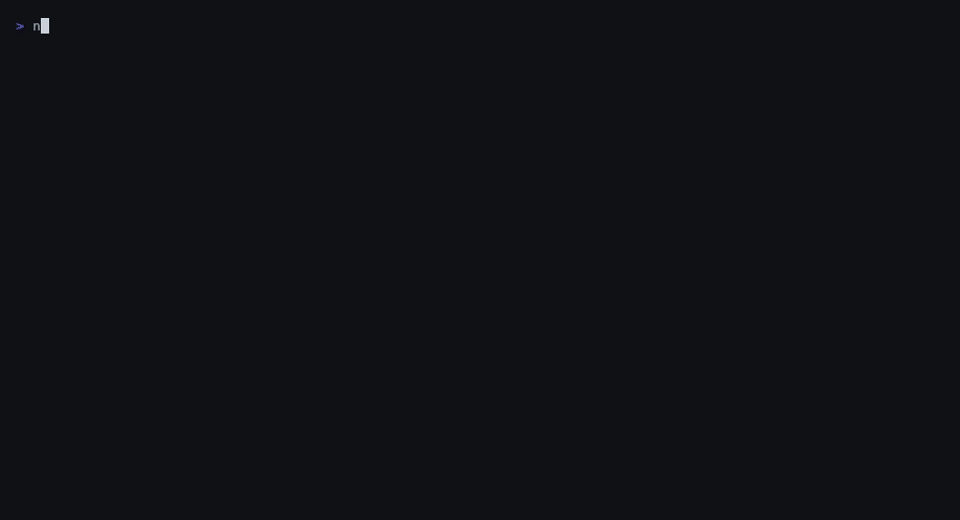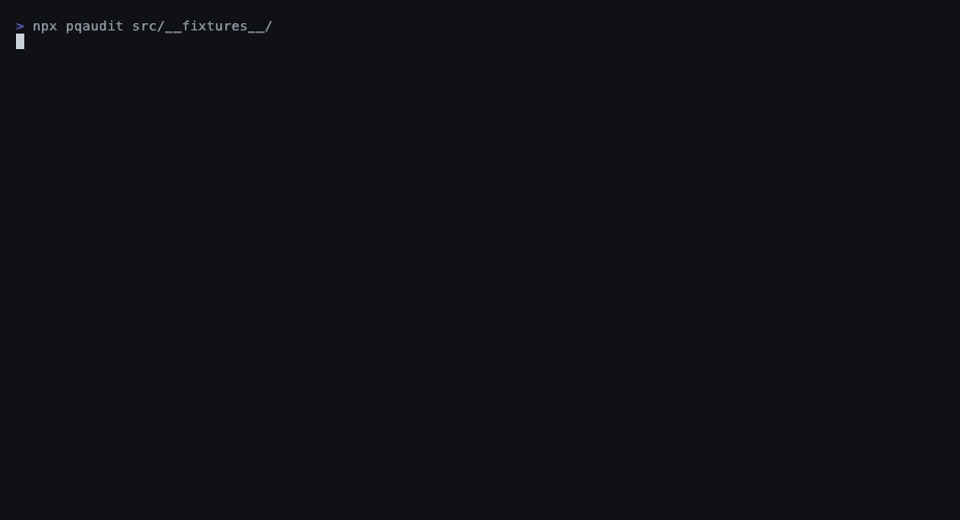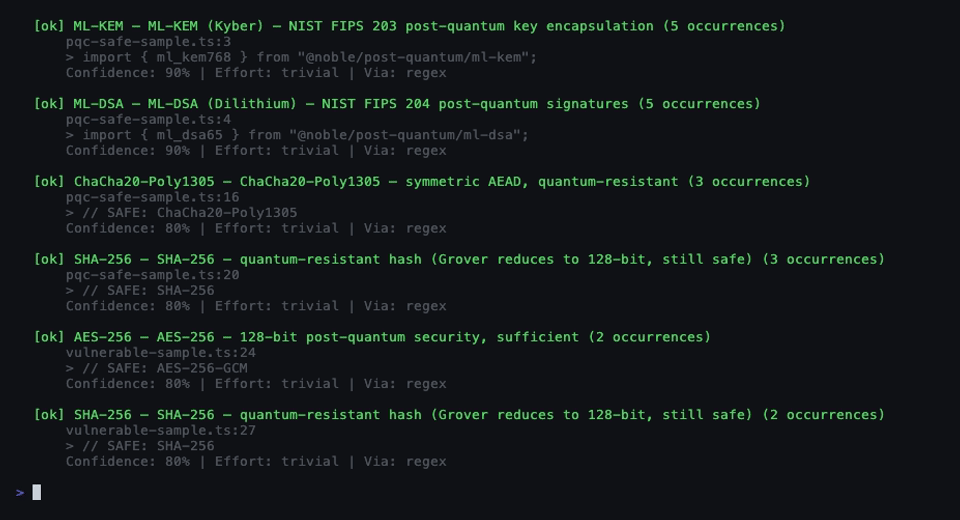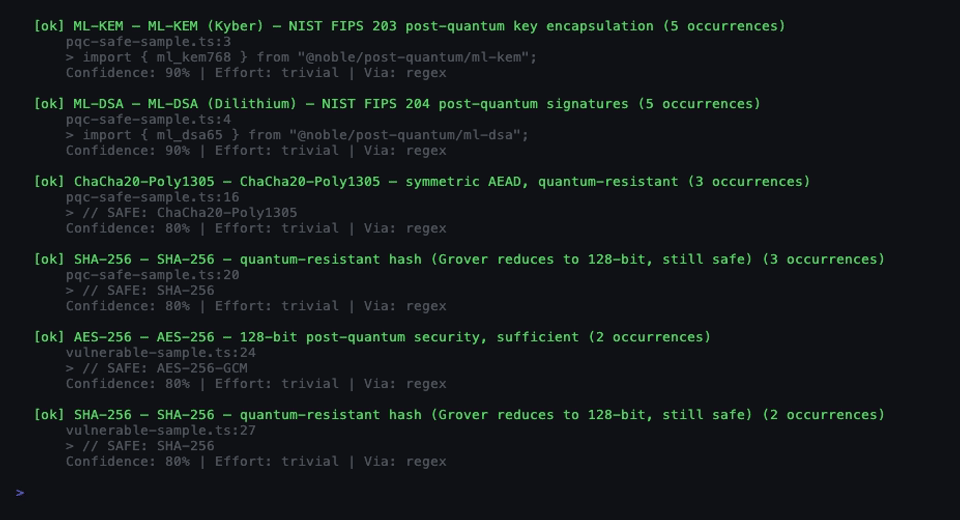 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 ak-cybe/cve-2025-68664-langgrinch-poc
A testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only
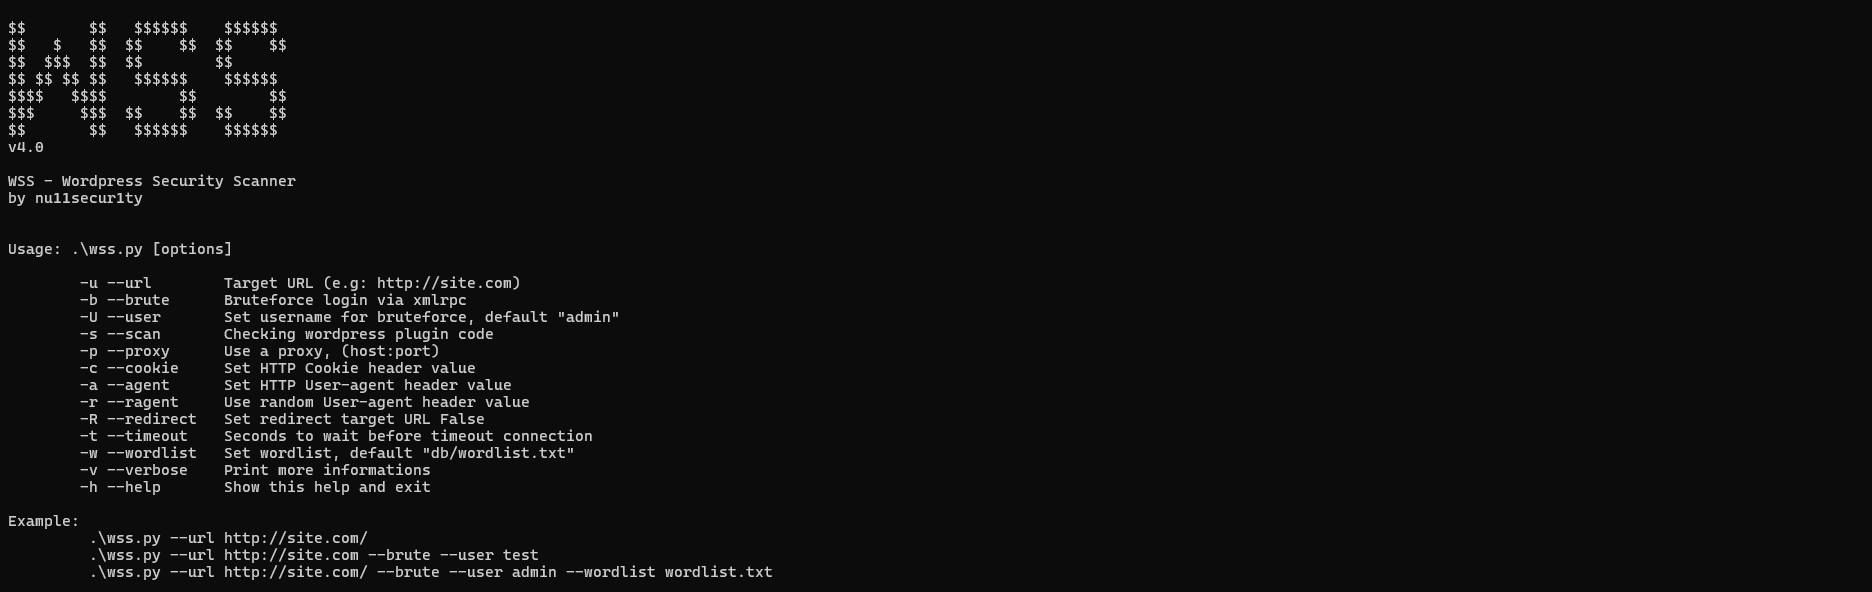 nu11secur1ty/wss
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 rndhouse/vcamper
PoC: identify silent security patches before CVE
 razureink/cve-2024-50330-ivanti_epm_sqli_reproduction
CVE Reproduction: cve-2024-50330-ivanti_epm_sqli_reproduction
 inferiorak/cve-2025-55182-react2shell-async-scanner
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.
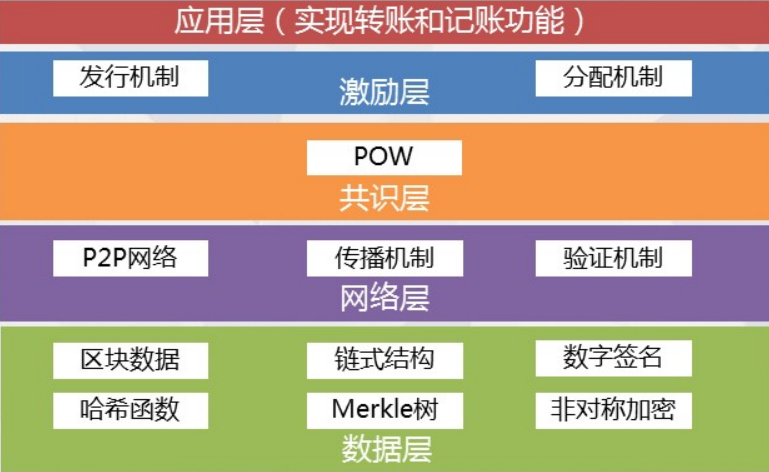 al1ex/blockchainconstruction
BlockChain Security Construction