
CVE-2022-1329
 mcdulltii/cve-2022-1329
WordPress Elementor 3.6.0 3.6.1 3.6.2 RCE POC
code-analysisexploitationpayload-development+3
mcdulltii/cve-2022-1329WordPress Elementor 3.6.0 3.6.1 3.6.2 RCE POC
 x1r0z/spring-amqp-deserialization
PoC of Spring AMQP Deserialization Vulnerability (CVE-2023-34050)
 mpgn/cve-2018-19276
CVE-2018-19276 - OpenMRS Insecure Object Deserialization RCE
 p0in7s/cve-2024-38475
Proof-of-concept exploit for CVE-2024-38475 targeting Apache HTTP Server mod_rewrite improper escaping, enabling URL-to-filesystem mapping for code…
 sickwell/cve-2025-55182
CVE-2025-55182 - React Server Components RCE Exploit & Scanner Supports external servers and CLI interface
 theori-io/reactguard
ReactGuard provides framework- and vulnerability-detection tooling for CVE-2025-55182 (React2Shell)
 jweny/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980, a remote code execution vulnerability in Spring Data MongoDB via SpEL injection in the username…
 sudistark/vscode-rce-electrovolt
Trying to reproduce CVE-2021-43908
 hunntr/cve-2023-46818
An issue was discovered in ISPConfig before 3.2.11p1. PHP code injection can be achieved in the language file editor by an admin if…
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
 csenox/cve-2021-21425
GravCMS Unauthenticated Arbitrary YAML Write/Update leads to Code Execution (CVE-2021-21425)
 dollarboysushil/dolibarr-17.0.0-exploit-cve-2023-30253
In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…

 fuzzlove/fudforum-xss-rce
FUDForum 3.0.9 - XSS / Remote Code Execution (CVE-2019-18873, CVE-2019-18839)
 vulnmachines/spring-cve-2022-22947
Spring cloud gateway code injection : CVE-2022-22947
 randomrobbiebf/cve-2024-9593
Time Clock <= 1.2.2 & Time Clock Pro <= 1.1.4 - Unauthenticated (Limited) Remote Code Execution
 mogwailabs/cve-2017-1000486
Proof of Concept Exploit for PrimeFaces 5.x EL Injection (CVE-2017-1000486)
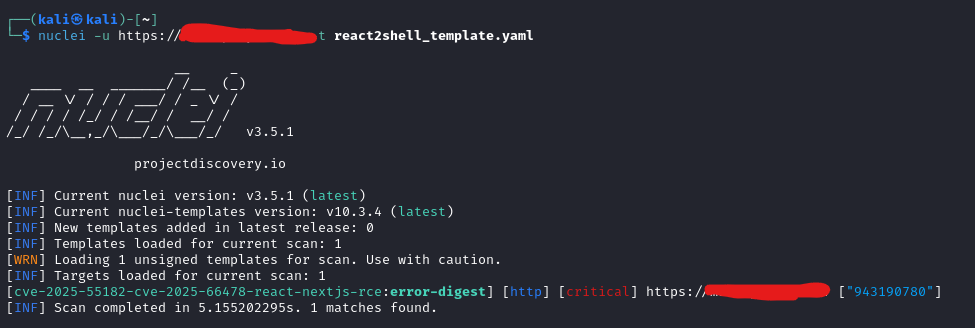 shamo0/react2shell-poc
Nuclei template for detecting react2shell (CVE-2025-55182 & CVE-2025-66478)