
 cookiengineer/exocomp
Self-hosted multi-agent environment for Go with LLM-powered pentesting agents (exploiter, reverser, threathunter, webscanner) that automate…
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
 rahulreddykarne/cve-2026-65320-fastcore
Documents CVE-2026-65320, a tar-slip path traversal in fastcore's untar_dir(), with a harmless proof-of-concept demonstrating arbitrary file write…
 siunam321/cve-2024-7627-poc
Proof-of-Concept script for WordPress plugin Bit File Manager version 6.0 - 6.5.5 Unauthenticated Remote Code Execution via Race Condition…
 hideki233/cve-2025-3248-langflow-rce
Proof-of-concept exploit for CVE-2025-3248, an unauthenticated remote code execution vulnerability in Langflow, demonstrating code injection via the…
 honeyb33z/cve-2020-11023-scanner
Static analysis scanner for CVE-2020-11023 XSS vulnerabilities in JavaScript. Detects vulnerable jQuery versions and dangerous DOM manipulation…
 p33d/cve-2024-9441
Exploit for CVE-2024-9441: Remote Code Execution via improper input sanitization in PHP forgot-password functionality. Uploads a malicious script and…
 cyberh3als/cve-2023-36845-poc
Automated PoC script for CVE-2023-36845, exploiting a PHP flaw in Juniper Junos OS J-Web to remotely modify PHPRC and achieve code injection on…
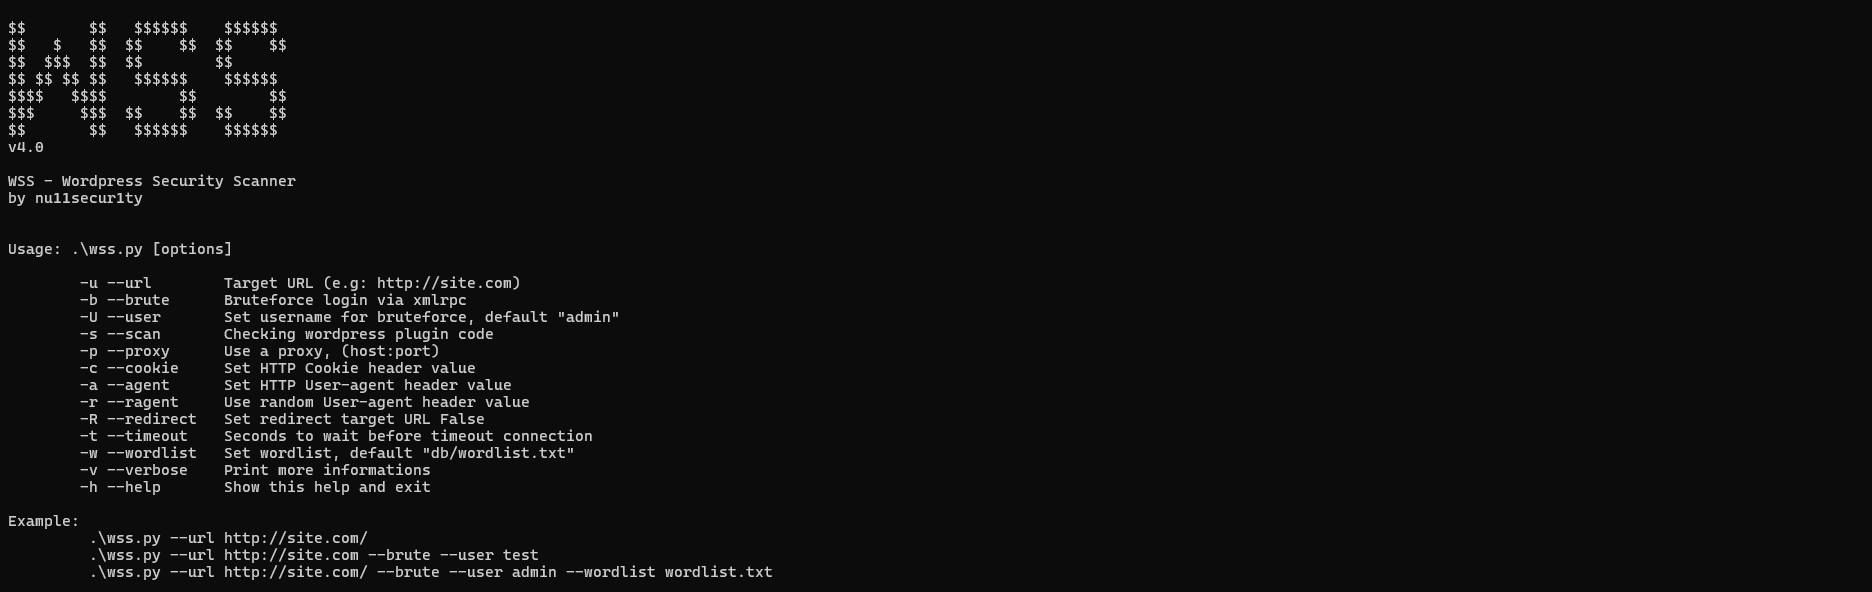 nu11secur1ty/wss
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…
 mehdichyhab/cve-2025-64512-exploit
CVE-2025-64512 - pdfminer.six Remote Code Execution Exploit
 windecks/cve-2023-46404
PoC and Writeup for CVE-2023-46404.
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
 hunt-benito/llama-factory-webui-rce-cve-2026-58116-trust-remote-code-model-path-injection
Proof-of-concept exploit for CVE-2026-58116 demonstrating remote code execution in LLaMA-Factory WebUI via trust_remote_code model path injection.…
 filipsedivy/cve-2020-15227
Python-based checker for CVE-2020-15227 that tests Nette applications for remote code execution vulnerabilities via file_put_contents and shell_exec…
 ahmedreda38/cve-2025-47273-poc
CVE-2025-47273 is a high-severity path traversal vulnerability in the setuptools library ,specifically version 78.1.0 .